
In this post, I want to look at the relationship between Object Storage and some other organization personas, such as the Project Admin and the Project Advanced User.
247 links
In this post, I want to look at the relationship between Object Storage and some other organization personas, such as the Project Admin and the Project Advanced User.
Learn how to setup Confidential Compute with Intel TDX in VCF 9.1 offering data in-use protection for critical workloads.
The other day a serious vulnerability was disclosed in one of the newer Linux distributions (the one led by the racist, so it isn't getting a mention here). The issue was interesting because it was…
implements both distributed firewall rules and gateway firewall rules for each DSM database deployed via VCF Automation
Putting videos on YouTube is a convenient solution, but not a privacy-friendly one. Using HLS, it's possible to self-host videos while being...
VMware Explore 2026 Session URLs. Contribute to lamw/vmware-explore-2026-session-urls development by creating an account on GitHub.
Sous le capot d'un PDS ATProto : un dépôt de données cryptographique, trié dans un Merkle Search Tree et signé à chaque écriture. On ouvre mon propre dépôt à la main : on liste ses records, on télécharge son export CAR, et on vérifie sa signature nous-mêmes, sans jamais faire confiance au serveur.
Oh look npm registry got compromised… again.
Comment connecter External Secrets Operator (ESO) à l'OVHcloud Secret Manager pour synchroniser automatiquement vos secrets dans Kubernetes, avec un compte de service IAM en moindre privilège.
A look inside Copilot’s network traffic, harness, memory, and how context is becoming the product.
Learn the most common reverse proxy mistakes in home labs and how I avoid them using Traefik, Docker, proper networking, TLS, and security best practices.
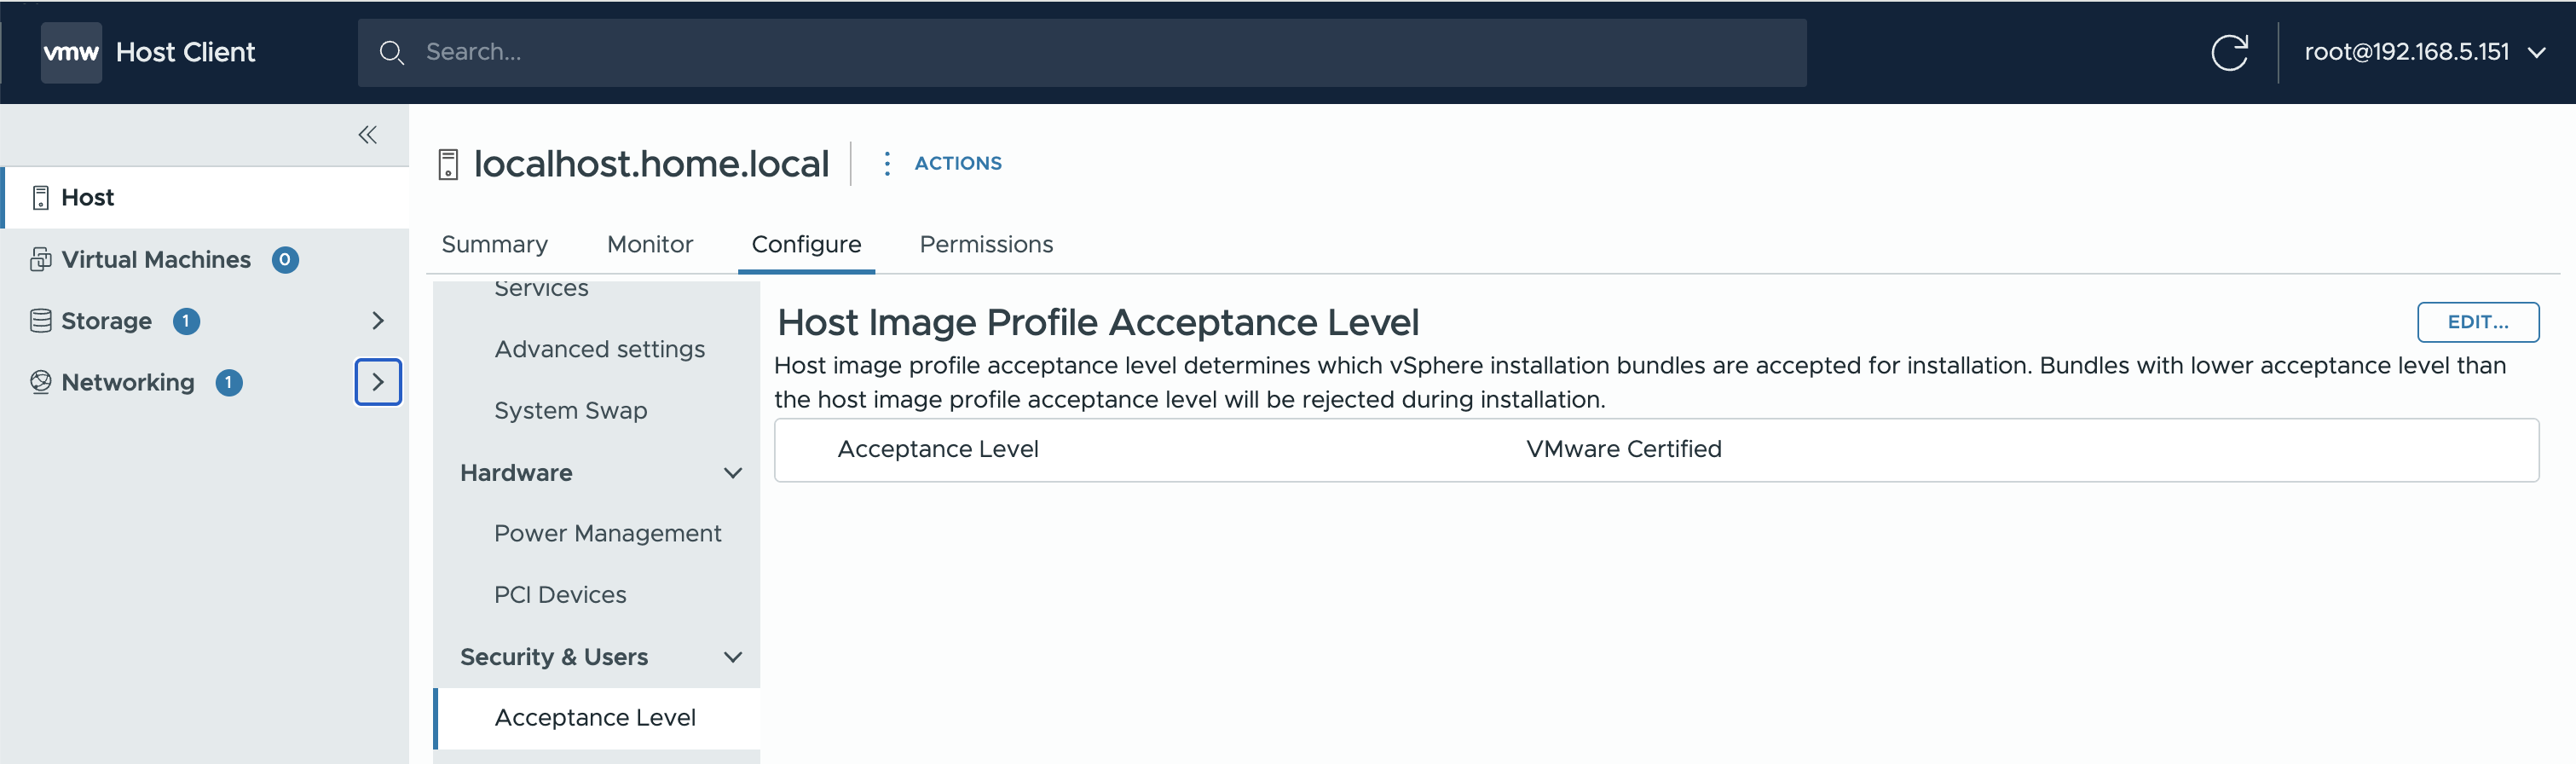
How configstorecli bypasses ESX Acceptance Level guard on a Secure Boot-enabled host, letting unsigned VIBs run.
We’re on a journey to advance and democratize artificial intelligence through open source and open science.
Single Sign-On for Your Self-Hosted Universe 🐈⬛🔒
In this guide, we set up the Hermes AI agent on a Linux server and access it securely from anywhere with NetBird, including the built-in dashboard, the community web UI, and a private HTTPS domain through the NetBird reverse proxy. All the commands and a more detailed walkthrough are in the knowledge hub article linked below.
GhostLock (CVE-2026-43499) is a Linux kernel vulnerability found by VEGA that exists in every major distribution since 2011. Triggering the bug does not require any special kernel config or privilege. By turning it into a 97% stable privilege escalation and container escape, Google has rewarded us $92,337 in kernelCTF. This writeup covers the technical details of the exploit.
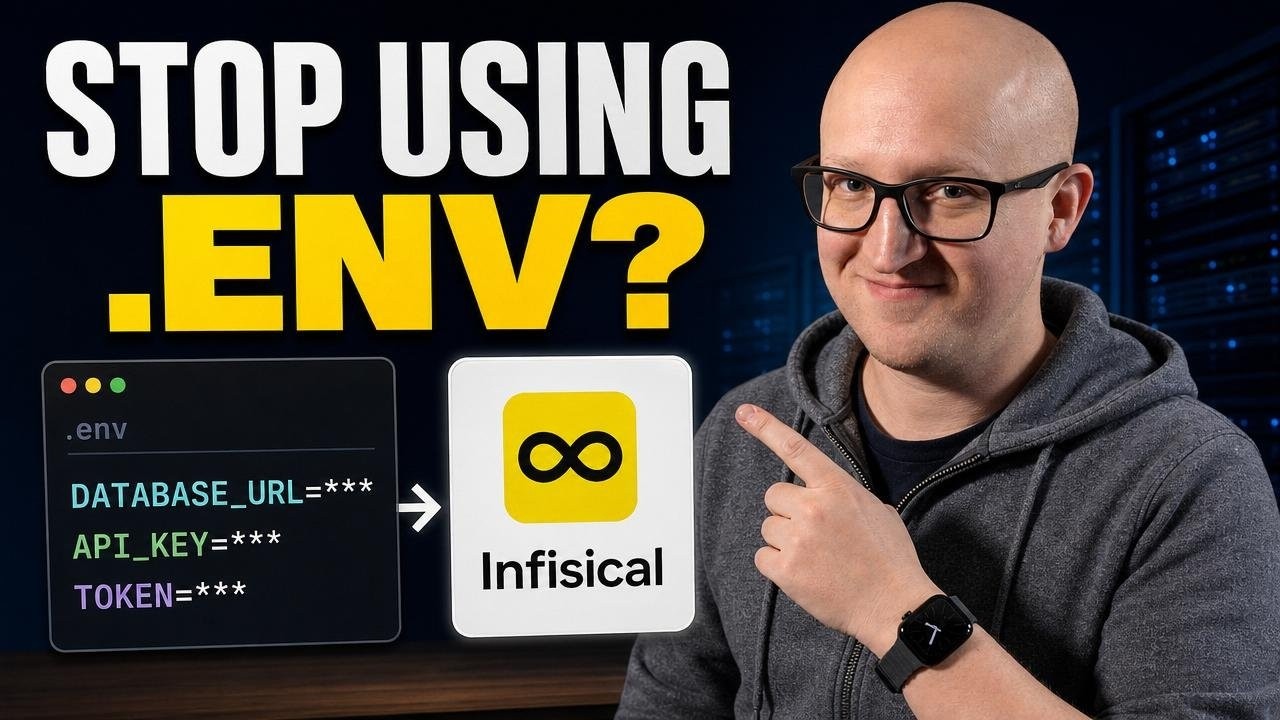
HomeLab secrets usually start simple: one `.env` file next to a Docker Compose stack. But over time, those secrets spread into GitLab variables, deployment scripts, copied folders, backups, notes, and places where they should not live.
No self-signing headaches, no TLS erros.
I have several Cisco network devices in my homelab. In this post will showcase a first-glance on how to access such via Boundary, a PAM solution from HashiCorp.
Replace long-lived AI API keys with groups from your identity provider. Verified identity flows into LiteLLM Cloudflare, and other gateways or providers for audit, cost attribution, and policy enforcement.
Check out Twingate and supercharge your security: https://bit.ly/3Y1OaZi
Sorry I’ve been quiet lately. My head has been down on my newest adventure. I’m so used to being the sole operator, platform engineer, SRE, or whatever that day brings that it’s odd to take a step back and be tasked with providing enterprise cybersecurity for cloud environments that other teams are operating. I’ve had so many cool new projects that will make for some great technical blogs, so I figured I would start with this one. The idea is simple: how do you provide your organization with hardened operating systems that teams can actually deploy into the cloud? A lot of compliance terms and frameworks get tossed around, but the vision is this: how do you provide an image factory of CIS-hardened AMIs, bake in a custom baseline of tools, and share those images across numerous AWS accounts and organizations?
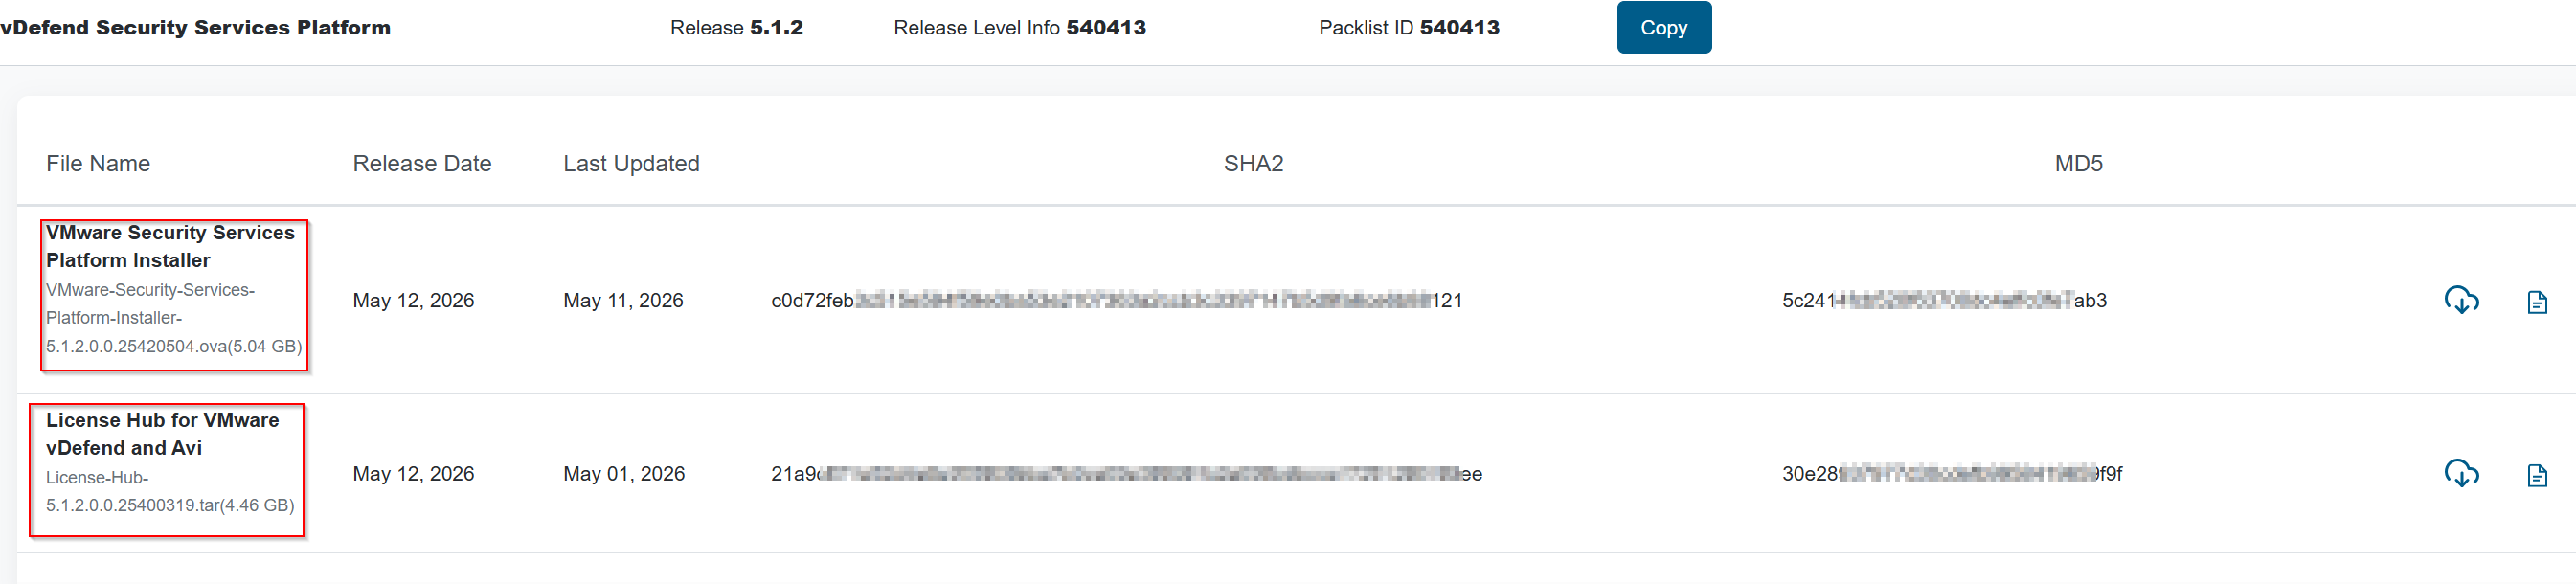
Introduction Architectural Comparison: SSPI, SSP 5.1.1, and SSP 5.1.2Centralized Licensing Policies and Compliance MechanicsEnvironmental Dependencies and Deployment SequencePhase 1: Core Virtualiz…
Today, I’m proud to announce Homebrew 6.0.0. The most significant changes since 5.1.0 are a new tap trust security mechanism, the new faster, smaller, default internal Homebrew JSON API, sandboxing on Linux, better defaults informed by our user survey, many brew bundle improvements, improved performance and initial support for macOS 27 (Golden Gate).
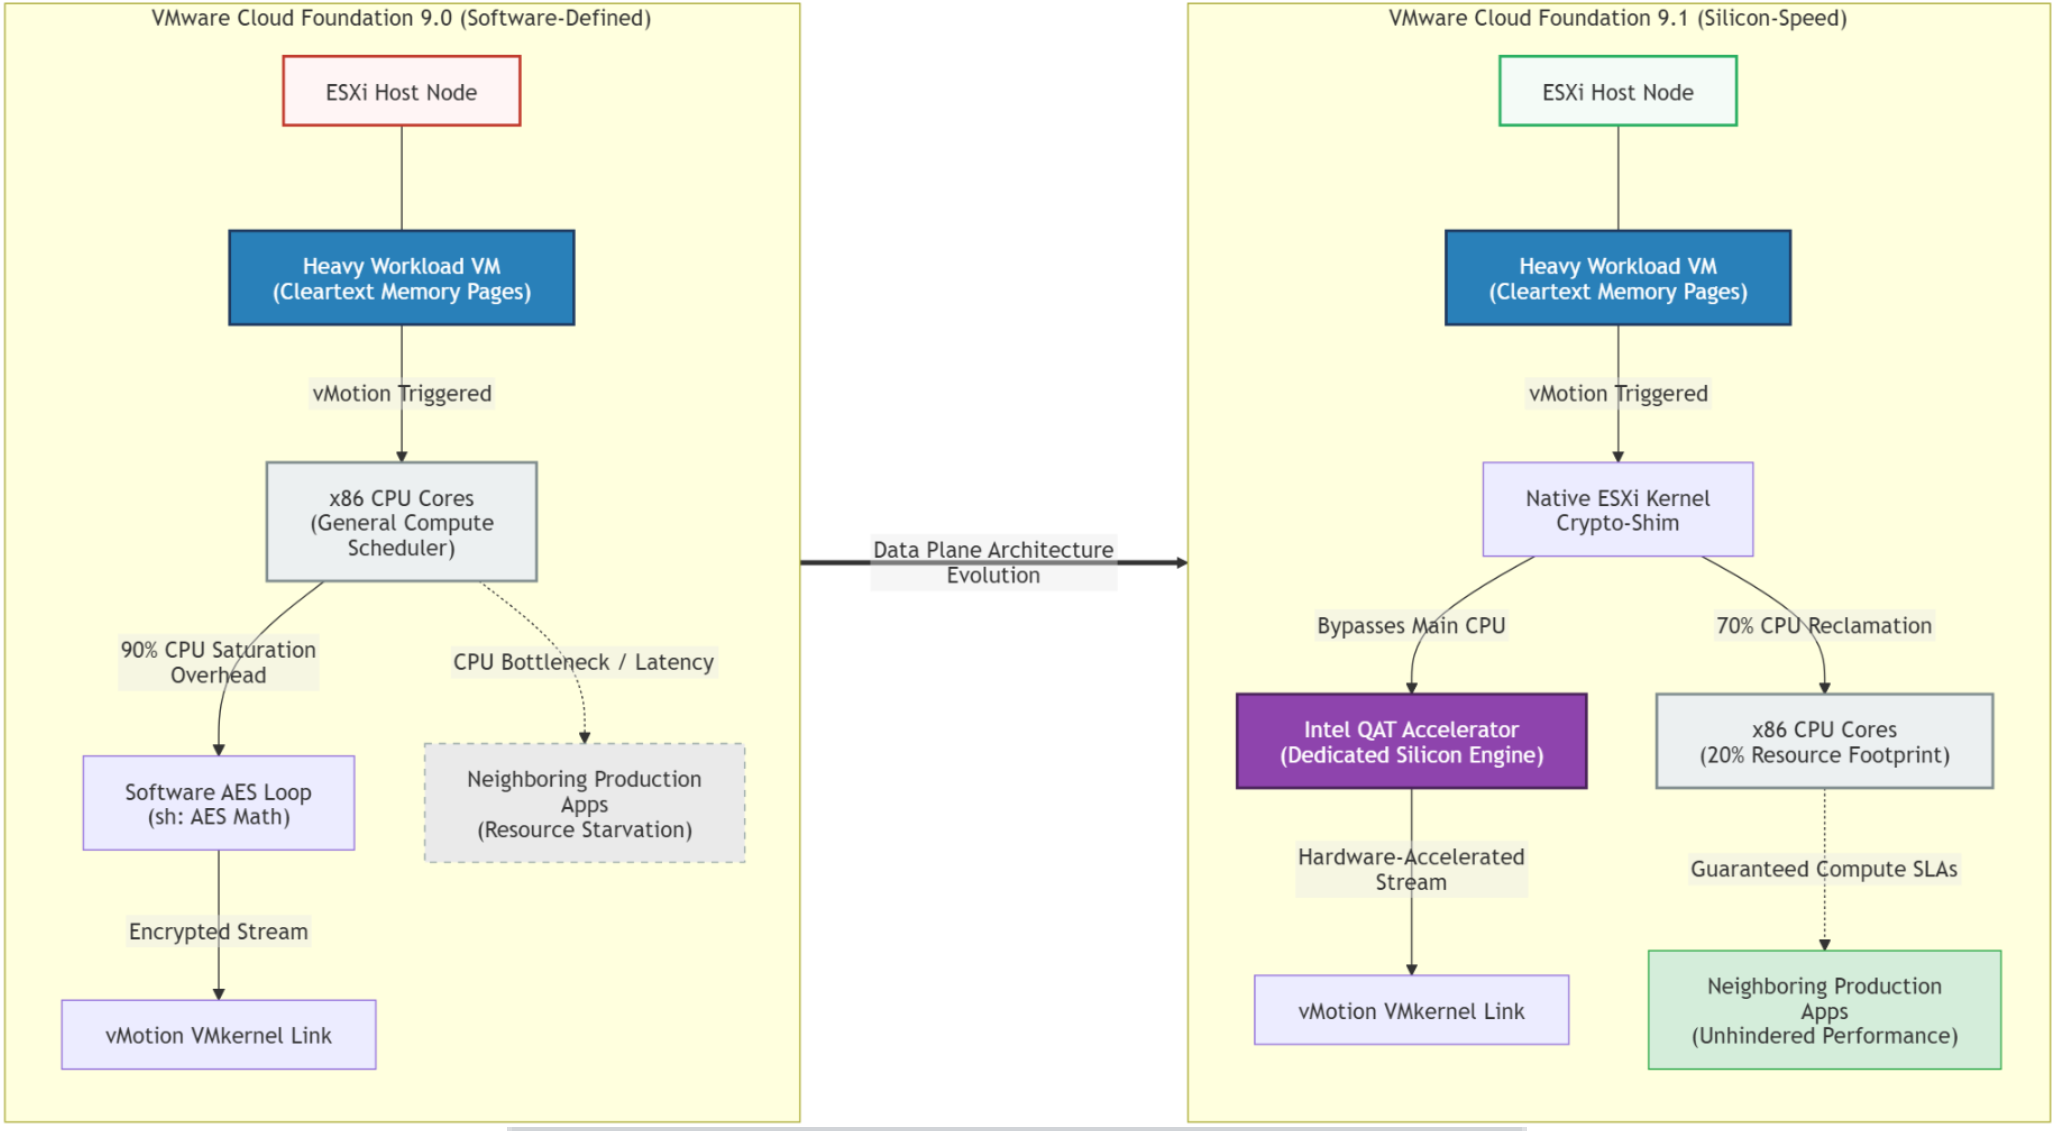
IntroductionThe Architectural Breakthrough: Moving from Software to SiliconVCF 9.0 : Software-Defined EncryptionVCF 9.1: Silicon-Layer Hardware OffloadControl-Plane Encryption: vSphere NKPDeep Dive…
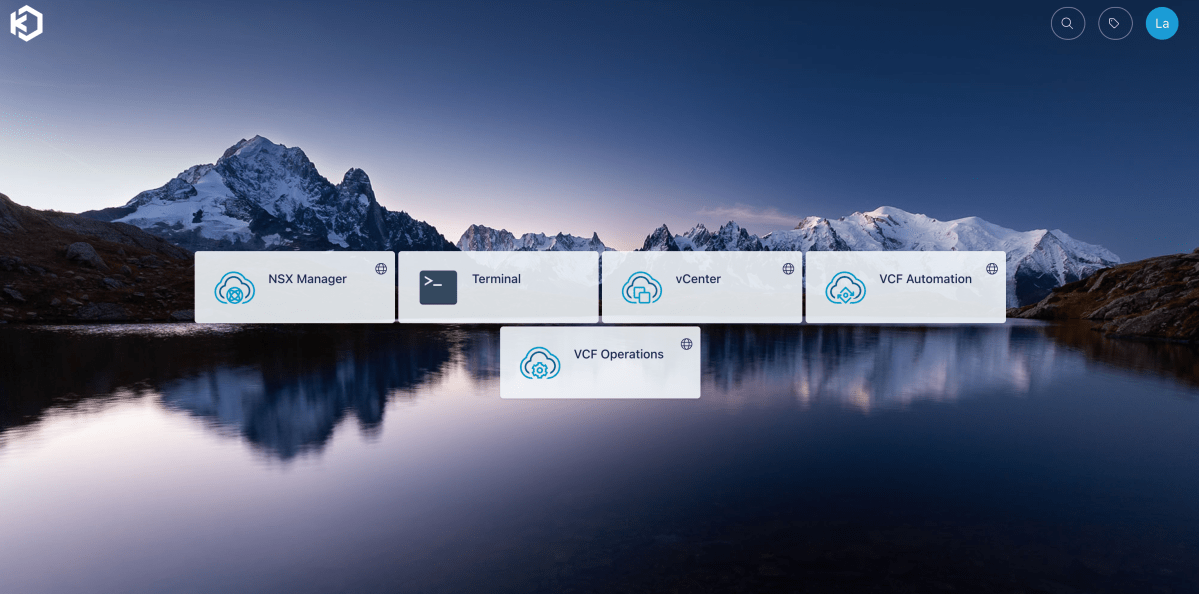
Using Kasm as a browser-based access layer in front of a VCF lab turned out to be a useful pattern. With Keycloak providing authentication for both Kasm and VCF SSO, the lab gets a cleaner access f…

Welcome to the third entry in our VCF 9.1 Fleet Management Blog Series. In our previous posts, we discussed automating certificate lifecycles using both custom and integrated Certificate Authoritie…

Unlocking the power of automation in VMware Cloud Foundation (VCF) 9.1 requires a solid understanding of how to manage programmatic access. By transitioning from manual administration to an API-fir…
For a long time I wanted a piece of software that usedFirecrackerto create MicroVMs on my Linux hosts. It seemed like it would be really useful for vulnerability research and testing features that wer
Headscale gives you CONTROL over your mesh network!
https://headscale.net
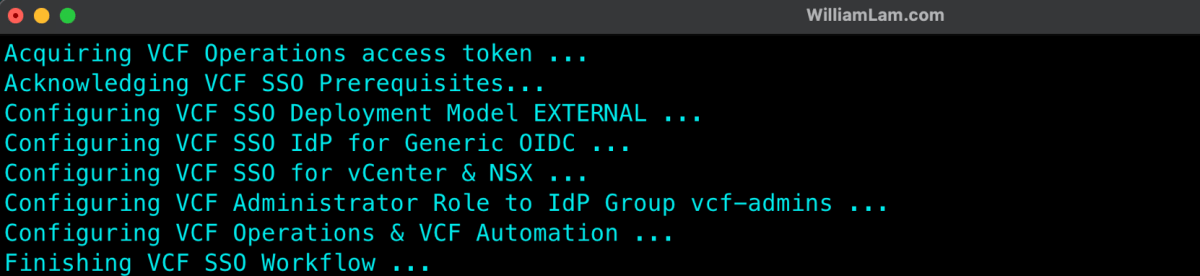
There are a number of exciting enhancements to VMware Cloud Foundation (VCF) Single Sign-On (SSO) with the release of VCF 9.1 from Generic OIDC/SAML2 Identity Provider (IdP) support, streamline way…
Over the weekend, I had to re-deploy a portion of my VCF 9.1 Fleet, including VCF Operations, VCF Management Services, VCF License Server, SDDC Manager and VCF Automation, due to some workflows I w…
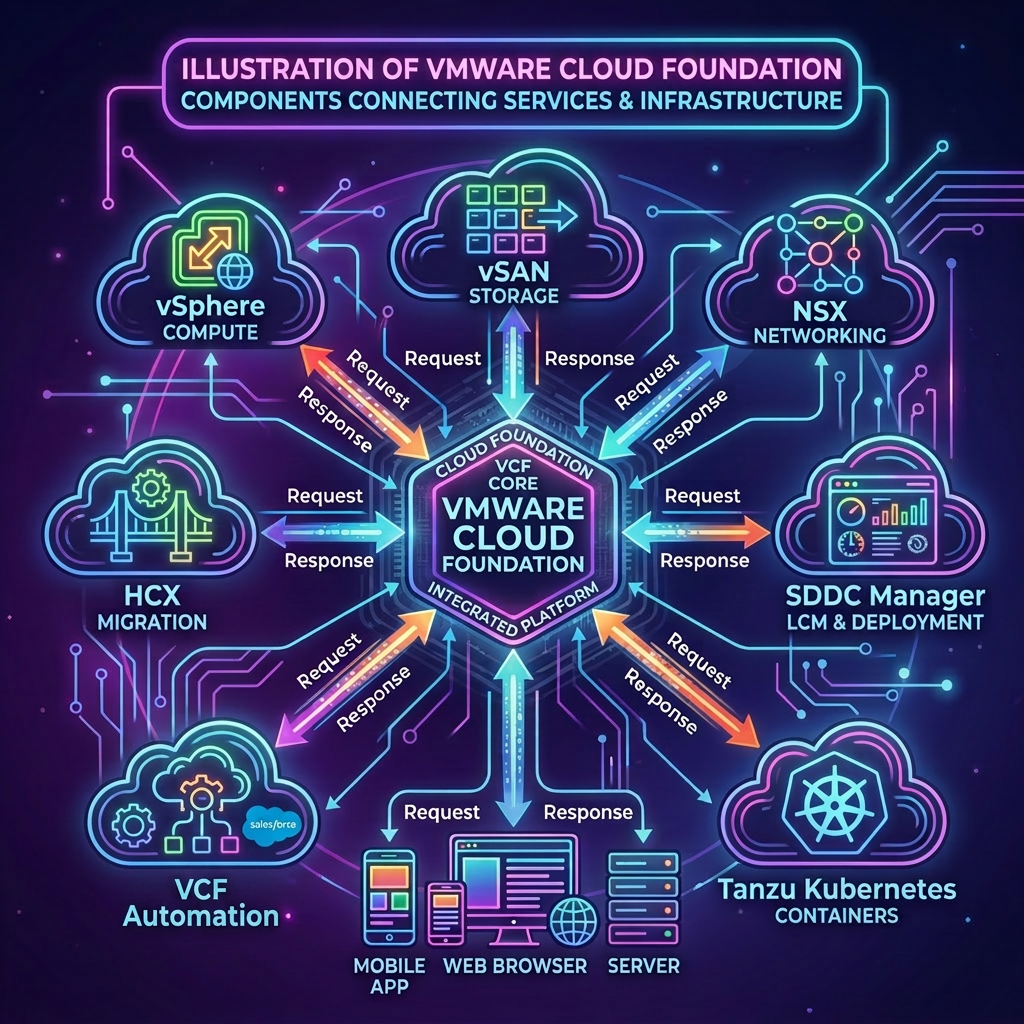
This post outlines how organizations can leverage public APIs of the VMware Cloud Foundation platform for custom automation. It emphasizes obtaining authentication tokens across various endpoints, …
In this video, I’m taking a look at Dockhand, a Docker management platform focused on safer remote Docker management, smart updates, and vulnerability-aware update workflows.
This technical session covers what's new in vSphere as part of VMware Cloud Foundation 9.1. Féidhlim O'Leary walks through lifecycle management, VM management, and Kubernetes enhancements. Dave Morera covers workload acceleration including memory tiering, vMotion encryption offload, NUMA scheduling improvements, and expanded GPU support. Bob Plankers closes with platform security topics.
In this blog post, I’ll discuss the new VPC connectivity Policies and how they can be used to enhance security.
Comment Kloak intercepte le trafic TLS de vos pods au niveau kernel avec des uprobes eBPF pour injecter vos secrets de façon transparente, sans modifier vos applications ni déployer de sidecar.
tsnet let Cleric embed Tailscale into their AI SRE, replacing VPNs and VPC peering with a programmable, zero-config overlay network.
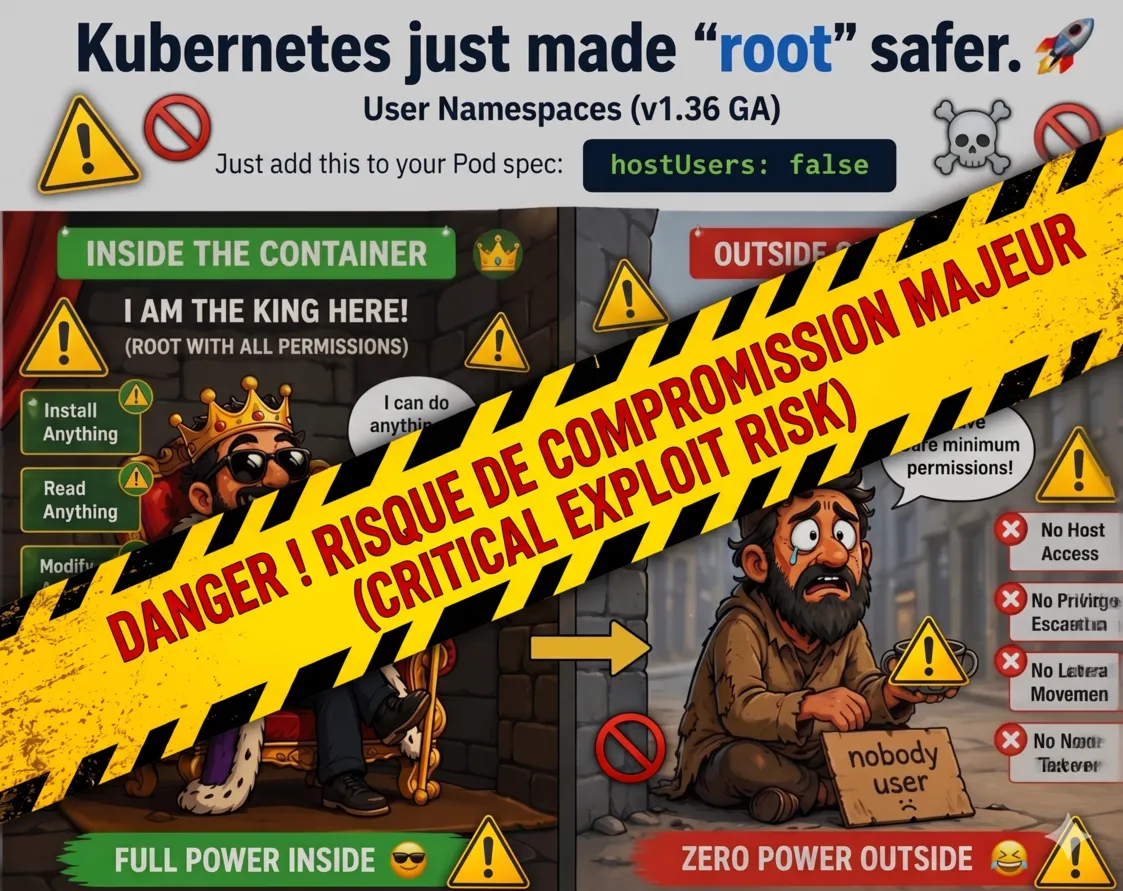
L’infographie qui m’a trigger Depuis quelques jours, les infographies se suivent (et se ressemblent) sur Linkedin. Kubernetes 1.36 est sorti et une des features qui fait le plus parler, c’est la sortie en GA des UserNamespaces.\nC’est un sujet que je suis depuis 2018 (talk The Route to rootless container à la kubecon EU de 2018) donc je peux dire que je suis content de voir l’aboutissement de ce long chemin. Cependant, je suis “profondément choqué” de voir la façon dont c’est présenté sur LinkedIn, visiblement par des gens qui n’ont aucune idée de comment ça fonctionne (et qui probablement, s’en fichent).\n
CVE-2026-31431. 100% Reliable Linux LPE — no race, no per-distro offsets, page-cache write that bypasses on-disk file-integrity tools and crosses containers. Found by Xint Code.
A guide to figure out whether GrapheneOS makes sense for you and how to set up
a smartphone or tablet with Android 16, using GrapheneOS, in a privacy-focused
way.

Previous message (by thread):WireGuard Windows 0.6.1 - Timeline of issues (tunnels lost & import still broken)Messages sorted by:[ date ][ thread ][ subject ][ author ]Hey again,
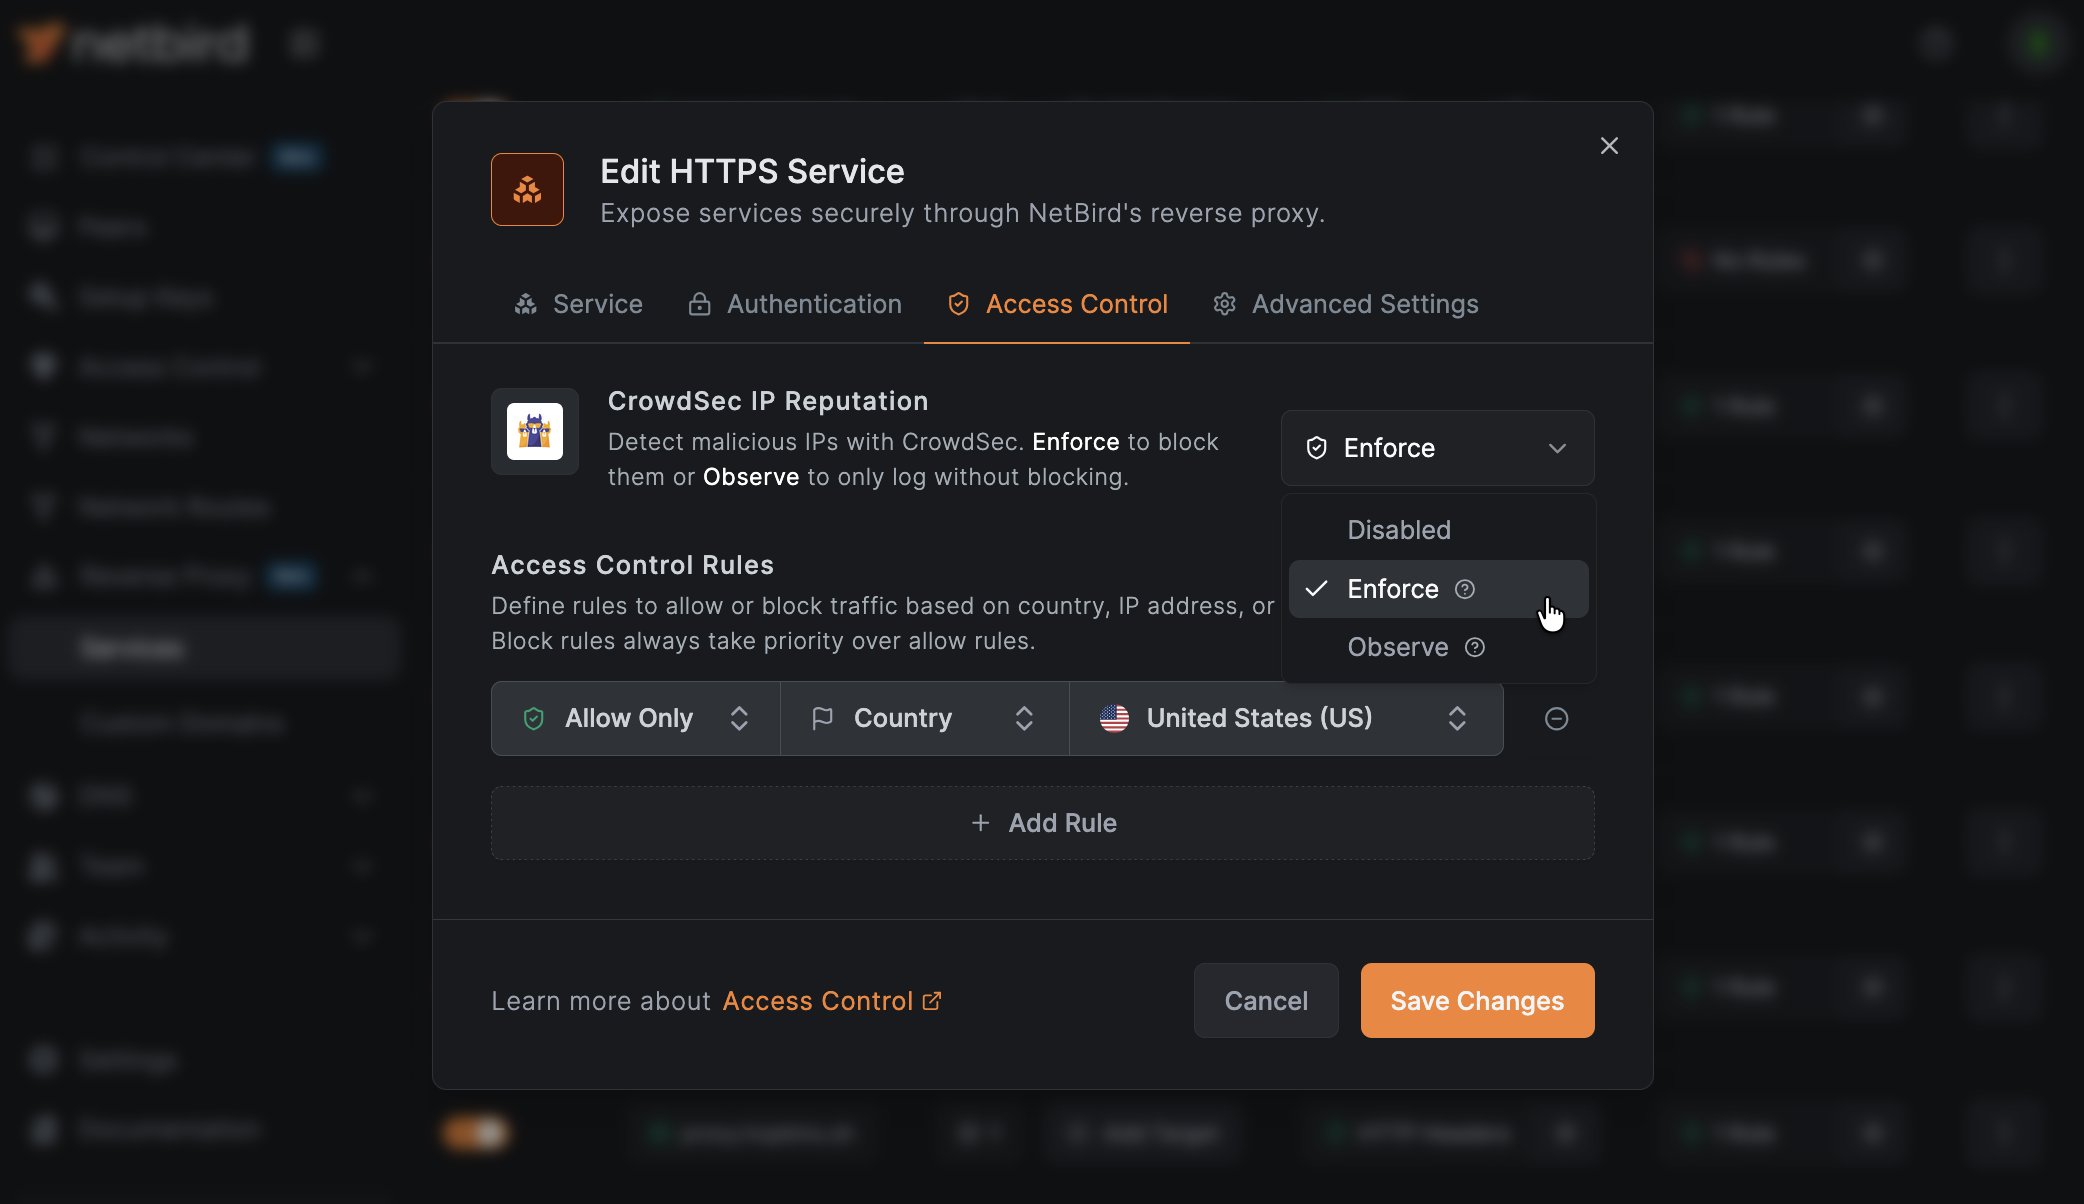
NetBird v0.69 is out. Top of the list for self-hosters:
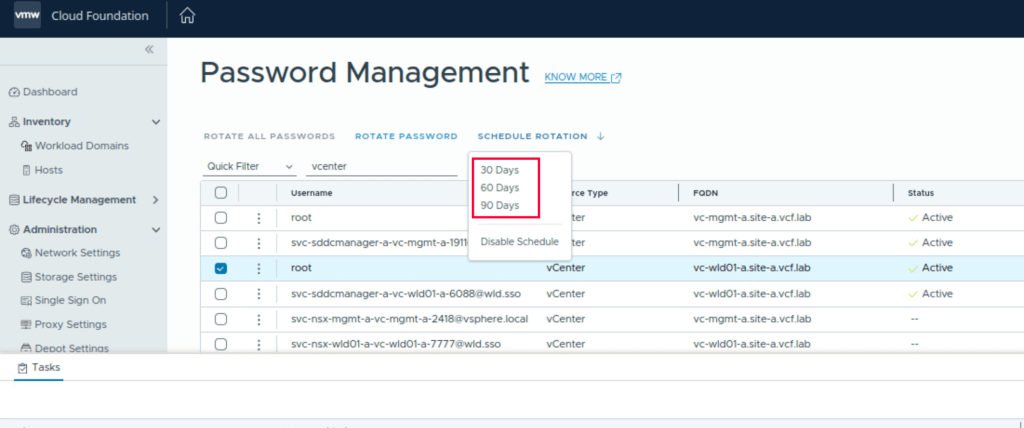
Learn how to use the VCF 9.0 SDDC Manager API to set custom password rotation schedules beyond the 30, 60 and 90 day UI presets
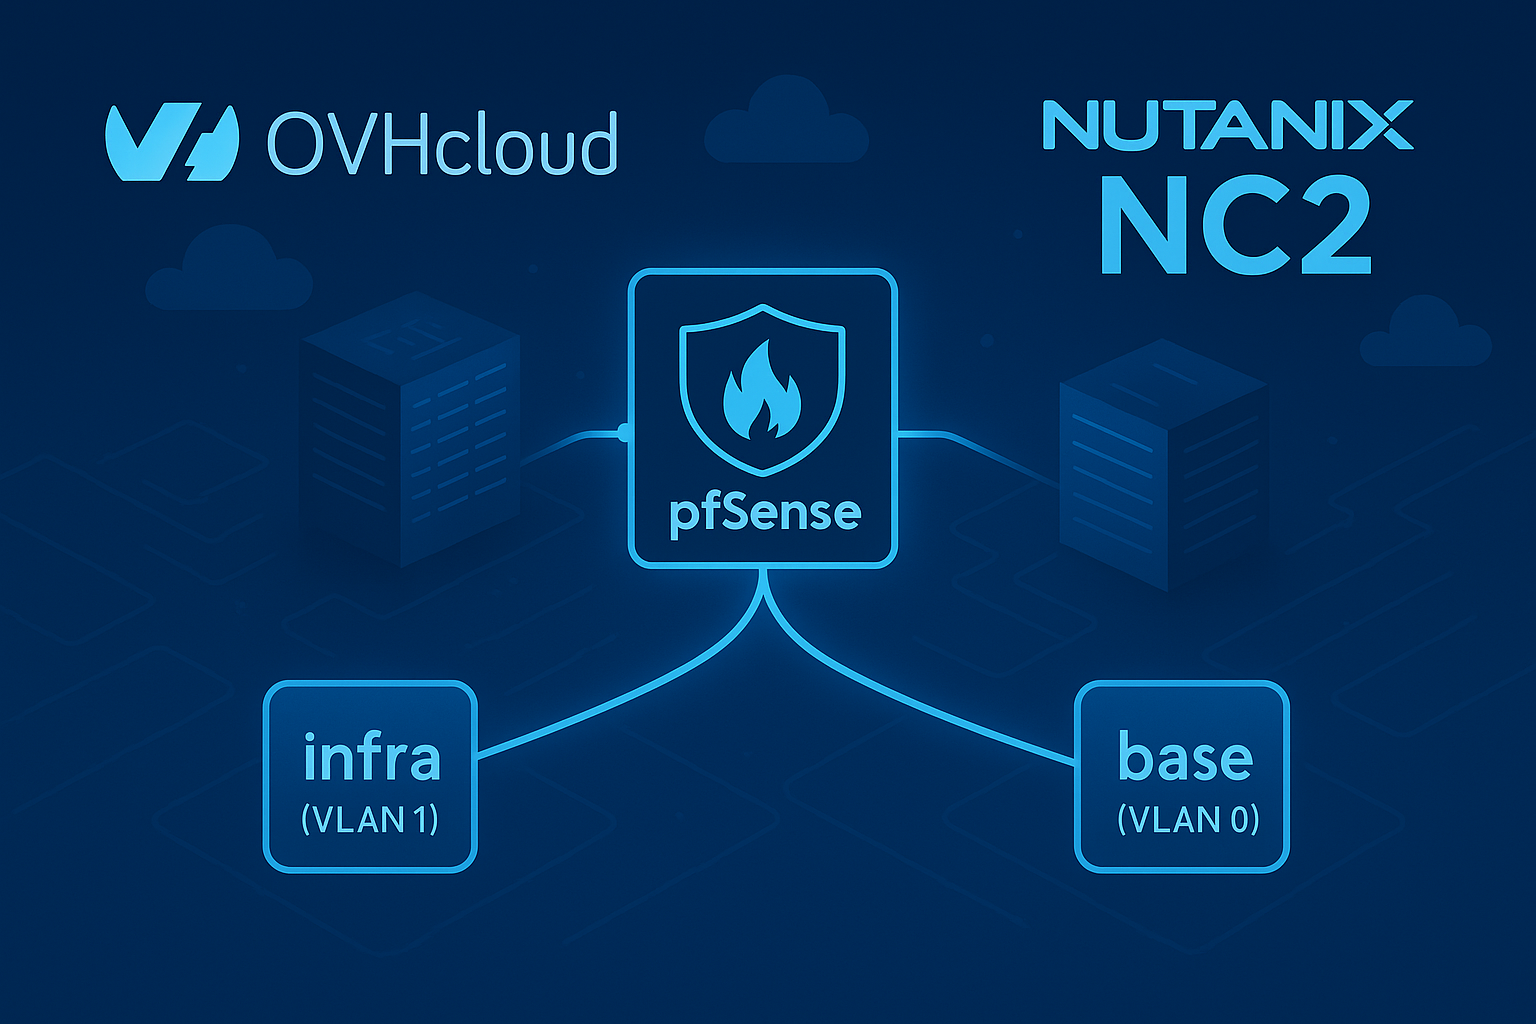
A complete guide to replacing the default OVHcloud gateway with a pfSense firewall on Nutanix NC2.
Nous exploitons déjà depuis plus de deux ans un cluster Kubernetes basé sur un empilement très complexe de couches OpenShift, mais aussi vSphere/VSAN/NSX-T, qui apporte un niveau de sécurité élevé avec le CNI Antrea (qui s’occupe du réseau du cluster Kube). Cela nécessite aussi un niveau d’expertise globalement très élevé, sans même parler du prix de ces couches…
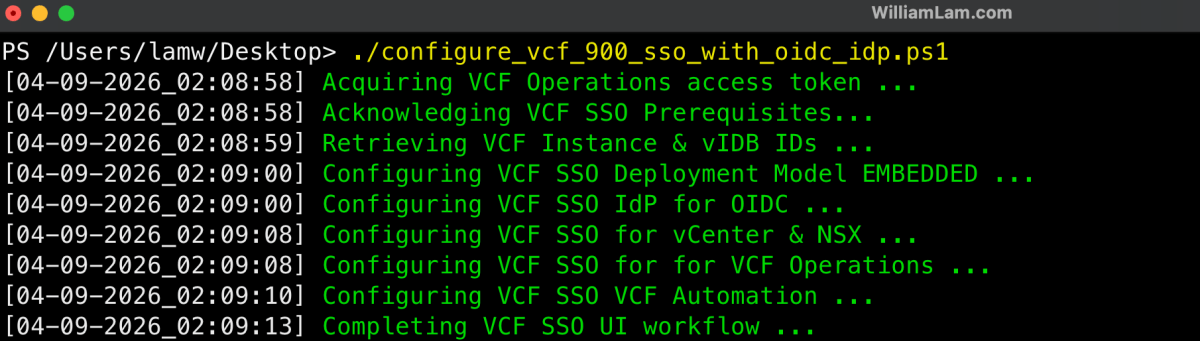
Configuring VMware Cloud Foundation (VCF) Single Sign-On (SSO), introduced in VCF 9.0, can be quite lengthy, especially when you go through the workflow for the first time. For my lab setup, I use …
I pulled apart NanoClaw's 8,000-line codebase and found six architectural patterns that most SaaS teams should steal — credential proxies, container isola…
Discover powerful applications such as Little Snitch Mini, Little Snitch, LaunchBar and Micro Snitch.
Talos Linux ne supporte pas nativement l'authentification OIDC. Voici comment j'ai construit talosctl-oidc, un serveur d'échange de certificats éphémères qui ponte SSO et mTLS.
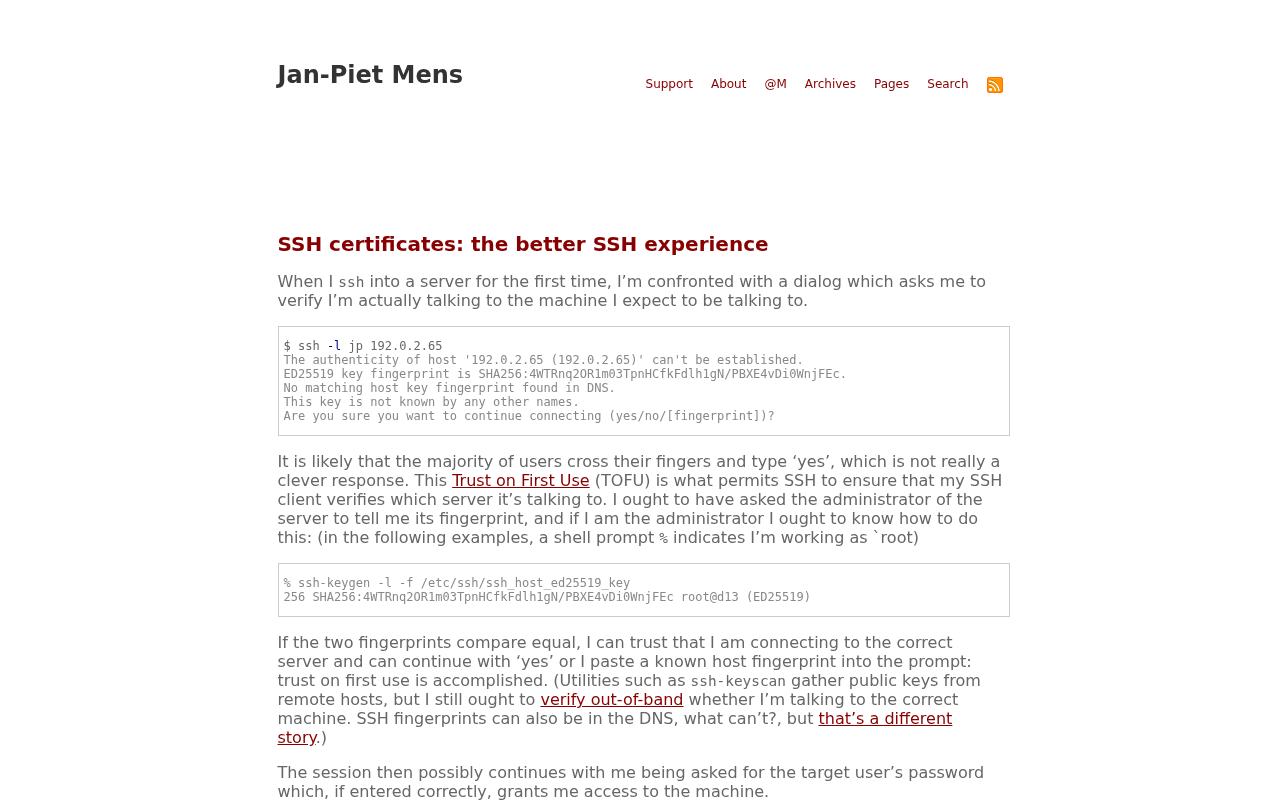
When Isshinto a server for the first time, I’m confronted with a dialog which asks me to verify I’m actually talking to the machine I expect to be talking to.
Today we are launching the beta of EmDash, a full-stack serverless JavaScript CMS built on Astro 6.0. It combines the features of a traditional CMS with modern security, running plugins in sandboxed Worker isolates.
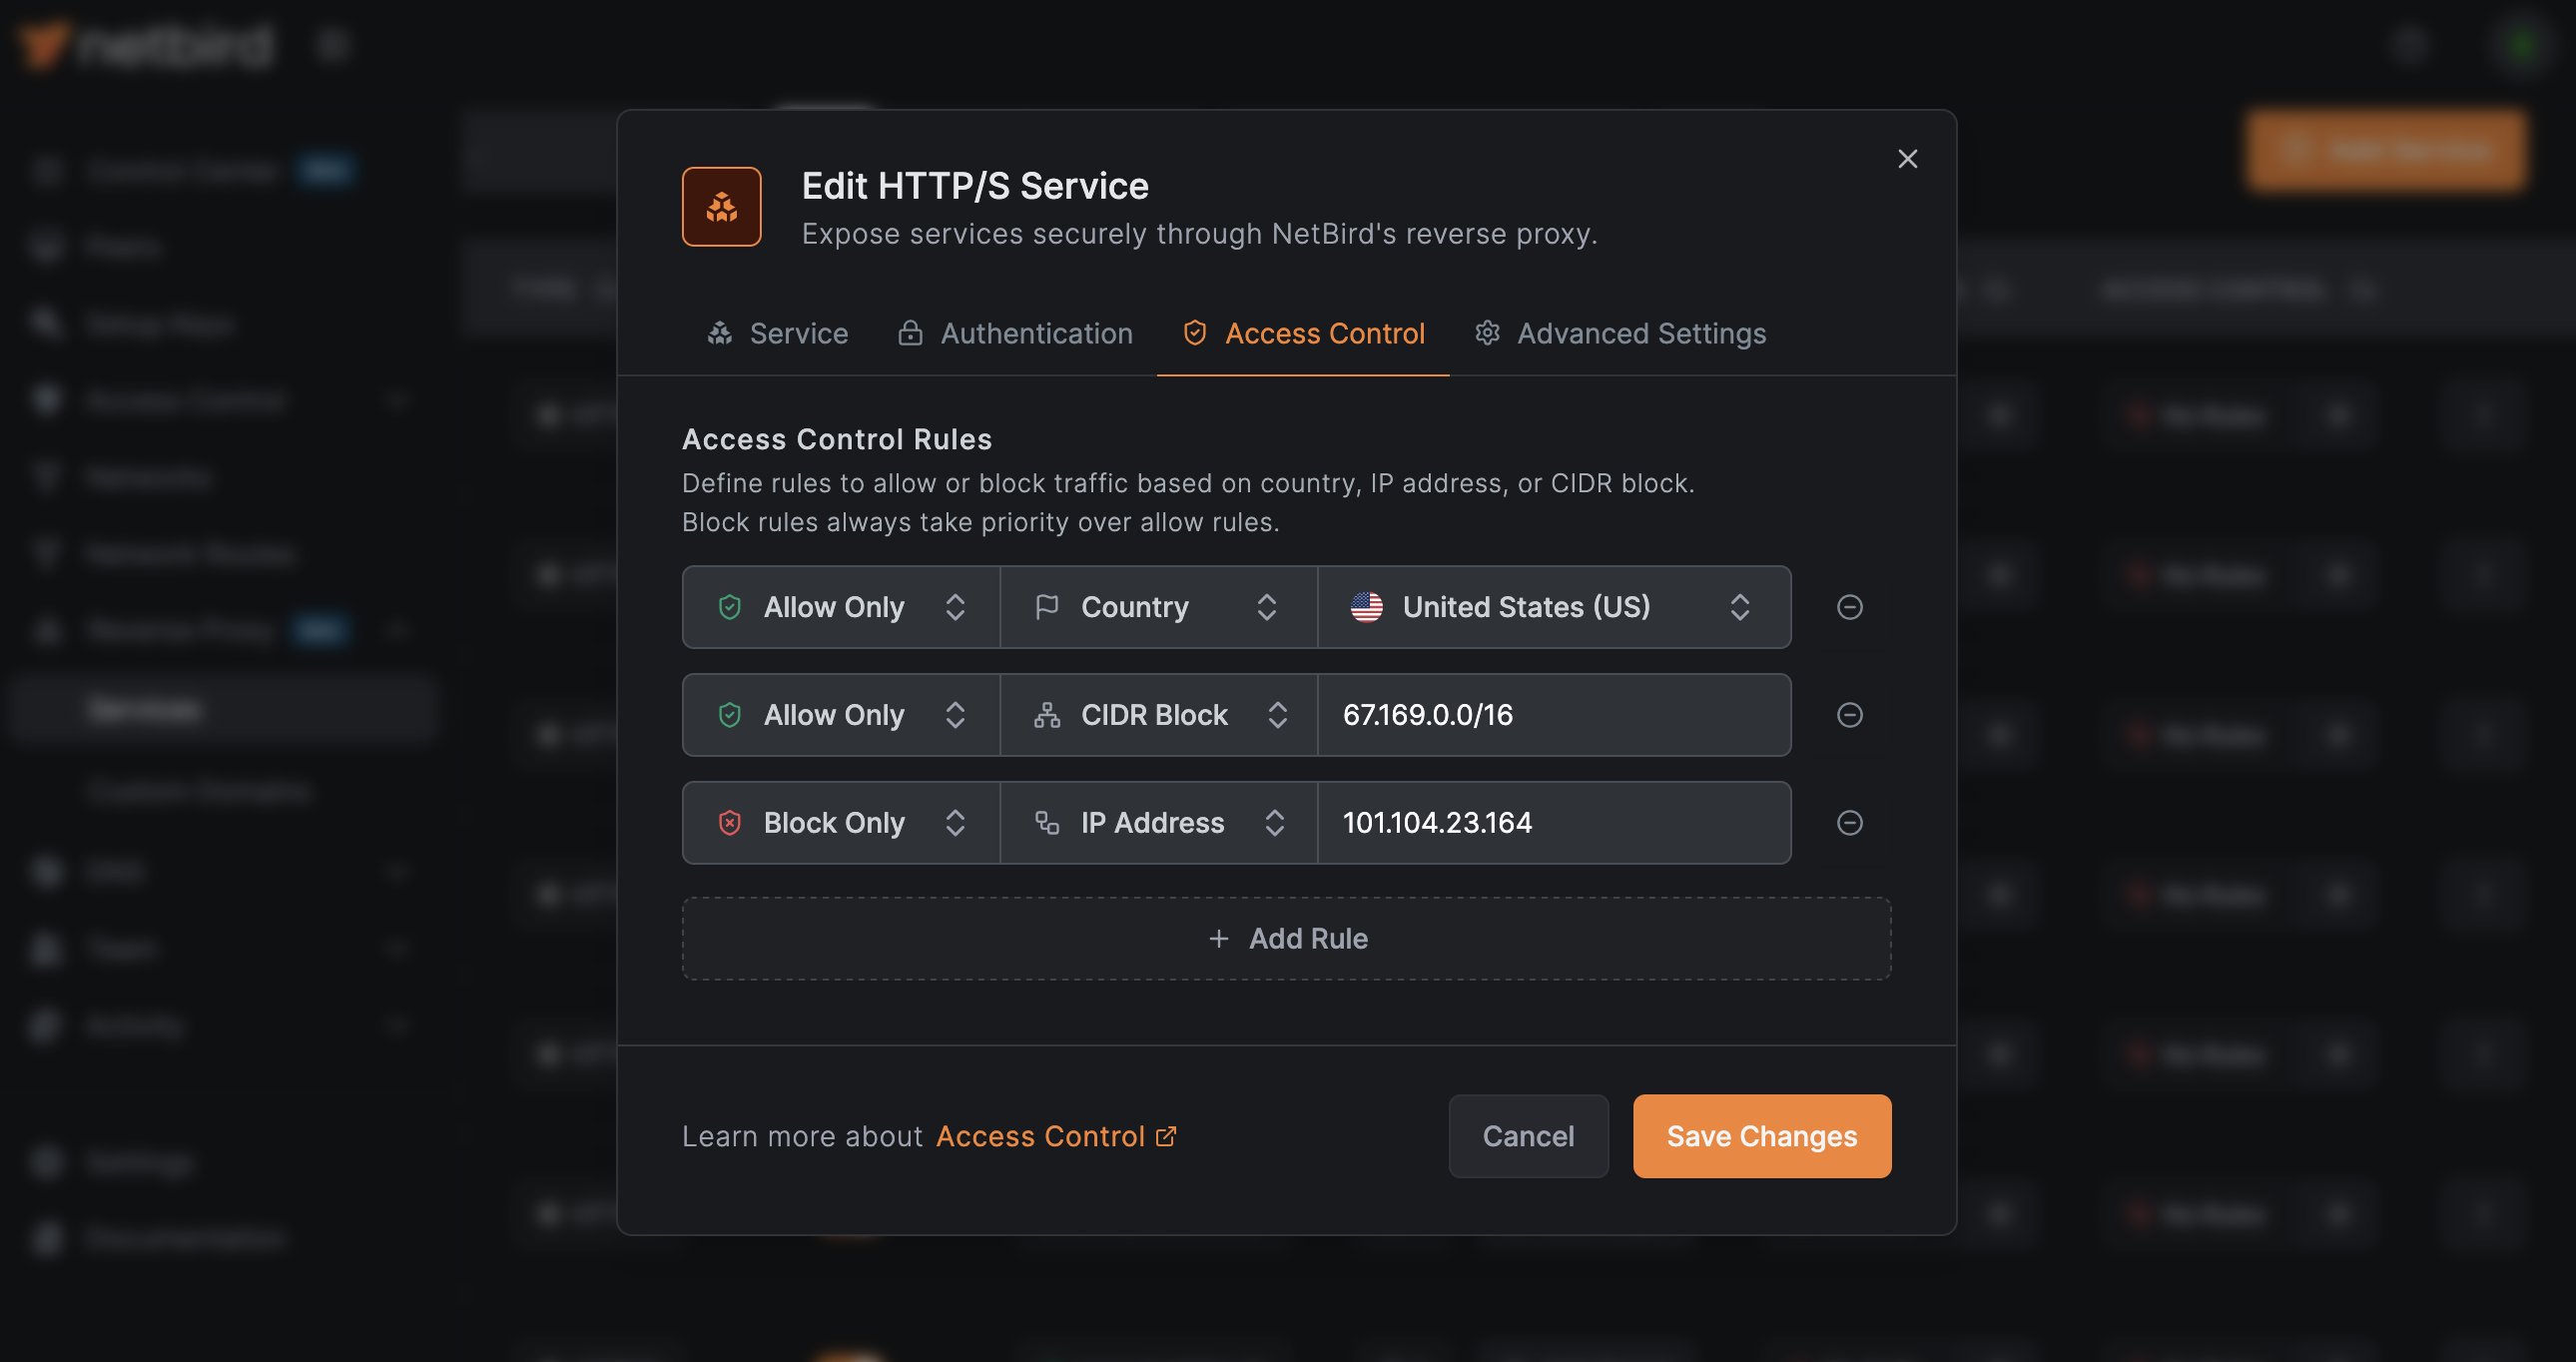
NetBird v0.67 brings Layer 4 proxy support to our reverse proxy! Expose TCP, UDP, and TLS services PLUS header-based auth, geo/IP access rules, client health checks, and more. https://netbird.io/knowledge-hub/l4-proxy
A 7-day package delay would have blocked installs in most short-lived malicious publish attacks from the last 8 years
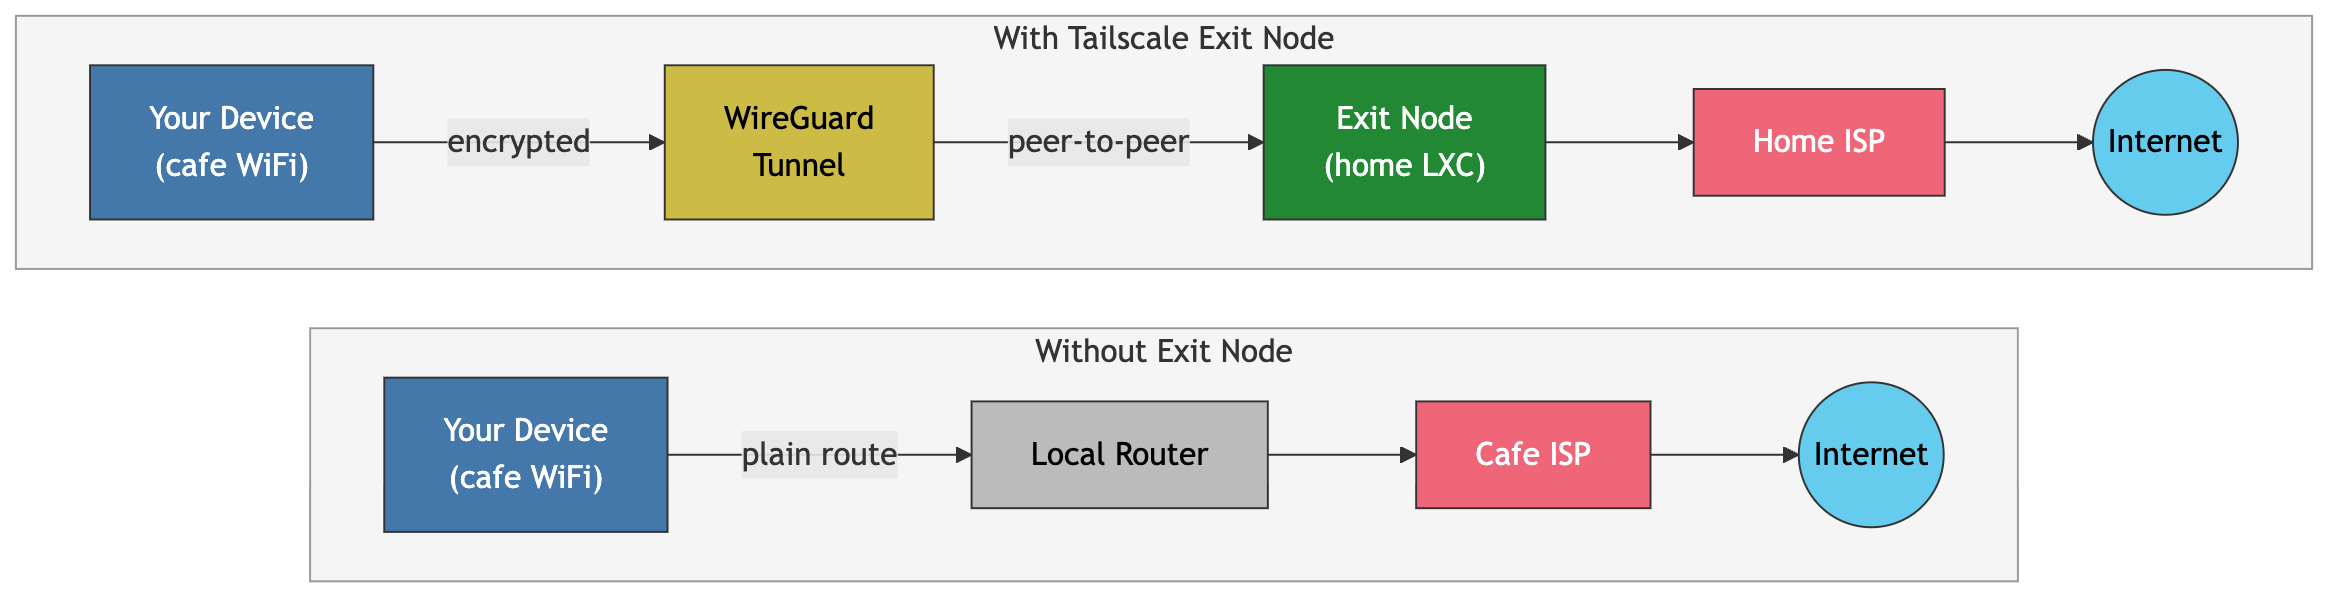
A practical deep dive into Tailscale exit nodes: route changes, traceroute evidence, DERP fallback, trust boundaries, and why this model can be free.
I run Coolify on a Hetzner bare metal server to host multiple web apps I have built and the services I use to maintain them. Of course almost none of my sites have any users, but I enjoy the process, and that is not here or there (but if you
Bitwarden Agent Access SDK integrates with OneCLI. Credentials stay in the vault, OneCLI proxies API calls and enforces policies. Agents never see keys.
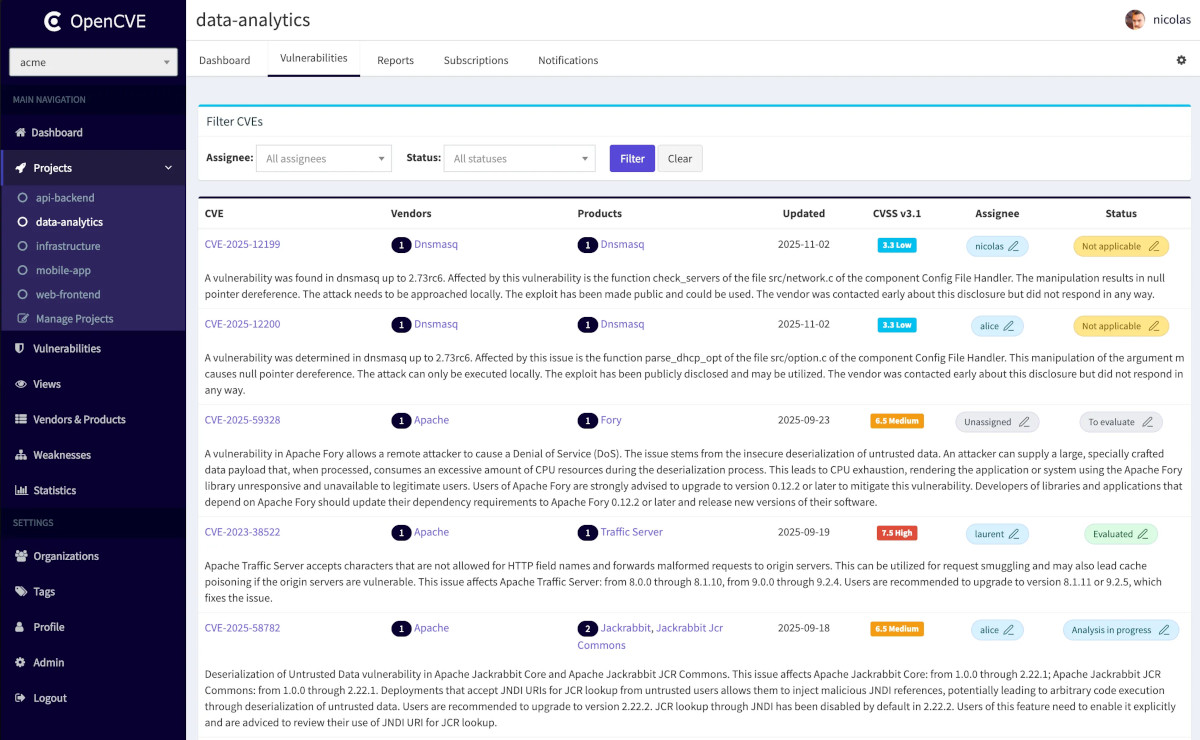
OpenCVE is a vulnerability intelligence platform that helps security teams monitor CVEs, track affected vendors, and receive real-time vulnerability alerts.
Every NanoClaw agent will access external services through OneCLI's Agent Vault, a gateway that handles credential injection, access policies, and approvals so agents never hold raw API keys.
The full Claude Code transcript from discovering and responding to the litellm 1.82.8 PyPI supply chain attack on March 24, 2026 — from mysterious process explosions to malware identification to public disclosure.
A survey of dependency cooldown support across package managers and update tools.
The web browser made for people, with love. Best privacy by default, unbiased ad-blocking, no bloat and no noise. Fully open source.
With VCF 9.0, Broadcom has announced the deprecation of the SDDC Manager UI, pushing Day-N workflows to the VCF Operations Console. In this post we explore what password management looks like in the new console, what capabilities have landed including Update, Remediate and a polished filtering experience, and what still requires SDDC Manager directly such as Rotate, scheduled auto-rotation and credential retrieval via the API
Get started with Hostinger VPS: https://hostinger.com/LEMPA10 — use code LEMPA10 for 10% off
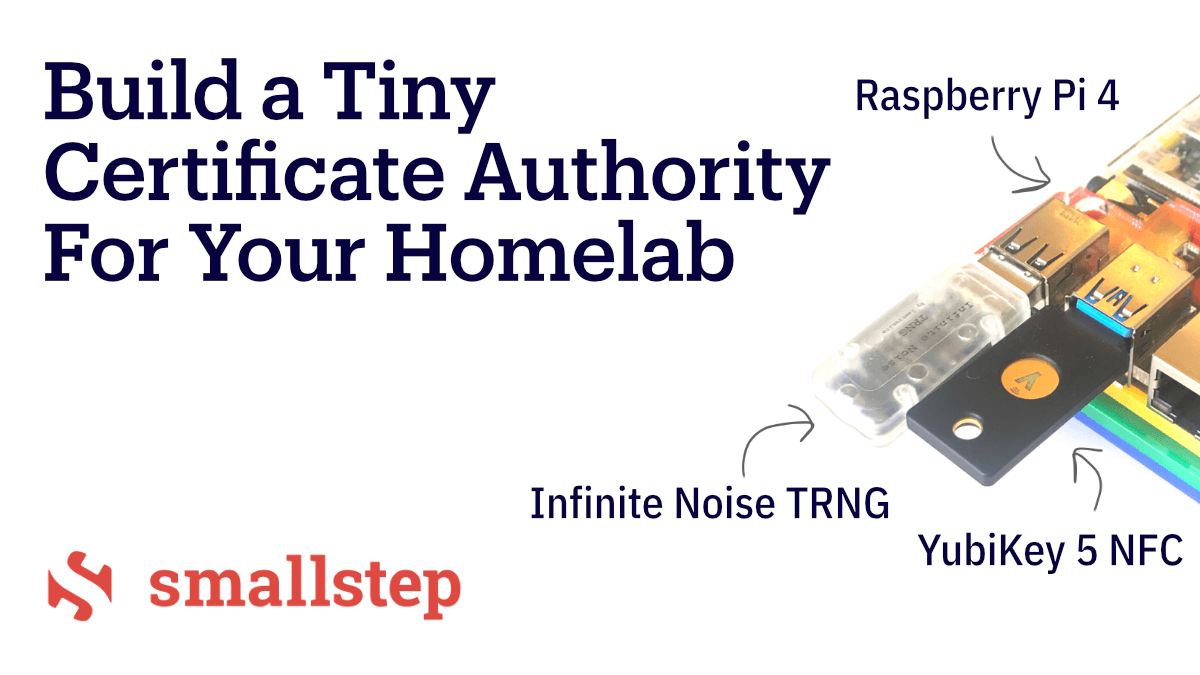
Let's make a tiny, standalone CA! We'll use a Raspberry Pi 4, YubiKey 5 NFC, and Infinite Noise TRNG.
Introduction
Knock Knock Knock ! Connaissez-vous le port knocking ?
Le tocage à la porte, ou port-knocking, est une méthode...
The biggest shock of my early career was just how much code I needed to read that others wrote. I had never dealt with this. I had a hard enough time understanding my own code. The idea of understandi
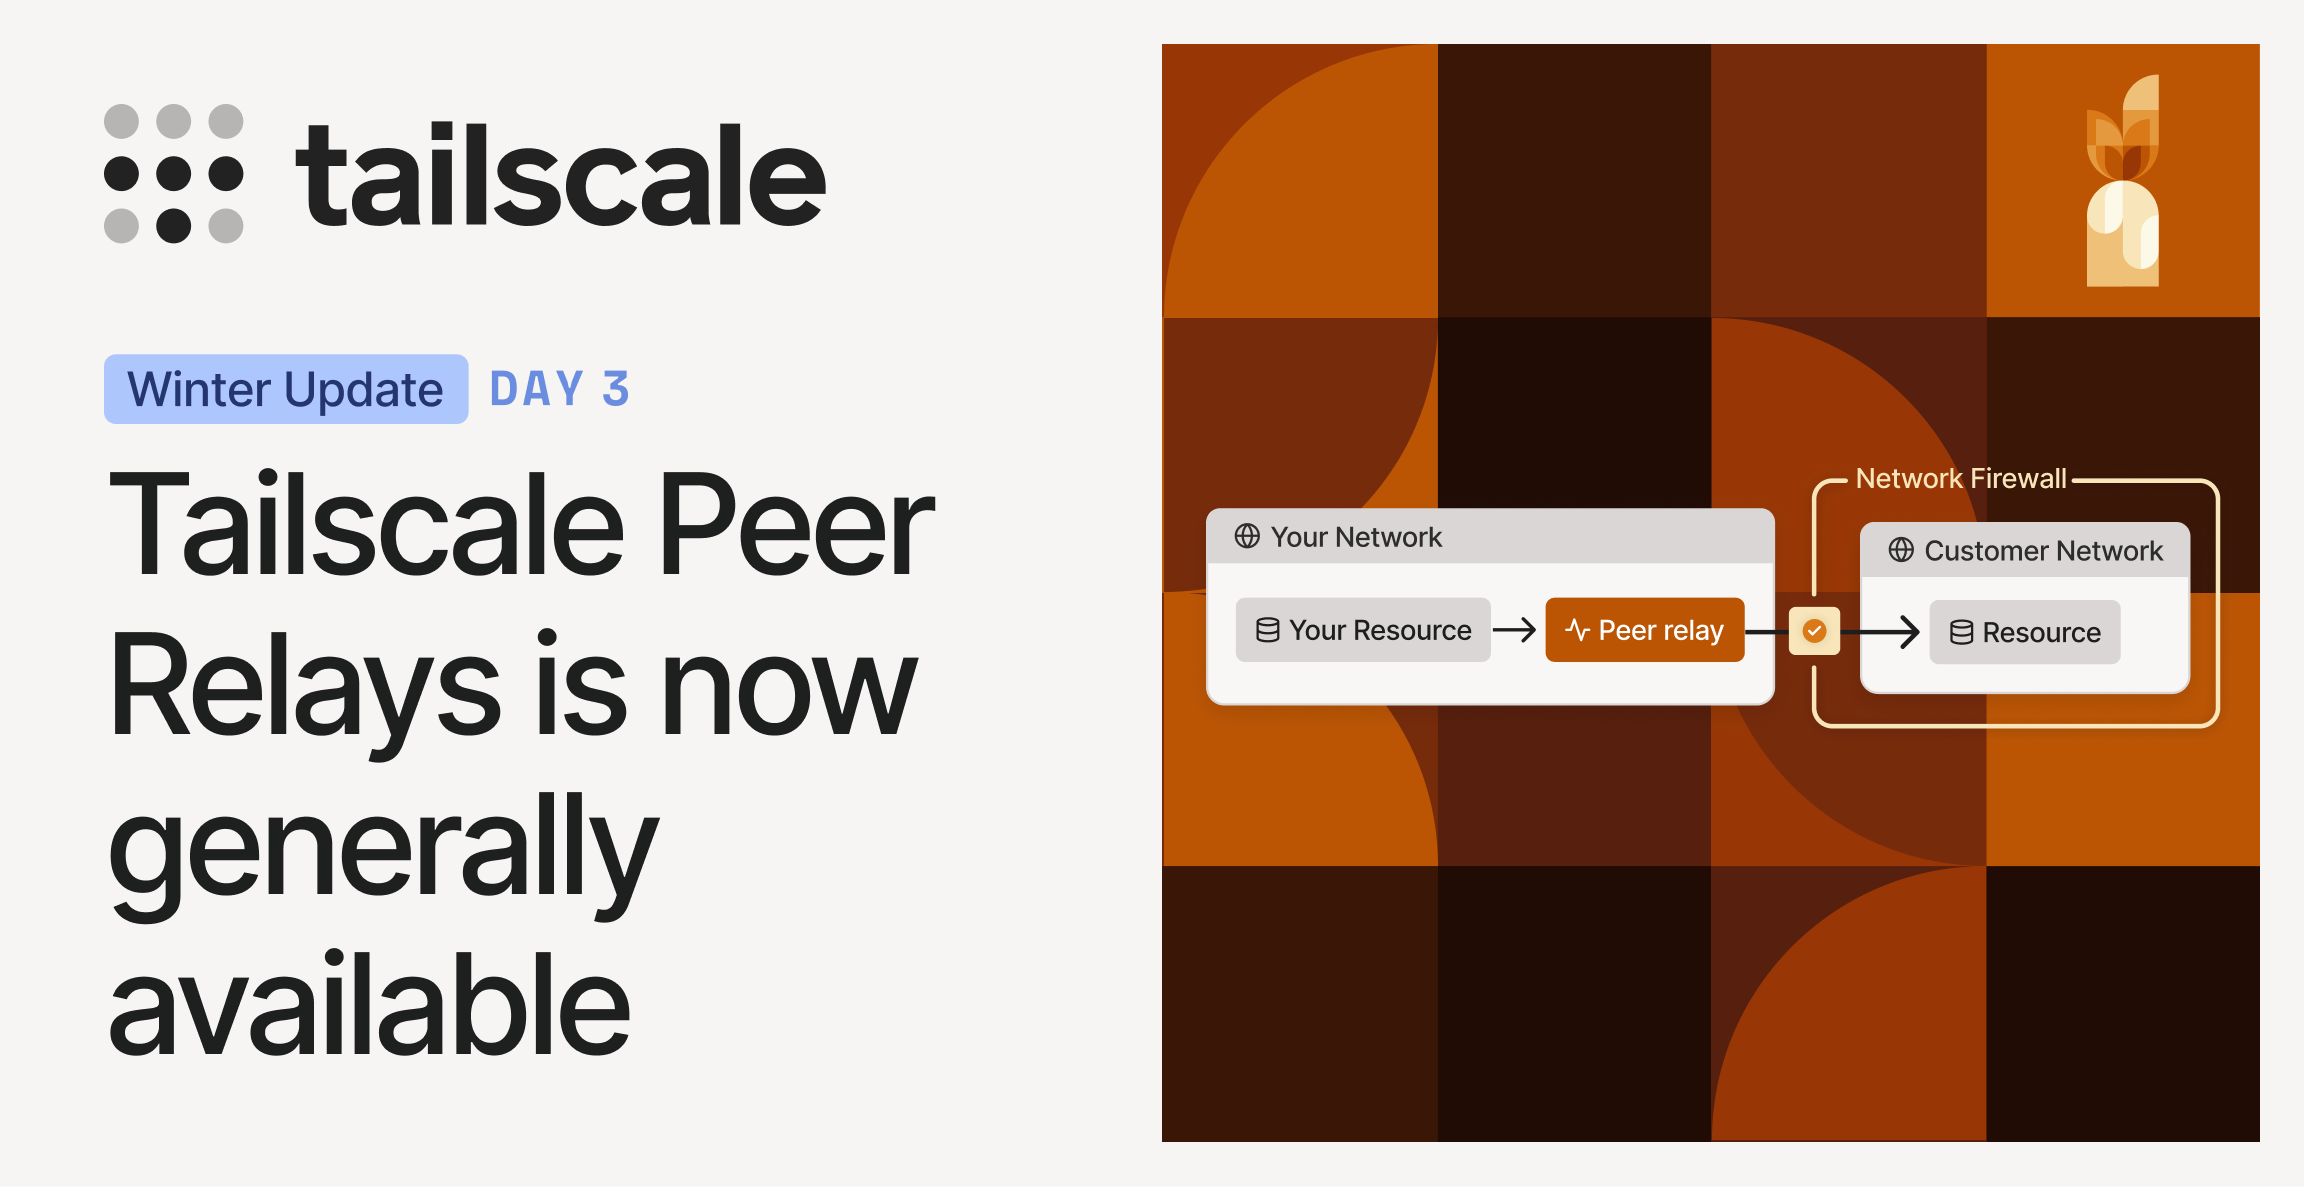
Work around hard NATs and tricky networks with production-grade connectivity nodes you control
When you request a certificate from Let’s Encrypt, our servers validate that you control the hostnames in that certificate using ACME challenges. For subscribers who need wildcard certificates or who prefer not to expose infrastructure to the public Internet, the DNS-01 challenge type has long been the only choice. DNS-01 works well. It is widely supported and battle-tested, but it comes with operational costs: DNS propagation delays, recurring DNS updates at renewal time, and automation that often requires distributing DNS credentials throughout your infrastructure.
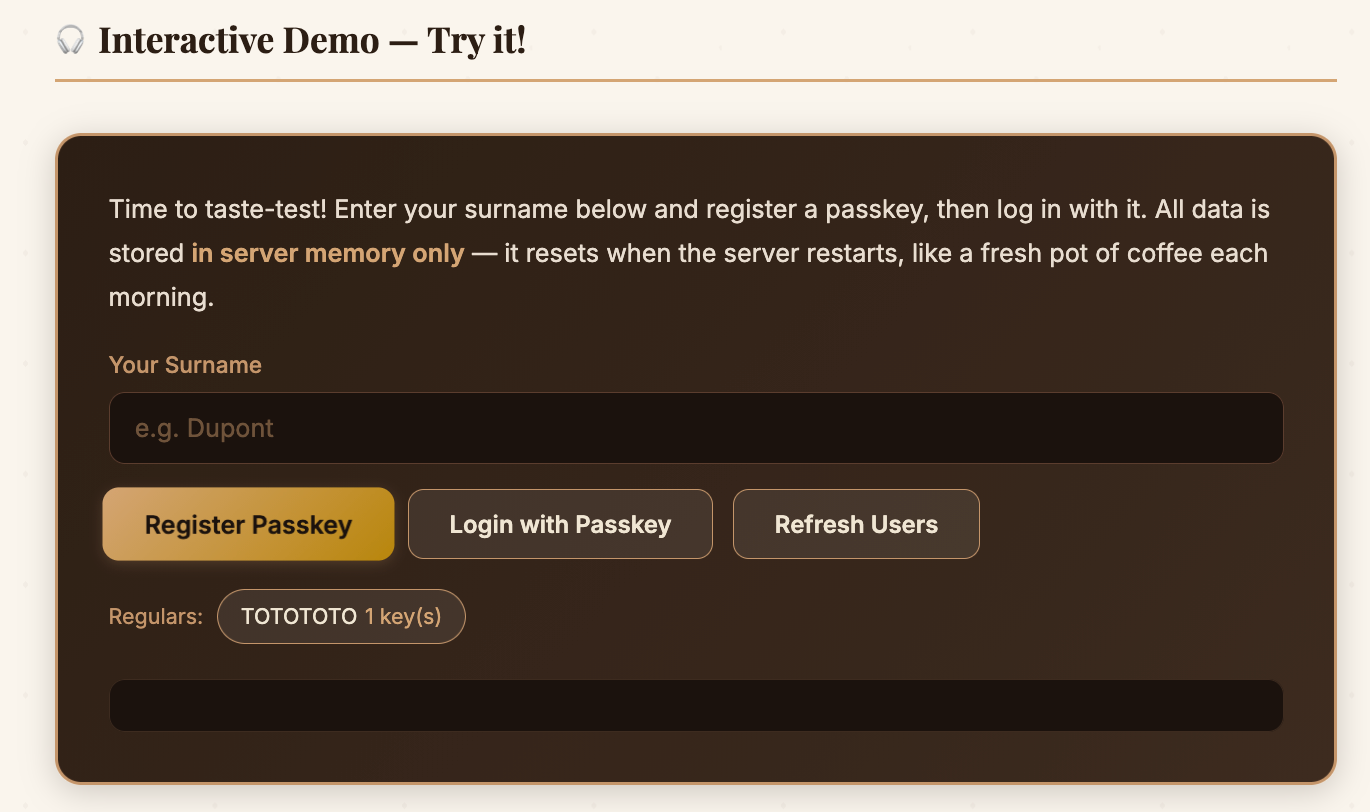
Learn how passkeys work with interactive diagrams and a hands-on WebAuthn demo. From cryptography to code, all explained over a cup of coffee.
You never have to see comments again if you don't want to.
Give LLM agents shell access without risking your host system. A practical libvirt guide covering VM creation, snapshots for safe experimentation, and remote access options.
On January 14, 2026, global telnet traffic observed by GreyNoise sensors fell off a cliff. A 59% sustained reduction, eighteen ASNs going completely silent, five countries vanishing from our data entirely. Six days later, CVE-2026-24061 dropped. Coincidence is one explanation.
Comment j'ai obtenu mon propre ASN et utilisé BGP pour annoncer des routes IPv6 depuis chez moi.
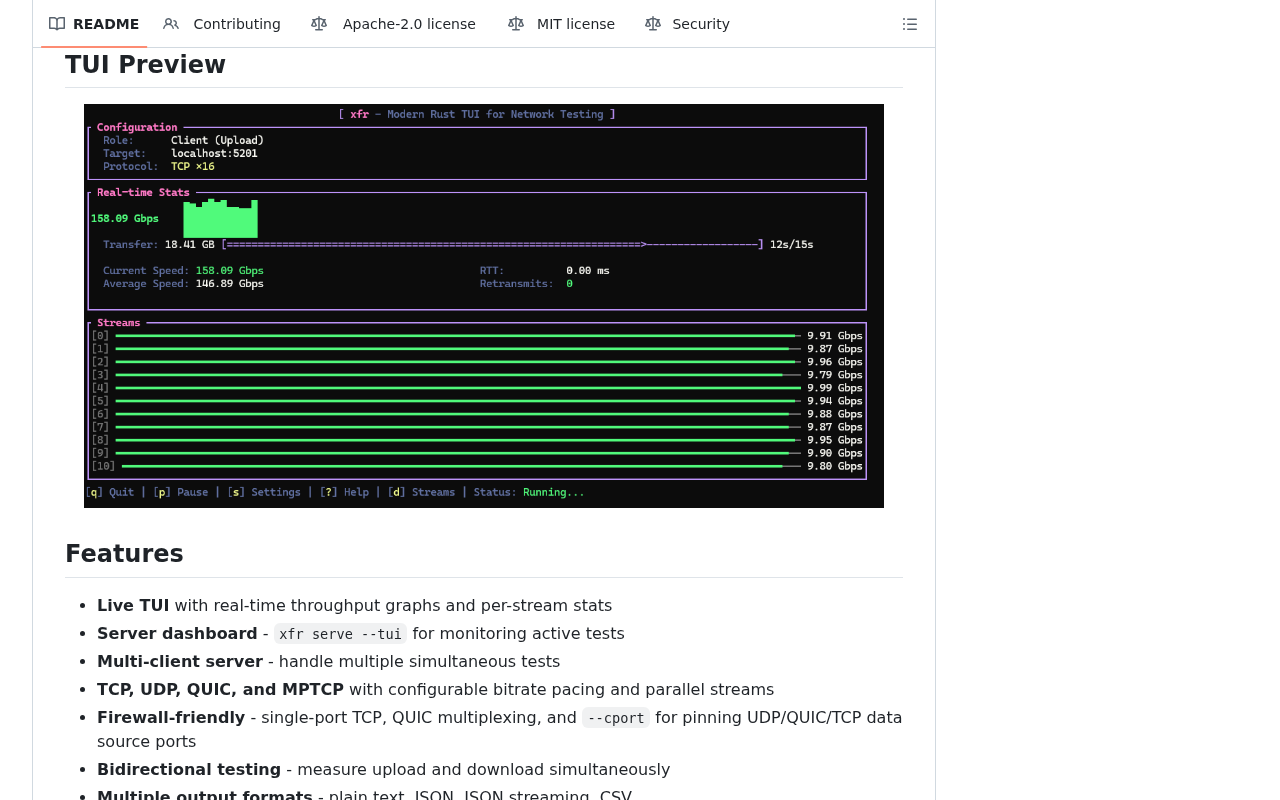
A modern iperf3 alternative with a live TUI, multi-client server, and QUIC support. Built in Rust. - lance0/xfr
Author: Nemanja Ilic
We built an open-source proxy that adds tenant isolation to Prometheus, Loki, and Tempo by rewriting queries based on user identity.
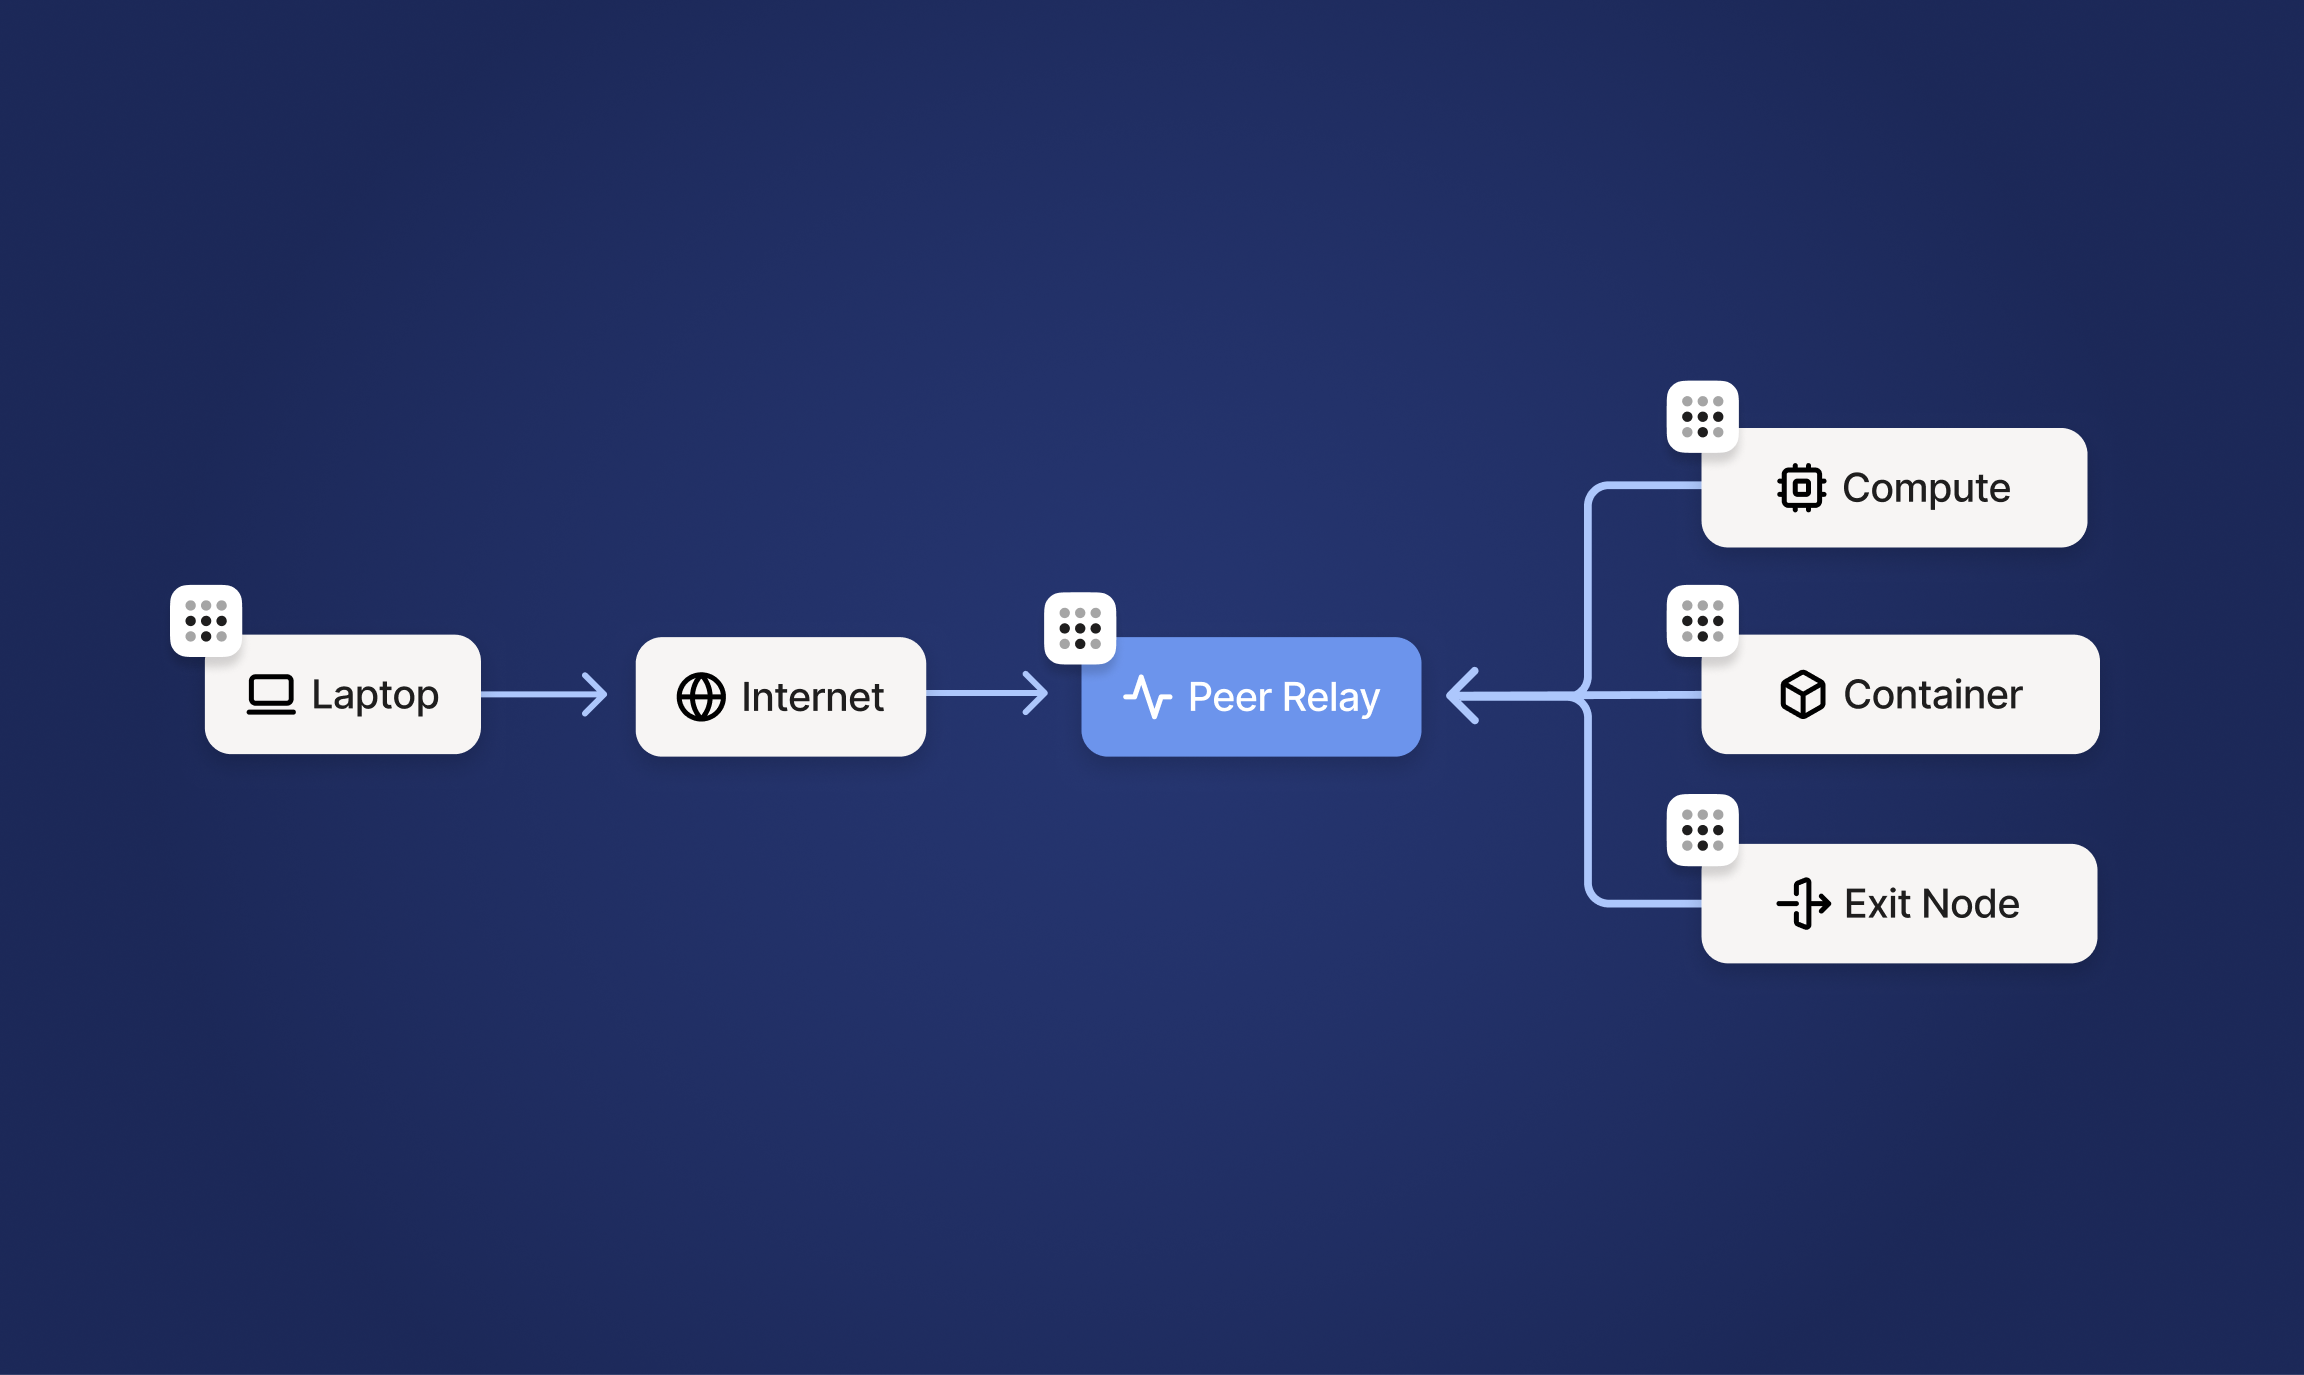
Getting from Delhi back to a Minnesota meant unforgiving networks. Tailscale Peer Relays offered a massive improvement.
Learn how requests flow through the Kubernetes API server — from authentication to etcd storage.
Today is a big day for us, and for everyone who cares about transparency, privacy, and having full control over their own traffic. We’re finally open-sourcing the protocol that powers AdGuard VPN. And it now has a name: TrustTunnel.
●
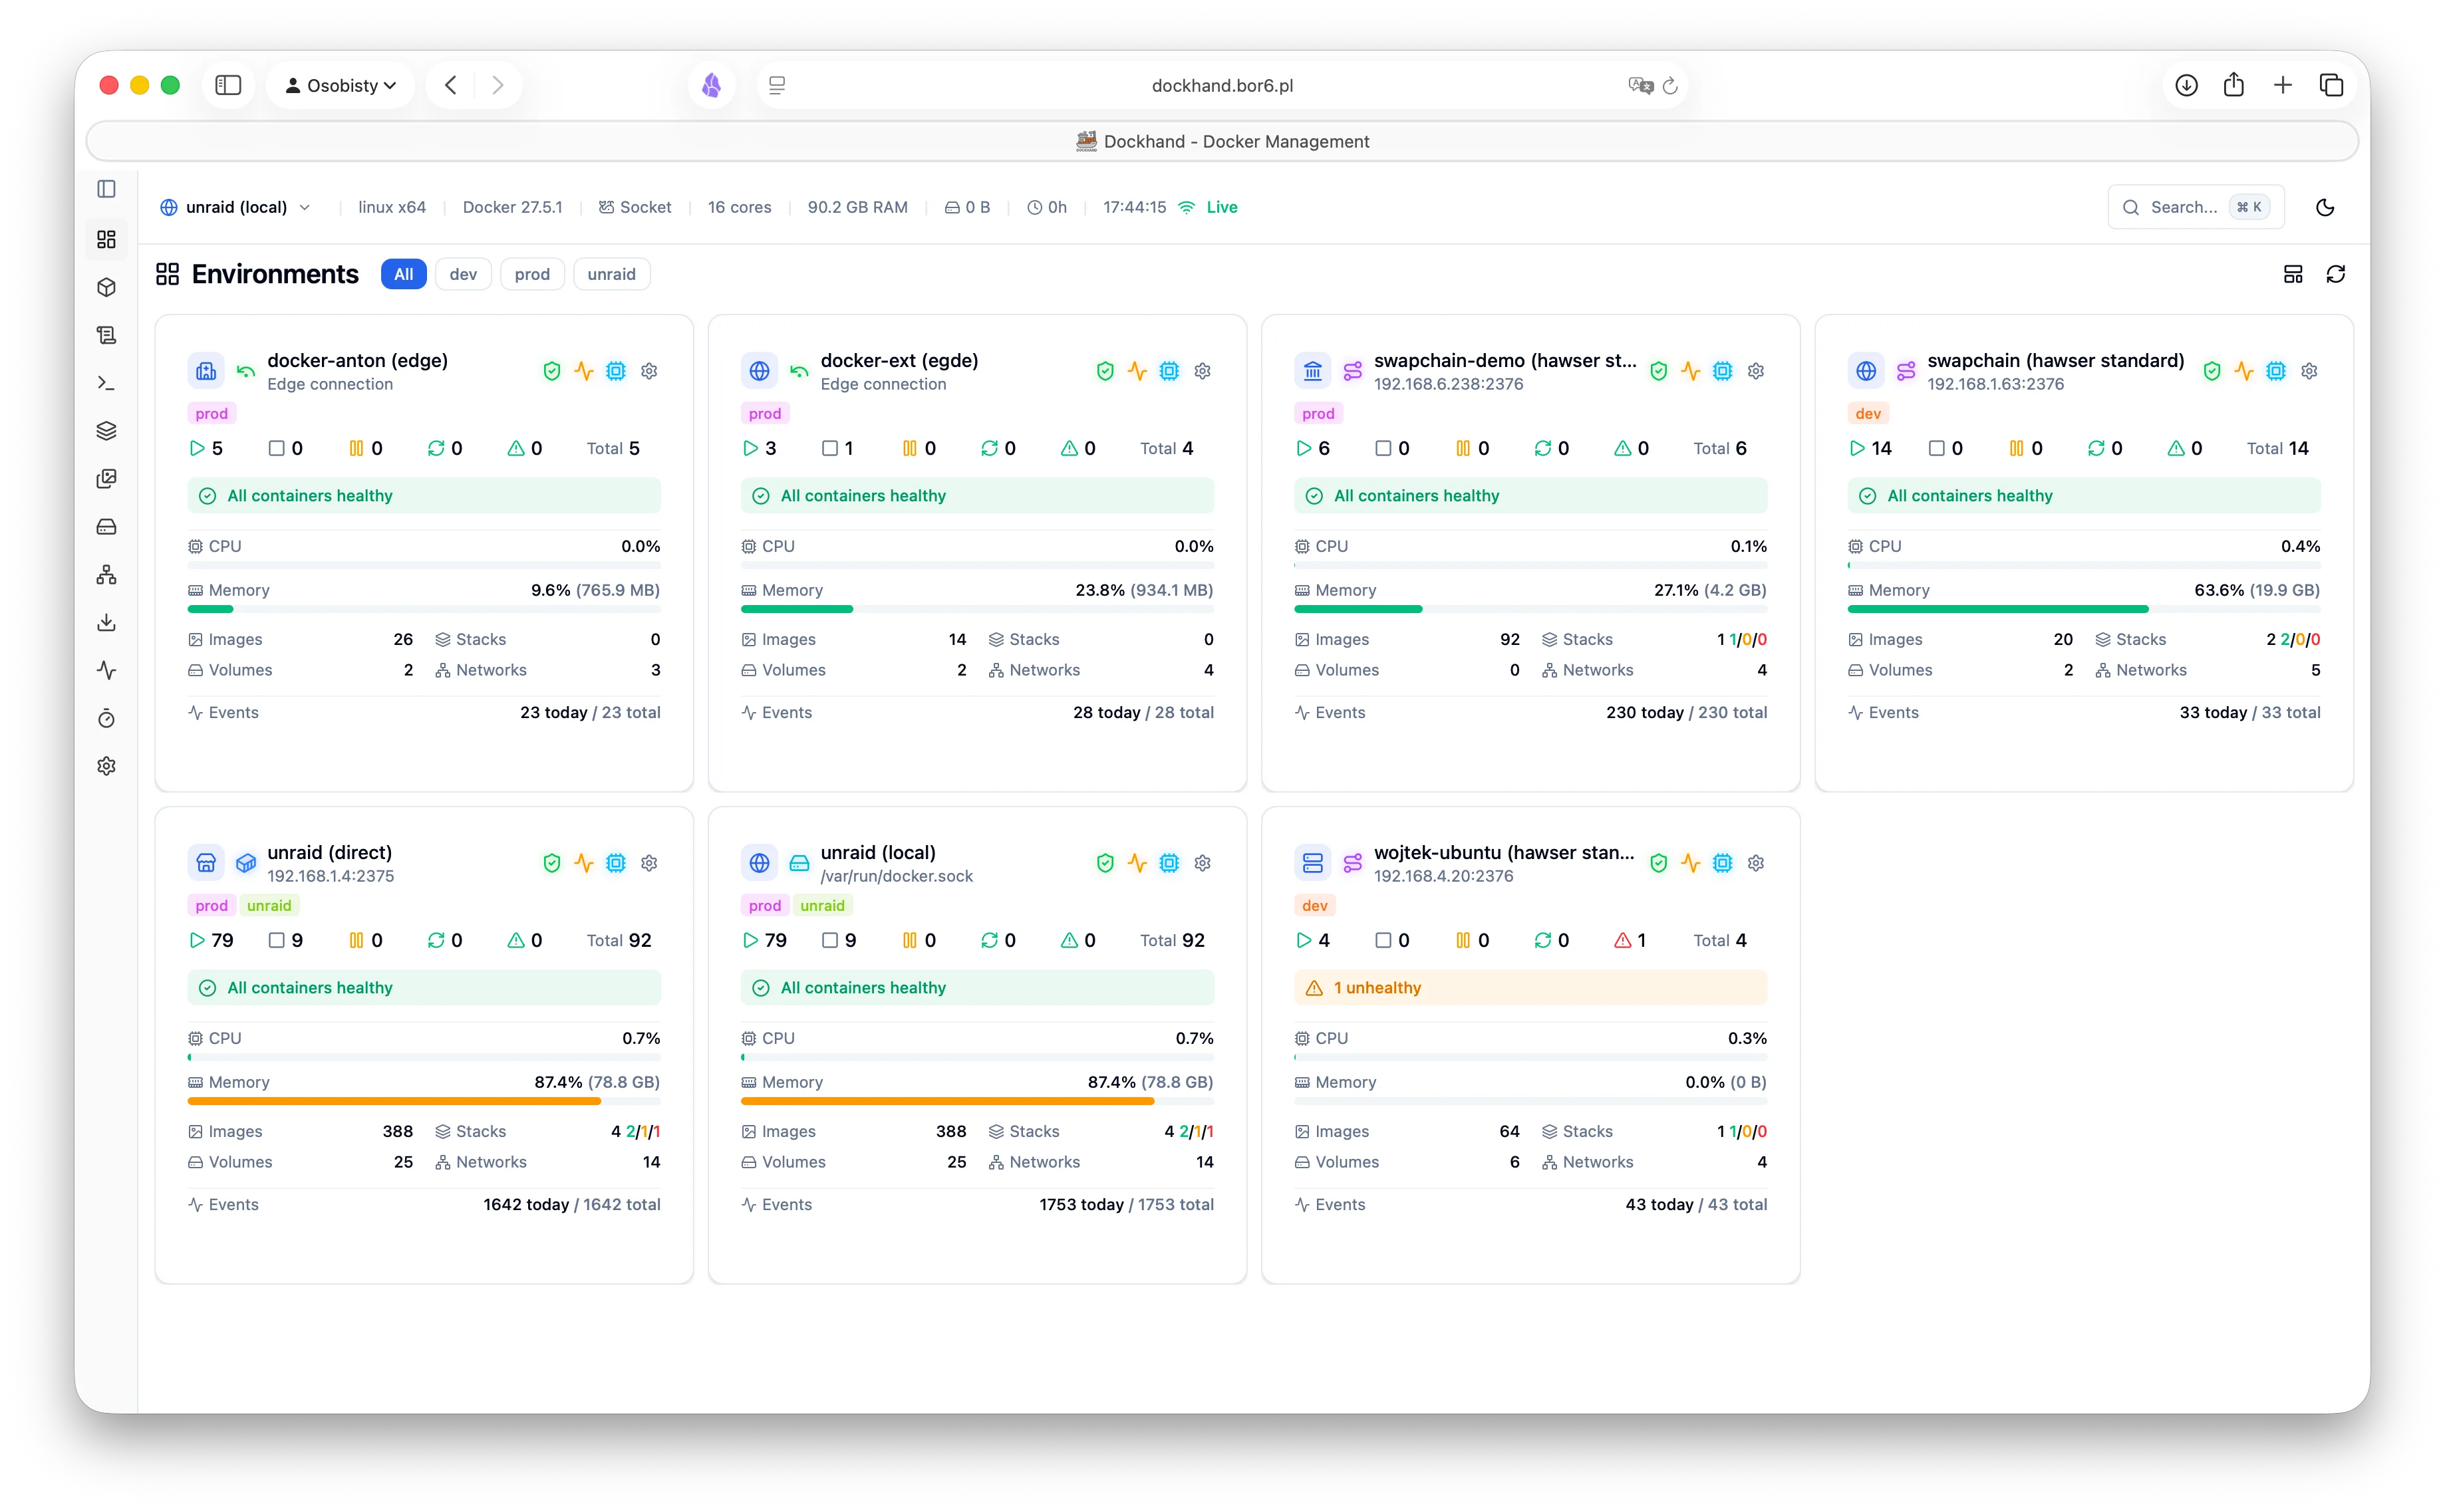
A powerful, intuitive Docker platform for everyone. Real-time container management, Compose stacks, Git deployments, and SSO - all free.
 > **Disclosure**: This article documents security research ...
An inspection of Claude Code's network requests, system prompt, and context handling by intercepting real traffic.
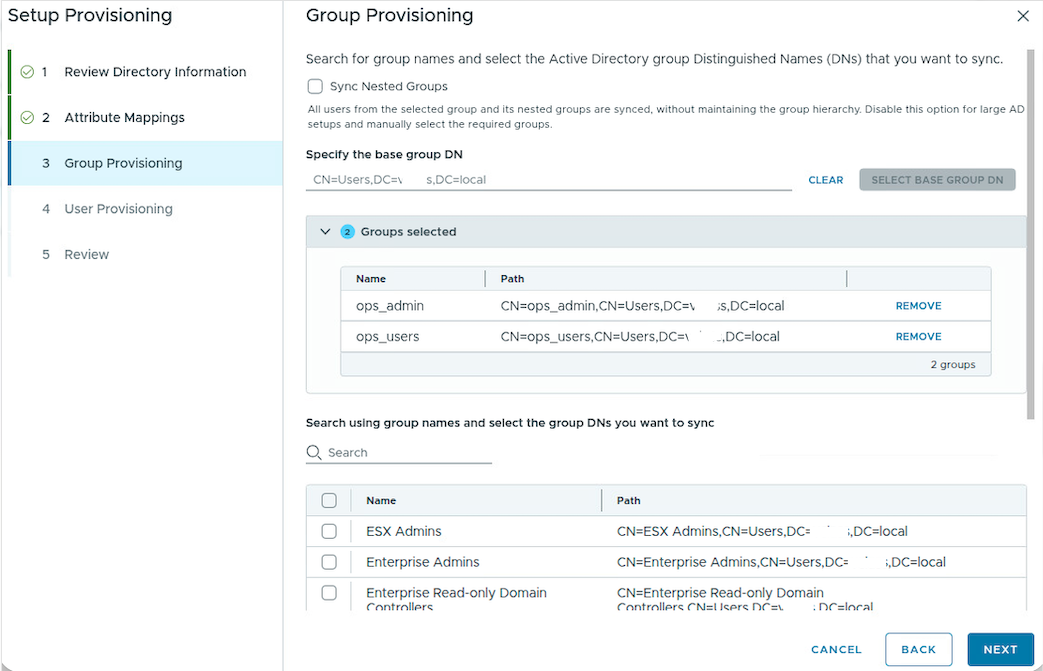
In VMware Cloud Foundation (VCF) 9.0, identity management takes a leap forward with the introduction of the VCF Identity Broker (VIDB)—a modern, flexible solution for enabling Single Sign-On (SSO) …
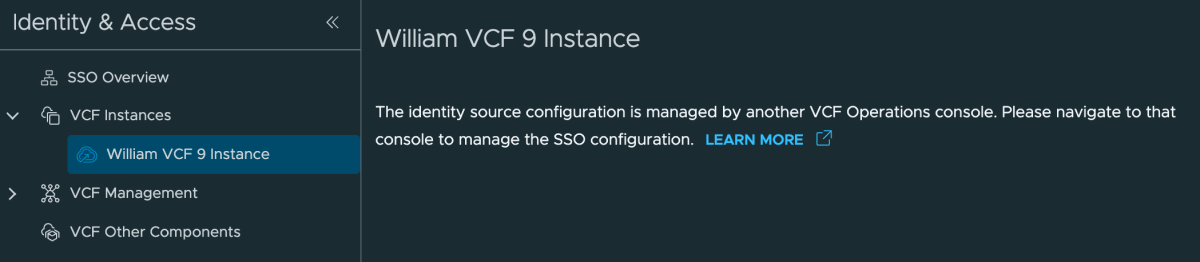
Over the holidays, I was testing some new VMware Cloud Foundation (VCF) upgrade flows in my lab environment, where I ended up bricking SDDC Manager, which was completely my fault! While I had backu…
This post explains how I operate my homelab with no public WAN exposure, using WireGuard to stay permanently connected to my home network from all my devices, …
“Bye bye bye.” It took some time, and a serious amount of research, but I have finally crossed the finish line. I have officially migrated my digital life to pure, EU-hosted solutions.
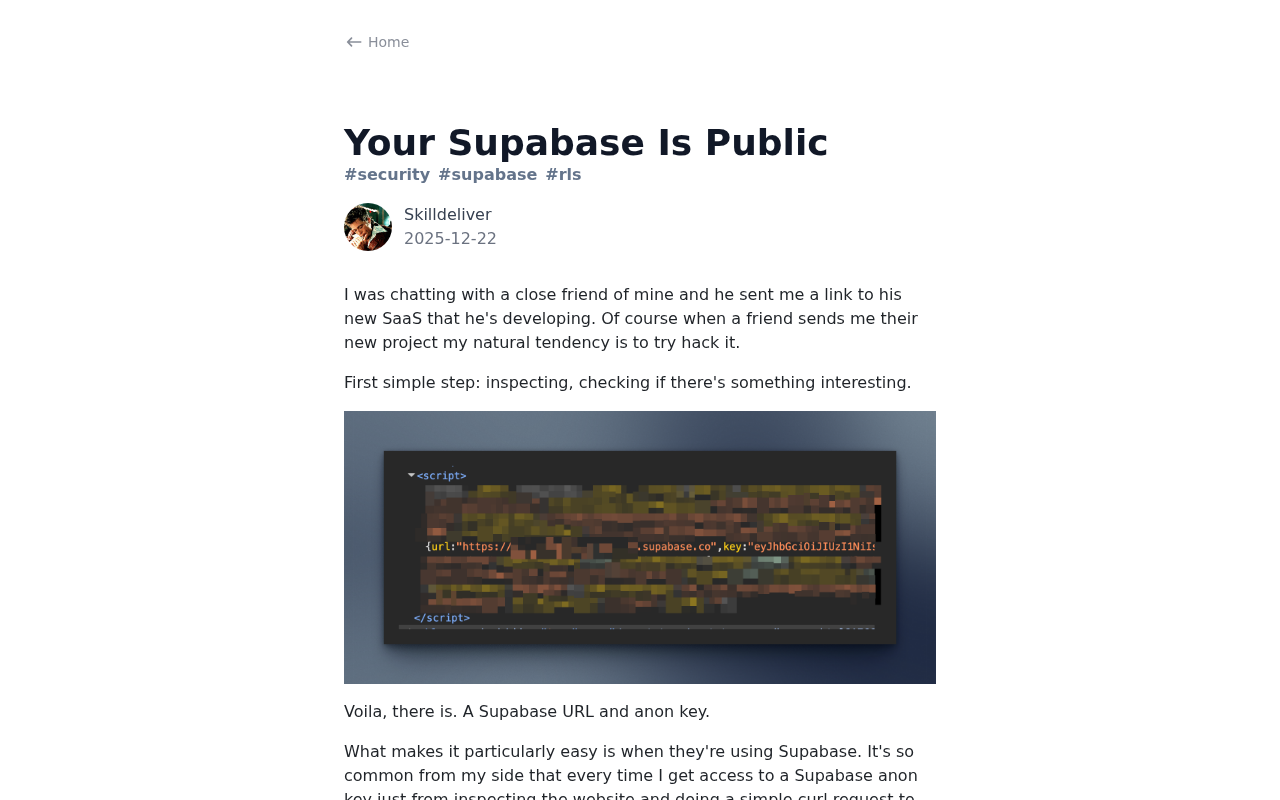
I was chatting with a close friend of mine and he sent me a link to his new SaaS that he's developing.
Userspace WireGuard® Implementation in Rust. Contribute to mullvad/gotatun development by creating an account on GitHub.
I got hacked, my server started mining Monero this morning.
Firstyear's blog
Brian Scott made an app that's safe, simple, and educational for kids to chat in, using Tailscale's tsnet and connectivity.
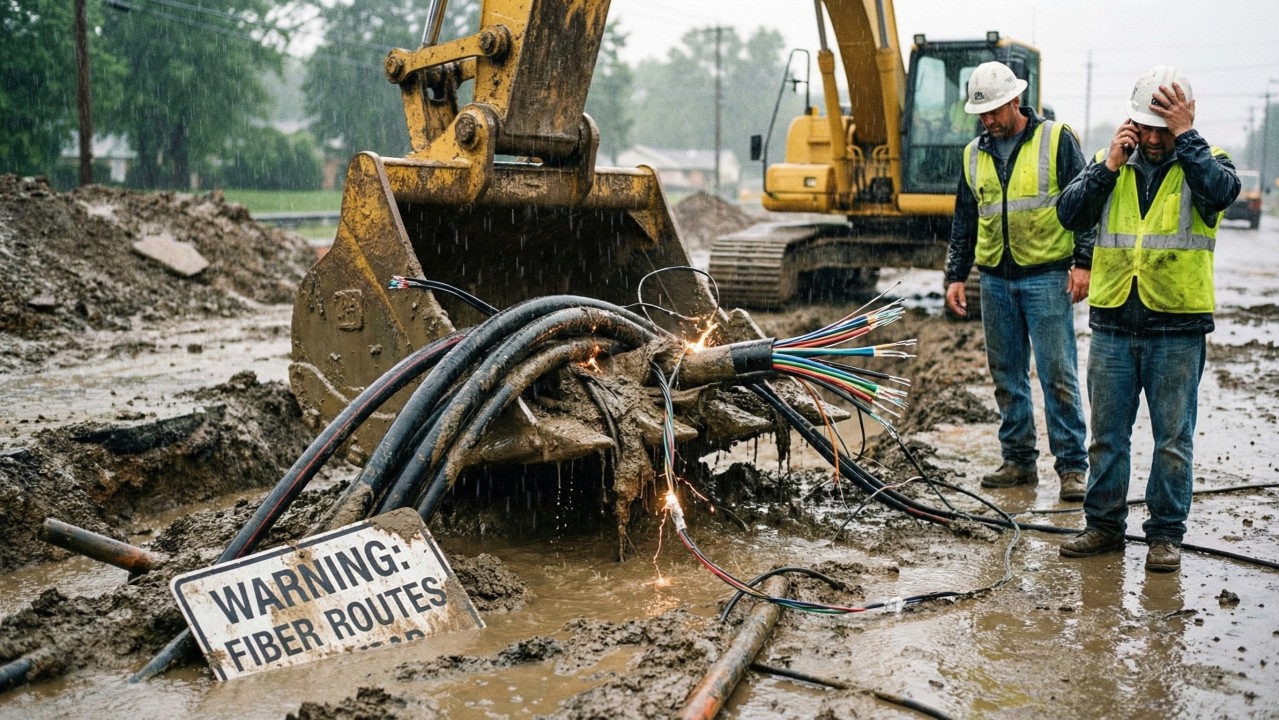
The Excavator Doesn't Care About Your Diversity We'd done everything right. Diverse and multiple fiber paths to our remote site.
Lately, I’ve been spending a lot of time getting our company lab set up and configured with all the bells and whistles that VCF 9 brings to the table. The new SSO experience was something I was really looking forward to. Previously, you had to configure the identity provider for every single product and platform, then add in the permissions and then manage that connection seperately. The new SSO experience, powered by the all new Identity Broker, is supposed to alleviate a lot of that management overhead.
Cloudflare suffered a service outage on November 18, 2025. The outage was triggered by a bug in generation logic for a Bot Management feature file causing many Cloudflare services to be affected.
Kasm Workspaces delivers zero-trust remote browser isolation (RBI), desktop as a service (DaaS) and open-source intelligence (OSINT) workloads to the web browser.
Kasm Workspaces delivers zero-trust remote browser isolation, Desktop as a Service (DaaS), and OSINT workloads to your web browser.
💚 Secure remote browsing anywhere. . Contribute to BrowserBox/BrowserBox development by creating an account on GitHub.
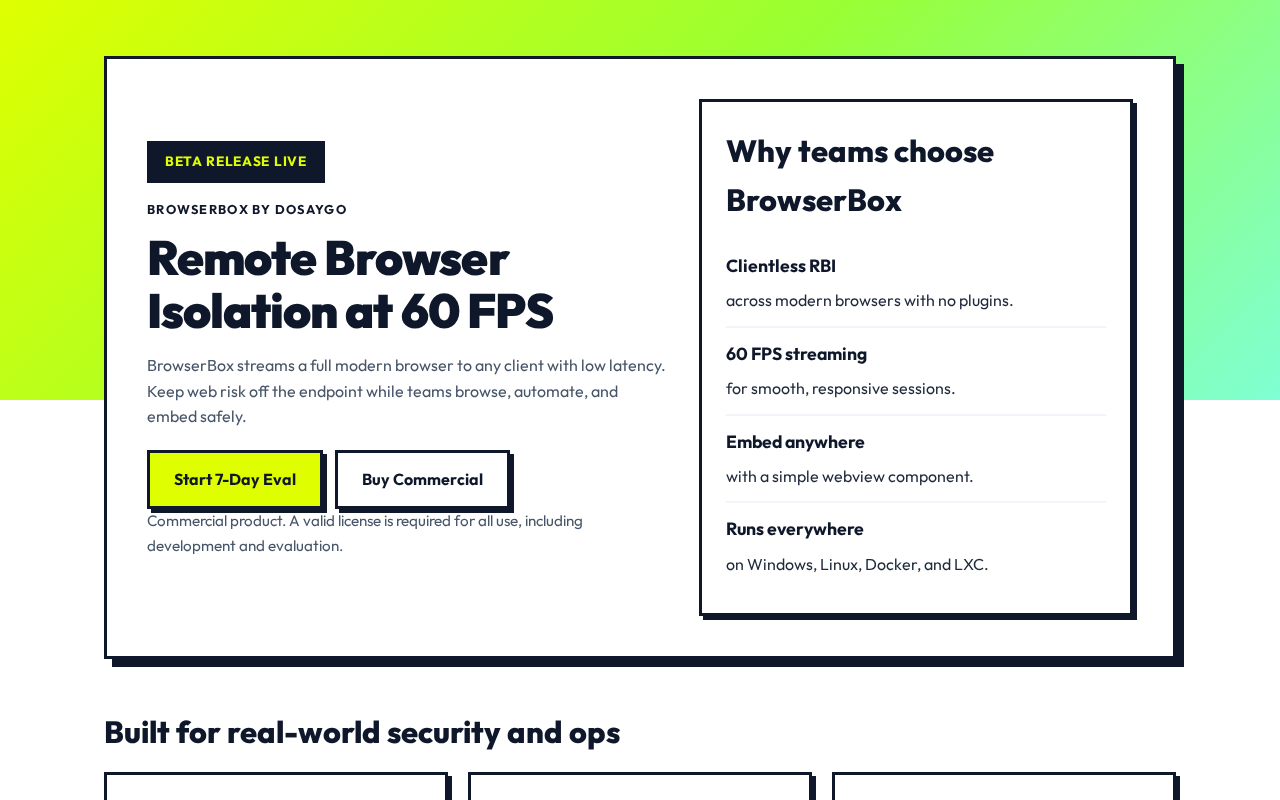
BrowserBox streams a full modern browser to any client with low latency. Keep web risk off the endpoint while teams browse, automate, and embed safely.
Windows 11 now supports 1Password and Bitwarden passkeys, enabling faster, safer, and passwordless sign-ins across devices.
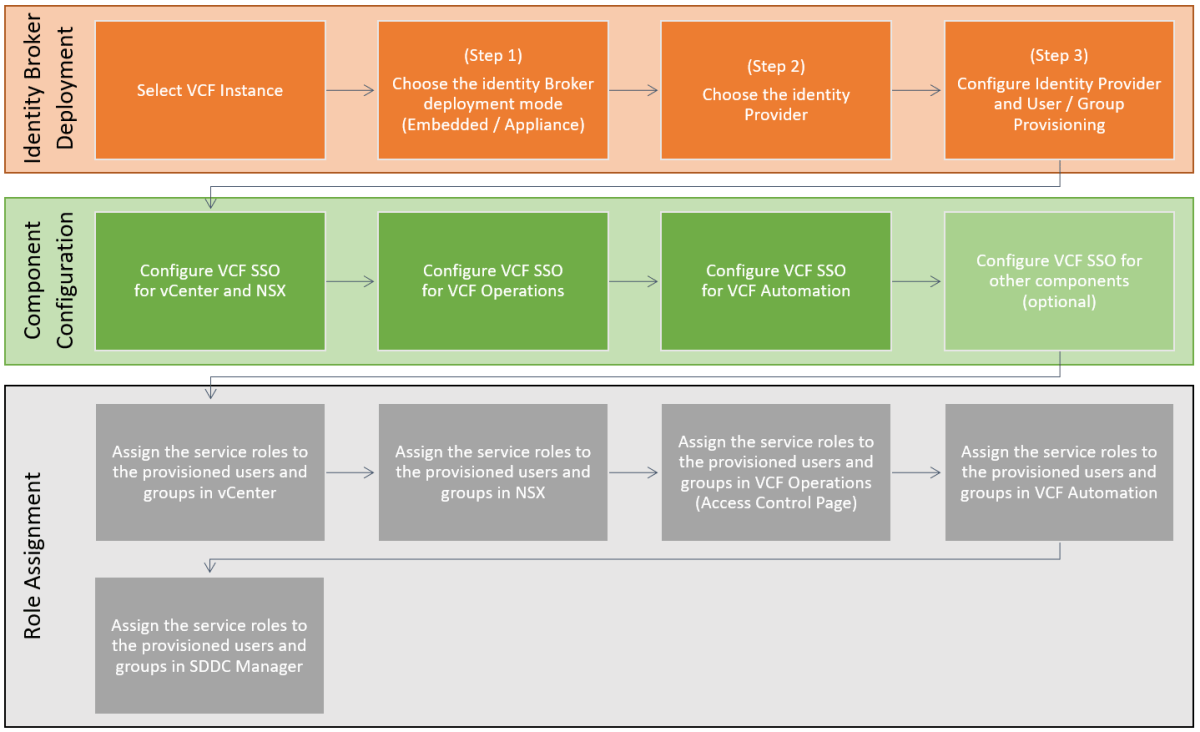
Phase 3: Role AssignmentAssign the service roles in vCenterAssign the service roles in NSXAssign the service roles in VCF OperationsAssign the service roles in VCF AutomationAssign the service role…
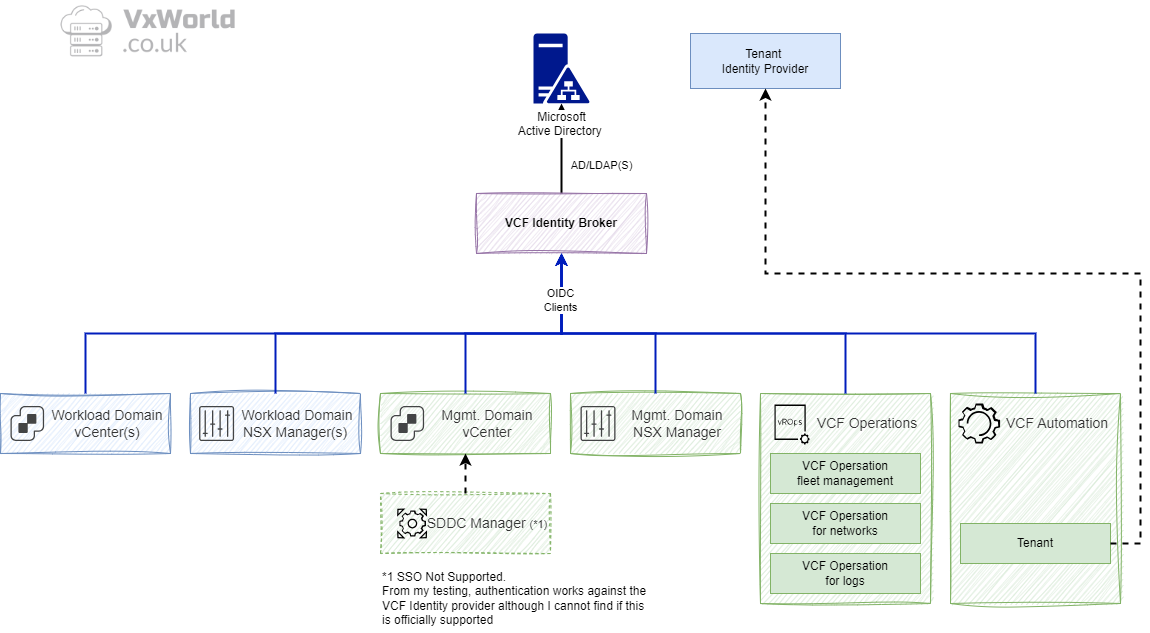
In VCF 9, VMware introduces a major shift in Single Sign-On (SSO) architecture via the new “Identity Broker” service. This change not only consolidates identity management across the VCF stack, but…
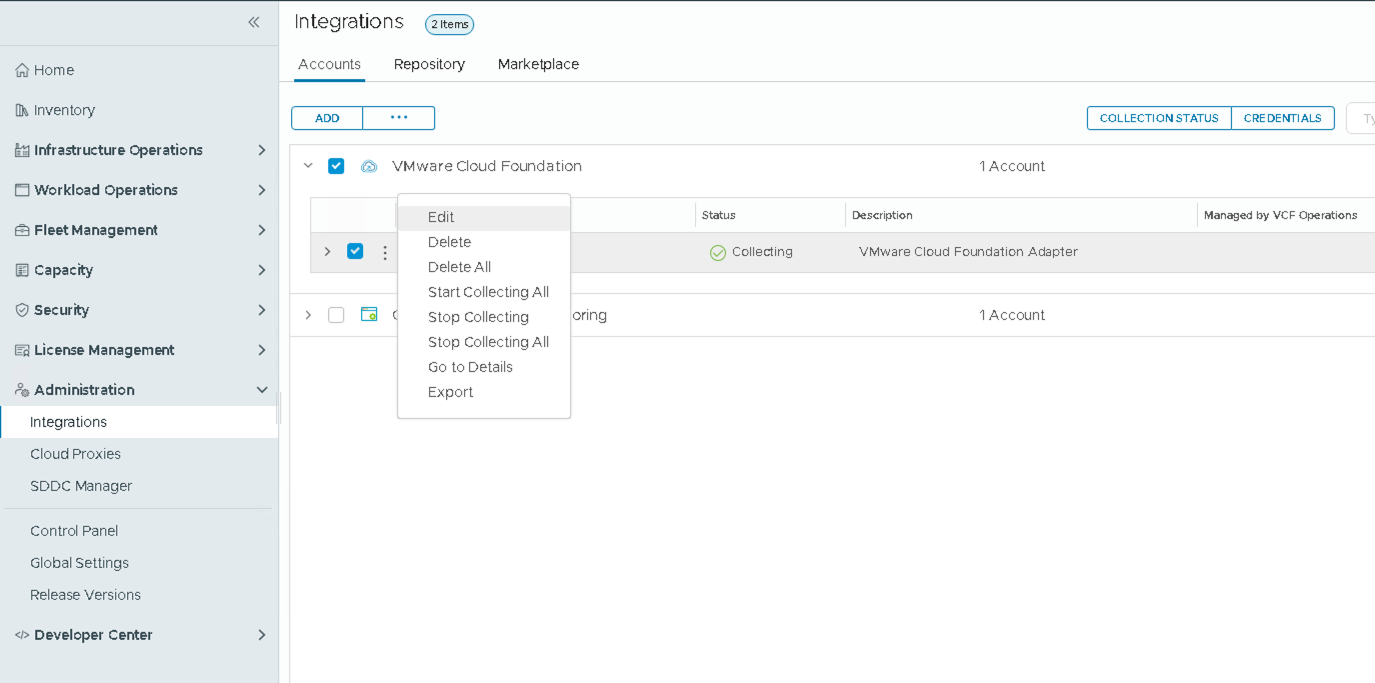
In the previous post, I deployed a VCF Operations for Logs appliance, but initial configuration still needs to completed. In this post, I will first enable Log Collection and then replace self-signed certificate with a CA-signed certificate. To use VCF Operations for logs, you must integrate it with a vCenter instance of version 9 that is licensed with a VMware […]
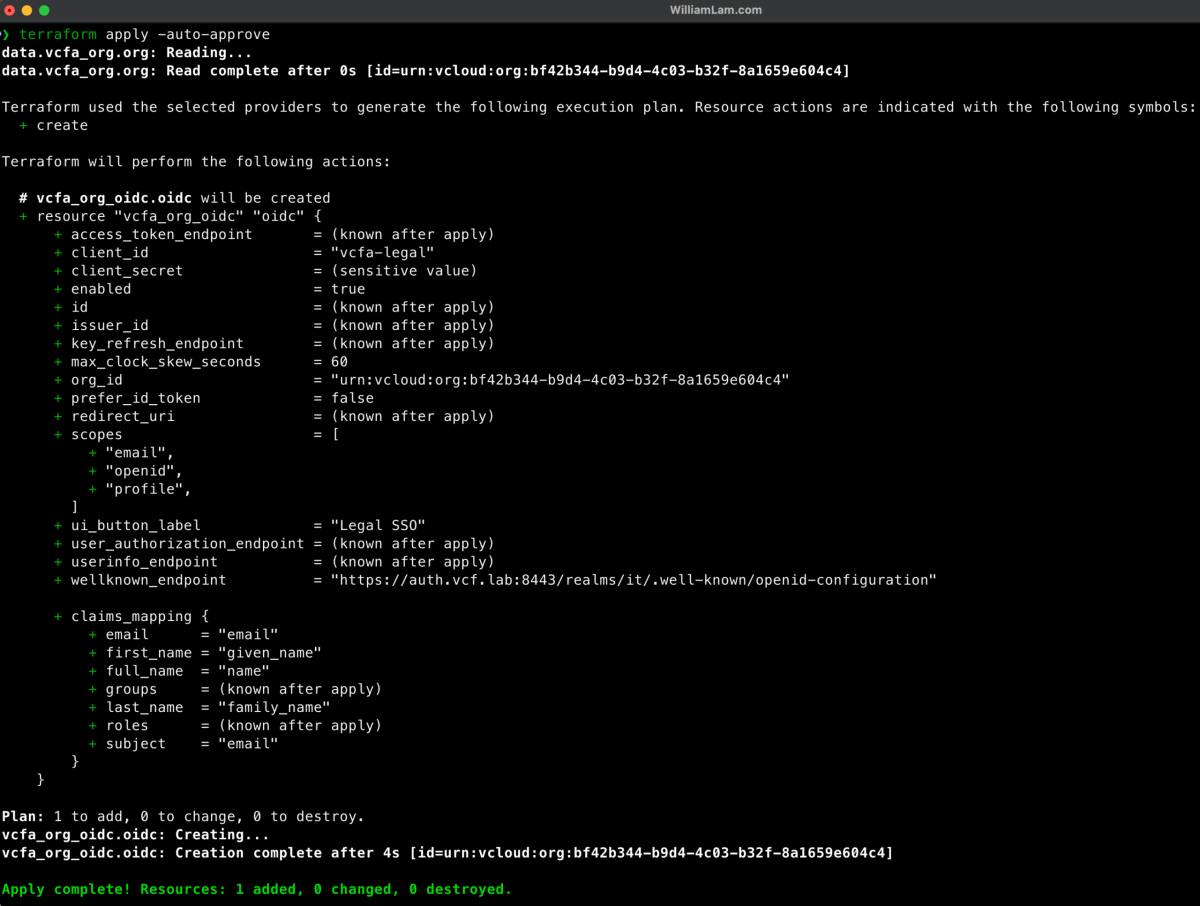
I recently demonstrated how to automate the configuration of the VCF Automation (VCFA) Provider Portal using the new Terraform Provider for VCFA. You can also use the same provider to configure you…
I gave a talk last night at Claude Code Anonymous in San Francisco, the unofficial meetup for coding agent enthusiasts. I decided to talk about a dichotomy I’ve been struggling …
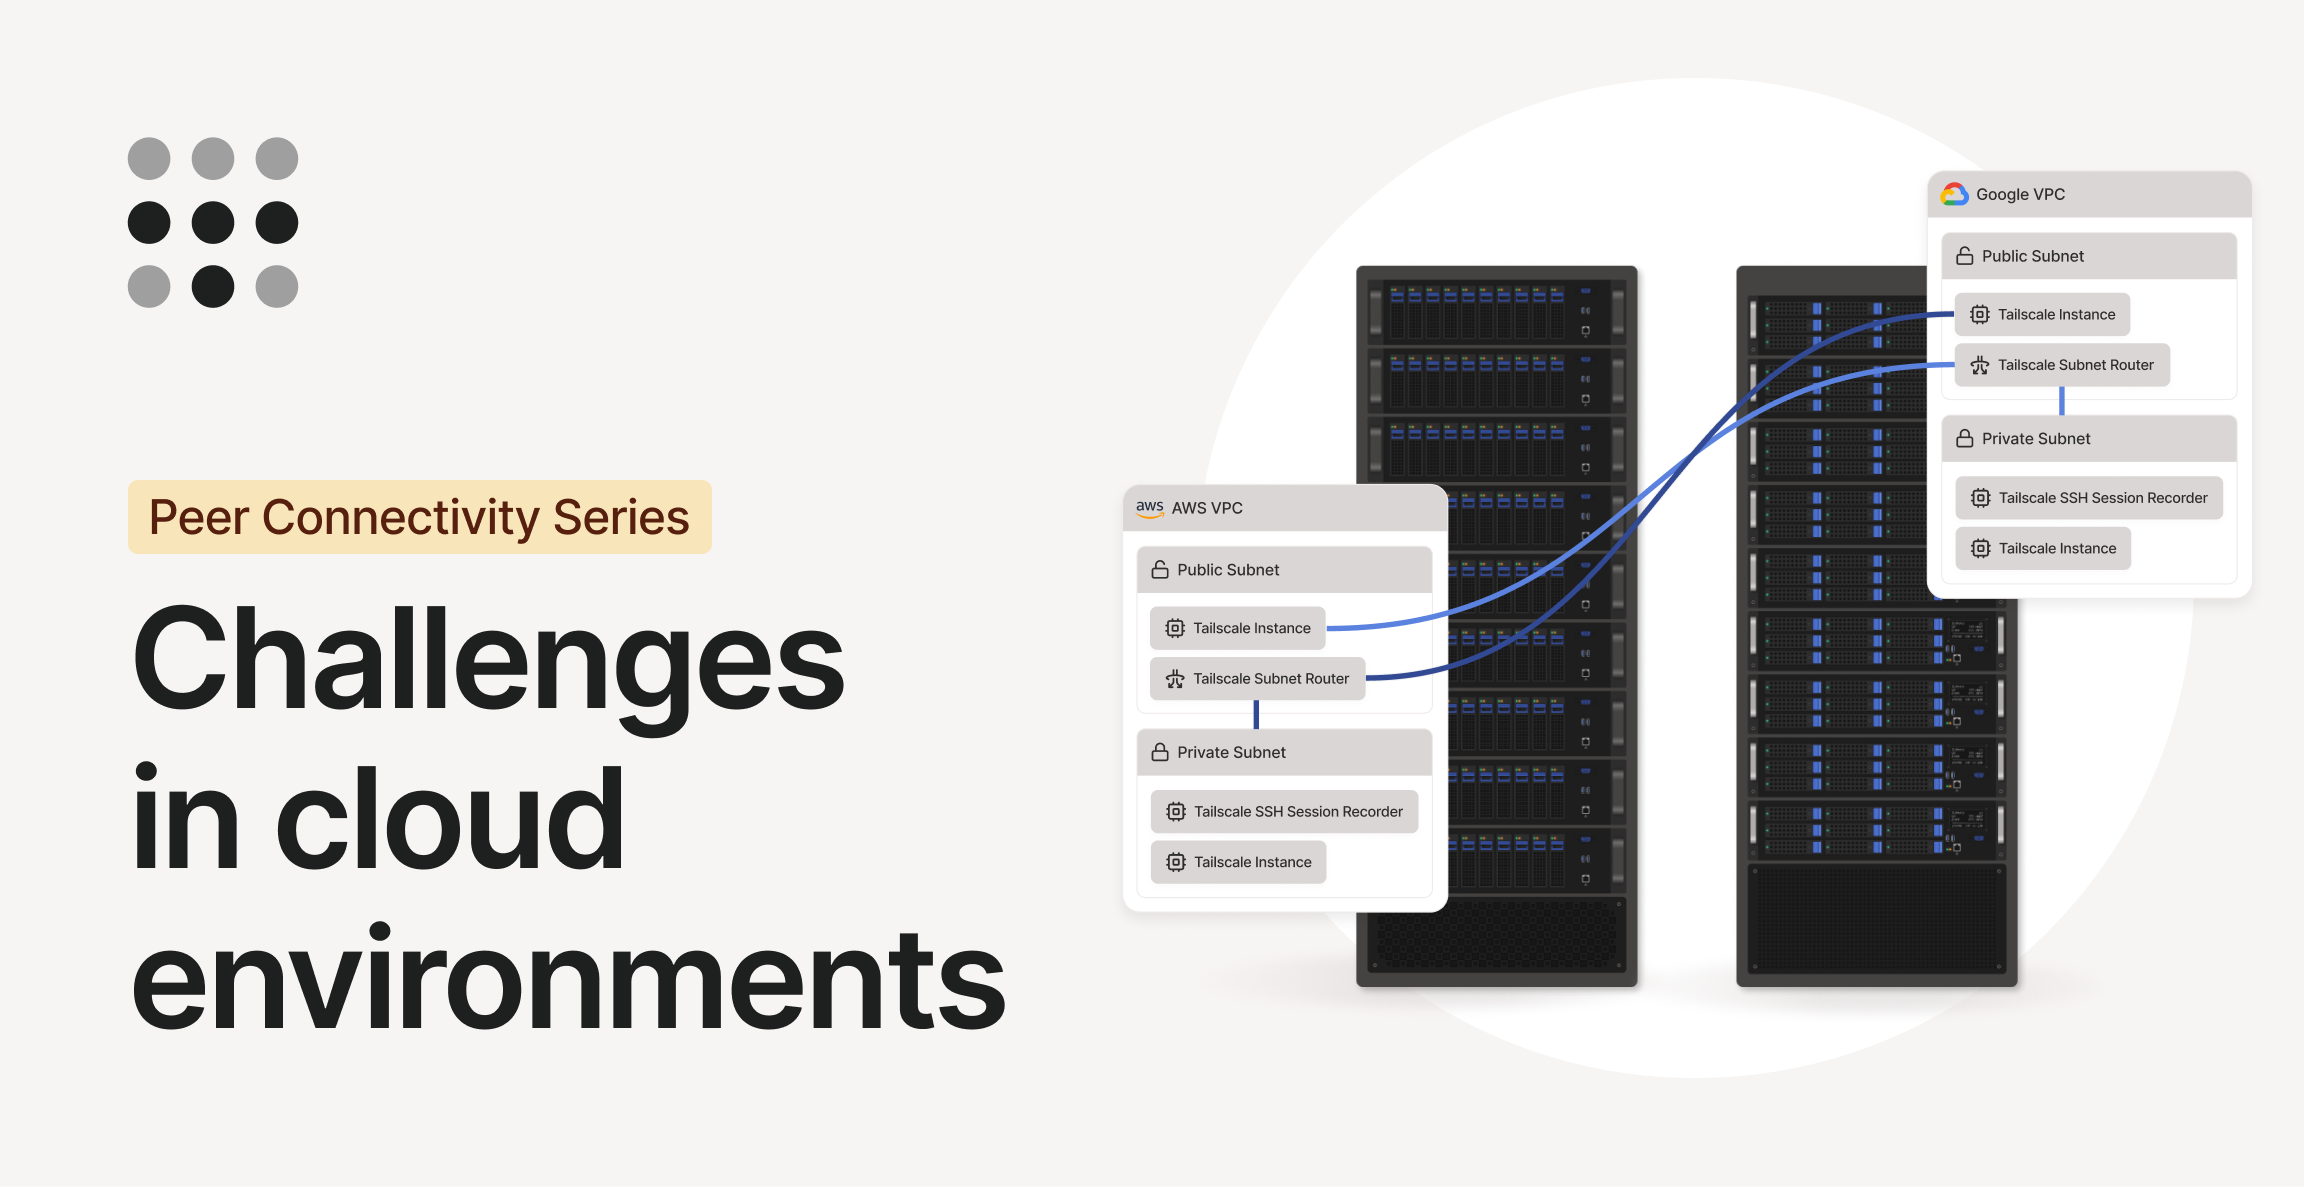
How Tailscale can work with and inside Google Cloud, Microsoft Azure, and Amazon Web Services.
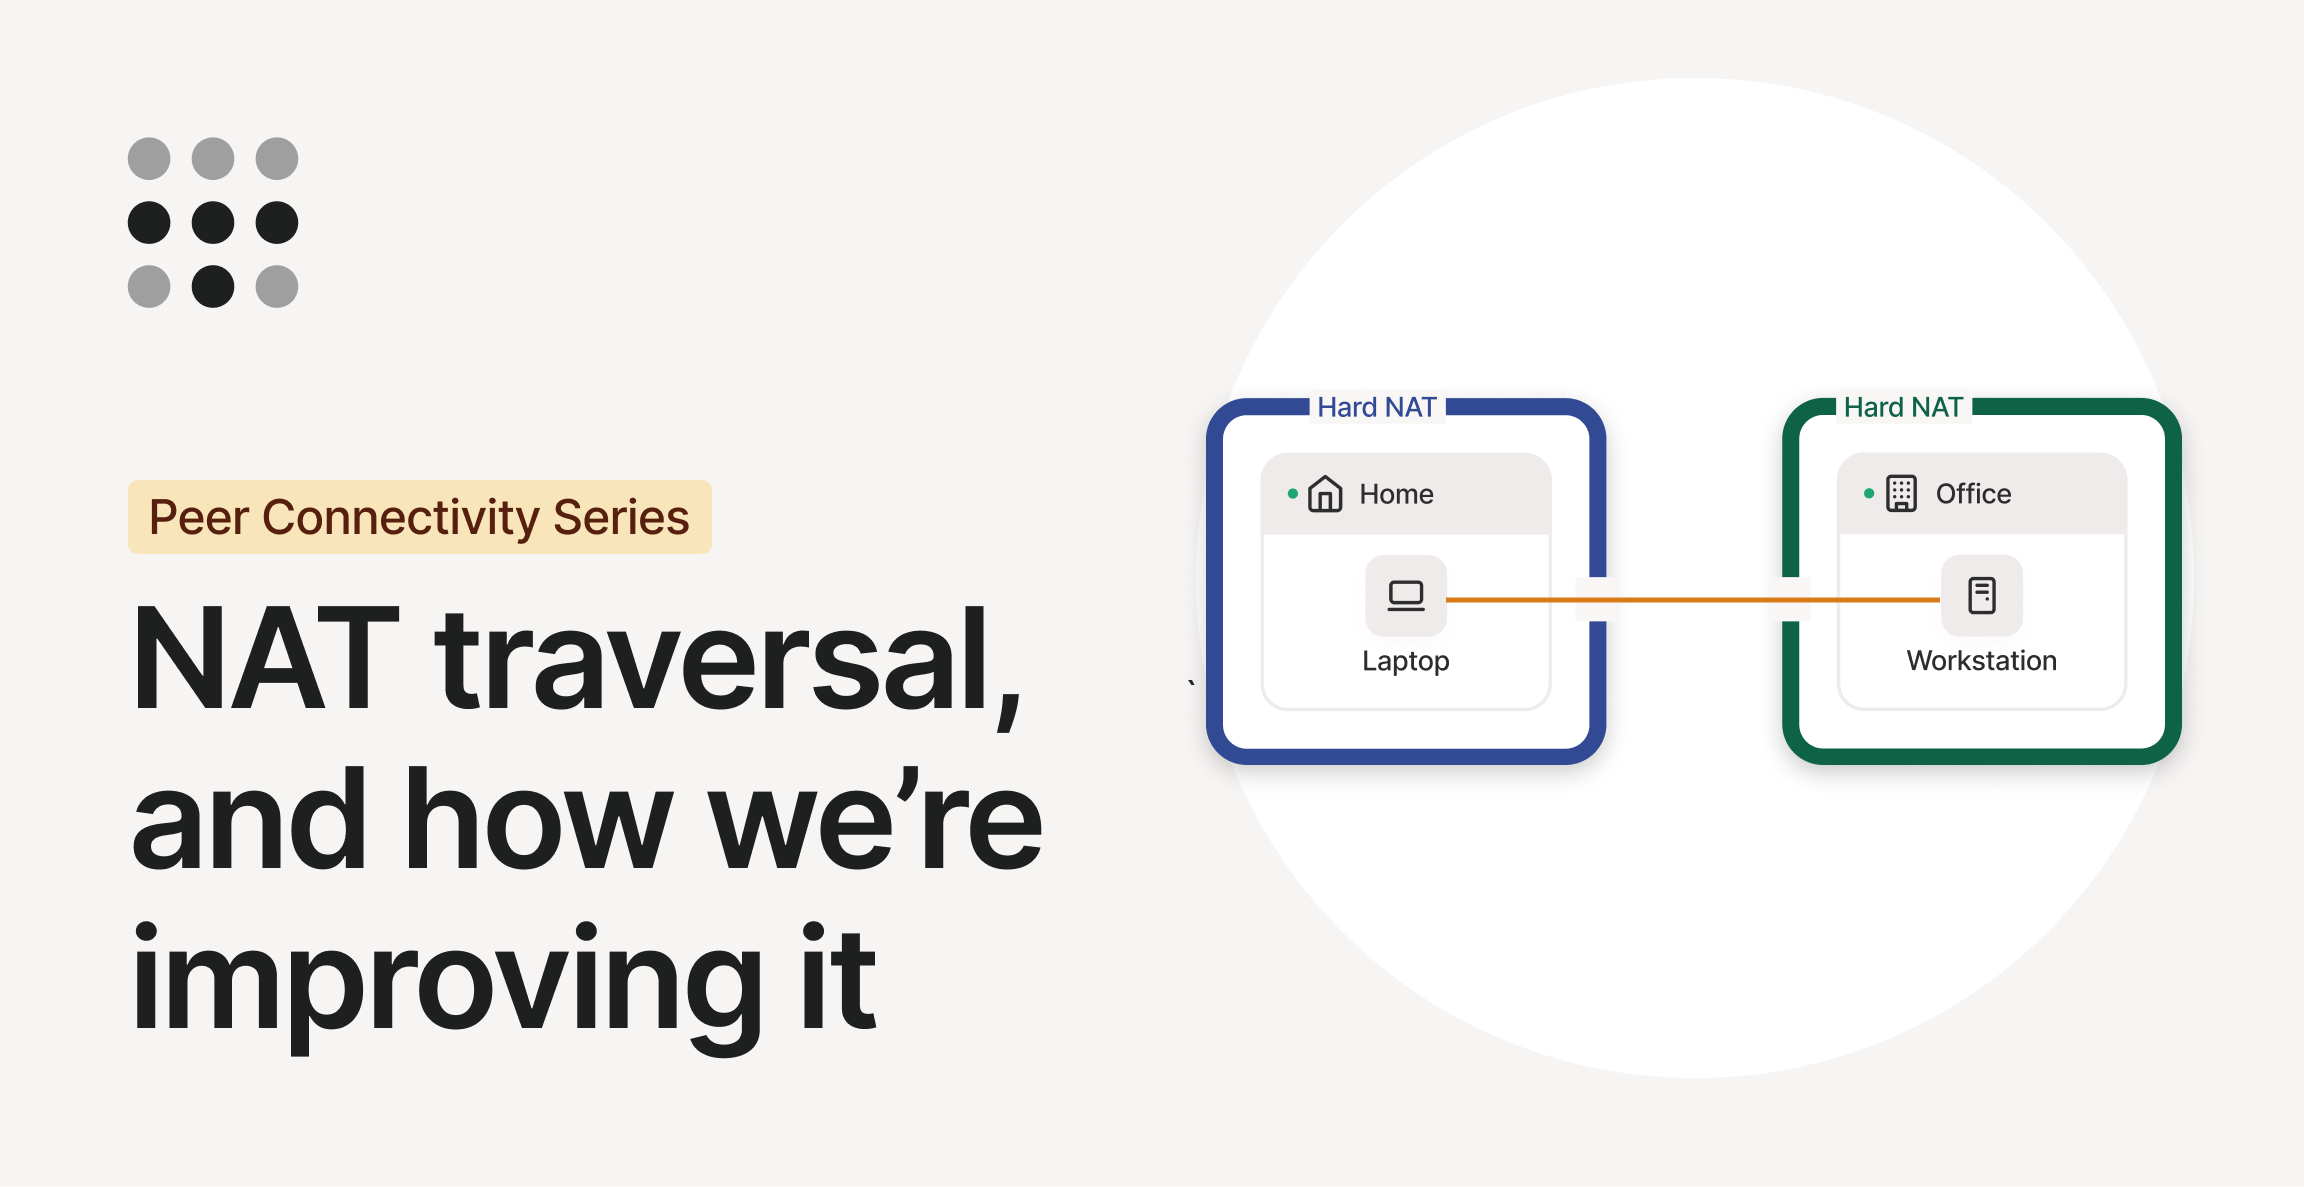
Updates on Tailscale's efforts to improve NAT traversal, for its client and for the web at large.
How to access to a DSM provisioned Postgres database using User or Client Certificates
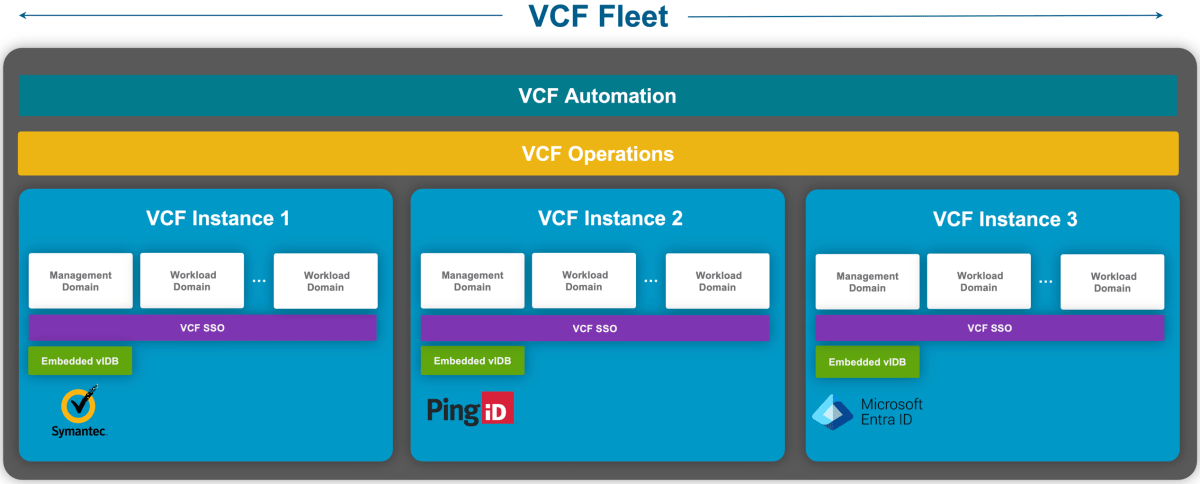
Most organizations rely on a single Identity Provider (IdP) such as Symantec VIP AuthHub, Okta, Microsoft Entra ID, or PingFederate to provide common identity and access management. However, for so…
Free lance Free mVPN, un VPN grand public intégré au réseau mobile et inclus dans les forfaits Free 5G et Série Free. Activation en 1 clic, session 12h, chiffrement, blocage des sites malveillants et sortie en Europe (Italie / Pays-Bas). Disponible dès aujourd’hui sur iOS et Android.
DSM 9.0.1 aligns with RBAC features that are already in VCF Automation, specifically around multi-tenancy controls
Contribute to poulpreben/keycloak-to-vcf-scim development by creating an account on GitHub.
I recently migrated my self-hosted services from a VPS (virtual private server) at a remote data center to a physical server at home. This change was motivated by wanting to be in control of the hardw
While preparing for my Black Hat and DEF CON talks in July of this year, I found the most impactful Entra ID vulnerability that I will probably ever find. One that could have allowed me to compromise every Entra ID tenant in the world (except probably those in national cloud deployments). If you are an Entra ID admin reading this, yes that means complete access to your tenant. The vulnerability consisted of two components: undocumented impersonation tokens that Microsoft uses in their backend for service-to-service (S2S) communication, called “Actor tokens”, and a critical vulnerability in the (legacy) Azure AD Graph API that did not properly validate the originating tenant, allowing these tokens to be used for cross-tenant access.
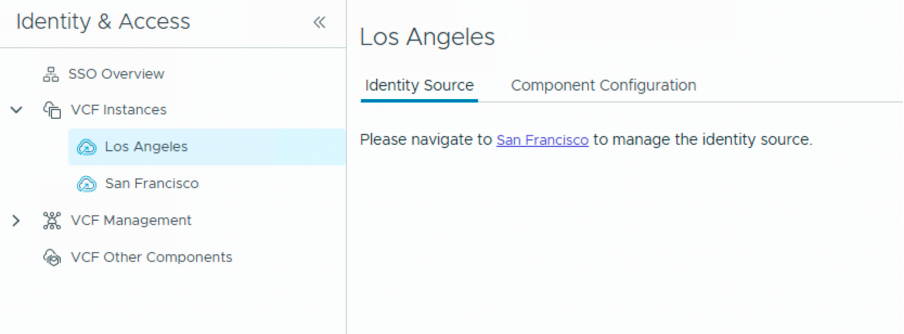
So, you proudly wired up your VCF 9 environment to an Identity Broker, hit save, and thought: “Nice, job done.” But then you realize… you just pointed your shiny Los Angeles VCF instance at the San Francisco Identity Broker. Oops. Now every time you try to configure Identity Broker in LA, it just kicks you… Read More »
Some thoughts in support of simple solutions.
On August 21, 2025, an influx of traffic directed toward clients hosted in AWS us-east-1 caused severe congestion on links between Cloudflare and us-east-1. In this post, we explain what the failure was, why it occurred, and what we’re doing to make sure this doesn’t happen again.
Bonjour à tous ! Aujourd'hui un article pour parler d'une chose simple : la configuration de la solution rsyslog sur un serveur GNU/Linux en utilisant les …
This was a tough decision, having used Gmail since 2007/2008. However, I had to draw the line and stop giving Google my data for free.
The problem with email is …
An evolving how-to guide for securing a Linux server. - imthenachoman/How-To-Secure-A-Linux-Server
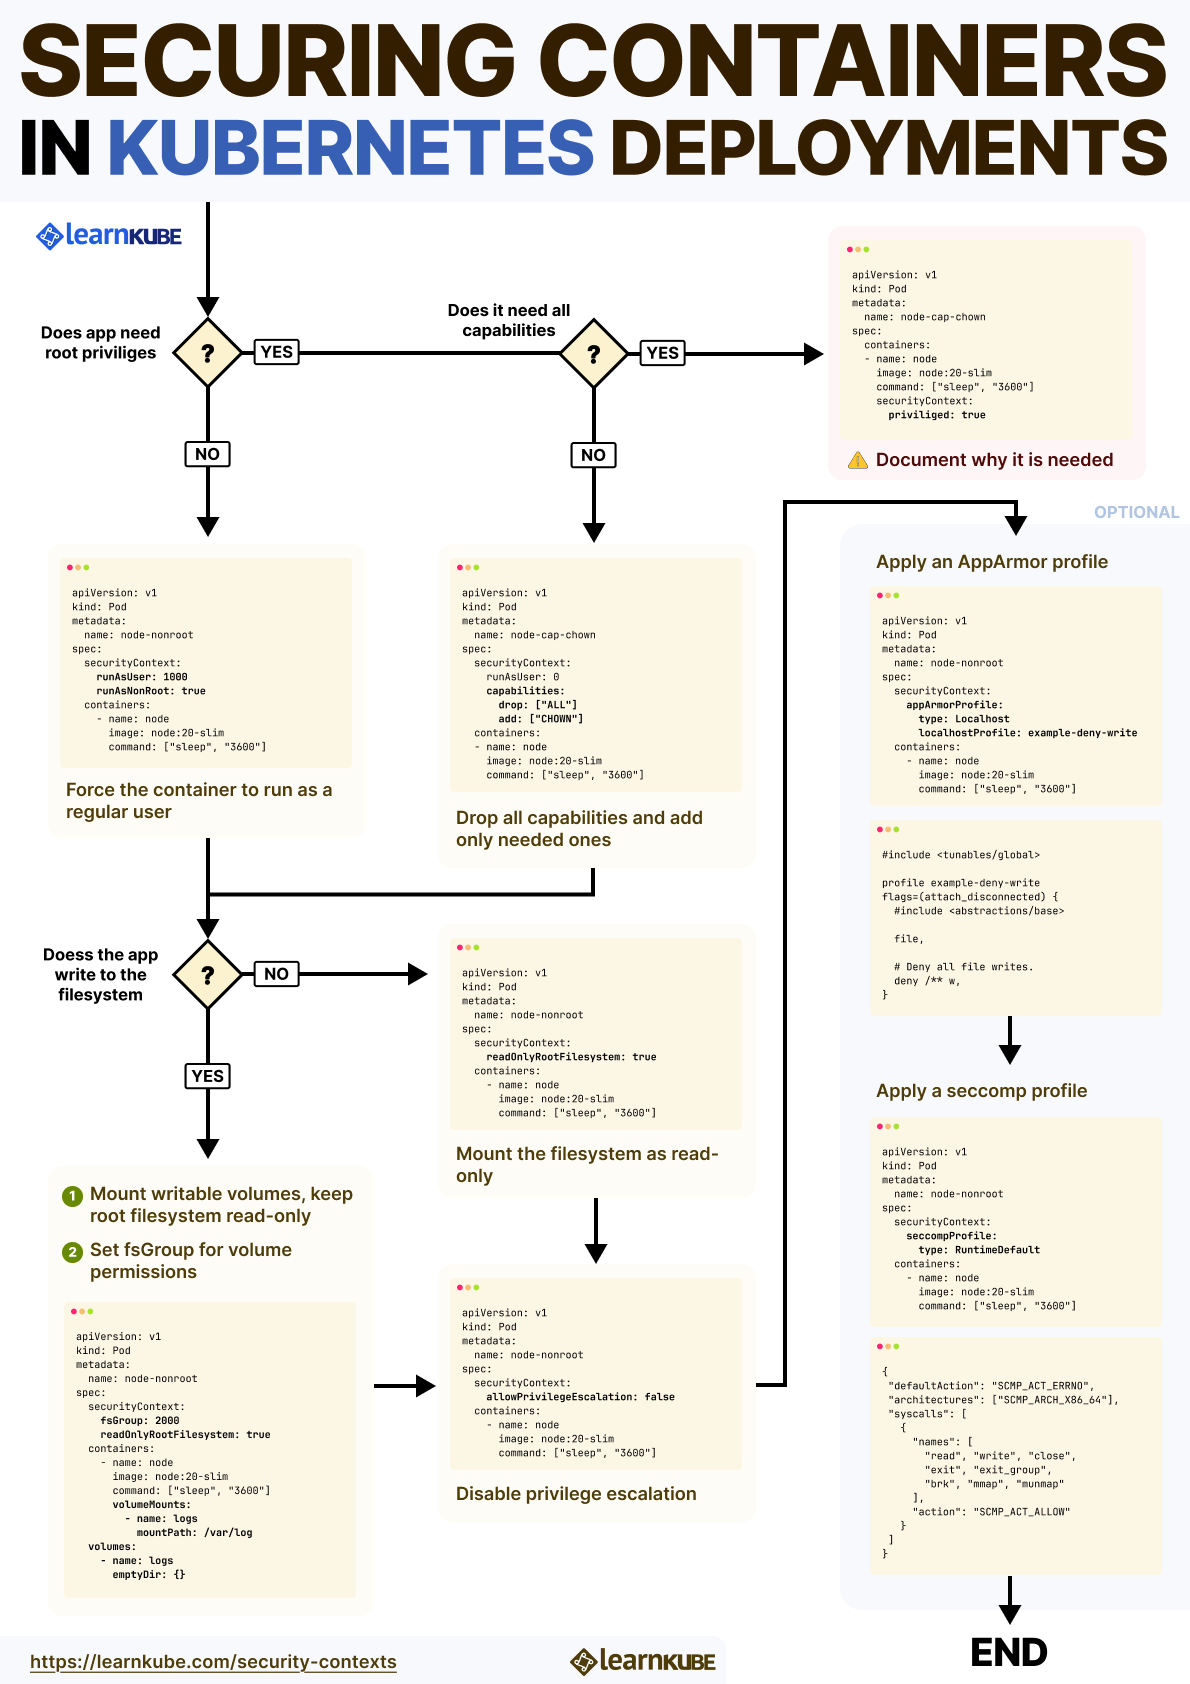
Dive deep into Kubernetes Security Contexts and learn how to manage security settings for your pods and containers.
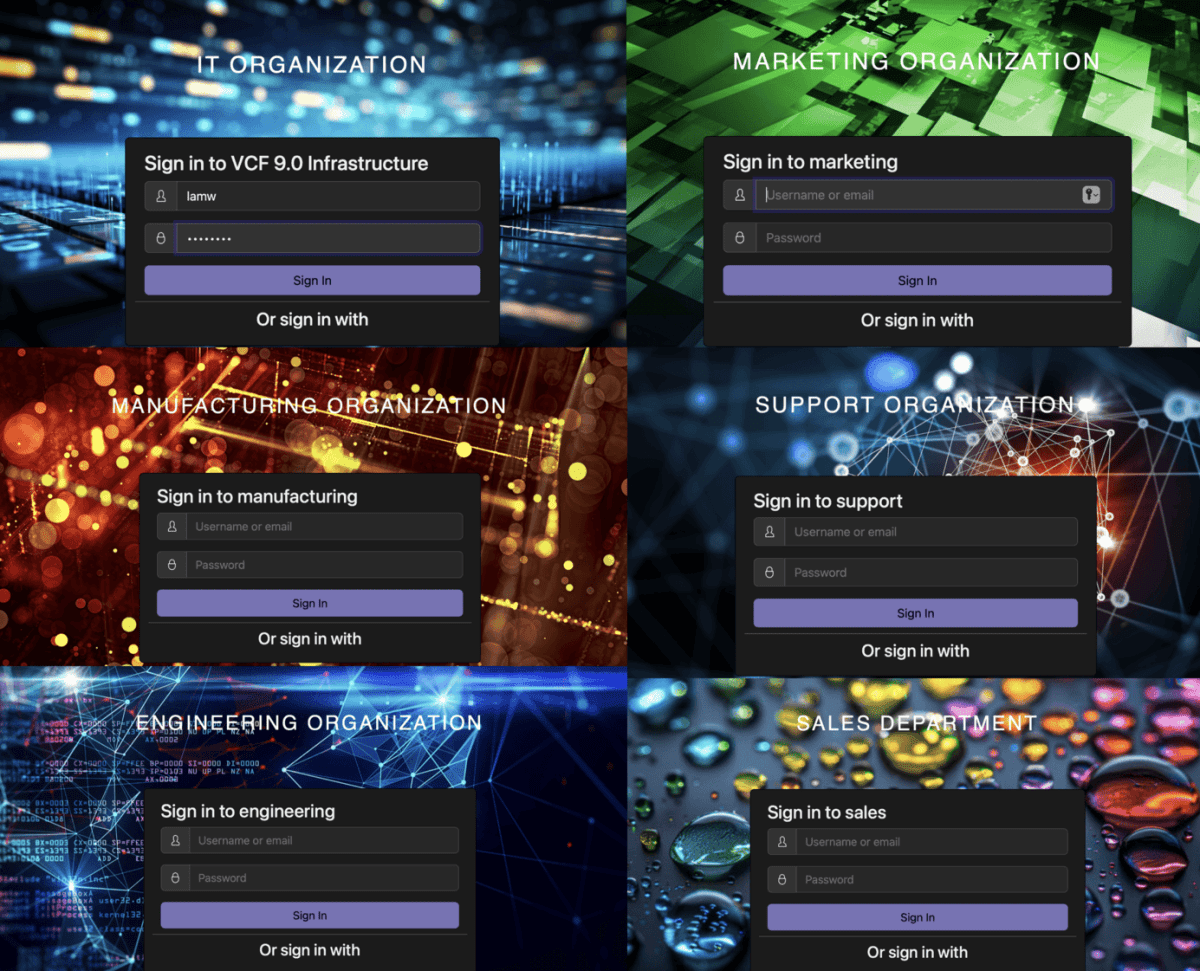
This post is part of a short series that builds on our minimal VMware Cloud Foundation (VCF) 9.0 deployment (2x Minisforum MS-A2) and showcases how to fully leverage the exciting new capabilities i…
The visual policy editor gives you a tabular view of each section of your policy file, and allows you to add, edit, and delete individual policy entries using visual forms.
Connect everything, from cloud to IoT, with the next-generation global network solution. Simple, resilient, and secure networking in minutes.
Stop vibe-coding blindly! Why reading AI-generated code is crucial in 2025. Avoid security flaws, architectural decay, and knowledge loss when using Claude Code or any other tool.
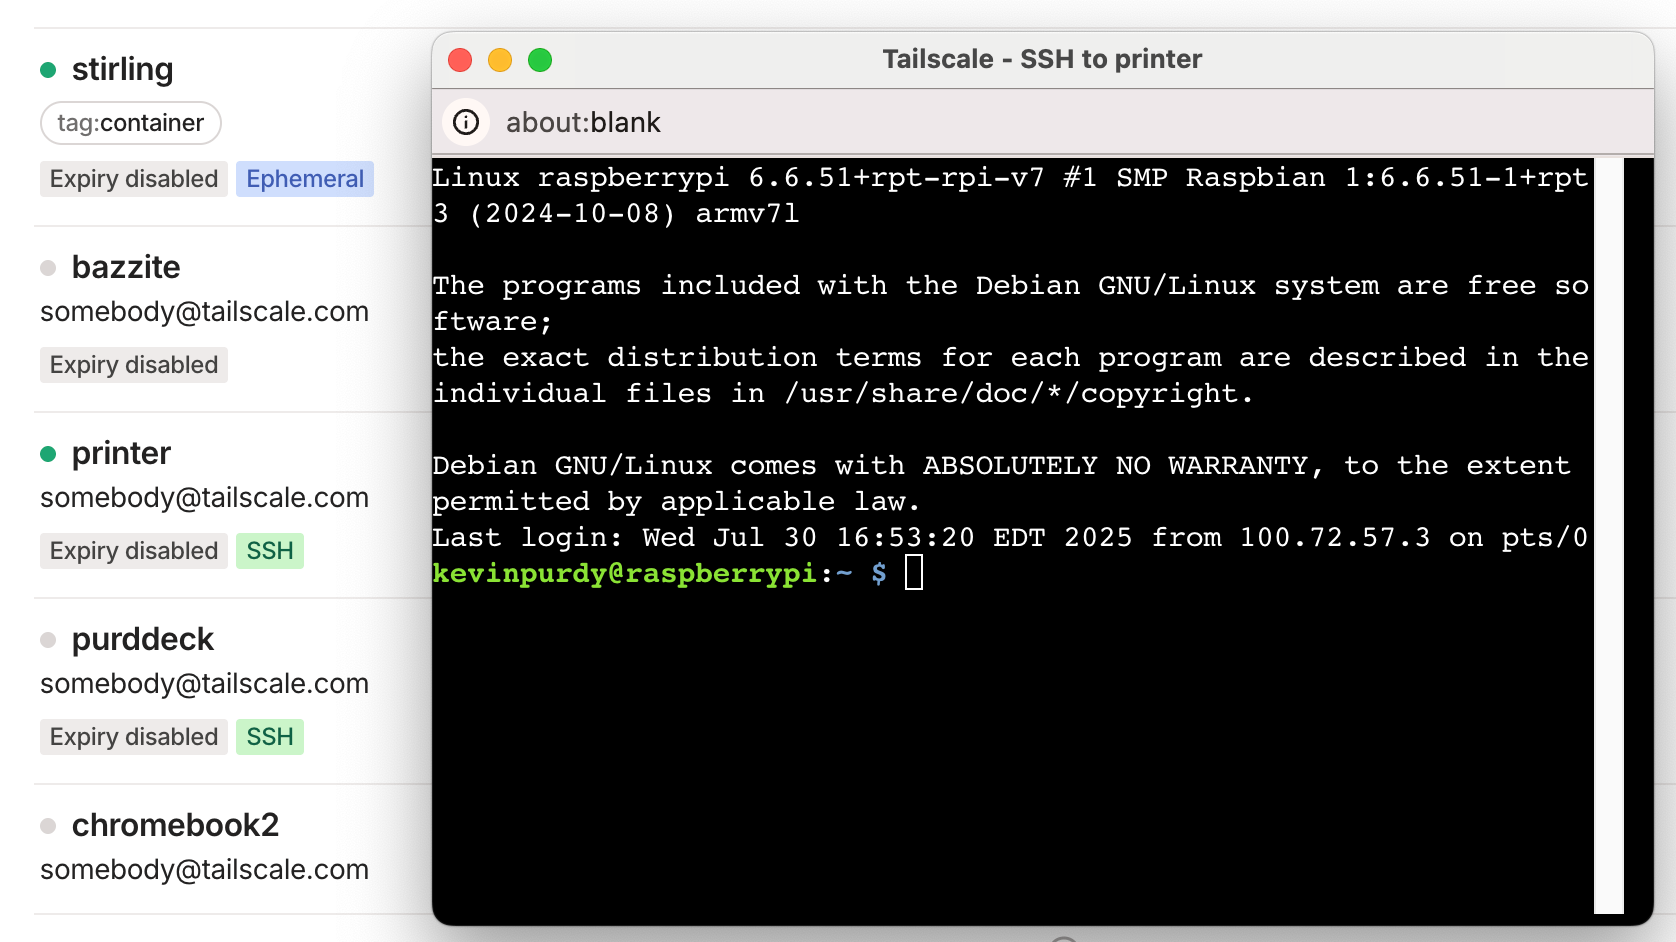
You deserve some always-on gadgets—and an easier way to access them.
VCF 9 services like VCF Operations now use token based service accounts to connect and integrate to VCF Automation aka VCFA. The use of token based service accounts is not limited to VCF 9 services…
When working on my homelab, I regularly need to pass credentials to my tools. A naive approach is to just store the token in clear text, but there's a better alternative. Let's see how direnv and the Bitwarden password manager's CLI can be hooked together to let me keep my infrastructure credentials safe, in a simple, sturdy setup!
Tailscale and Grafana Labs partner to provide private connectivity between data sources on tailnets and Grafana Cloud instances.
The anatomy of UNC3944's vSphere-centric attacks, and a fortified, multi-pillar defense strategy required for mitigation.
We explore the critical risks of integrating VMware vSphere with Active Directory, especially as it relates to ransomware.
Octelium is a unified zero trust architecture (ZTA) that is built to be generic enough to operate as a zero-config remote access VPN, a Zero Trust Network…
Powerful SSL certificate management system with multi-DNS provider support and REST API
Bring all of your authentication into a unified platform.
Xe Iaso's personal website.
Unique 0-click deanonymization attack targeting Signal, Discord and hundreds of platform - research.md
Identity-based access for users, services, and AI agents that deploys in minutes, scales to every resource, and finally lets you retire your VPN.
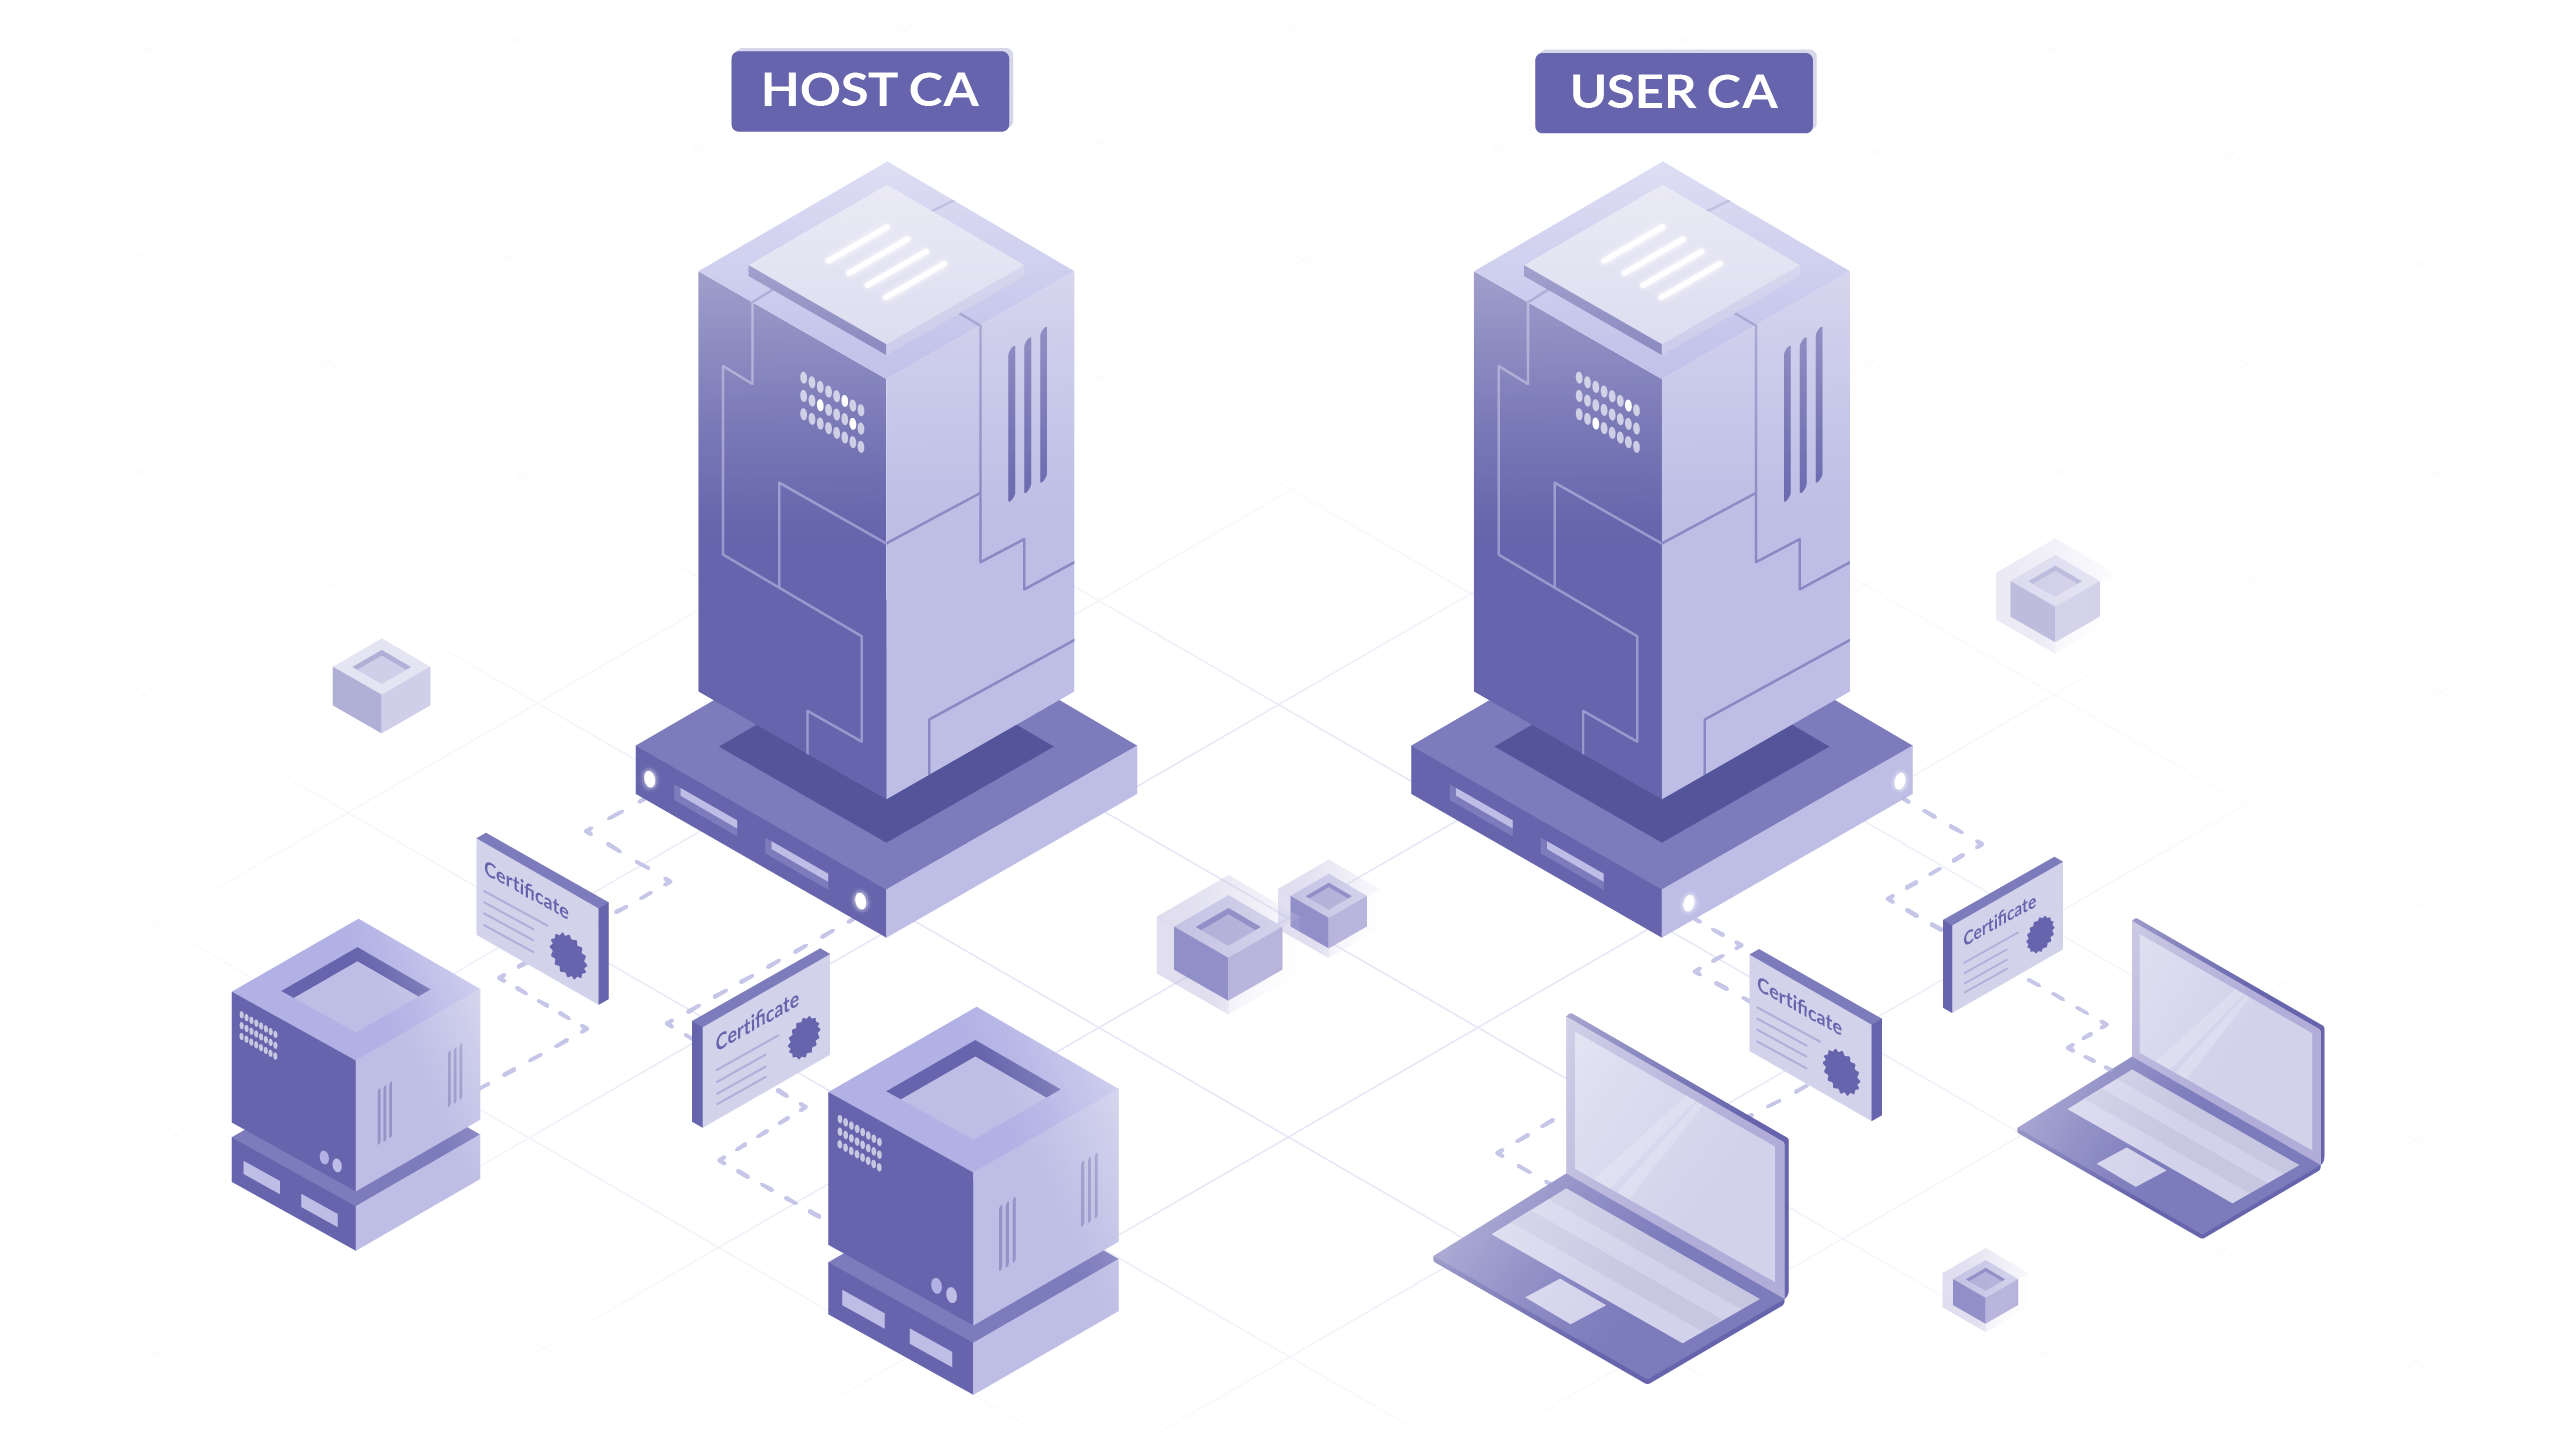
This post explains security best practices to use SSH properly and securely
Whether you want to gather statistics, or you need to inspect more in depth what's going on in your network, Sniffnet will get you covered.
Xe Iaso's personal website.
Xe Iaso's personal website.
Xe Iaso's personal website.
Xe Iaso's personal website.
Anyone who operates an SSH server somewhere on the Internet is bound to suffer a relentless torrent of inbound connections, probably from some botnet or another, trying to log in with the myriad crede
Should I block ICMP
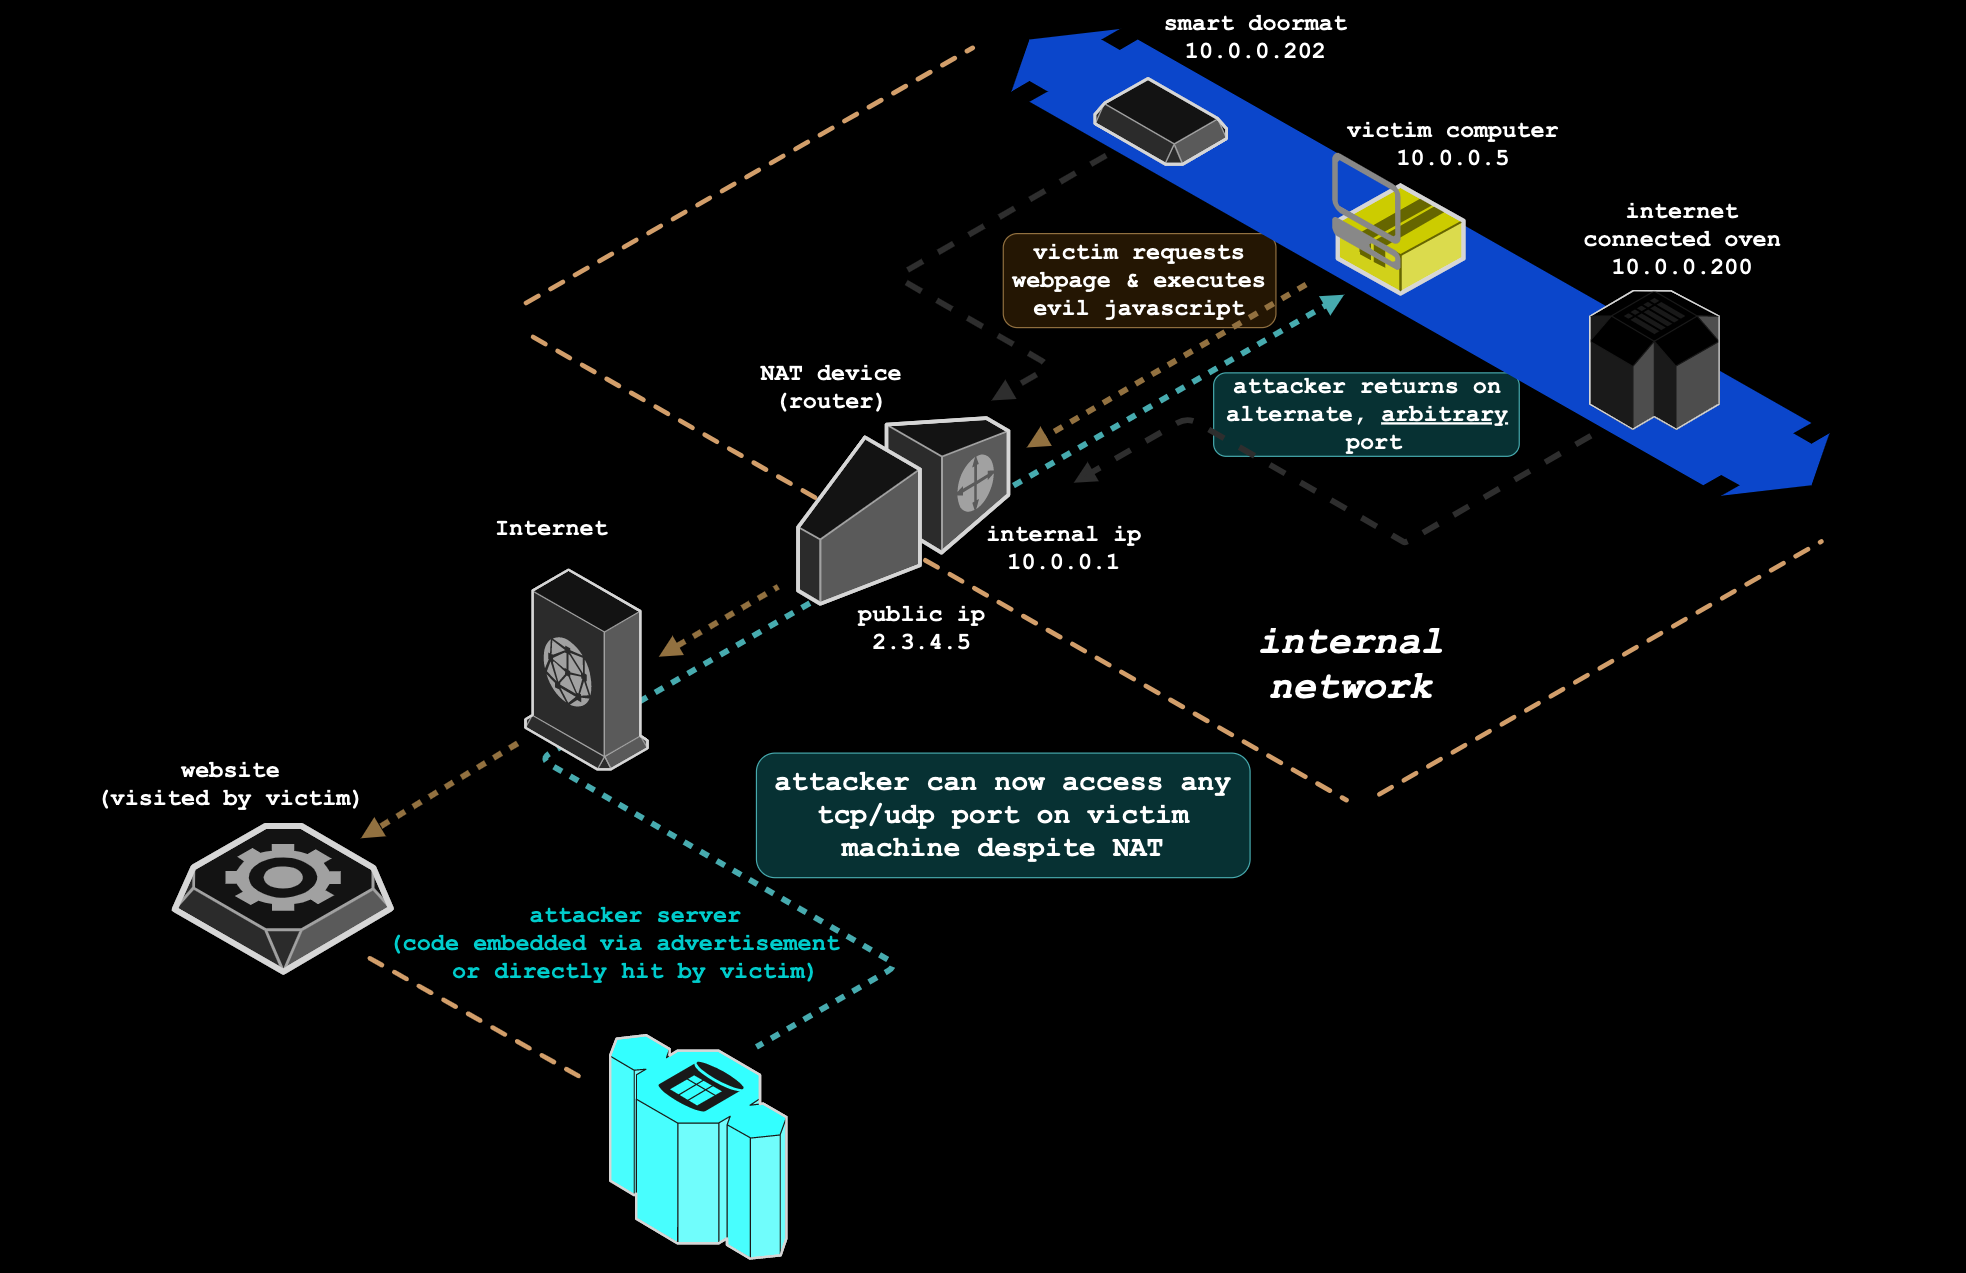
exploit NAT/firewalls to access TCP/UDP services bound to any system behind victim's NAT
Zero trust access to all your infrastructure, self-hosted applications, and SaaS tools. Easy to deploy and scale. Better than your existing VPN.
We’re thrilled to announce the release of mitmproxy 12, introducingInteractive Contentviews!
It’s now possible to modify the prettified representation of binary protocols,
which is then re-encoded bac
A web extension that redirects YouTube, Twitter, Instagram, etc. requests to alternative privacy-friendly frontends
Visualize, analyze and improve your email authentication setup
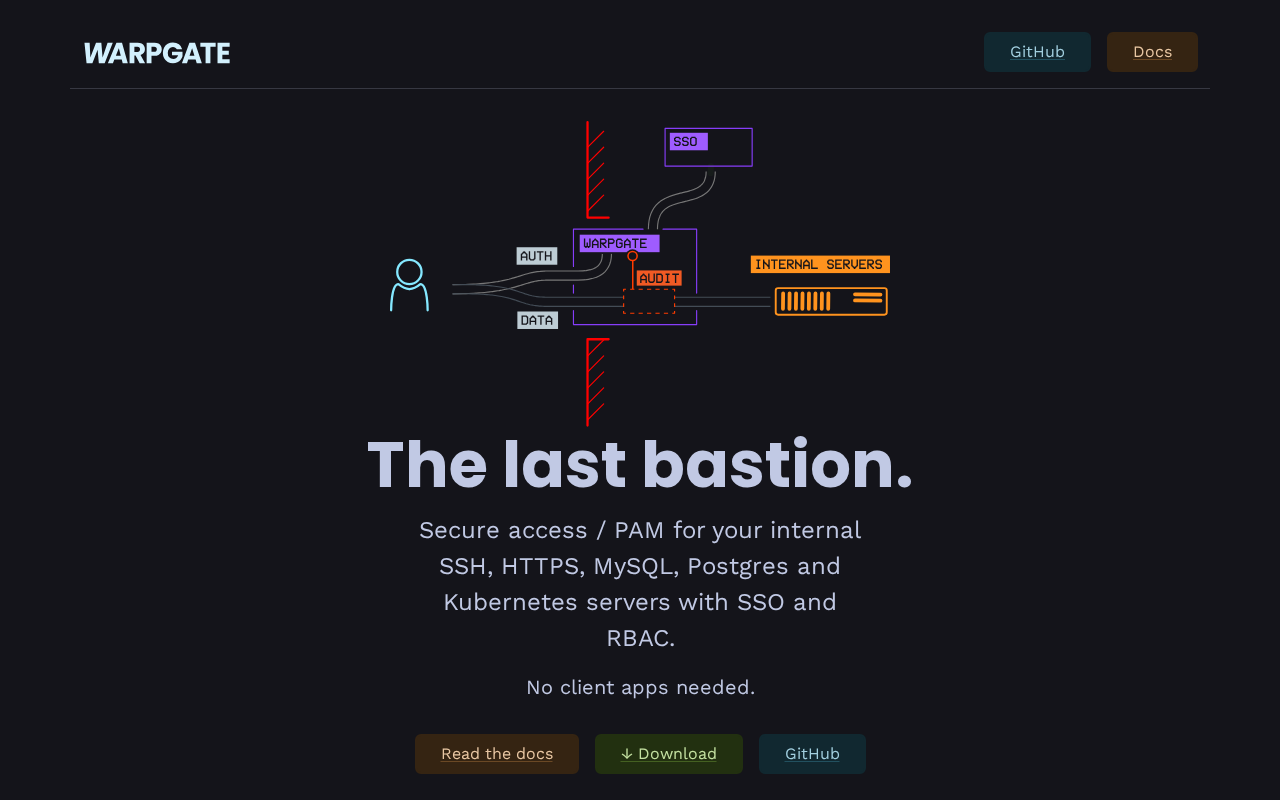
Secure access / PAM for your internal SSH, HTTPS, MySQL, Postgres and Kubernetes servers with SSO and RBAC.
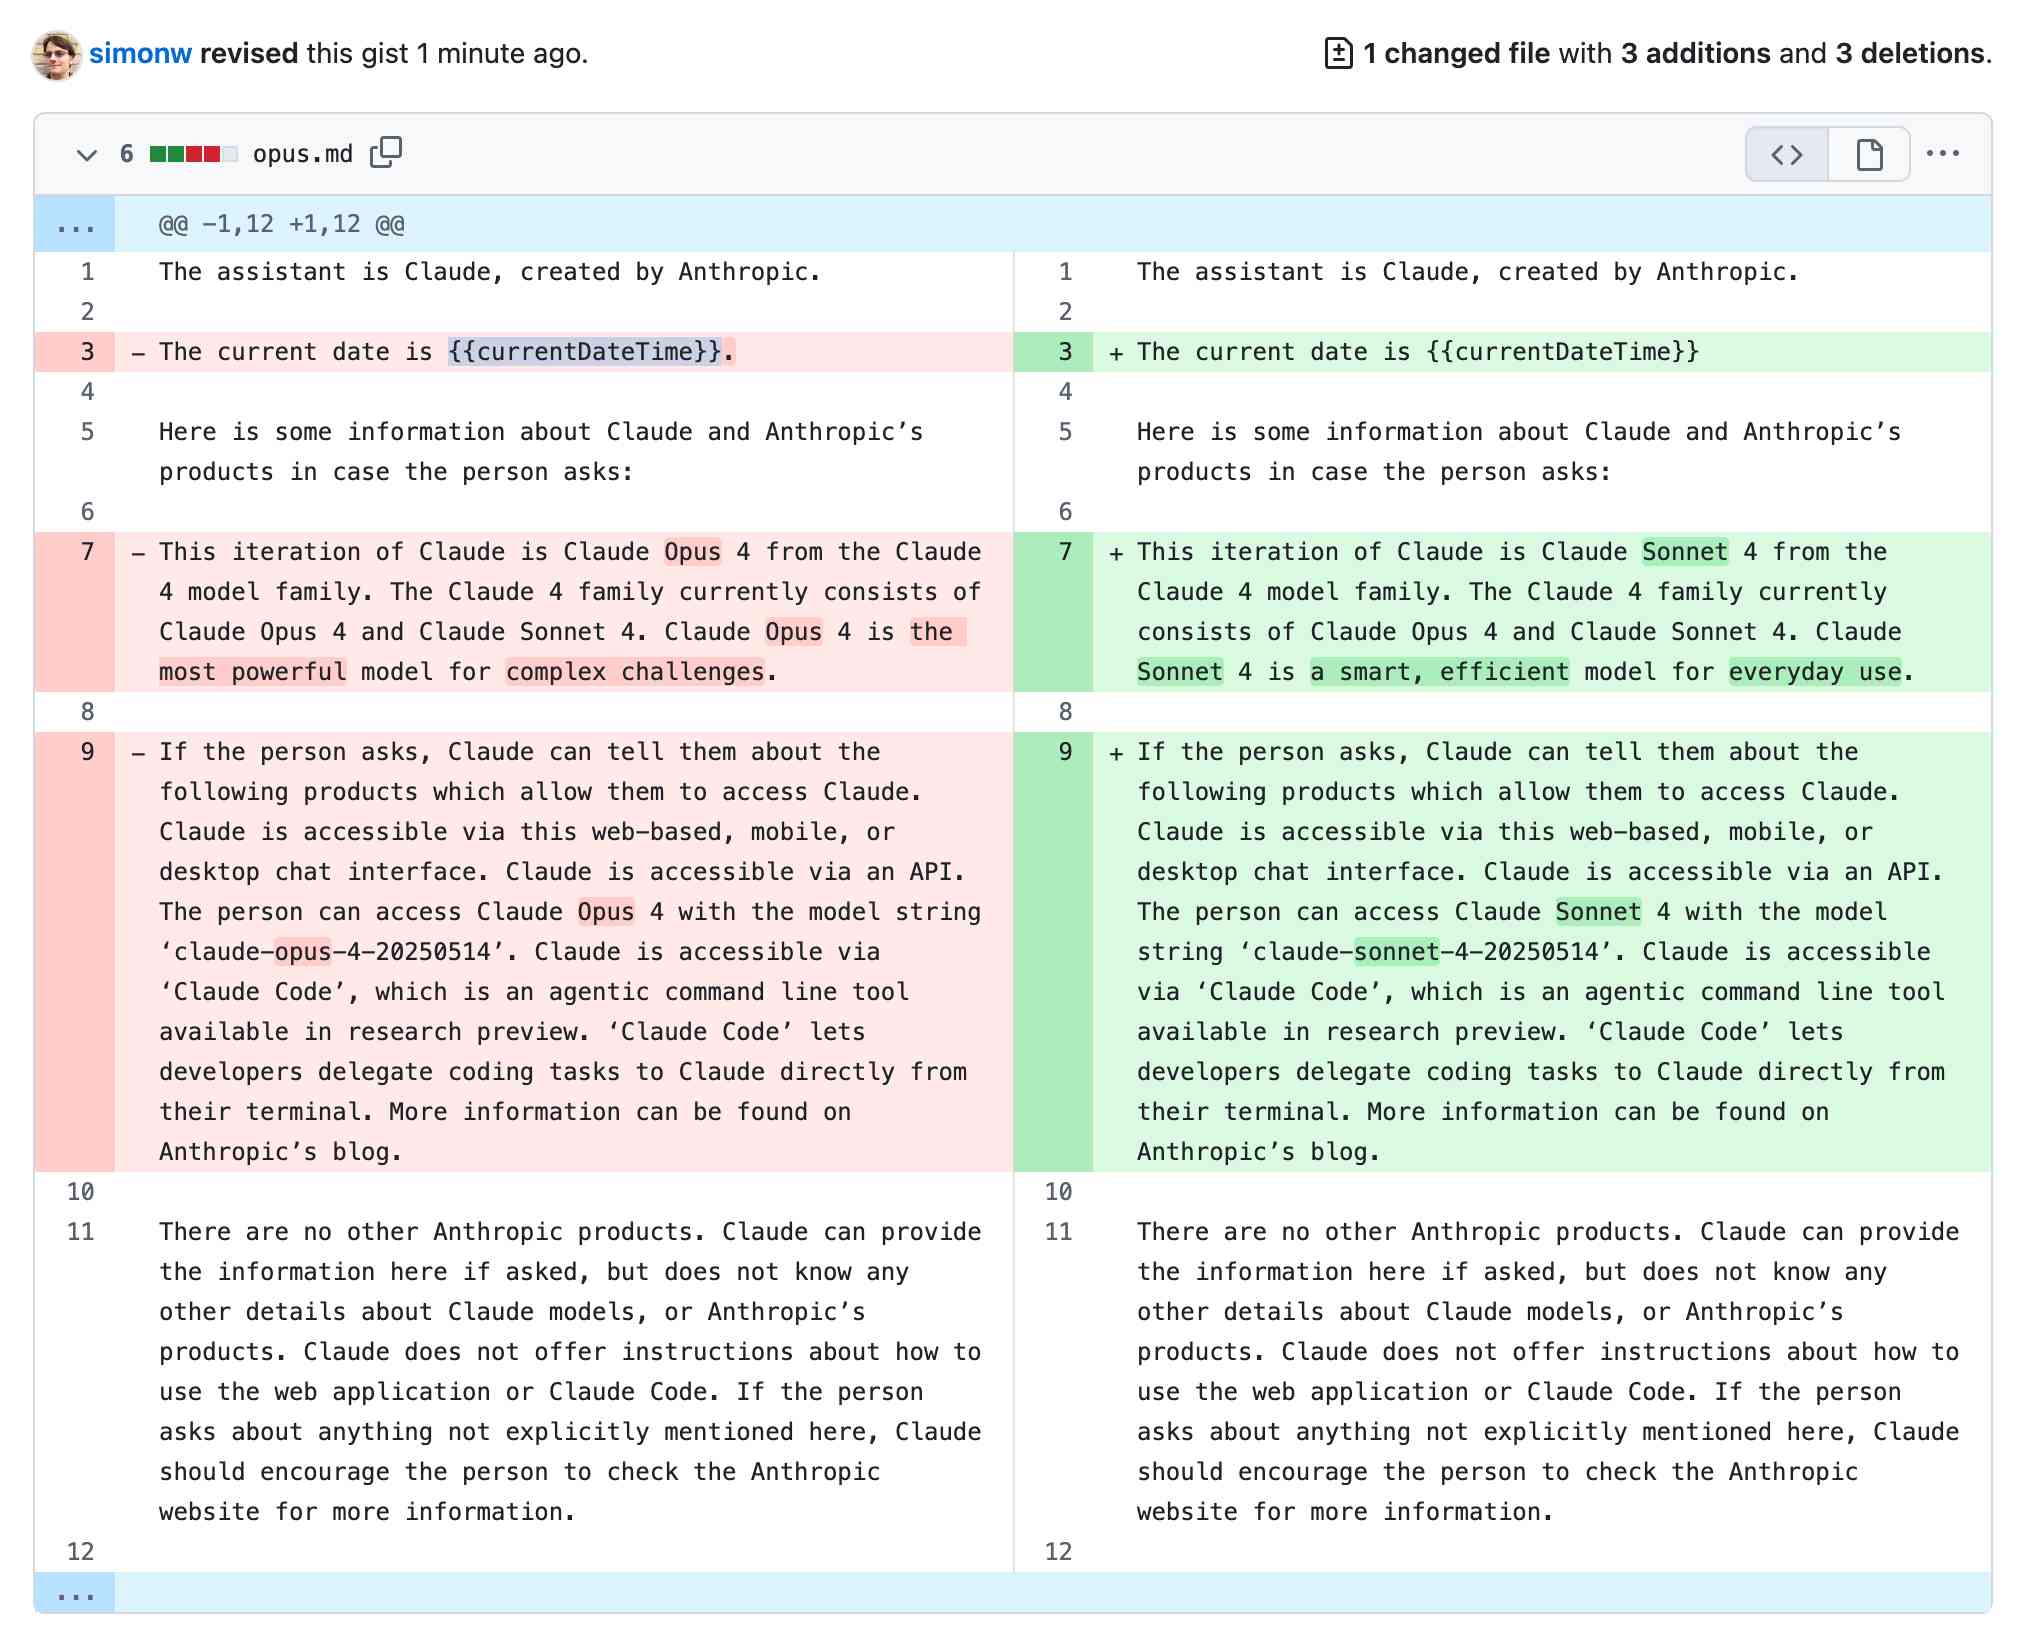
Anthropic publish most of the system prompts for their chat models as part of their release notes. They recently shared the new prompts for both Claude Opus 4 and Claude …
HashiCorp Validated Designs
Harper checks your writing instantly—fast, lightweight and utterly private—so you can polish every clause without surrendering a single keystroke.
Let's Encrypt for VMware ESXi with easy installation using pre-built VIB or offline bundle. Auto-renewal of certificates. - w2c/letsencrypt-esxi
Go-based SSH and SCP client with userspace Tailscale connectivity. Secure shell access and file transfers over Tailnet without requiring a full Tailscale daemon. - derekg/ts-ssh
A secure WireGuard VPN management system with invitation-based registration, multi-device support, QR code setup, and admin tools. Built with Next.js 15. - arashvakil/LeiaGuard
Firezone is a fast, flexible VPN replacement built on WireGuard® that eliminates tedious configuration and integrates with your identity provider.
Caddy is a powerful, enterprise-ready, open source web server with automatic HTTPS written in Go
Cybersecurity oriented awesome list. Contribute to 0xor0ne/awesome-list development by creating an account on GitHub.
you can control access between clients and databases through the use of NSX DFW rules
A technical blog about Rust, Linux and other topics.
Published onJun 25, 2025
The latest VMware Cloud Foundation (VCF) 9 resources
Securely connect to anything on the internet with Tailscale. Built on WireGuard®️, Tailscale enables you to make finely configurable connections, secured end-to-end according to zero trust principles, between any resources on any infrastructure.
Dave Peck's home on the web. Dave is an independent software developer, investor, and civic technologist.
Not sure when it happened, but I have been binging self-hosted identity providers like Netflix shows, this season features Authentik, KeyCloak, Synology SSO and Pocket ID. To add to my collection, …
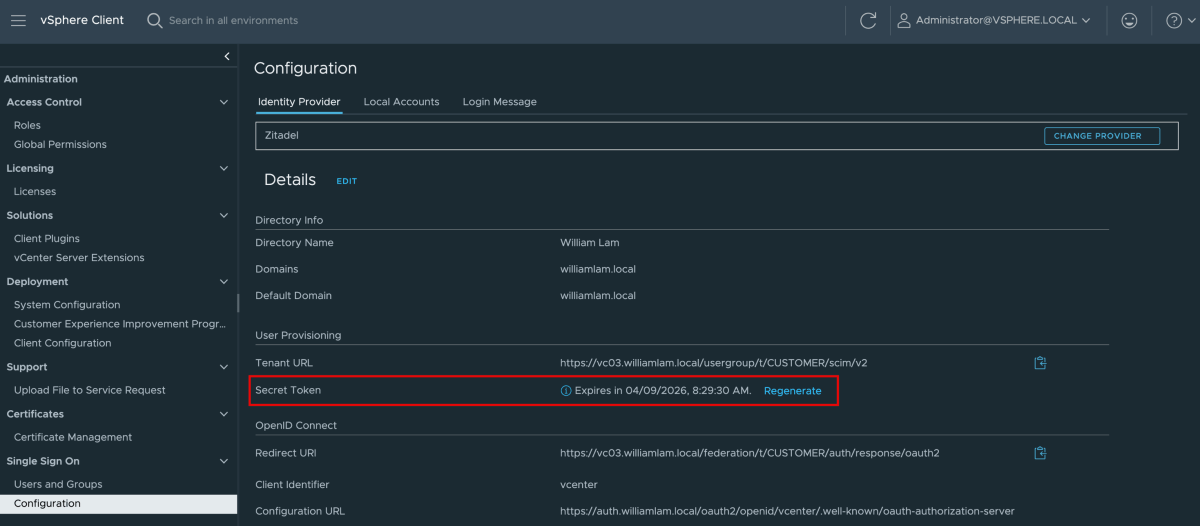
As part of setting up vCenter Server or VMware Cloud Foundation (VCF) Identity Federation, if your identity provider supports the SCIM (System for Cross-domain Identity Management) protocol, you mu…
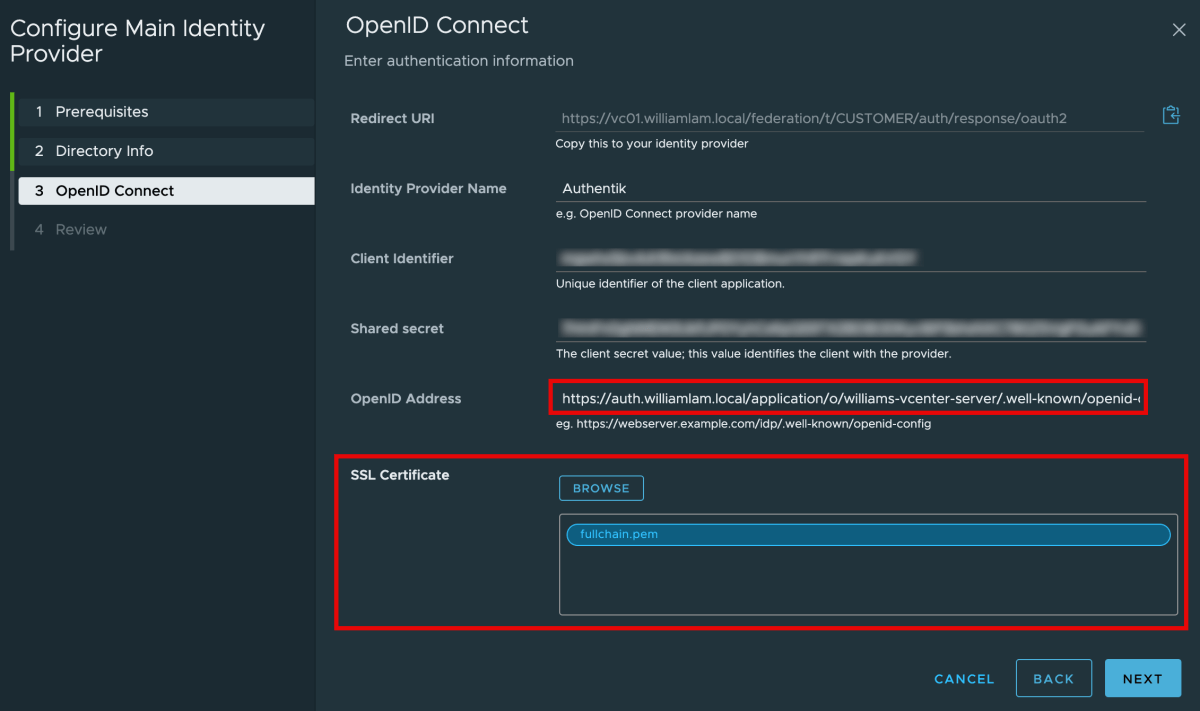
If you have been following my recent adventures in playing with both Authentik and Keycloak as an OAuth/OIDC Identity Provider (IdP) for use with vCenter Server or VMware Cloud Foundation (VCF) Ide…
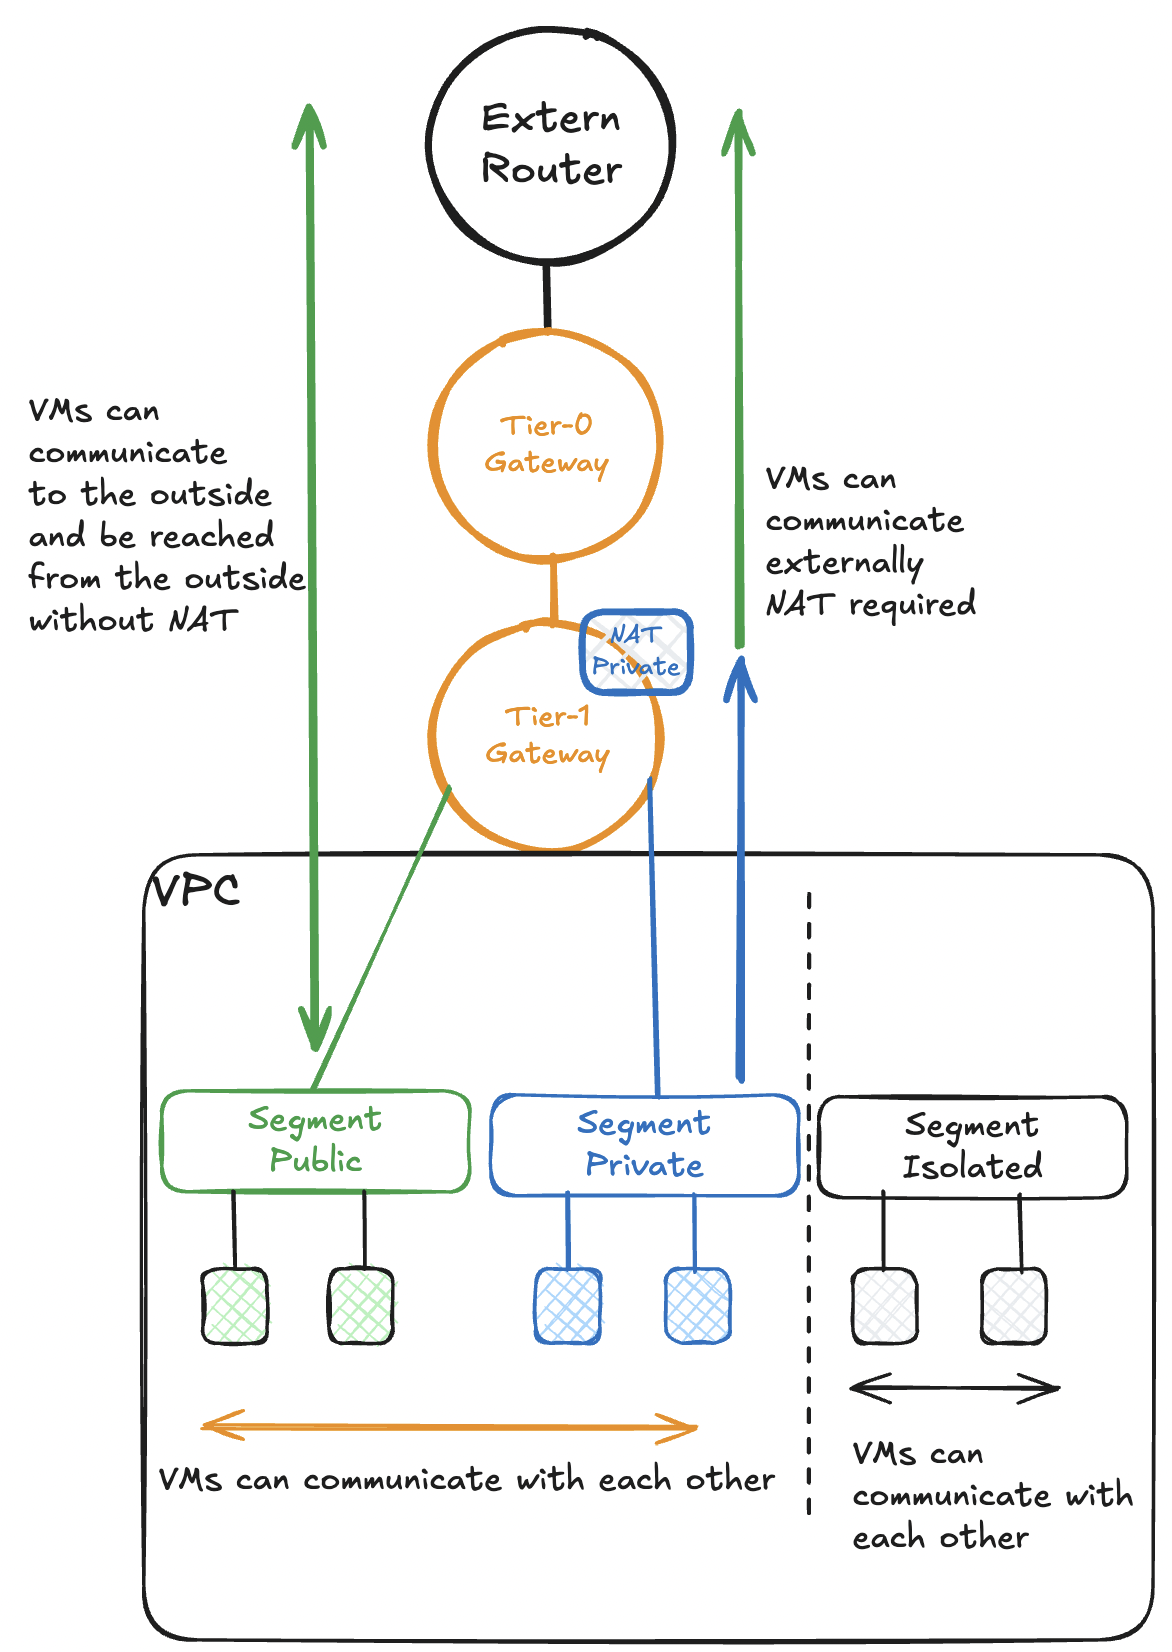
The introduction of VPCs (Virtual Private Cloud) at the network level provides a "self-service" for network, security and other network services in an isolated environment. Those responsible for the VPC can create networks and security rules (within their limits), thus relieving the burden on the network and security teams. It also enables the VPC owners to provide new services more quickly.
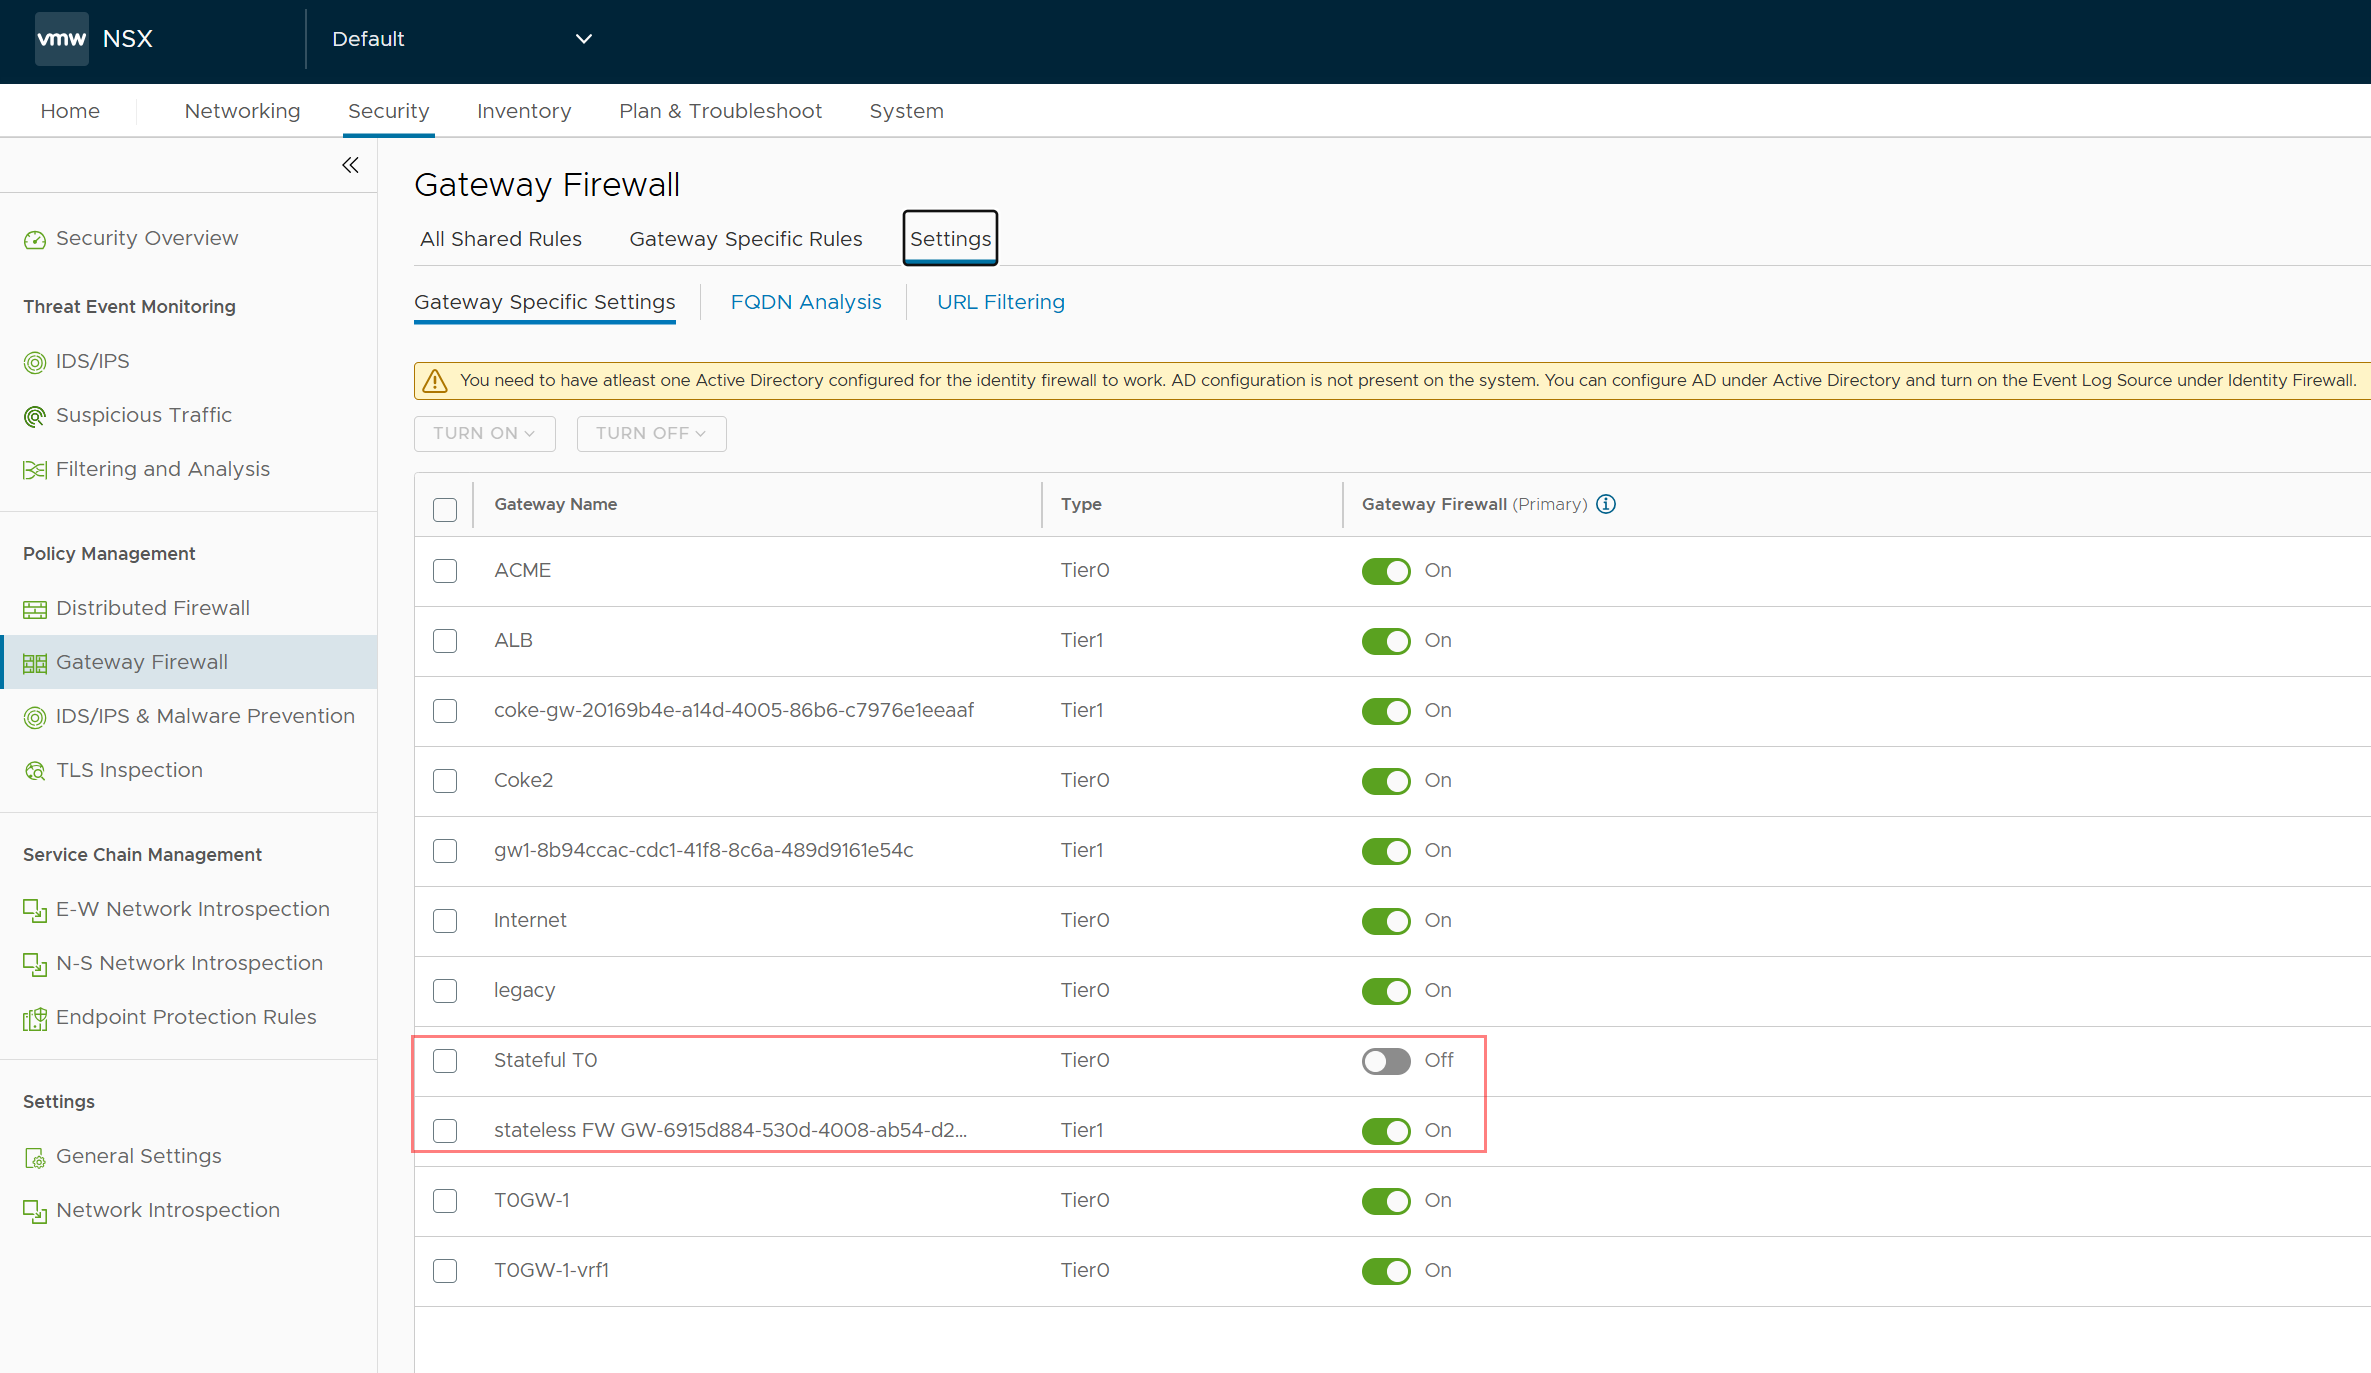
With the new Broadcom licensing changes related to NSX only the stateless firewall is included in the base VCF/NSX license while statefull firewall needs to be licensed separately. VMware Cloud Dir…
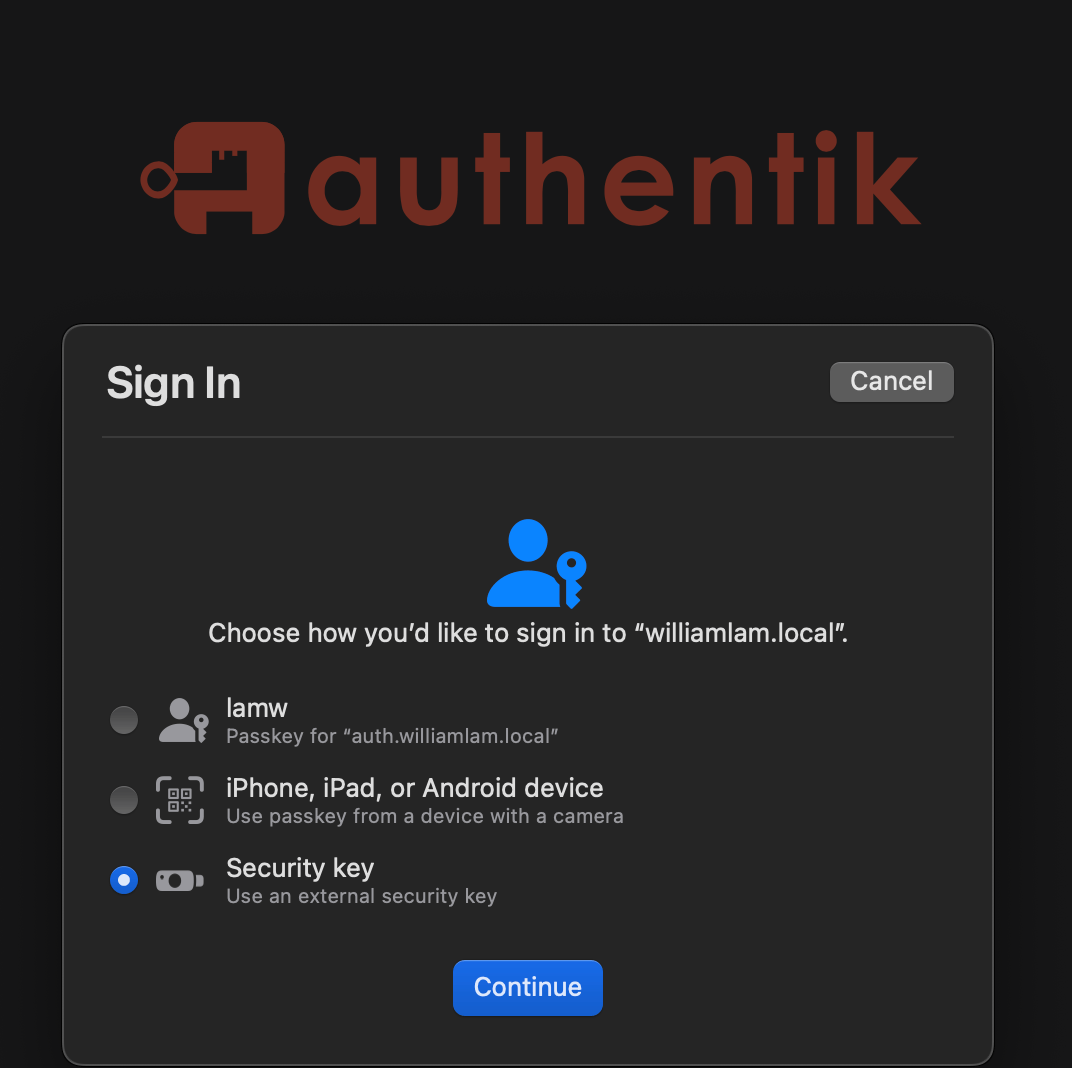
After spending some time playing with a couple of self-hosted Identity Providers solutions like Authentik and Keycloak for use with vCenter Server Identity Federation, I was curious about their Mul…
The ABC analysed 29 million stolen codes to help you avoid using an insecure one.
Why the OAuth2 protocol was designed the way it is and how it works.
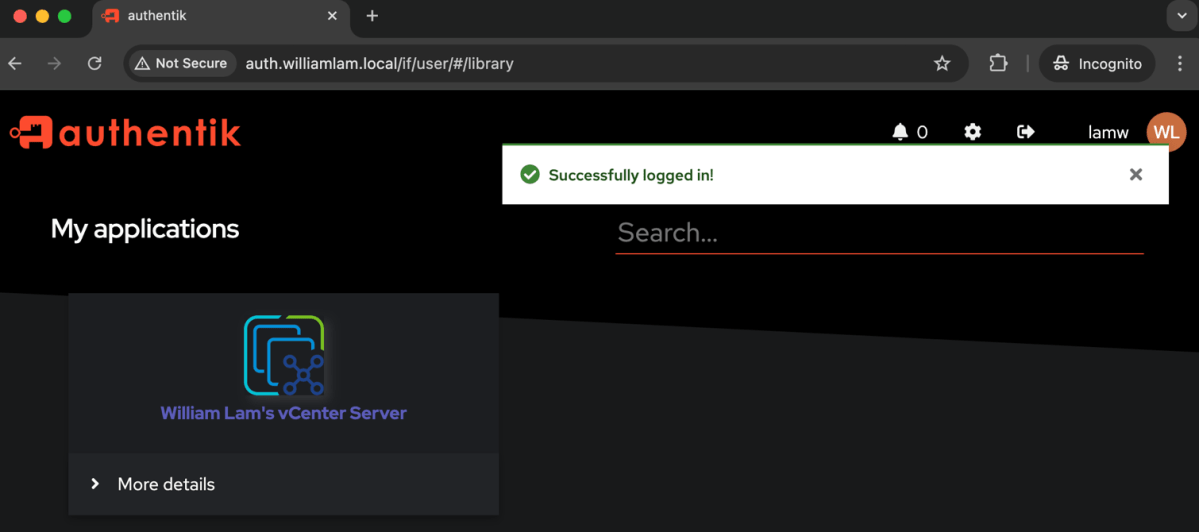
While answering a recent question on the VMware Reddit Community, I came to learn about Authentik, an open source identity provider (IdP), which is pretty feature rich and best of all, you can self…
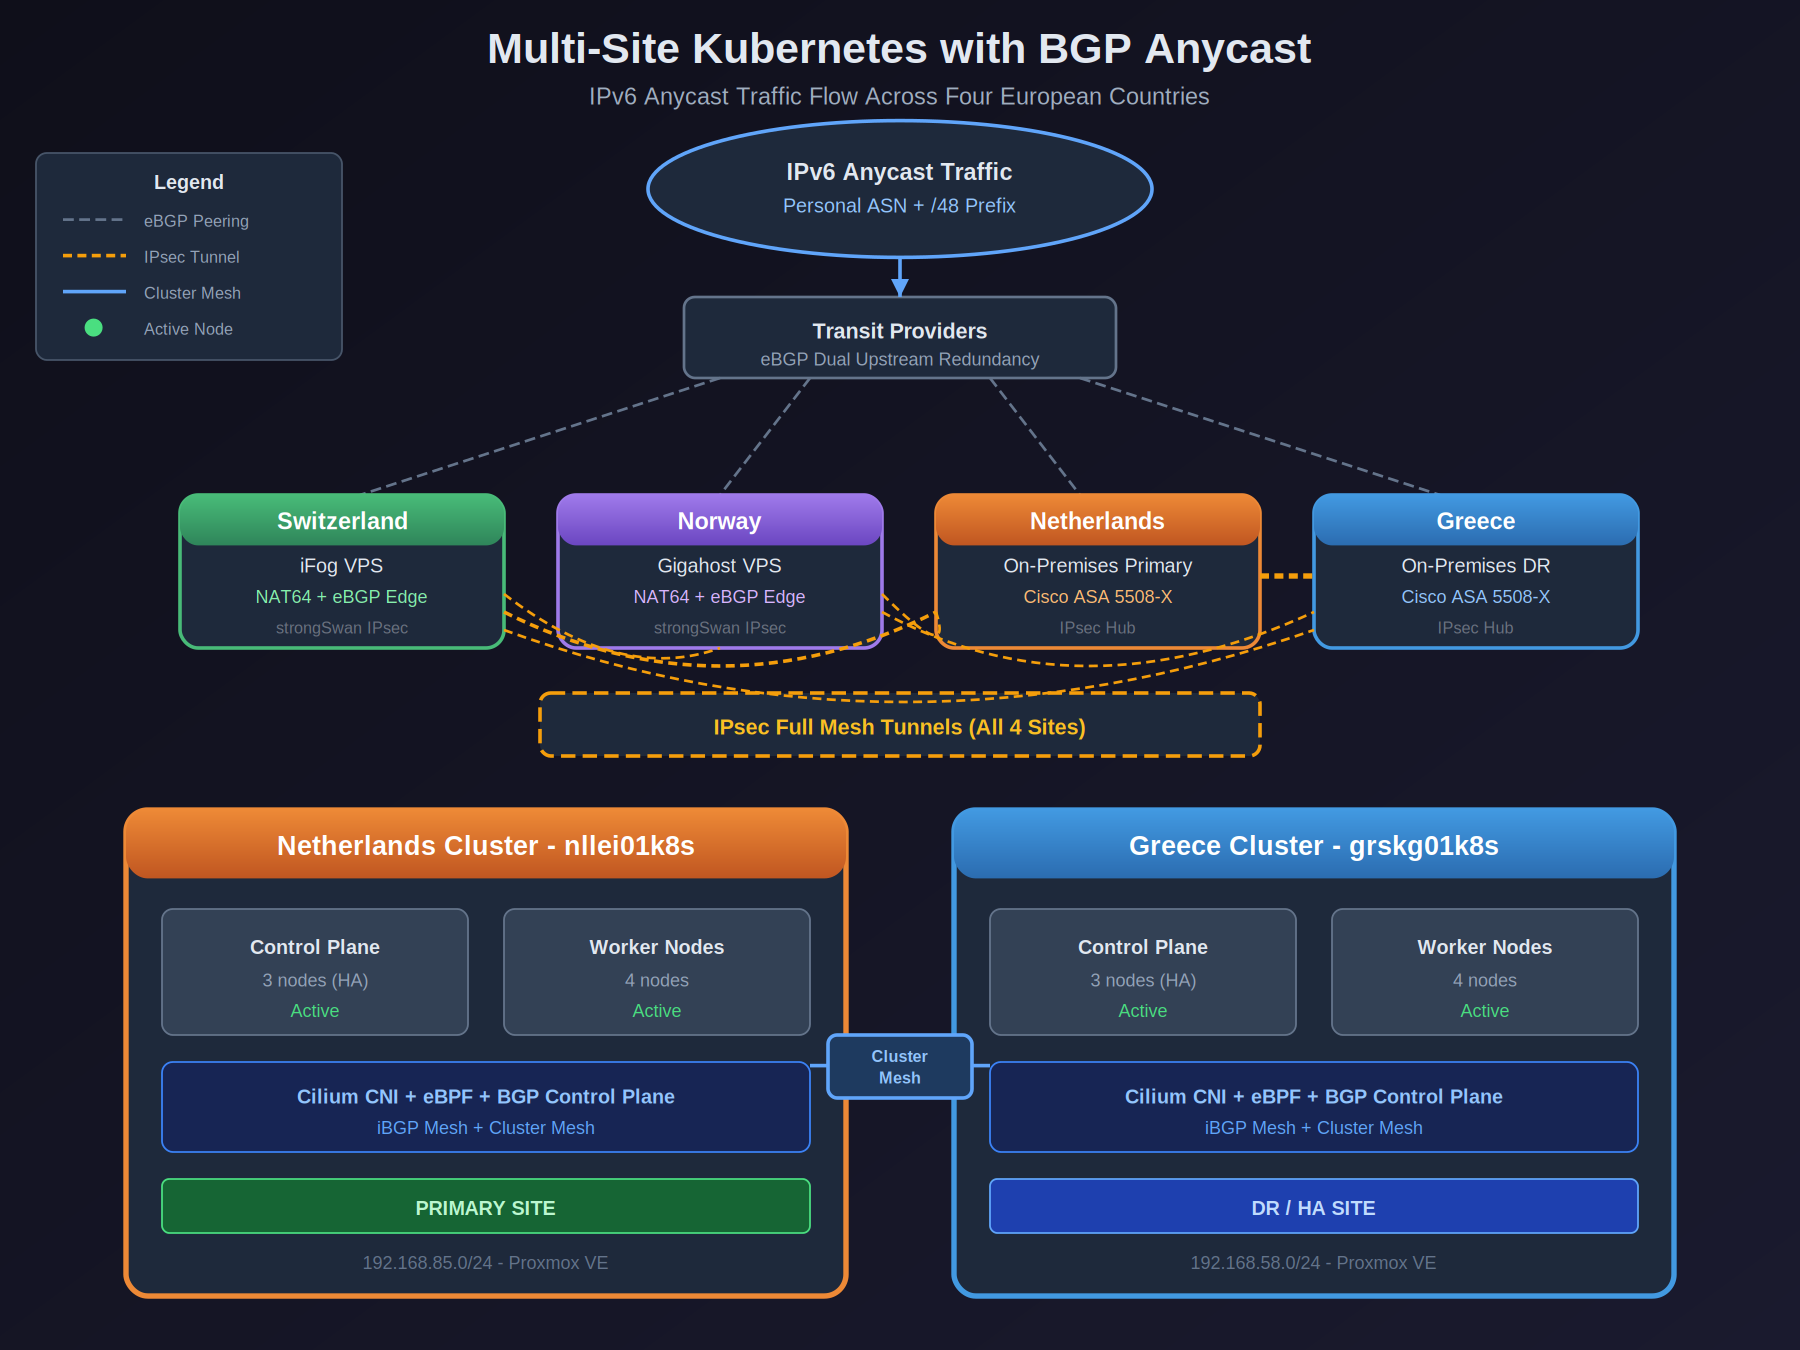
How I connected Kubernetes clusters across 4 countries with my own ASN, BGP peering, and perhaps too many IPsec tunnels
Don't forget to uv self update before trying those
Hola,
Recently, I have made several changes to the AsBuiltReport.Veeam.VBR script, so I will summarize here all the new capabilities added.
Here is the link to the most recent report in HTML format: Report The first change I will discuss is the support for Microsoft Entra ID. In this case the Veeam Backup & Replication (VBR) Powershell module allows extracting the information of the Tenants that are configured in the VBR infrastructure.
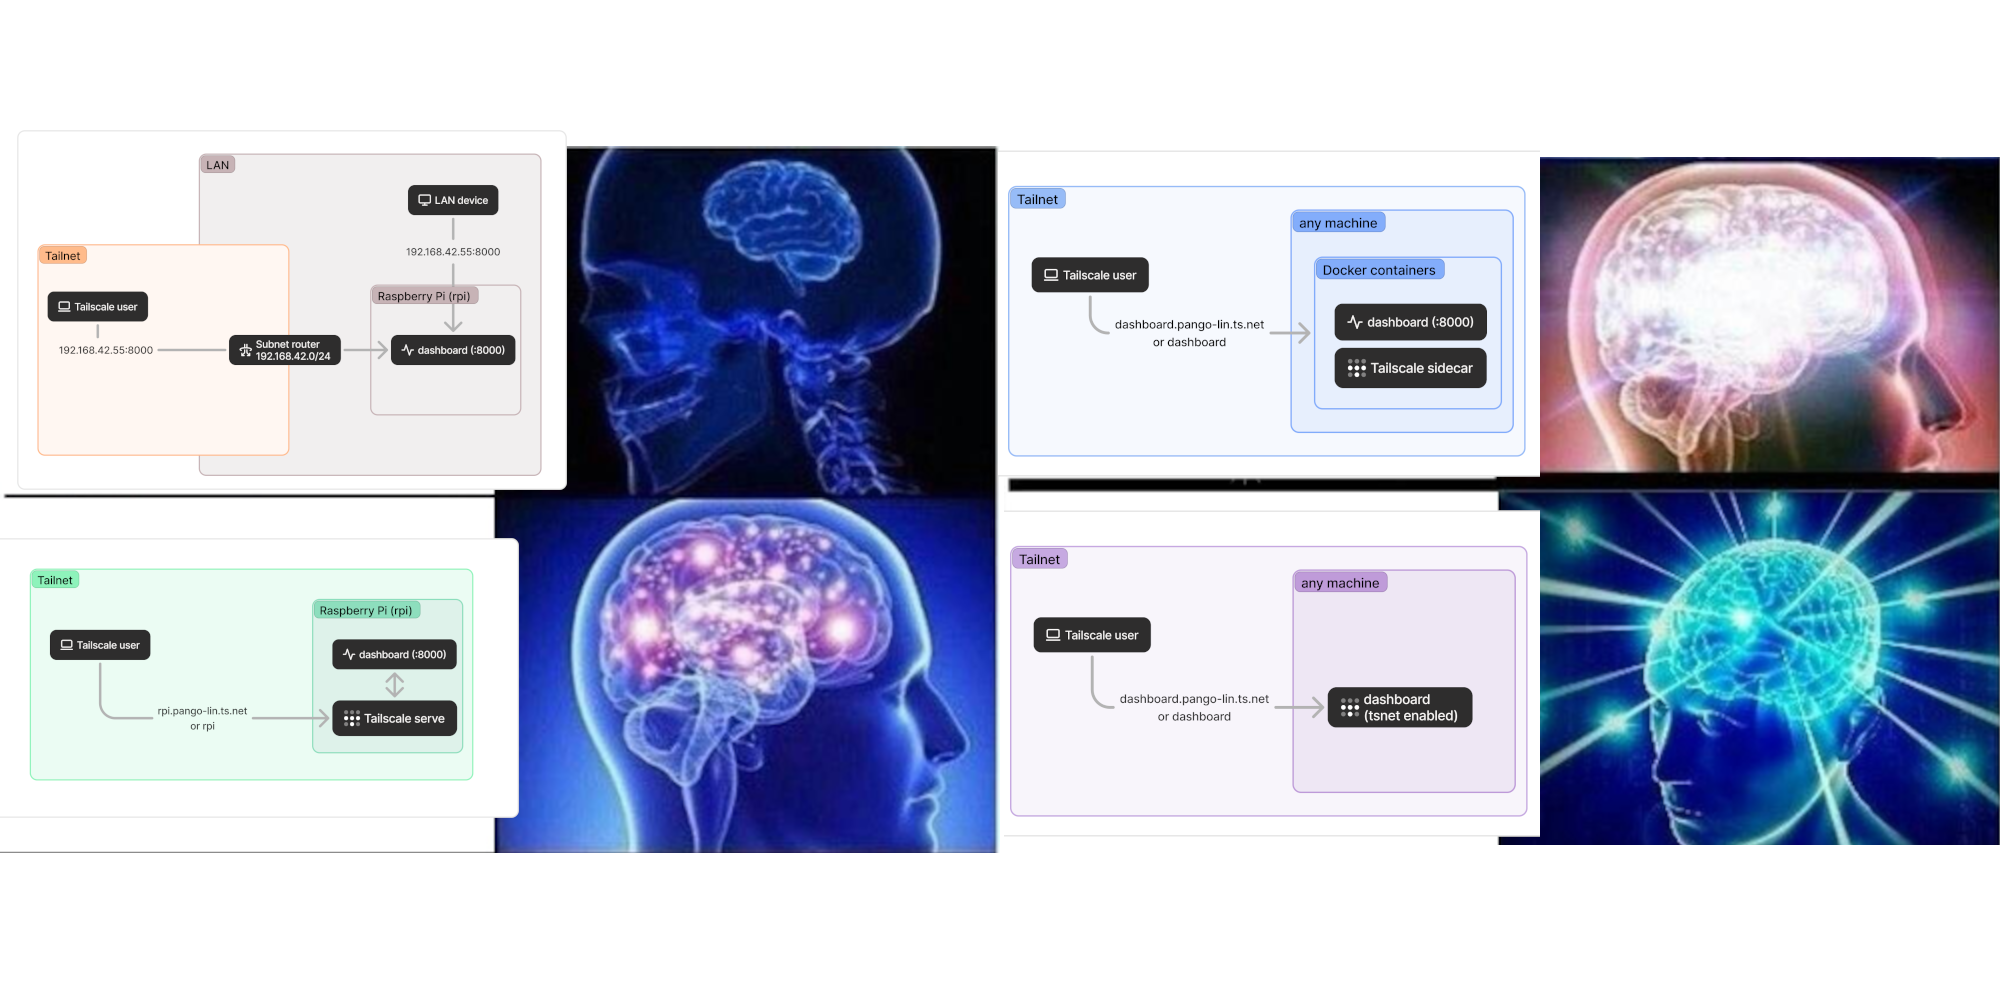
Let’s say you’ve got some kind of service you want to connect to through Tailscale. How do you make it accessible over your tailnet? It's easy for decision paralysis to set in here, so let's consolidate some of the possibilities in one place.
30 November 2024
Why you should use MAC Learning
Mac's Tech Blog
Using Linux's fancy networking to keep torrent traffic private
Let's walk through a common scenario.
A rant about caring
Ça fait un moment que j’utilise Github comme support OAuth2 pour m’authentifier sur des applications. Toutefois, je me suis toujours contenté de suivre une documentation sans réellement chercher à comprendre ce qu’il se passait sous mes yeux chaque fois que je voulais m’authentifier.
De ce fait, je me suis motivé à écrire cet article à propos du SSO. L’objectif est de découvrir les mécanismes disponibles pour gérer une grande quantité d’utilisateurs et leurs accès aux applications de l’infrastructure.
After having automated the downloading of bundles for an offline depot in my lab I got the idea of experimenting with hosting it using a containerized nginx instance.
While I was testing the new Release 8.0.3 from Broadcom, I ran into a few problems getting my nested lab...
Last week I wanted to replace my OpenVPN setup with WireGuard. The basics were well-documented, going beyond the basics was a bit trickier. Let me teach you want I learned.
The basics But first, let’s summarize the basics. I have a server with a hosting provider that I want to use as a VPN server. I won’t delve into details here, since there are so many great explanations on the web already (here, here, here or here), let’s just make a quick summary of a simple setup, as a base for discussing the (slightly) more advanced usages I had to configure myself:
Kubernetes doesn't load balance long-lived connections, and some Pods might receive more requests than others. If you're using HTTP/2, gRPC, RSockets, AMQP or any other long-lived connection such as a database connection, you might want to consider client-side load balancing.
Créer une infrastructure VPN hybride avec Headscale pour connecter des serveurs locaux et distants.
Smudge.ai is a Chrome extension that gives you ChatGPT-powered shortcuts in your right-click menu.
Découvrons ensemble comment utiliser le GPG pour sécuriser ses échanges (fichiers, mail, commits) et comment stocker ses clés sur une Yubikey pour plus de sécurité !
Adventures trying to minimise disk usage for servers
Dans cet article, je vous donne une première définition de ce qu'est le GitOps et comment le mettre en place avec ArgoCD dans un environnement Kubernetes.
In my 2022 December rumination about vCF I delved into how a union between VMware Cloud Foundation and a credential storage solution could make for a powerful combination.
After a homelab crash, the VCSA file-based backup isn't working anymore. In this post I'm describing how I was able to get the VMware Postgres Archiver service back into operating state by interfere with vCenters vPostgres instance.
Vault est un outil de gestion des secrets développé par Hashicorp. Il permet de stocker et de gérer ces derniers de manière sécurisée. Dans cet article, nous allons voir comment utiliser Vault pour gérer les secrets de vos applications.
Learn why DNS needs security through tacos, crabs, and cryptographic laughs. How DNSSEC Works turns complex internet plumbing into an illustrated adventure.
Slow Rust Builds?
Here are some tips to speed up your compile times.
This list was originally released on my private blo…
Découvrez la sélection de nos derniers travaux. Des projets Cyllene multiples regroupant de nombreux métiers afin de vous offrir une prestation sur-mesure.
Overview VMware recently released full support for Azure Active Directory (now called Entra ID) integration with vCenter with release 8.0 U2. Unfortunately, their documentation about integration had some major gaps, compelling us to write this guide. VMware’s documents initially recommended opening your vCenter server URL to the public (which you should NEVER do). They’ve since...
Sysadmin doing syadmin stuff
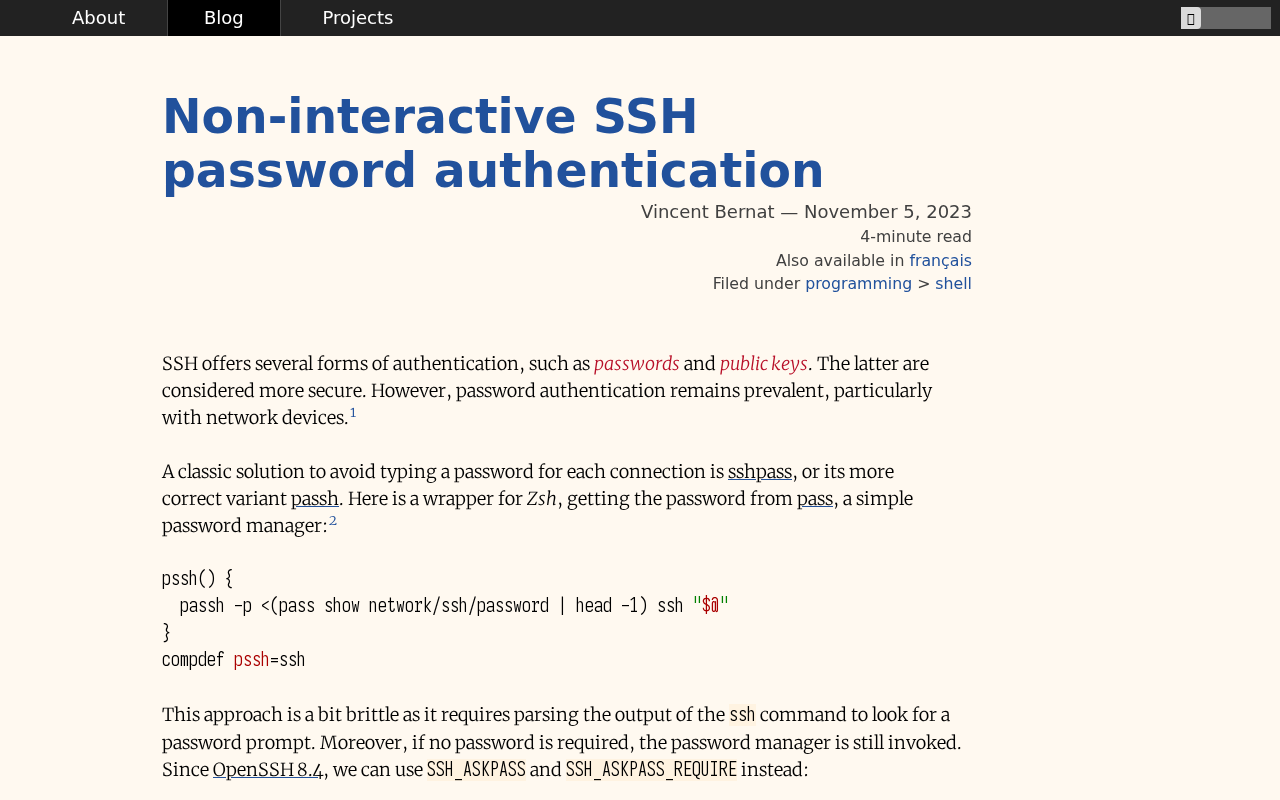
Instead of using sshpass to non-interactively provide an SSH password, here is a simpler approach by harnessing the built-in features of OpenSSH...
Prometheus est une solution de supervision créée par Soundcloud en 2012 et open-sourcée en 2015. C'est un incontournable qui se démarque via l'intégration à de nombreux services tiers non supportés nativement.
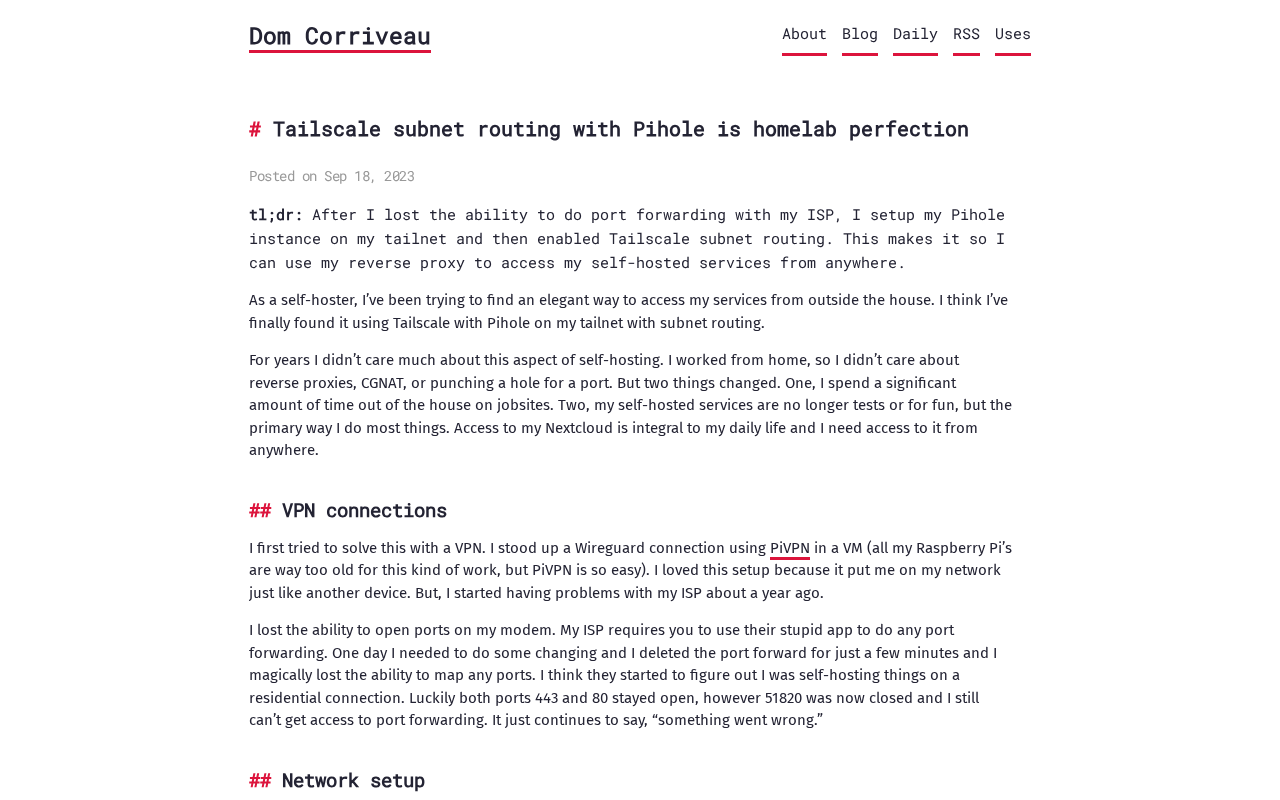
Mapping Pihole to Tailscale and enabling subnet routing has made accessing my homelab outside the house an absolute joy.
Terraform Associate est une certification officielle de HashiCorp. Celle-ci permet de valider vos connaissances sur Terraform via un examen en ligne. Je vous partage mon expérience dans cet article !
Want to secure your Proxmox server with a trusted SSL certificate from Let's Encrypt? Check out my post! Includes Home Assistant integration too!
Exploring the balance between relying on AI assistance like ChatGPT and maintaining personal skills in a world of increasing AI capabilities.
Cert-Manager est un programme permettant de gérer les certificats (ainsi que leurs renouvellements) sur des clusters Kubernetes. Nous allons voir comment déployer Cert-Manager et générer nos premiers certificats
Lorsque nous avons de nombreux serveurs, il convient d'automatiser chacun des déploiements que nous réalisons. Et lorsque la majorité sont sous Debian, ces déploiements peuvent prendre la forme de fichiers .deb. Nous verrons donc sur cette page comment créer notre propre dépôt Debian
A next-generation sharing platform built on top of OpenZiti, a programmable zero-trust network overlay.
Lorsqu'on multiplie les infrastructures (locales, distante etc..), avoir un VPN de Mesh permet de vous faciliter la vie. Nous allons donc installer et configurer Tinc
Historically, we have rarely talked about how our servers fetch
the content from the Internet. In this blog we’re going to cover
this gap. We'll discuss how we manage Cloudflare IP addresses
used to retrieve the data from the Internet, how our egress
network design has evolved, how we optimized it for best use
of available IP space and introduce our soft-anycast technology.
This is my documentation of how I publish my notes from a private [[Obsidian]] vault to my
How Relational Databases Work. This post talks about how indexes and transactions work on the inside of relational databases.
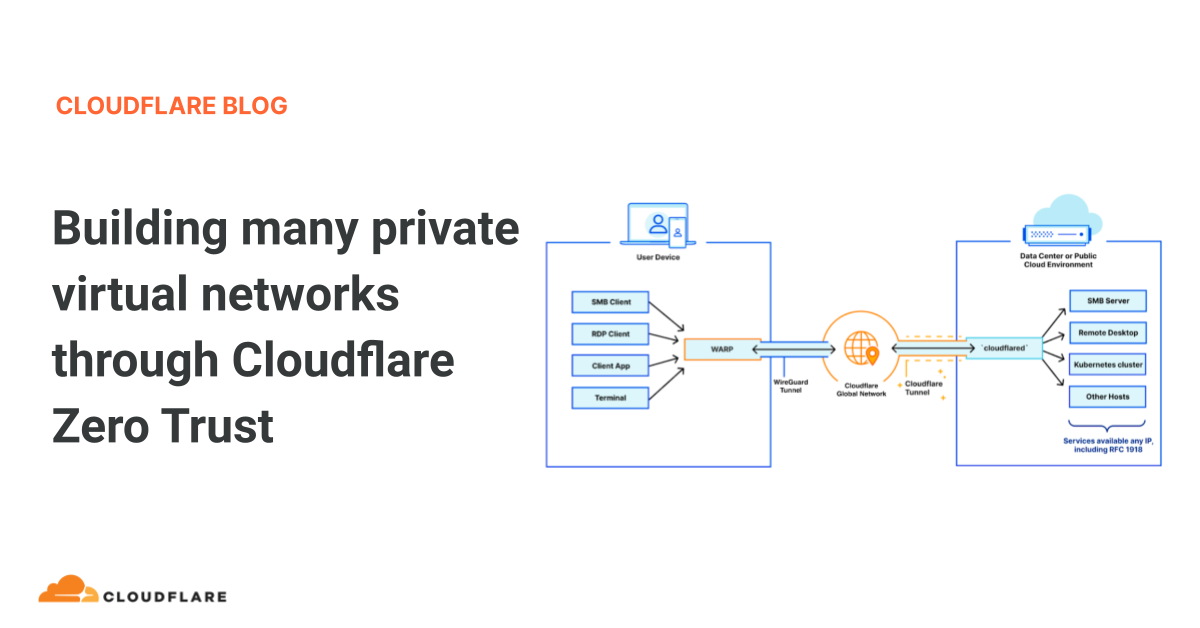
Starting today, we are thrilled to announce that you can start building many segregated virtual private networks over Cloudflare Zero Trust, beginning with virtualized connectivity for the connectors Cloudflare WARP and Cloudflare Tunnel
A technical dive into traditional TCP proxying over HTTP
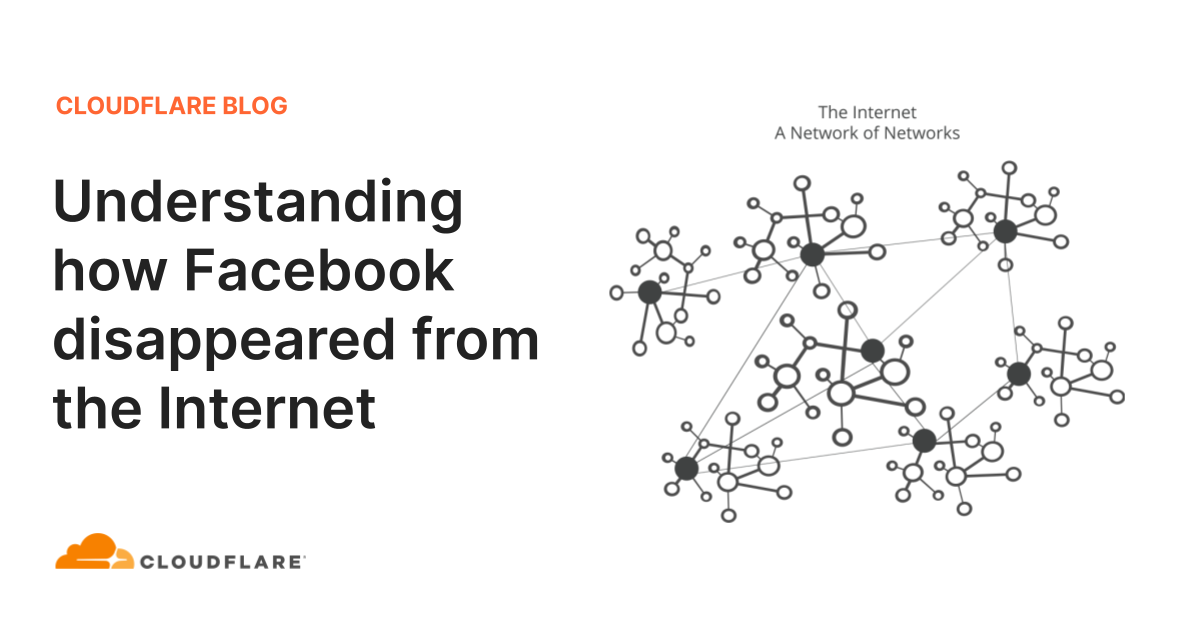
Today at 1651 UTC, we opened an internal incident entitled "Facebook DNS lookup returning SERVFAIL" because we were worried that something was wrong with our DNS resolver 1.1.1.1. But as we were about to post on our public status page we realized something else more serious was going on.
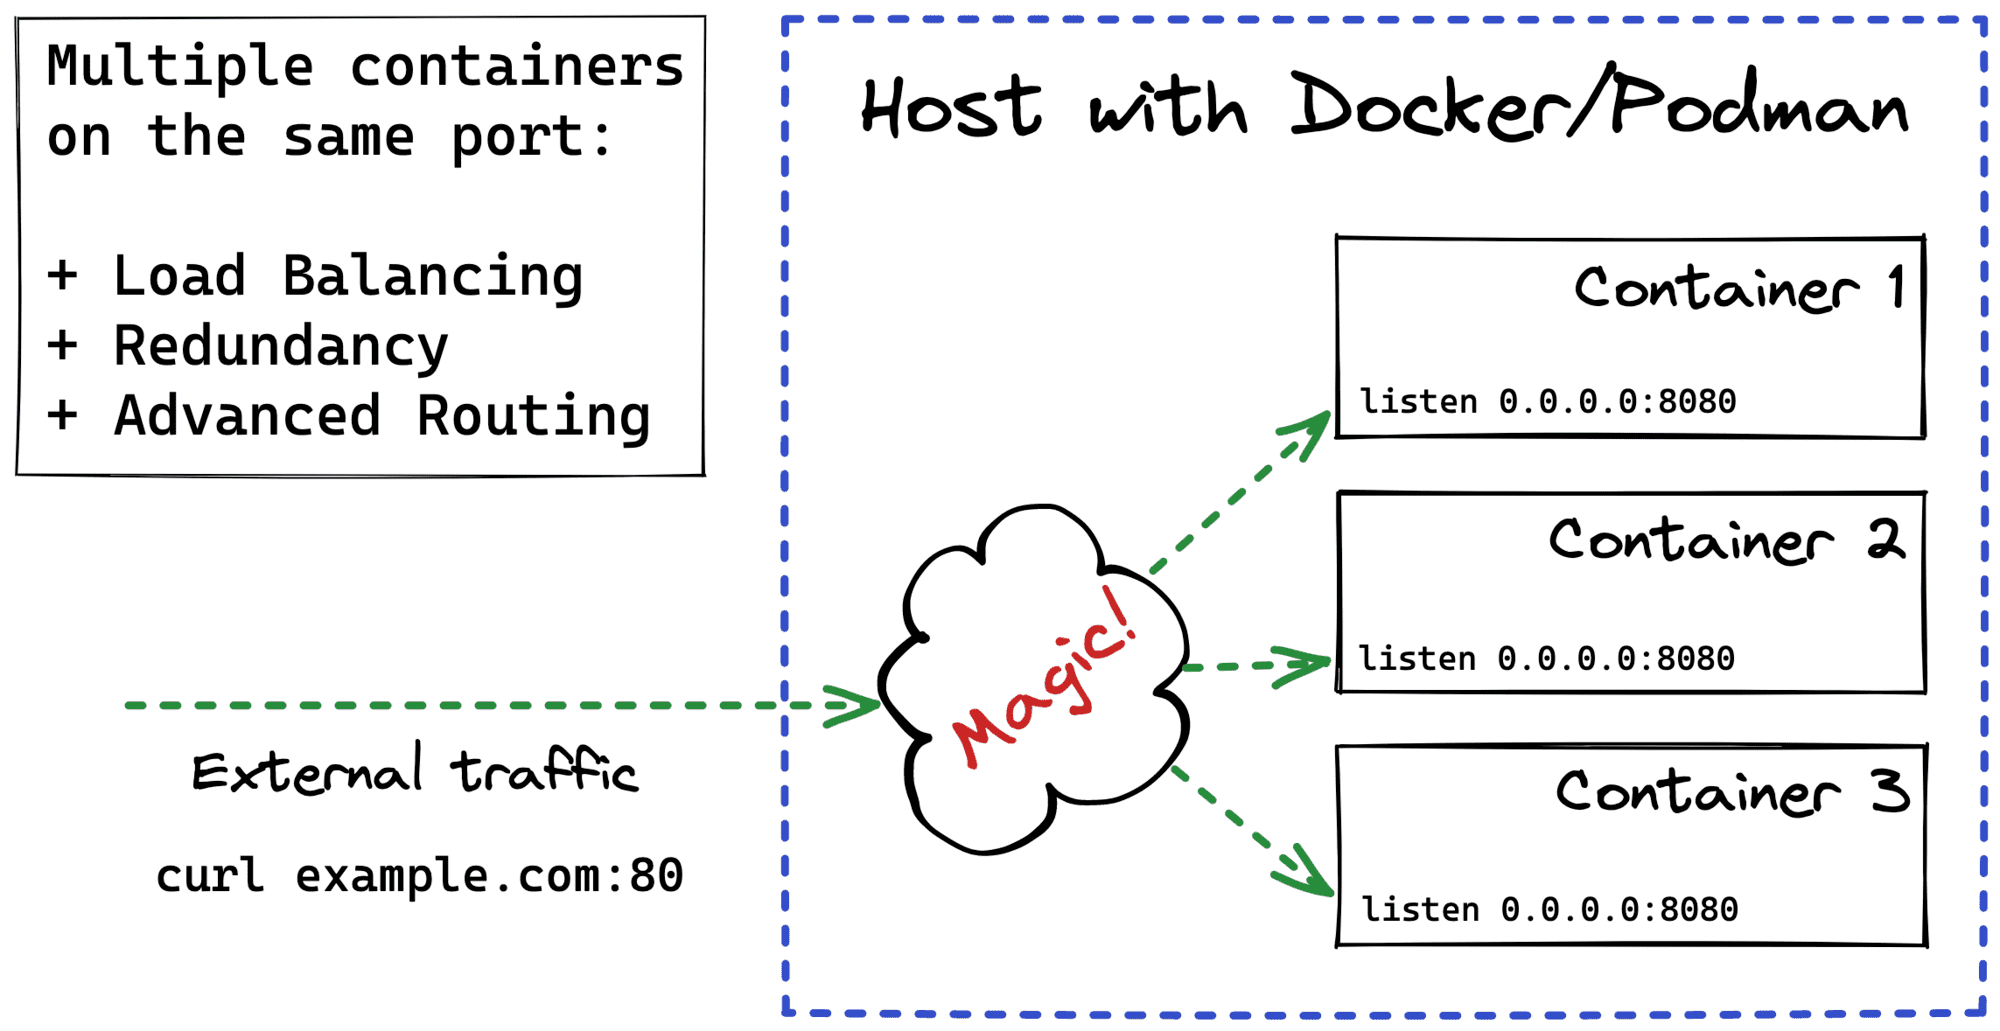
How Docker publishes container ports on the host? How to use SO_REUSEPORT to make multiple containers listening on the same port? How to use iptables to make multiple containers exposed on the same port?
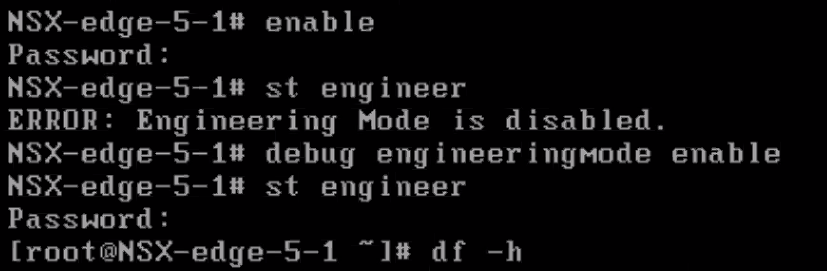
If you have ever tried to troubleshoot an NSX-v Management Appliance or Edge, you probably noticed that you are quite limited in the execution of your controls. That’s because in NSX-v you are standardly limited with most of the time only esxcli, even when you are logged in as admin.
To get past
Find the right requests and limits can be tricky. Instead of guessing, you could inspect the application at runtime and extrapolate the values.
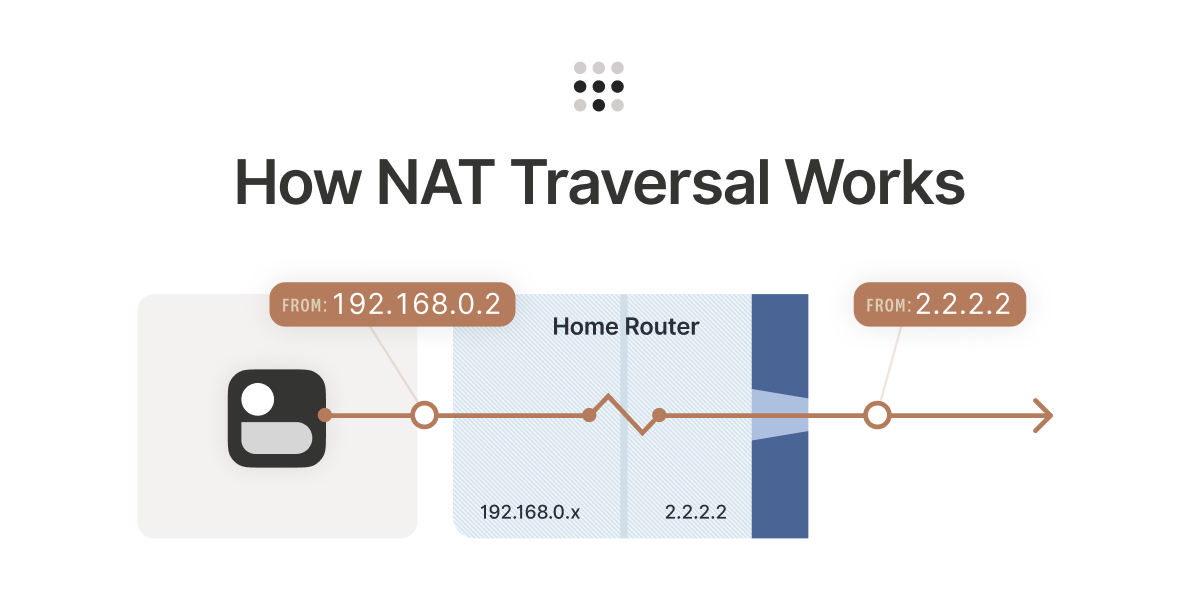
Learn how NAT traversal works, how Tailscale can get through and securely connect your devices directly to each other.
Todays topic is VMware Cloud Director inter-tenant routing with a NSX-T backed provider VDCs (pVDC). The reason for writing this post is that some use-cases require routed connectivity between Org VDC
Docker vous permet d’empaqueter facilement vos applications et services dans des conteneurs afin de pouvoir les utiliser partout. Cependant, lorsque vous tra…
Applying DevOps to networks.
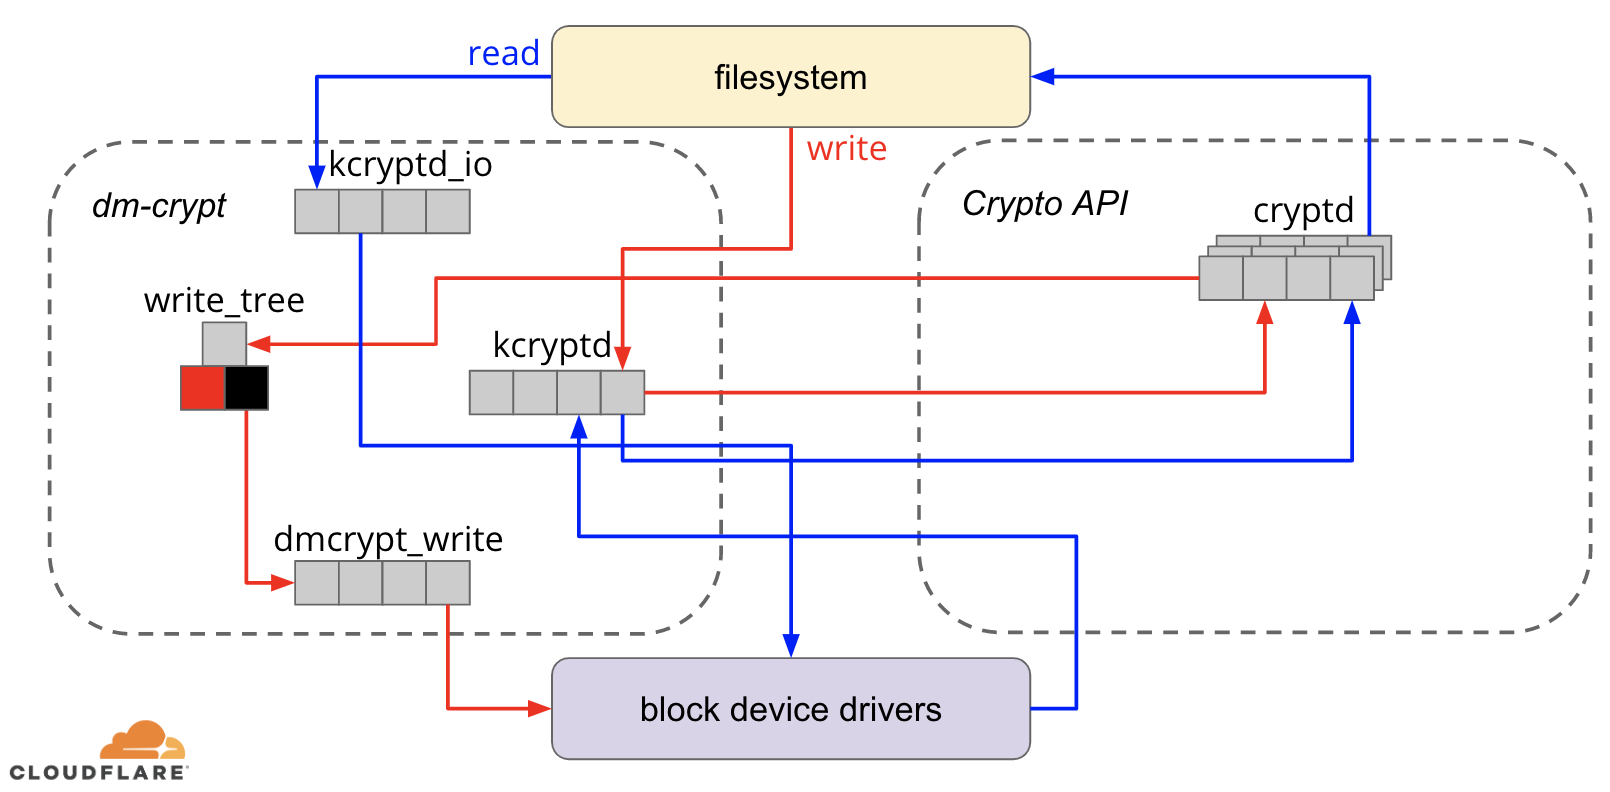
In this post, we will investigate the performance of disk encryption on Linux and explain how we made it at least two times faster for ourselves and our customers!
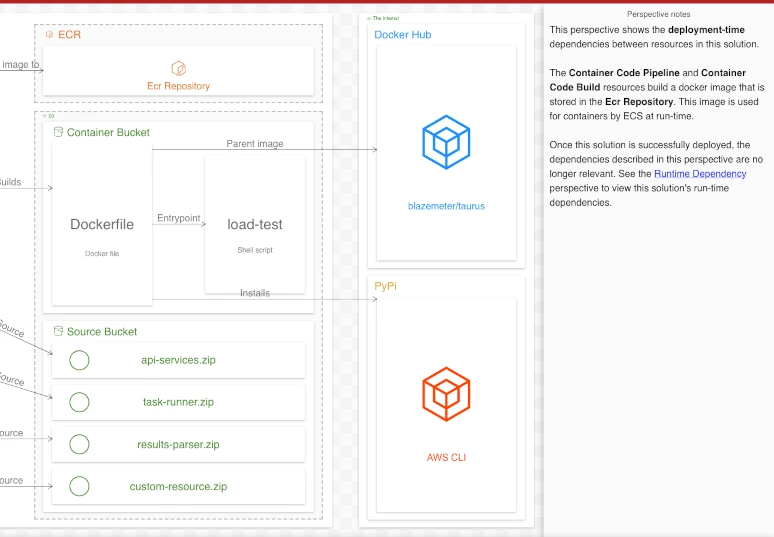
A rundown of seven common mistakes is system architecture diagrams and how to fix them
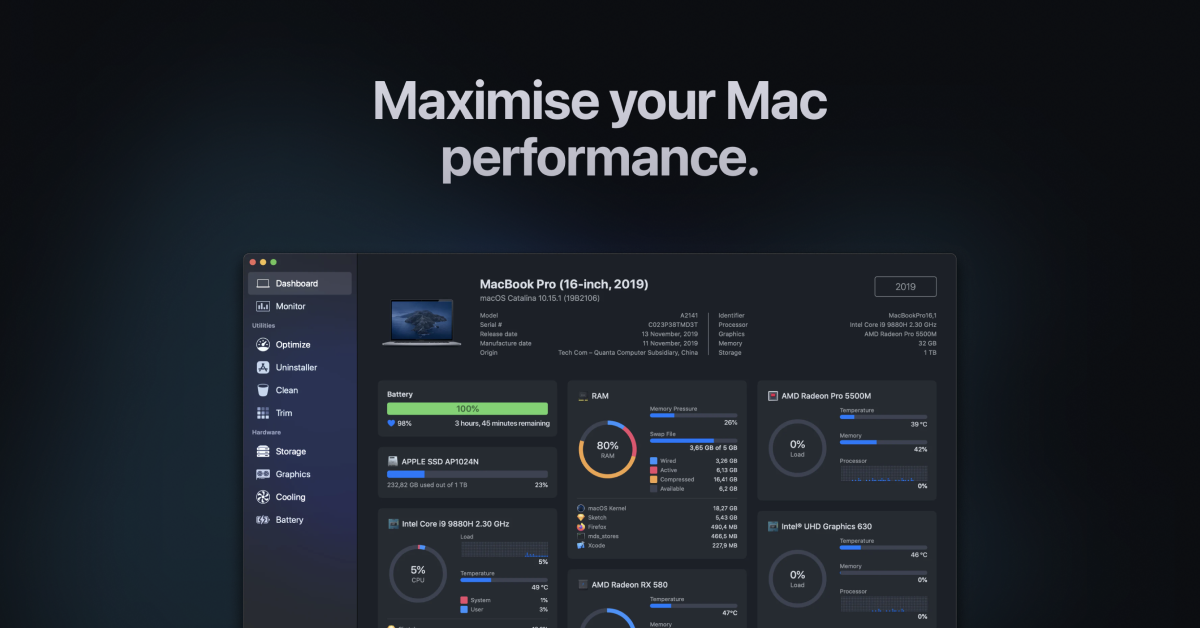
Monitor CPU, GPU, and storage, clean junk files, check battery health, and keep your Mac fast with Sensei. Free download.
Guest Post: Why does half the Internet use a TTL of 1 minute or less?
How to backup and restore K8s applications on vSphere
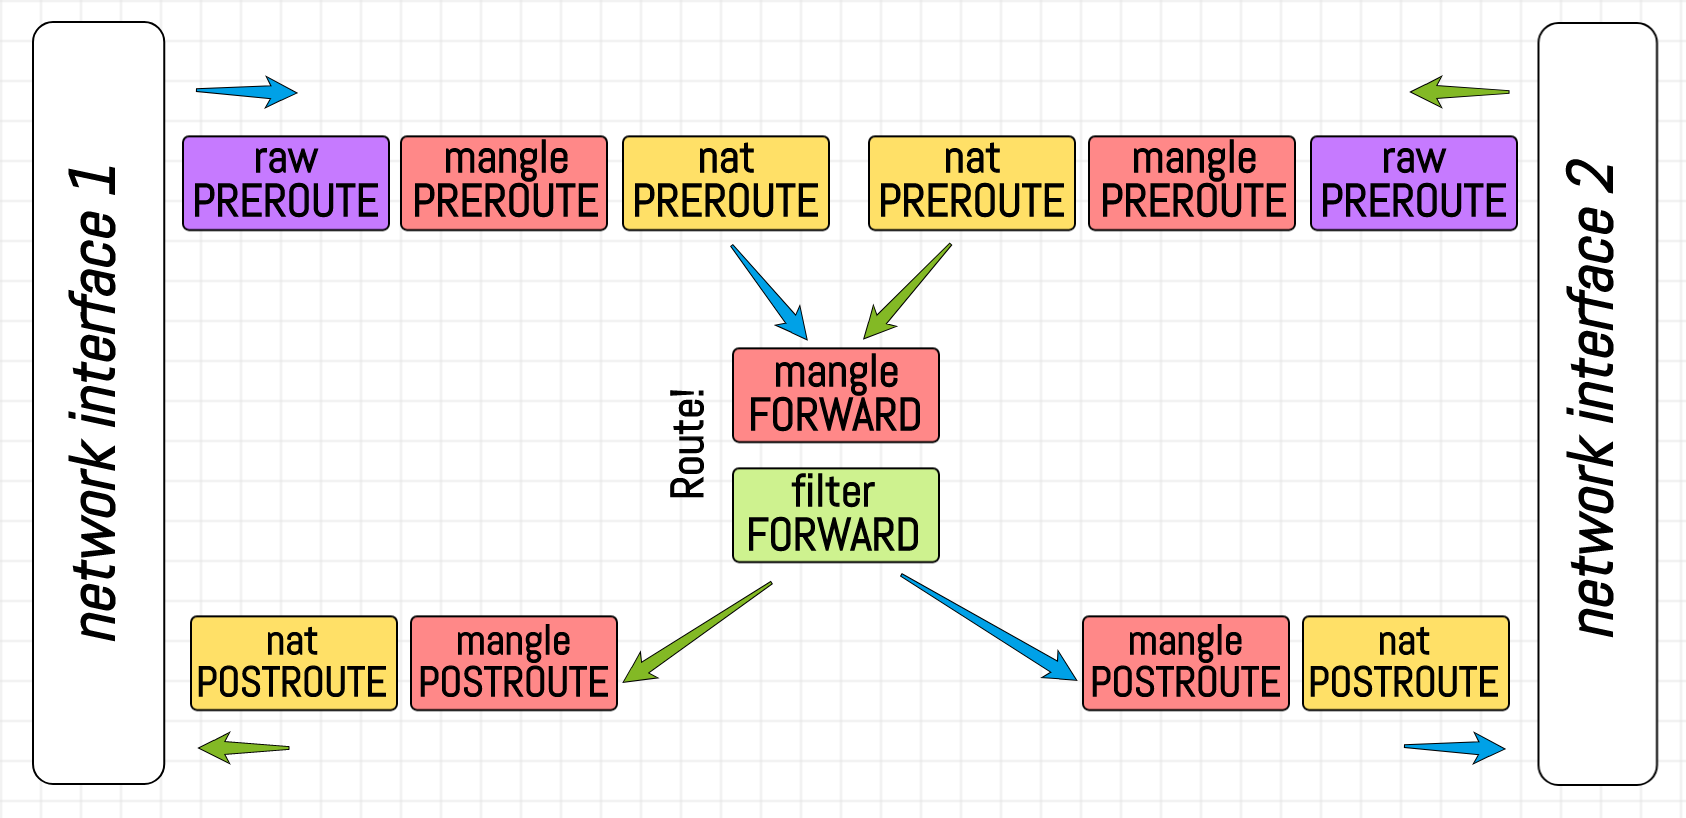
What are iptables chains, rules, policies, and tables? Describe iptables in layman's terms.
Implementation of redundant site-to-site VPNs on Linux with WireGuard (instead of IPsec) and BGP.
VXLAN is an overlay network for L2 traffic over an existing IP network. One deployment option is BGP EVPN.
On Linux, a network bridge without any IP address configured will still process IP packets. How to disable such a feature?
Automation is an increasingly interesting topic in pretty much every technology discipline these days. There’s lots of talk about tooling, practices, skill set evolution, and more - but little conversation about fundamentals. What little is published by those actually practicing automation, usually takes the form of source code or technical whitepapers. While these are obviously valuable, they don’t usually cover some of the fundamental basics that could prove useful to the reader who wishes to perform similar things in their own organization, but may have different technical requirements.
A short while back I participated in an internal event. A number of priority customers of our internal cloud service were invited for a feedback session, to voice their thoughts, listen to roadmap sessions and just to get to know each other.
There was one comment made there by one of the participants that has been on my mind since then, and it was something along the lines of:
“I have been using AWS longer than I have been using our internal cloud service – that is more than 5 years.
In a recently published article, Paul Vixie, past author and architect of BIND, one of the most popular internet domain servers, explains why DNS...
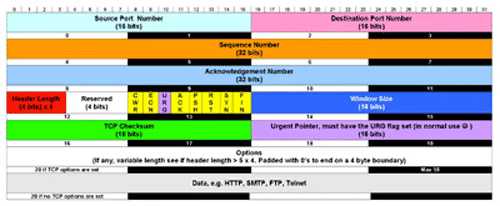
tcpdump is the world's premier network analysis tool—combining both power and simplicity into a single command-line interface. This guide will show