
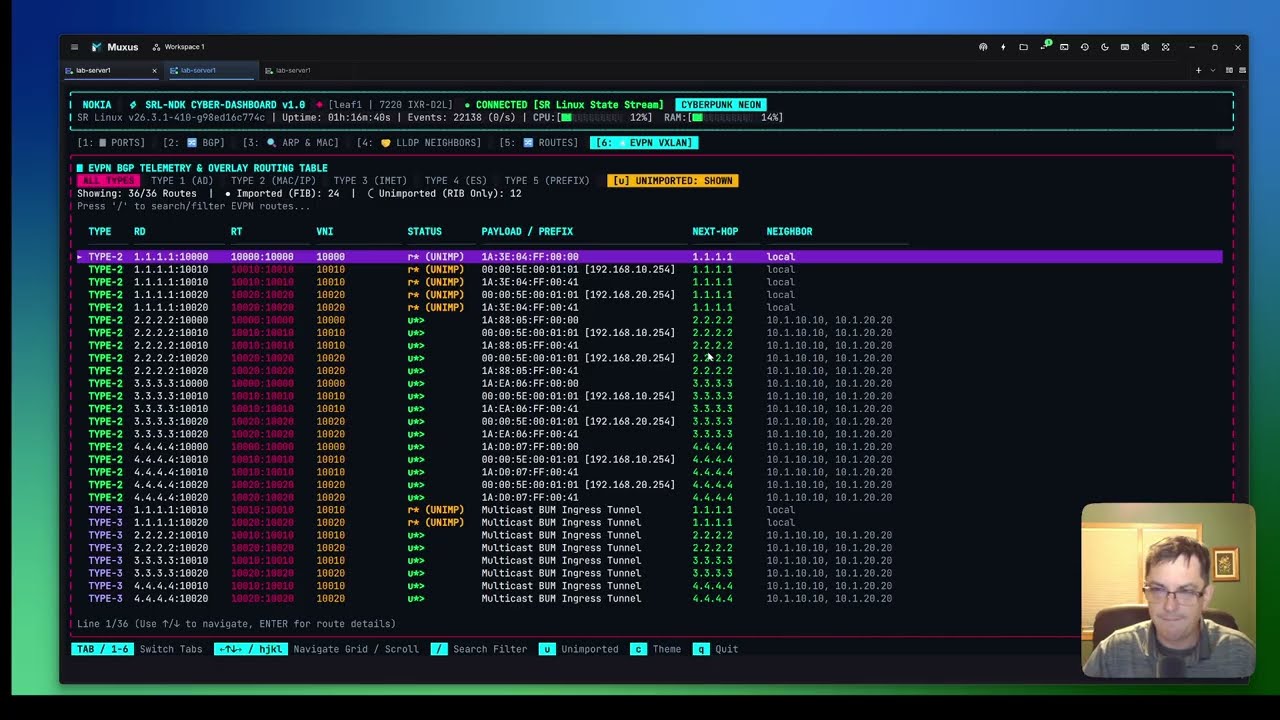
SR Linux Demo App: srl-tui
www.youtube.comSRL-TUI is a demo app demonstrating the power to extend Nokia's SR Linux.
259 links
SRL-TUI is a demo app demonstrating the power to extend Nokia's SR Linux.
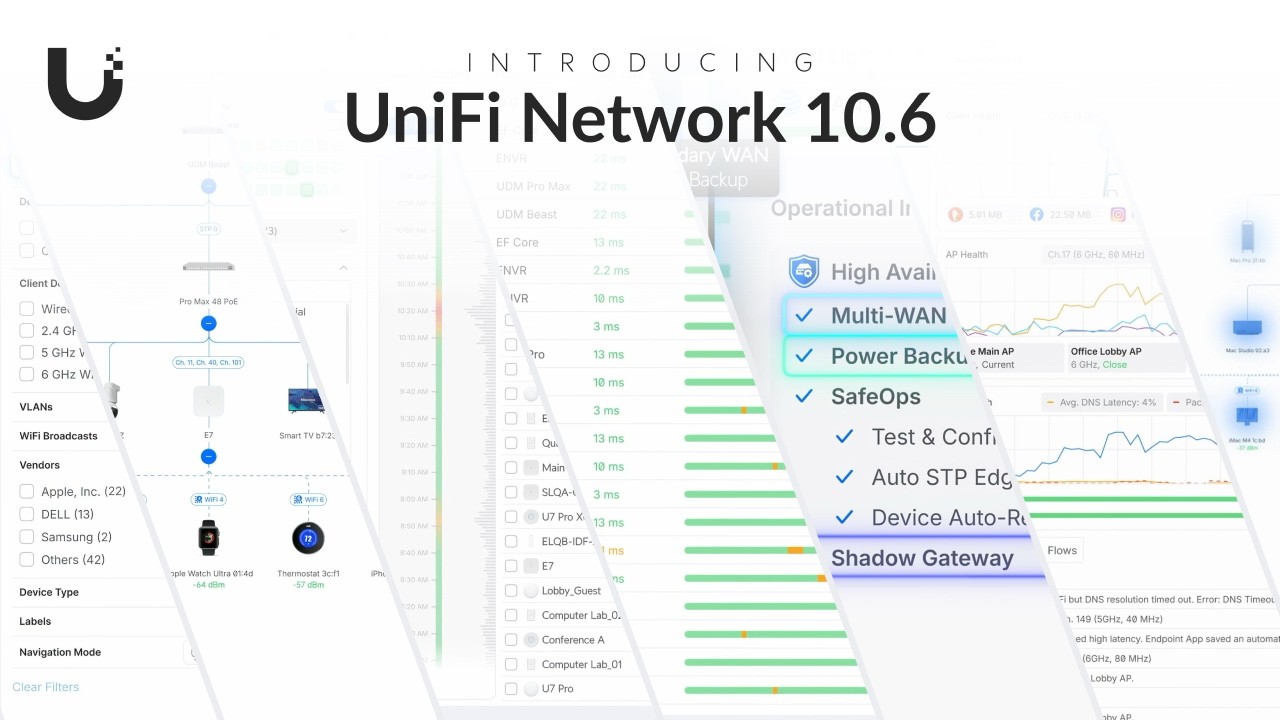
🔹 Topology Spotlight
🔹 Time Machine for Radios + Ports
🔹 Channel AI Nightly Automation
🔹 Port Locking & Expanded SafeOps
🔹 High Availability Readiness Score
Five Rust-level memory optimizations to the DNS cache layout of Big Pineapple cut per-entry memory by 56%, freeing approximately 100 TB of memory across Cloudflare's fleet.
Run a Minecraft server at home with Docker Compose, then publish it to players anywhere using the NetBird reverse proxy. Works behind CGNAT, needs no port forwarding, and your friends don't install a thing.
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed. - domcyrus/rustnet
Root election, port roles, proposals and agreements, topology changes: explore RSTP through simulations powered by MSTPD compiled to WebAssembly.
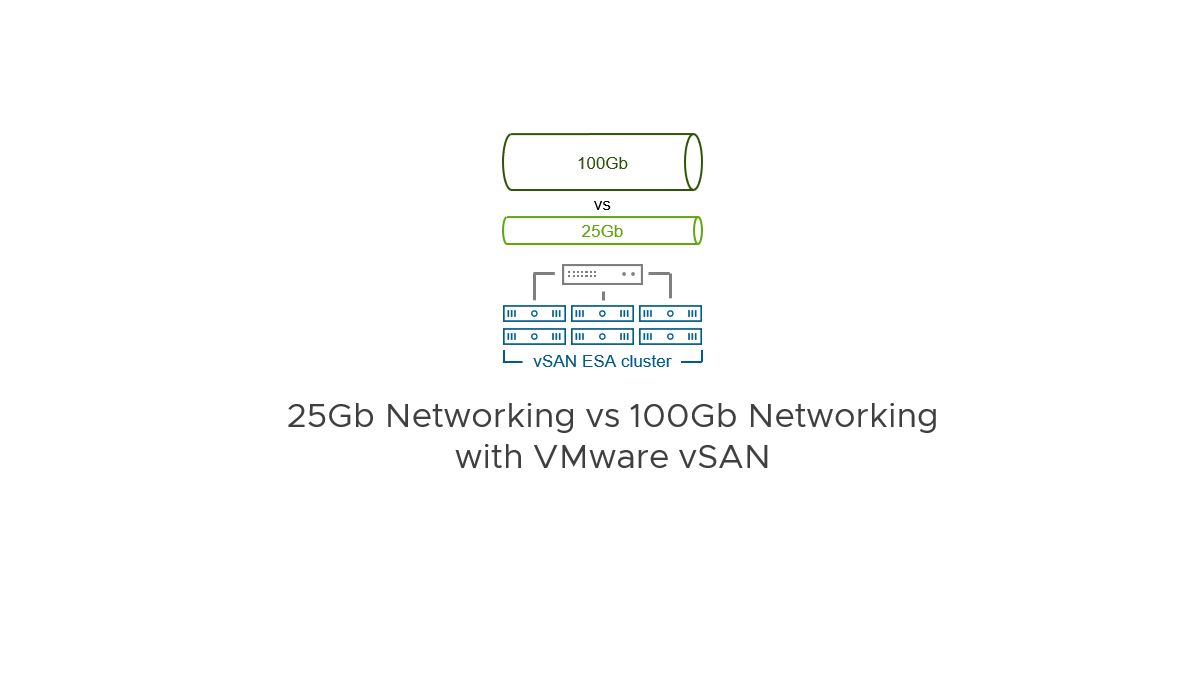
Over the past four years, the VMware vSAN Express Storage Architecture (ESA) has demonstrated extraordinary performance capabilities for our customers. But, as noted in a series of blog posts, a distributed storage system like vSAN relies not just on the hardware of the hosts, but the network fabric that connects them. The post: “What to … Continued
This is a full tour of my homelab which runs KTZ Systems and most of my digital life. I walk through the network, Proxmox and Ceph cluster, storage servers, cameras, core services and local AI hardware. It may not be the neatest rack on YouTube, but it is real, reliable and built to do a job.
Unbound Dashboard In Grafana With Prometheus & Loki - ar51an/unbound-dashboard
A look inside Copilot’s network traffic, harness, memory, and how context is becoming the product.
I've probably tried close to 5 different options for access to my homelab services. Whether public or private, SaaS or self-hosted, everything ended up falling short.
Pangolin is different.
A deep dive into the DNS and Caddy design behind my Proxmox VE homelab rebuild: layered resolvers, a deliberate core/apps zone split, a Cloudflare Tunnel, and a second, fully separate Caddy for anything genuinely public.
NSX 4.x DFW memory exhaustion explained: the commands to confirm it, why rebooting makes it worse, and the paced migration that recovers hosts live.
The everyday mechanics of running DNS in my homelab: the zone file format, how Knot auto-derives every PTR record, adding and removing hosts and zones, and what actually happens when something goes wrong.
Learn the most common reverse proxy mistakes in home labs and how I avoid them using Traefik, Docker, proper networking, TLS, and security best practices.
Give agents and applications structured access to UniFi without exposing your controllers to the public internet.
A technical guide toNetClaw— an autonomous, CCIE-level network-operations agent built on Anthropic Claude and the OpenClaw framework, orchestrating 191 skills across 113 MCP integrations with ITSM-gat
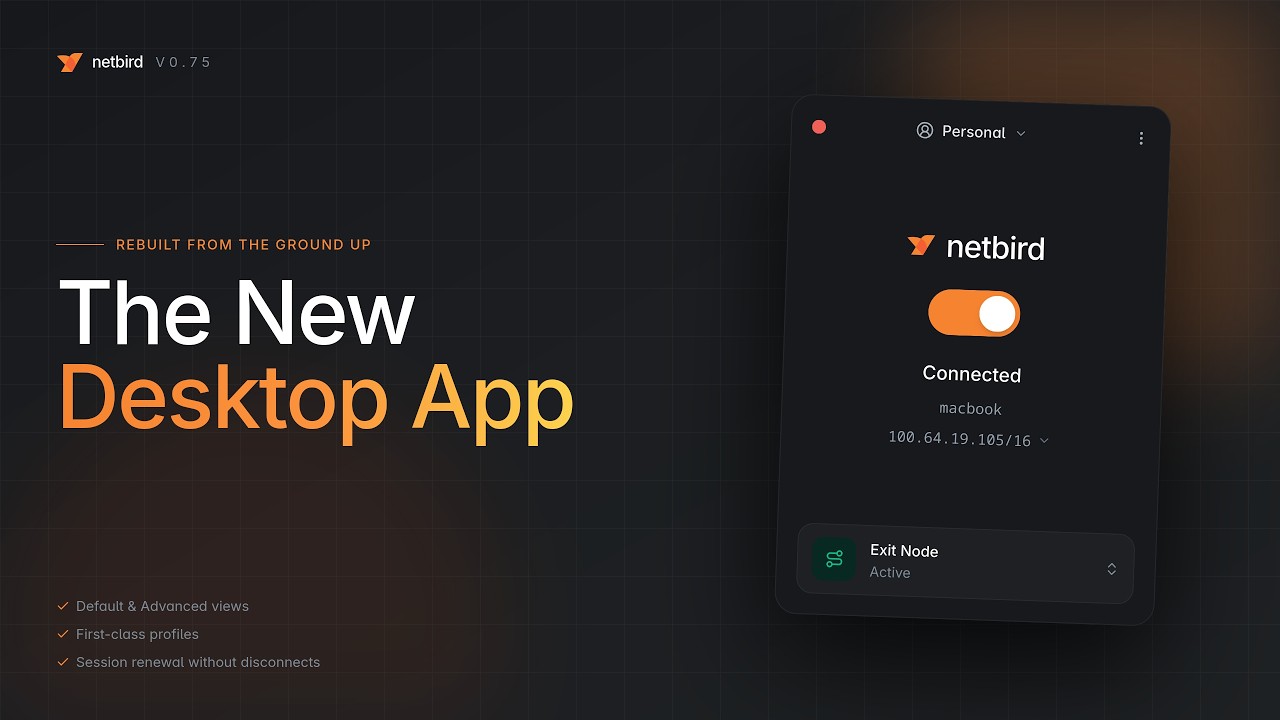
NetBird 0.75 is out! https://github.com/netbirdio/netbird/
it comes a completely refactored desktop client built on Wails 3, React, Vite, and Tailwind CSS. In this guide, we walk through the redesigned app across Windows, macOS, and Linux, including profiles, exit node switching, peer details, network resources, SSH settings, debug bundles, and the expanded MDM support for platforms like Intune. We also cover the new admin CLI for self-hosters and the optional HTTP and JSON sockets for building third-party tooling.
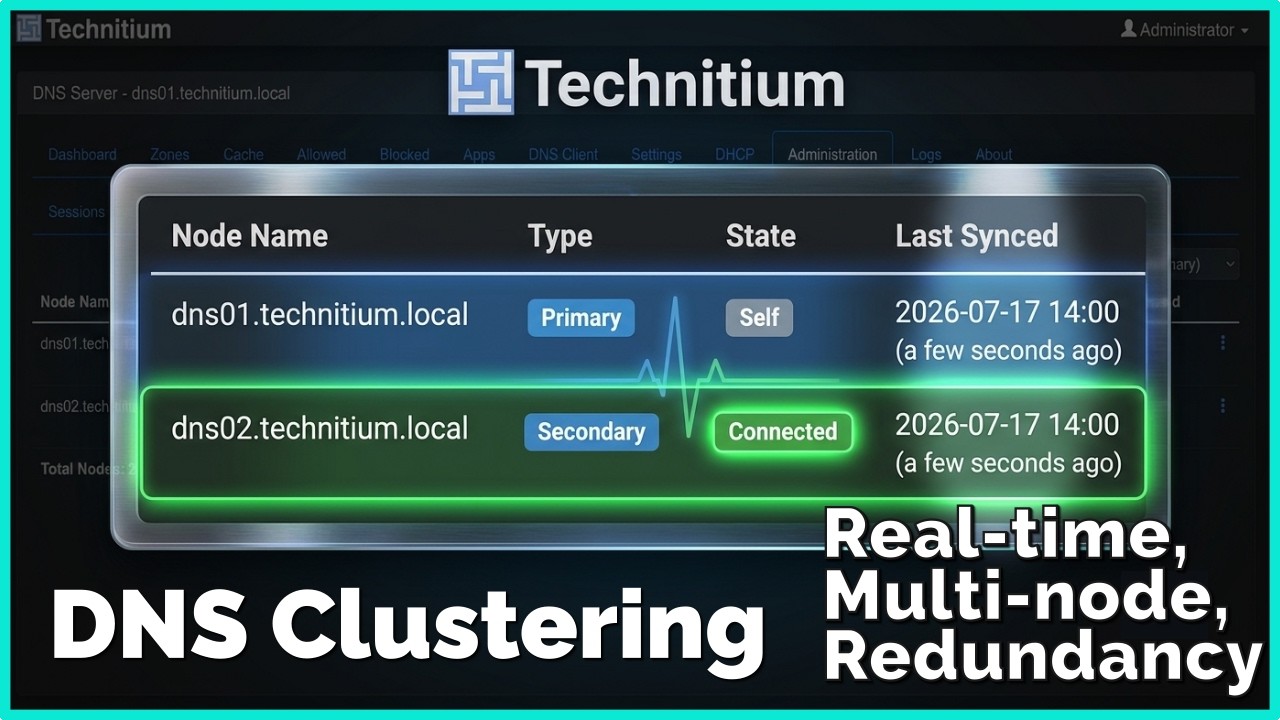
I've used and loved PiHole for years, but it's time for a change. Technitium provides the one thing I found sorely lacking from Pihole, that is clustering and real-time synchronisation between servers. In this tutorial I show how to create a cluster and configure it.
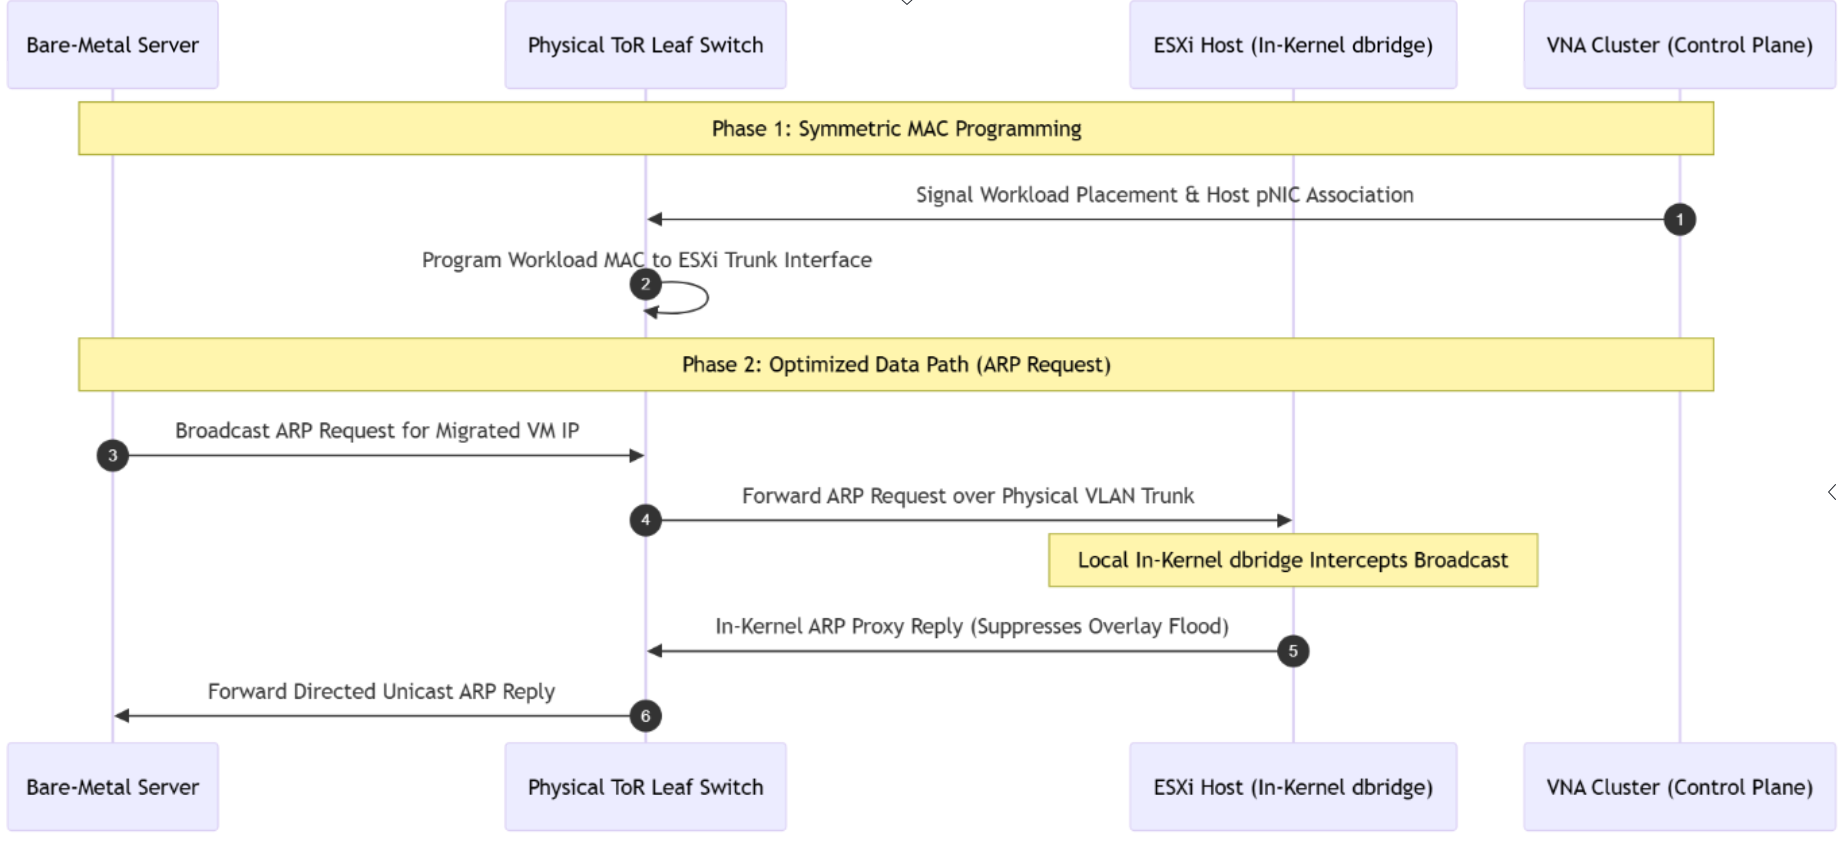
The Core Pain Point: Centralized Bridging BottlenecksThe Architectural ChallengeThe VCF 9.1 Solution: Out-of-Path Distributed BridgingPerformance & Resource DividendsThe Modern Fix: VNA-Driven …
IntroductionFeature Progression: VCF 9.0 vs. VCF 9.1 EVPN ArchitectureControl Plane Mechanics: The Interface-less IP-VRF ProcessingPhysical Interoperability & Platform Deployment PrerequisitesD…
IntroductionVNA Stateful Services SeriesArchitectural Dependencies Checklist Supported NAT Capabilities Matrix in VCF 9.1 VNADeep Dive: Default Auto SNAT vs. User-Defined SNATThe Default SNAT Verif…
A UniFi restore that reports no errors, restarts cleanly, and lets you log in with your admin account, but somehow leaves you with an empty configuration, is a special kind of frustrating. That's the short version of what it took to move from a HostiFi-hosted controller to a local UniFi Express 7 (UX7). It should have been a cable swap and a restore. Instead it turned into a two-attempt debugging exercise, followed by a workaround involving a throwaway Docker controller and some direct MongoDB open-heart surgery.
Proceed at your own risk! (... it's worth it)
Manage and monitor Traefik routes, middlewares, services, and providers through a clean web UI.
This is a follow up to Private Networking on Hetzner Cloud with Tailscale
This is a follow up to Why I Built My Own Kubernetes Cluster
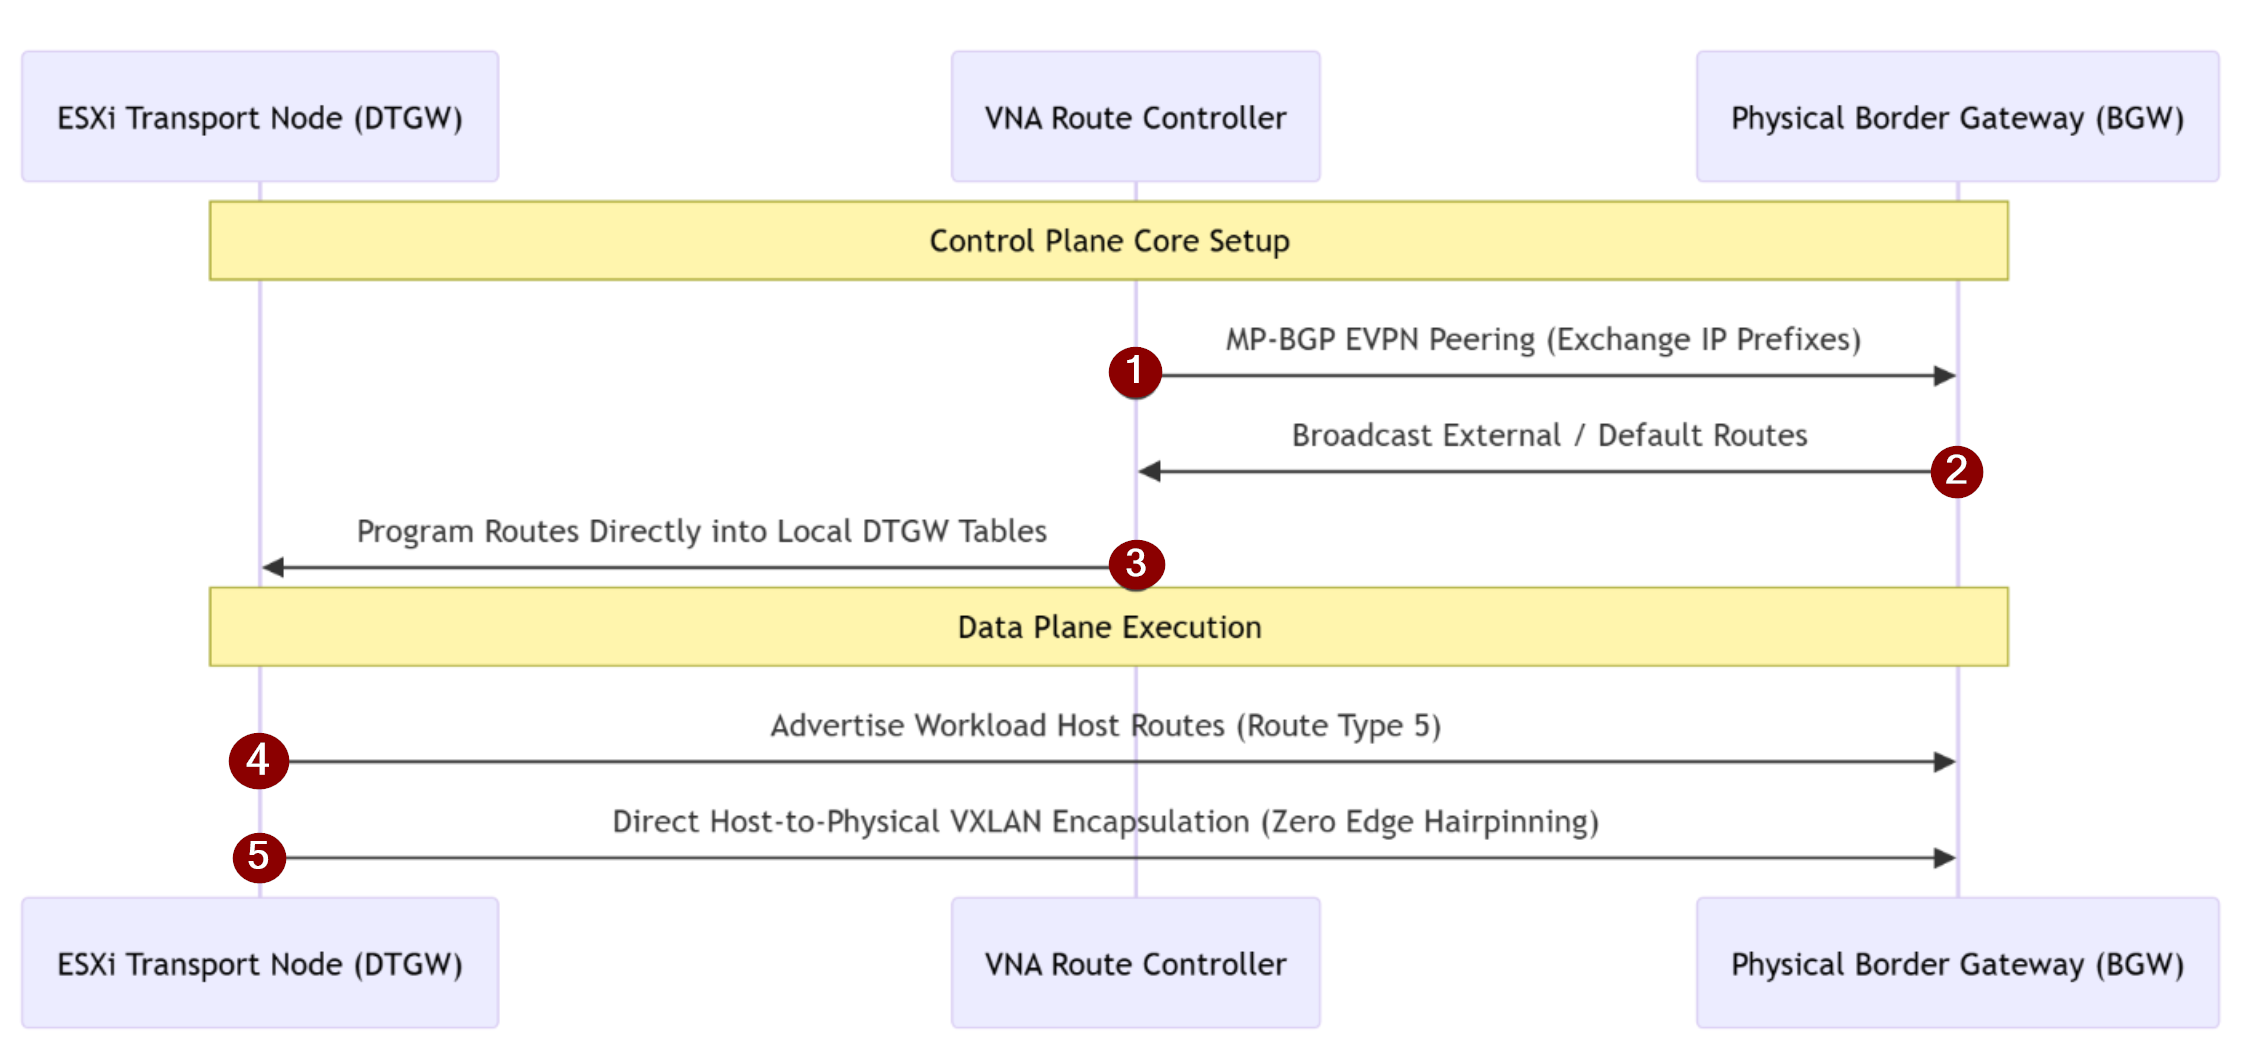
In this article, I’ll take another look at VPCs and the VNA. This time, the VNA acts as the route controller, and the VPC is connected via VXLAN/EVPN using Type 5 routes.
No self-signing headaches, no TLS erros.
Netbird does it all: tunnels, proxying, firewall, if you want it - netbird delivers.
https://github.com/netbirdio/netbird
🌊 see your network breathe. Contribute to programmersd21/flow development by creating an account on GitHub.
Global DNS propagation checker TUI — watch a DNS record propagate across 34 public resolvers worldwide, on a world map in your terminal - 514-labs/dnsglobe
I have several Cisco network devices in my homelab. In this post will showcase a first-glance on how to access such via Boundary, a PAM solution from HashiCorp.
Replace long-lived AI API keys with groups from your identity provider. Verified identity flows into LiteLLM Cloudflare, and other gateways or providers for audit, cost attribution, and policy enforcement.
DNSimple is a developer friendly, rich API DNS system!
Start your 30 day FREE trial here: https://dnsimple.com/api?utm_source=d...
---
Self-contained PXE and HTTP boot server. Single binary. Zero config. 50+ distros out of the box.
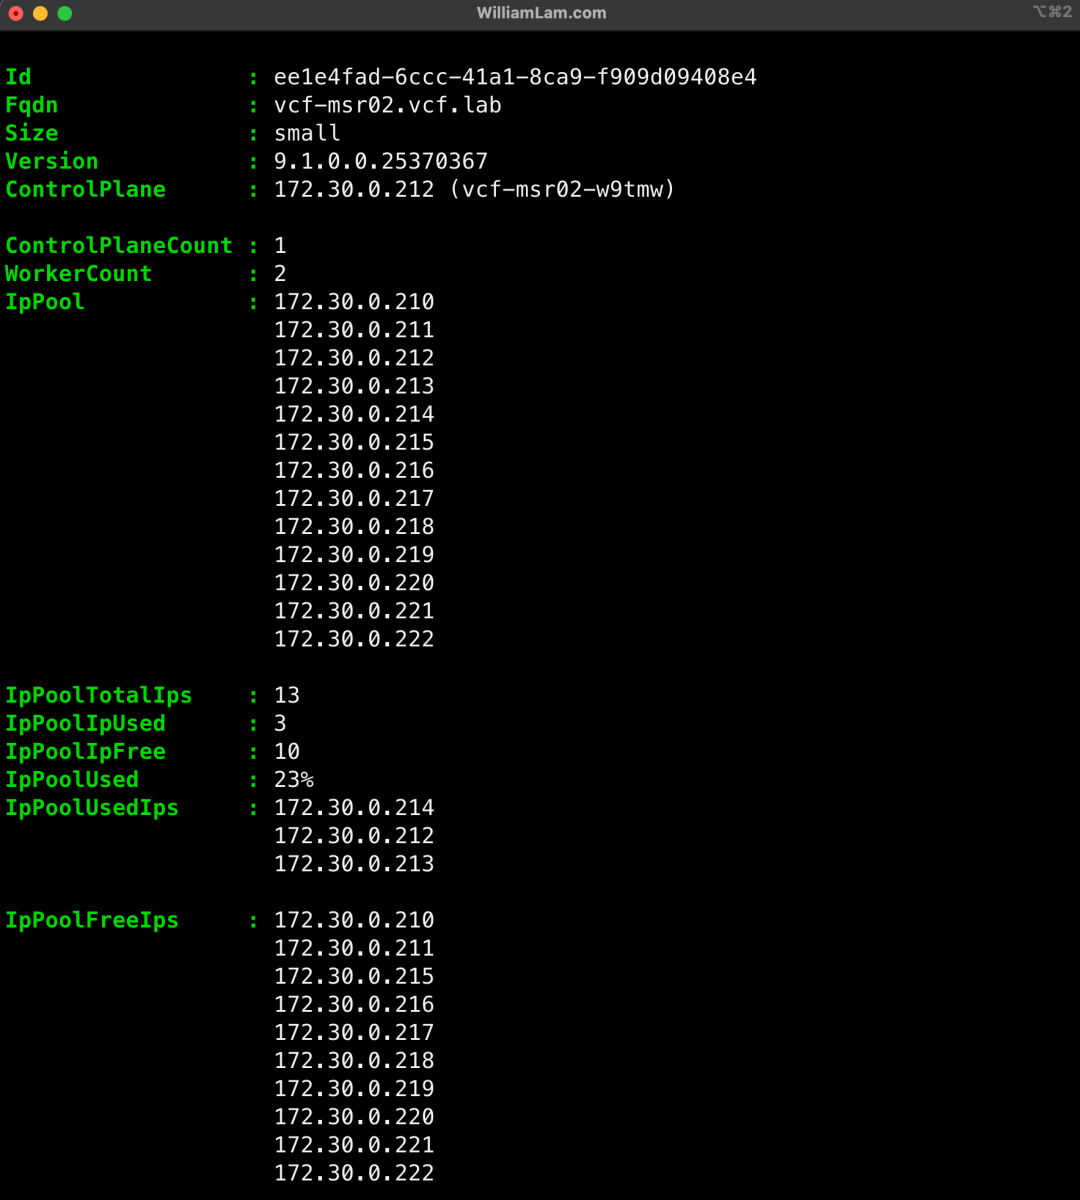
As part of deploying the new VCF Management Services (VCFMS) component, a pool of IP addresses is provided to support the automatic deployment and scale-out of additional worker nodes for Day-N ser…
Minimal container images often ship without curl, wget, or any HTTP client at all. Bash can open a TCP socket through /dev/tcp, which is enough to write a tiny HTTP/1.1 request by hand for quick checks.
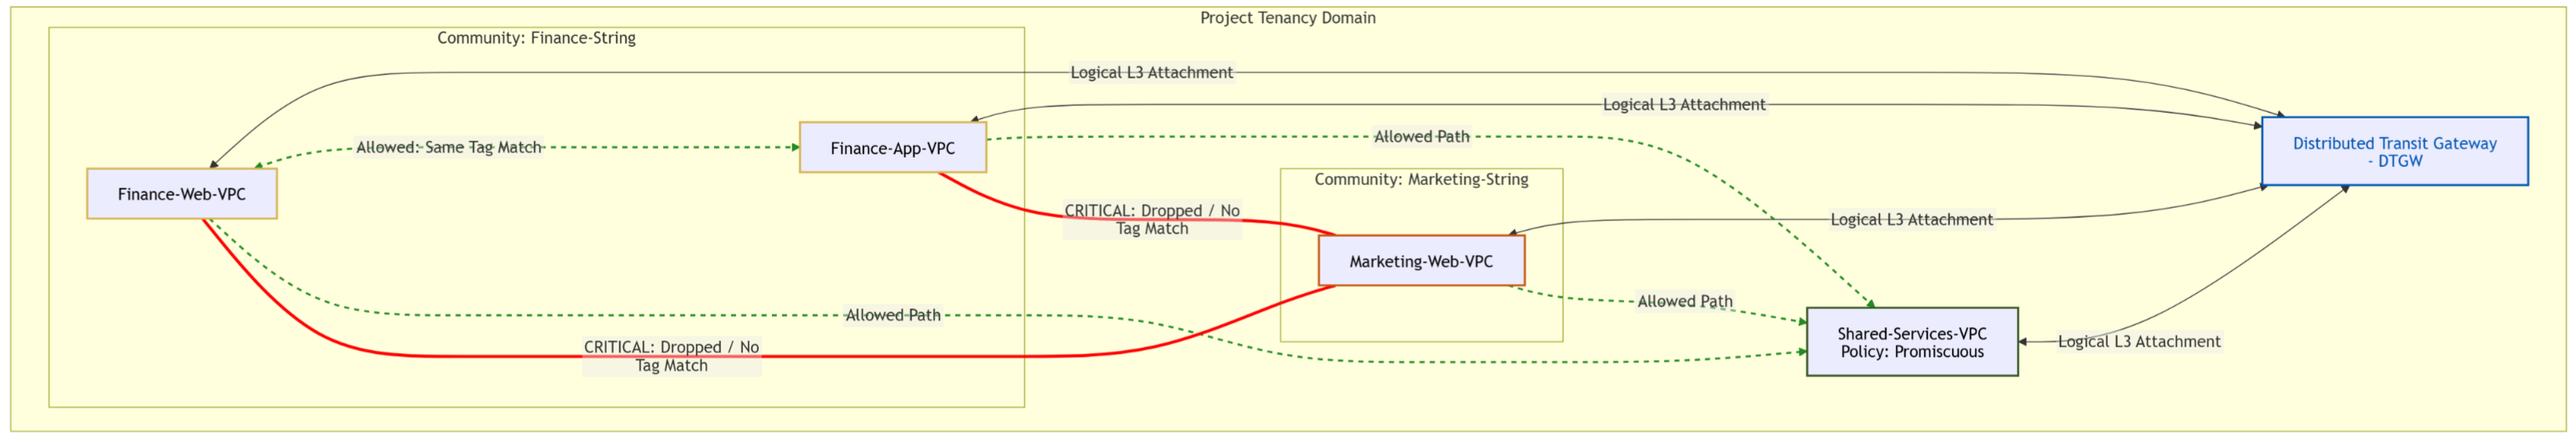
IntroductionArchitectural Shift: VCF 9.0 vs. VCF 9.1The Four Connectivity PosturesA. Community Policy (Group-Based Segmentation)B. Promiscuous Policy (Shared Services Baseline)C. Isolated Policy (S…
Here's a description of how to configure TGWEVPN/VXLAN in the new VCF 9.1 version. I encourage you to read on. Implementing this isn't difficult.
A post dedicated to configuring NSX-t EVPN inline mode in NSX-T. The MP-BGP session with Juniper vMX. Step-by-step setup description.
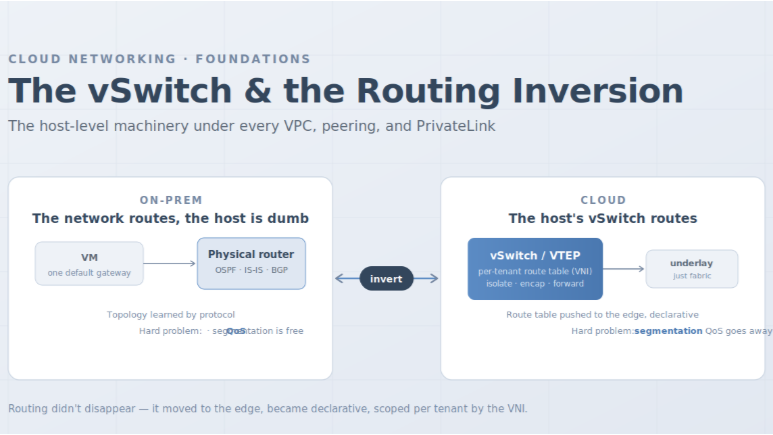
CLOUD NETWORKING SERIES · FOUNDATIONS Before VPCs, peering, or PrivateLink make sense, you have to see what happens inside a single physical server. Every cloud-networking concept is built on a few pieces living on one host — the guest VM, its network interface (ENI), the virtual switch, and the tun
Open-source MITM proxy to intercept, inspect, and mock network traffic. - sauravrao637/oproxy
nbor, flo, viaduct, wiremap. Four CLI tools for network troubleshooting, discovery, and monitoring. Built from frustrations, open-sourced, and available on GitHub and Homebrew.
VCF 9.1 adds VKS multi-network support allowing users to separate management, storage, and data traffic per node.
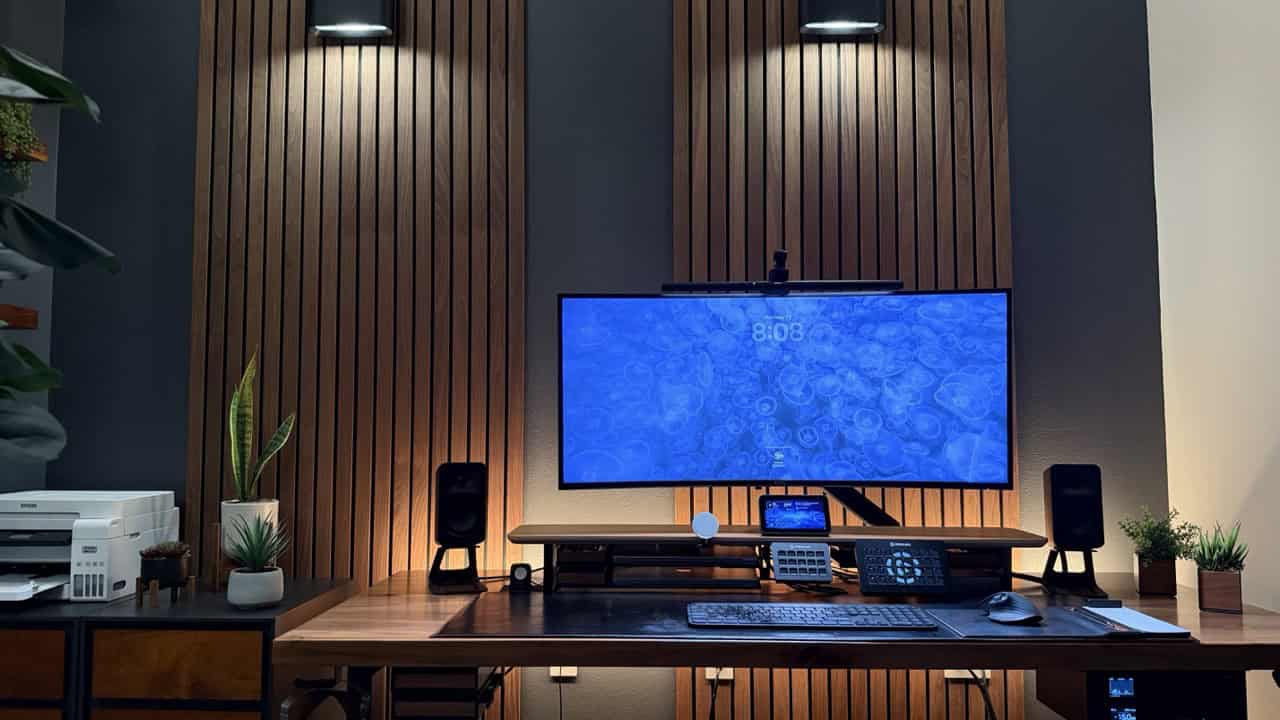
Do you want some inspiration for your ultimate home office desk setup? How about smart lighting, smart blinds and more? Look no further than my 2026 guide!
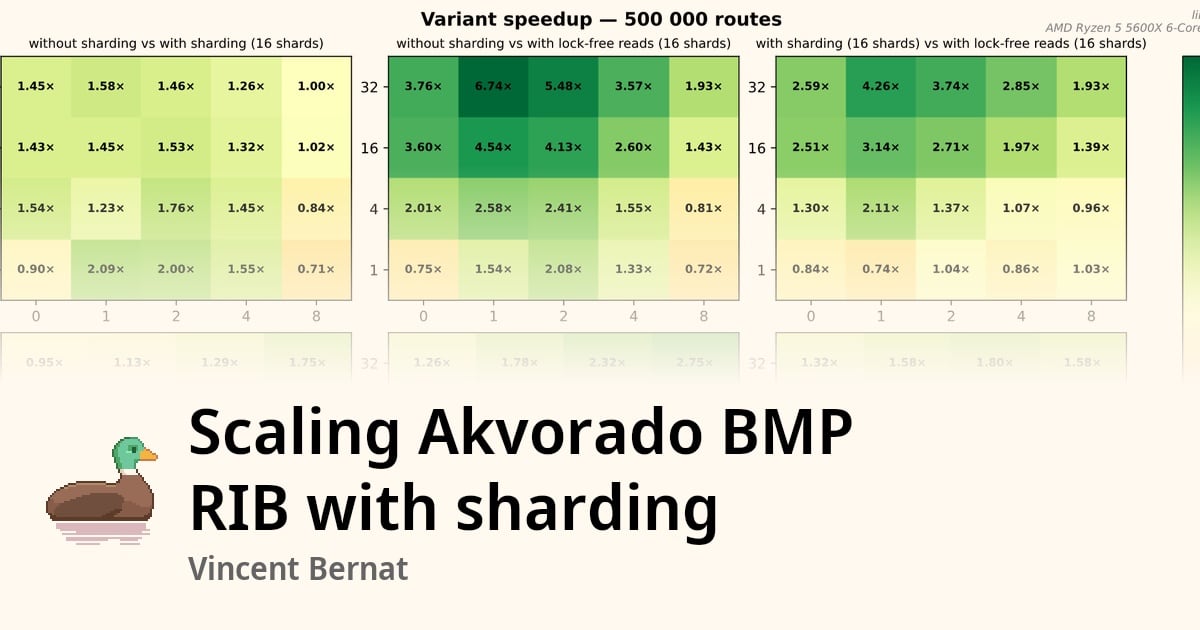
How Akvorado's BMP component scales to tens of millions of routes thanks to RIB sharding and lock-free reads.
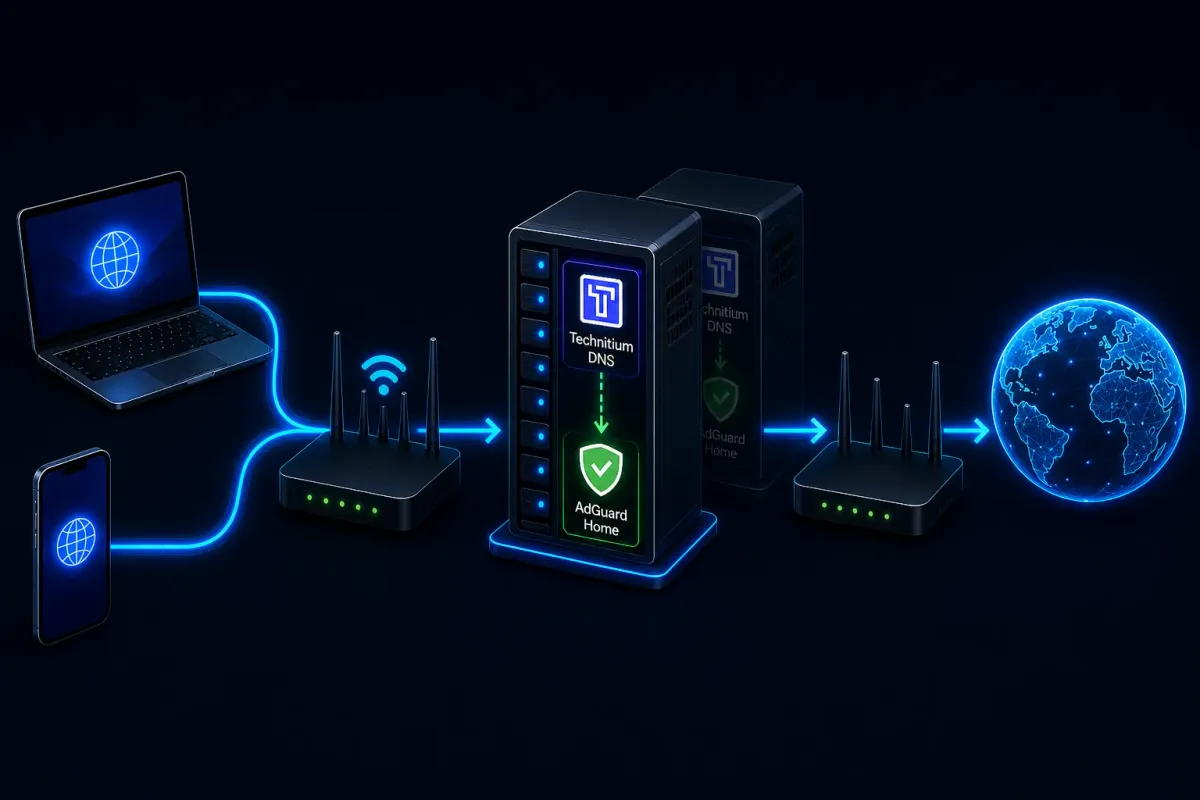
Un setup DNS sans redondance ni zone locale, c'est un SPOF qui s'ignore. Découvrez comment refondre son infrastructure DNS en haute disponibilité avec Technitium, AdGuard Home et Proxmox HA.
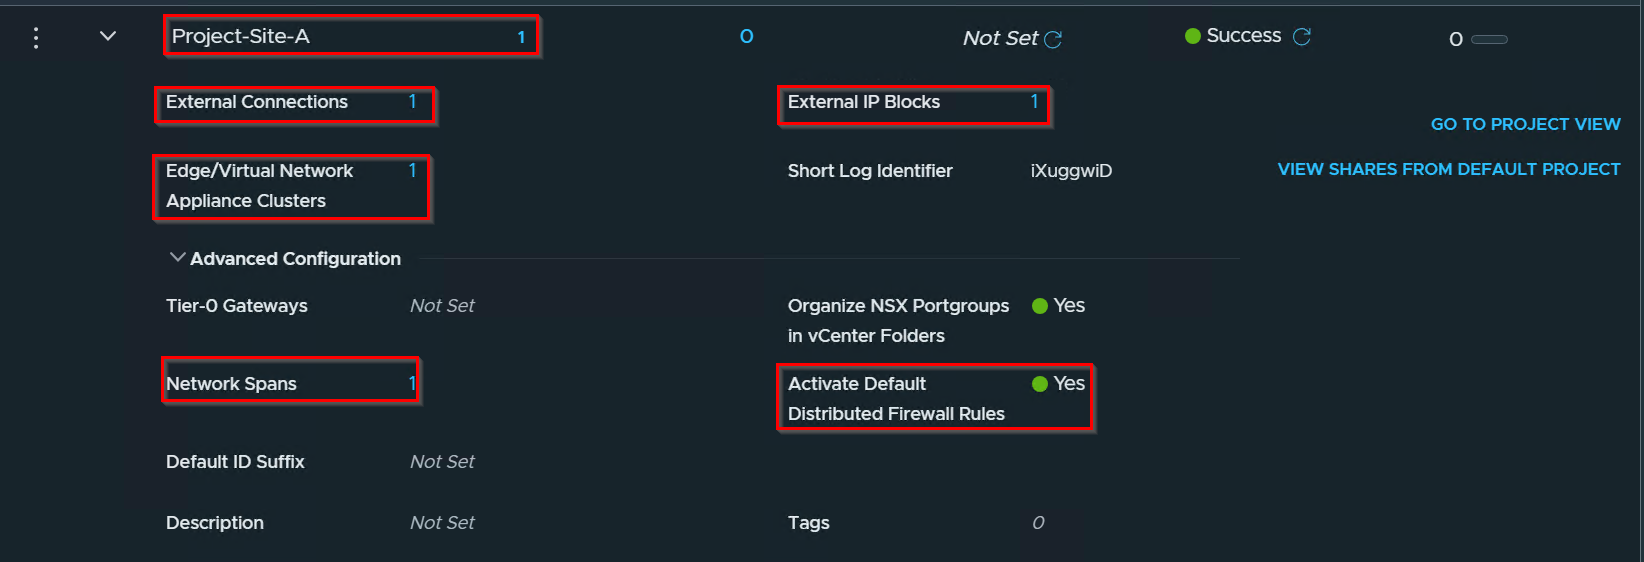
In this follow-up article, I take a deeper look at the VNA architecture in VCF 9.1, including placement, relocation, scaling, and network spans.
Headscale gives you CONTROL over your mesh network!
https://headscale.net
This video highlights the key features introduced in Proxmox Virtual Environment 9.2. The release debuts a Dynamic Load Balancer for real-time cluster resource scheduling and automated high-availability (HA) migrations. Networking receives an enterprise overhaul with native WireGuard and BGP fabrics for secure cross-site inter-node connections, alongside granular Route Maps and Prefix Lists for advanced BGP/EVPN route filtering.
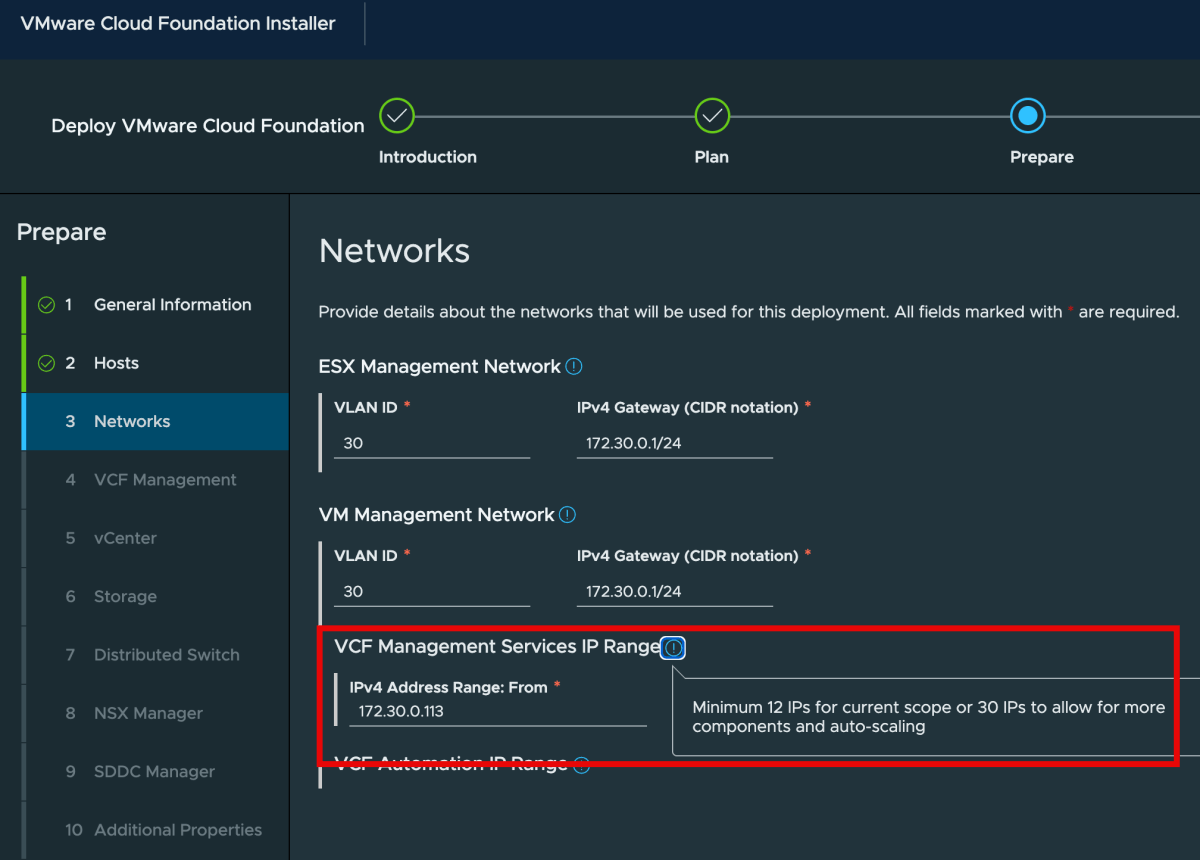
One of the new components introduced in VMware vSphere Foundation (VVF) and VMware Cloud Foundation (VCF) 9.1 is the VCF Management Services (VCFMS), which provides a centralized system for unifyin…
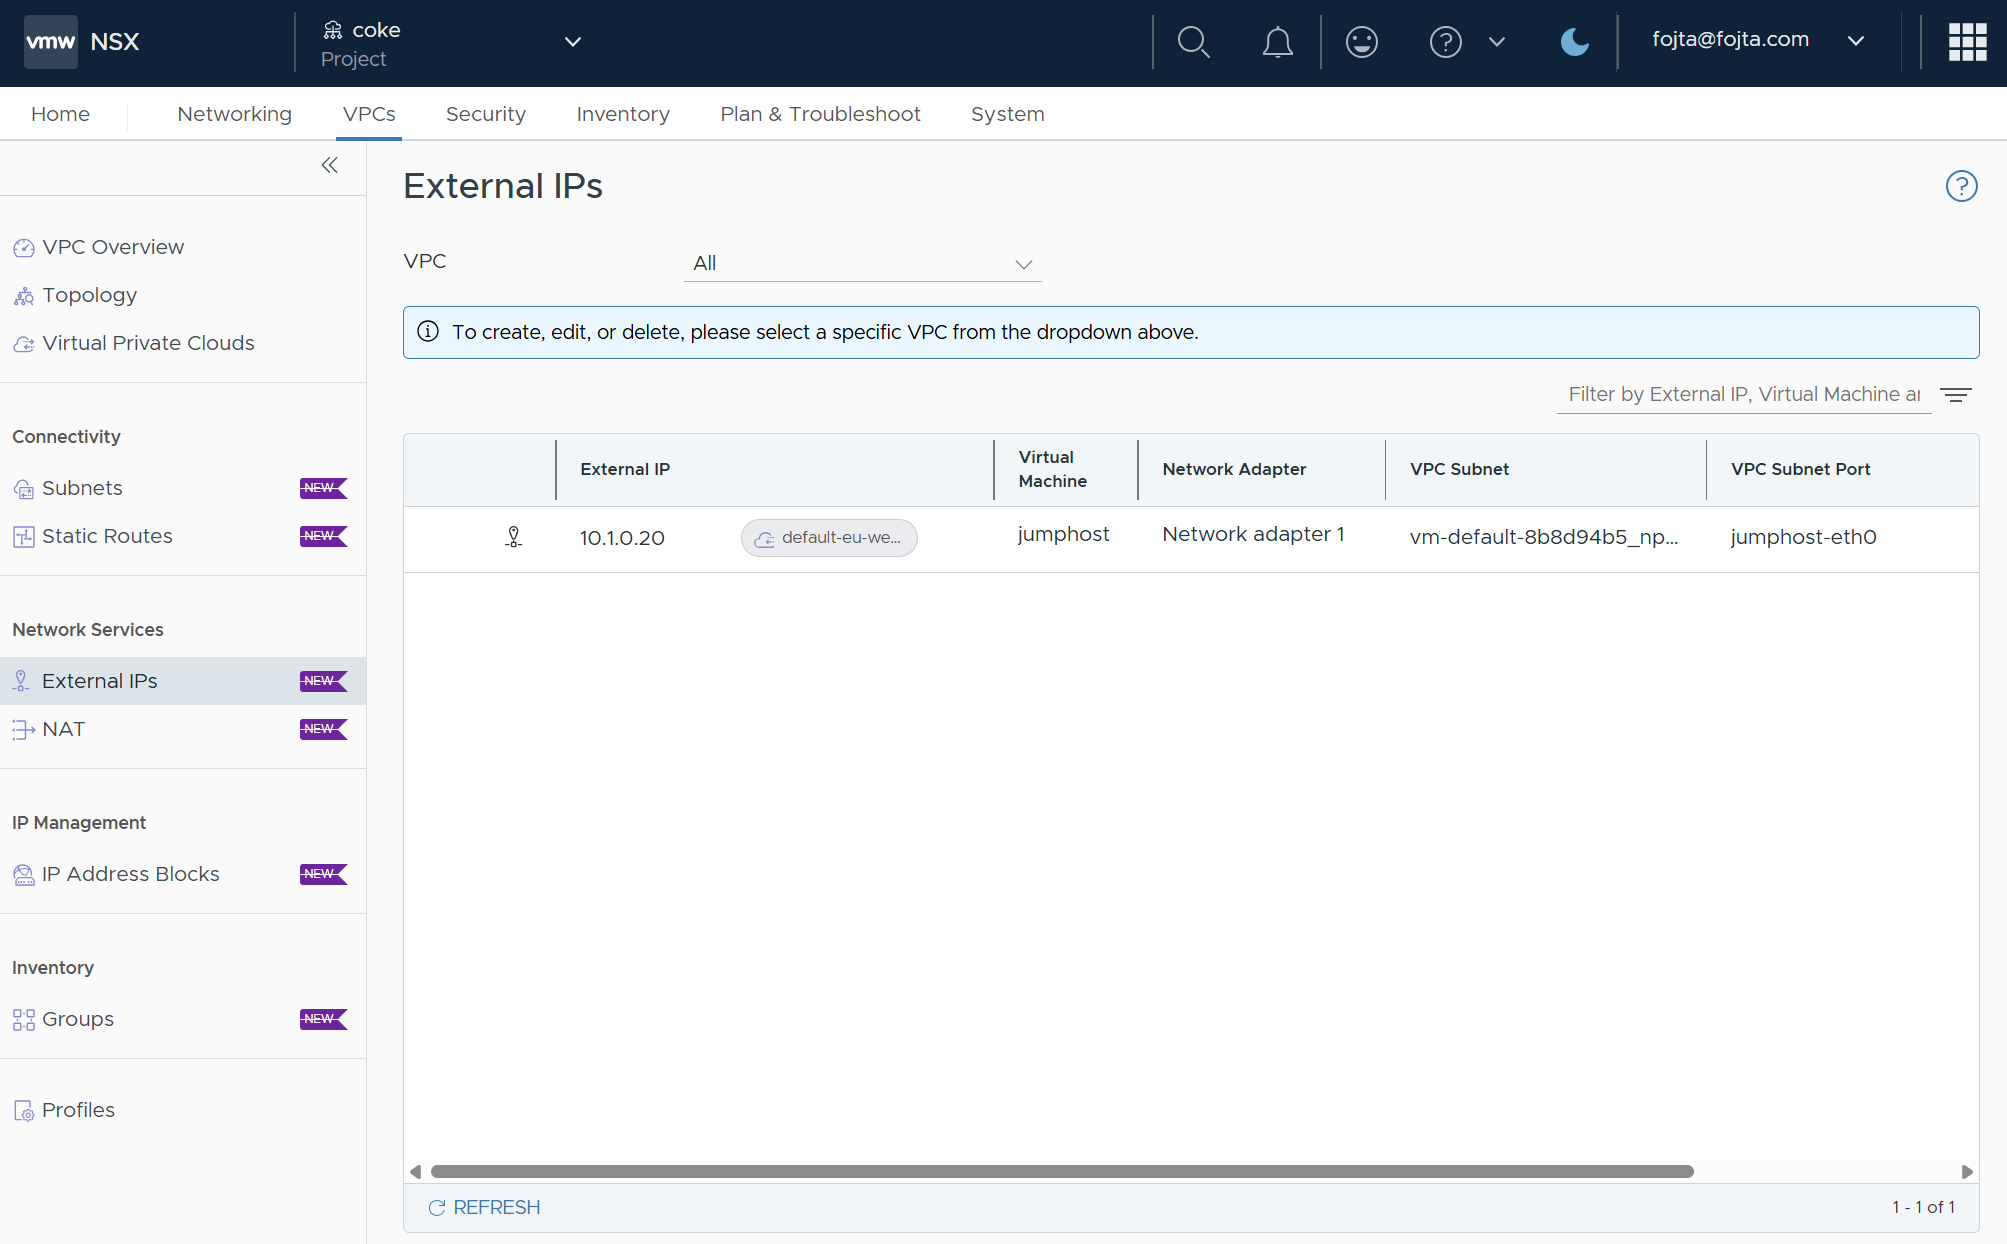
In VCF Automation 9.1 we can assign External IP to a particular VM that is connected to private or transit subnets and access it directly via that IP. This is similar to assigning public floating I…
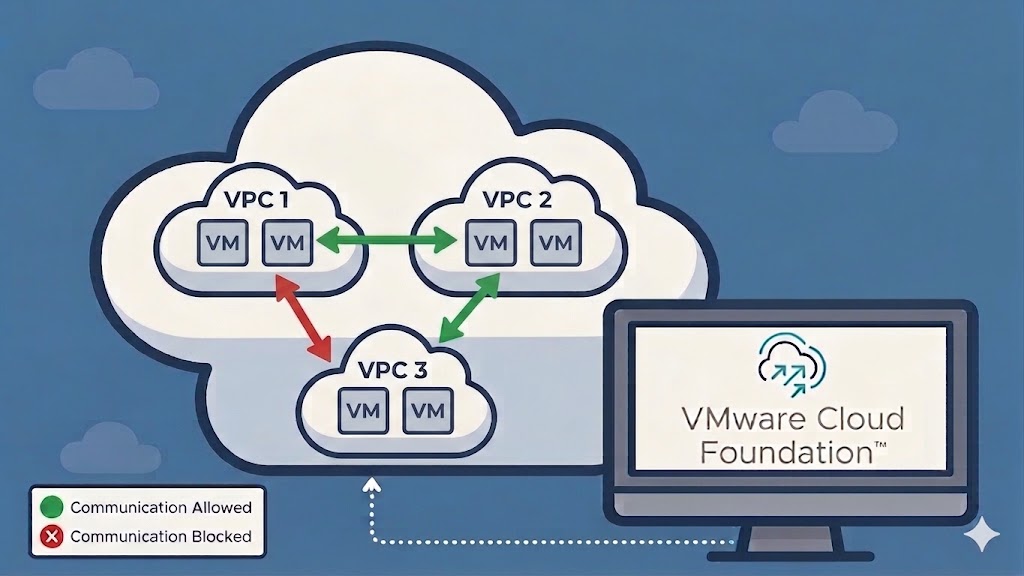
Related VCF Networking 9.1 Posts: VMware Cloud Foundation (VCF) provides a robust suite of self-service networking capabilities (as covered in our previous post: [Link to: VCF 9.1 – Network Services]) In this blog, we zoom in on a powerful new feature introduced in VCF 9.1: Connectivity Policy for Virtual Private Clouds (VPCs). Taking Control of … Continued
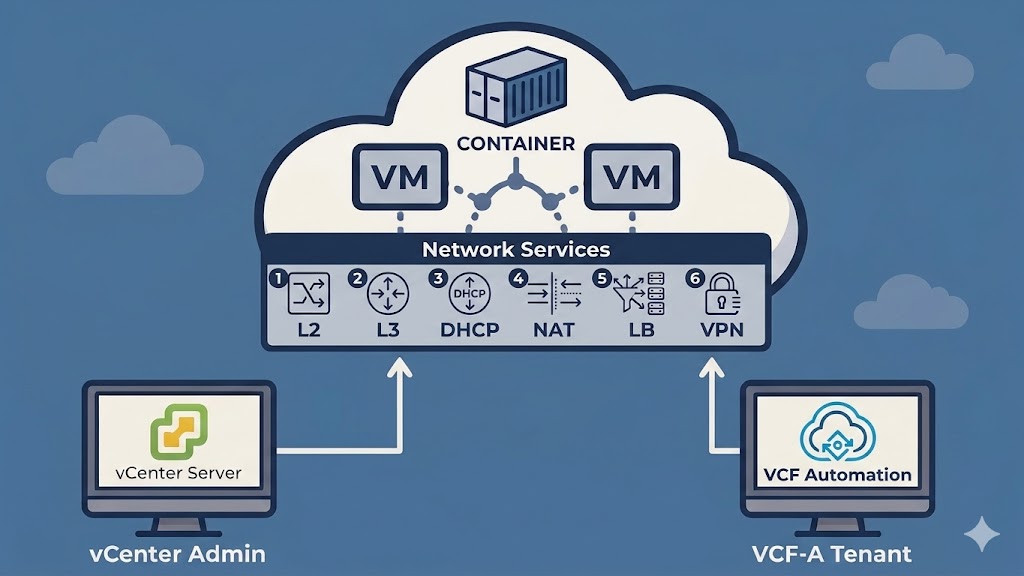
Related VCF Networking 9.1 Posts: VMware Cloud Foundation (VCF) delivers the compute, storage, and networking services required to power modern cloud environments. In this blog, we focus specifically on the network services available within VCF 9.1 Virtual Private Clouds (VPCs). Note: For a refresh into the fundamentals of VCF VPCs, check out our previous posts:Self-service … Continued
NetBird v0.71 introduces dual-stack overlay networking. Every peer can now receive both an IPv4 and an IPv6 address from a per-account prefix, with full DNS, ACL, exit-node, and network-route support out of the box.
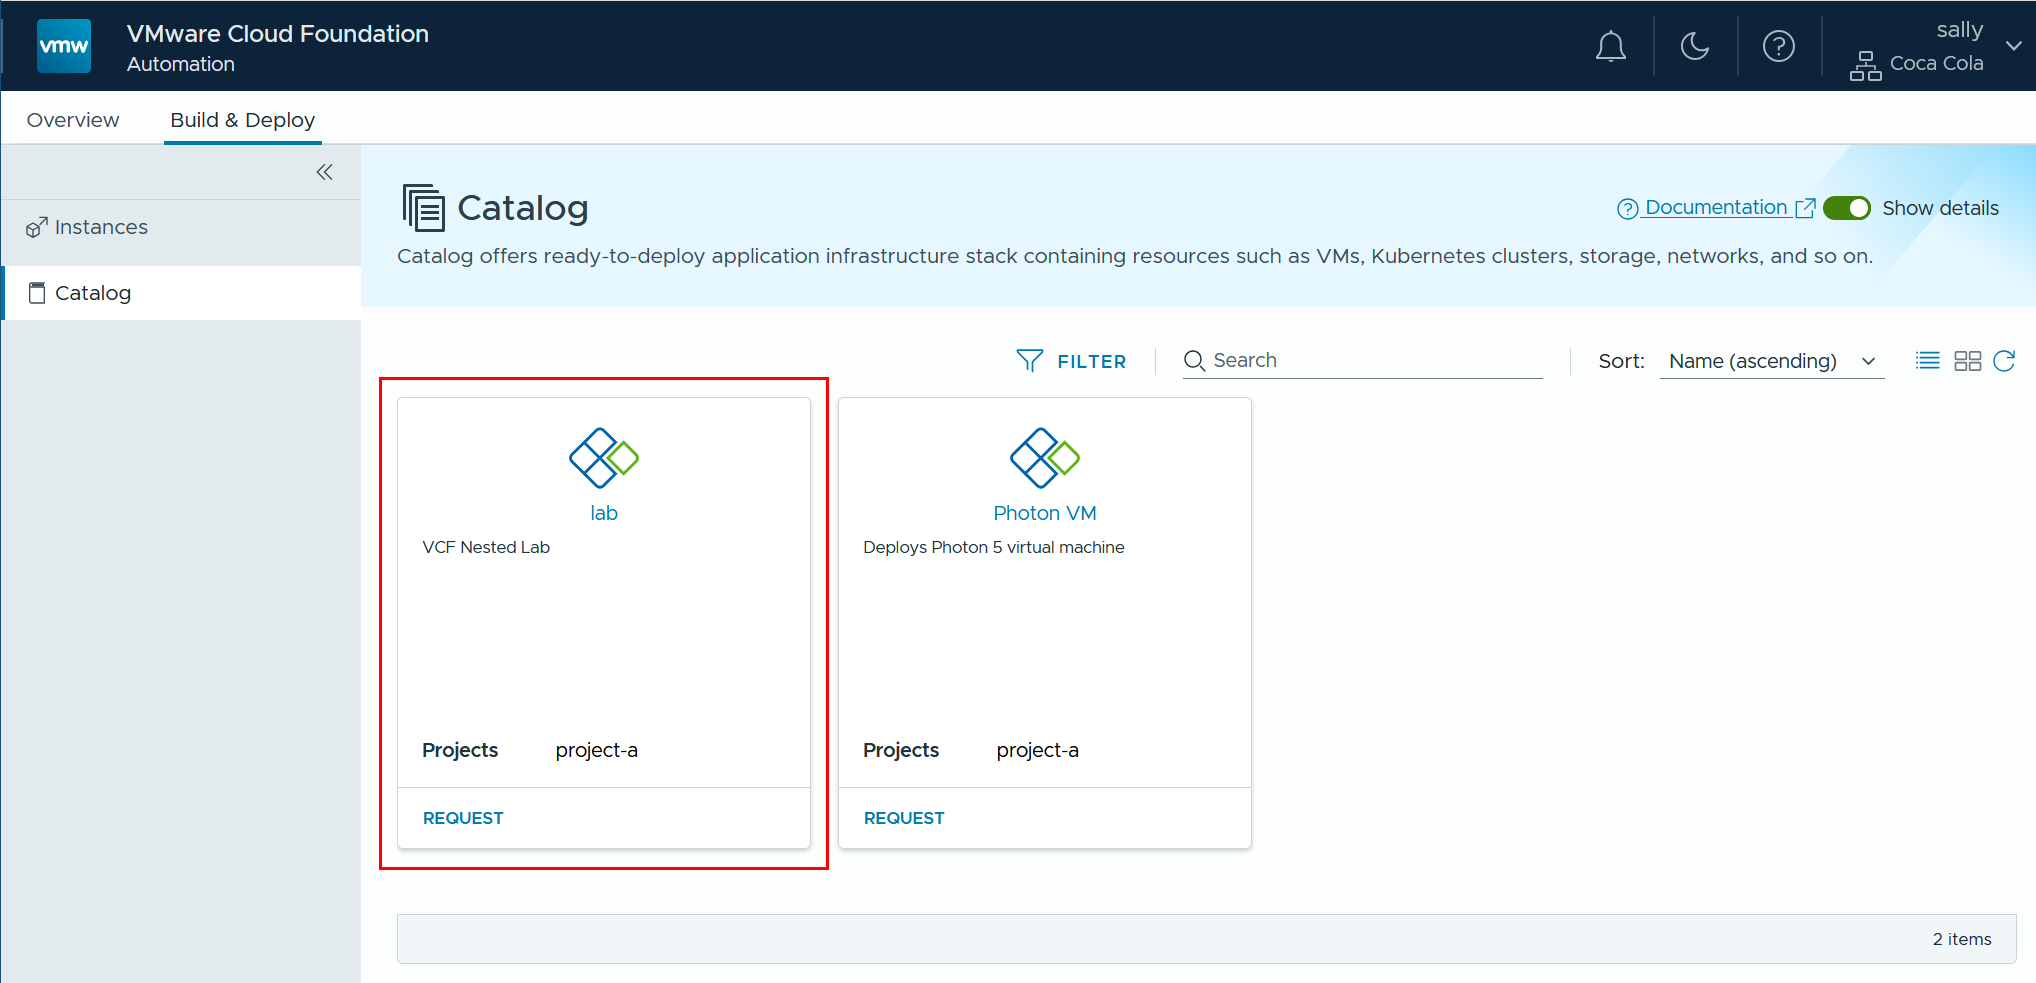
About two years ago I wrote blog post on how to create self-contained lab in VMware Cloud Director cloud environment with equivalent functionality to physical lab that can be rapidly deployed with …
In this new blog post, I will describe the benefits of virtual network appliances and how to use them.
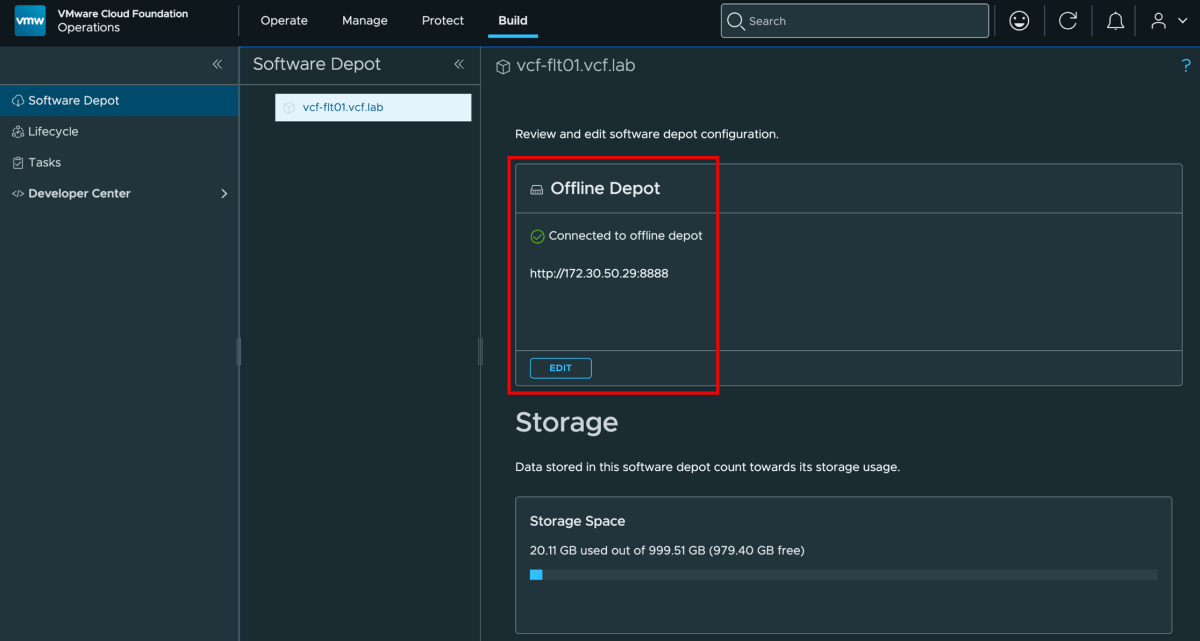
VMware vSphere Foundation (VVF) and VMware Cloud Foundation (VCF) 9.0 introduced the concept of a unified VCF Software Depot, which can connect to either Broadcom’s online repository or an offline …
Diskless Linux Boot
In this blog post, I’ll discuss the new VPC connectivity Policies and how they can be used to enhance security.
tsnet let Cleric embed Tailscale into their AI SRE, replacing VPNs and VPC peering with a programmable, zero-config overlay network.
Self-hosted homelab infrastructure visualizer — interactive network diagram with live status monitoring - Pouzor/homelable
In this blog post, I’ll explain how Nutanix Flow 7 works, how to set up and use virtual networking, take a look at VPCs, and highlight the differences from NSX.
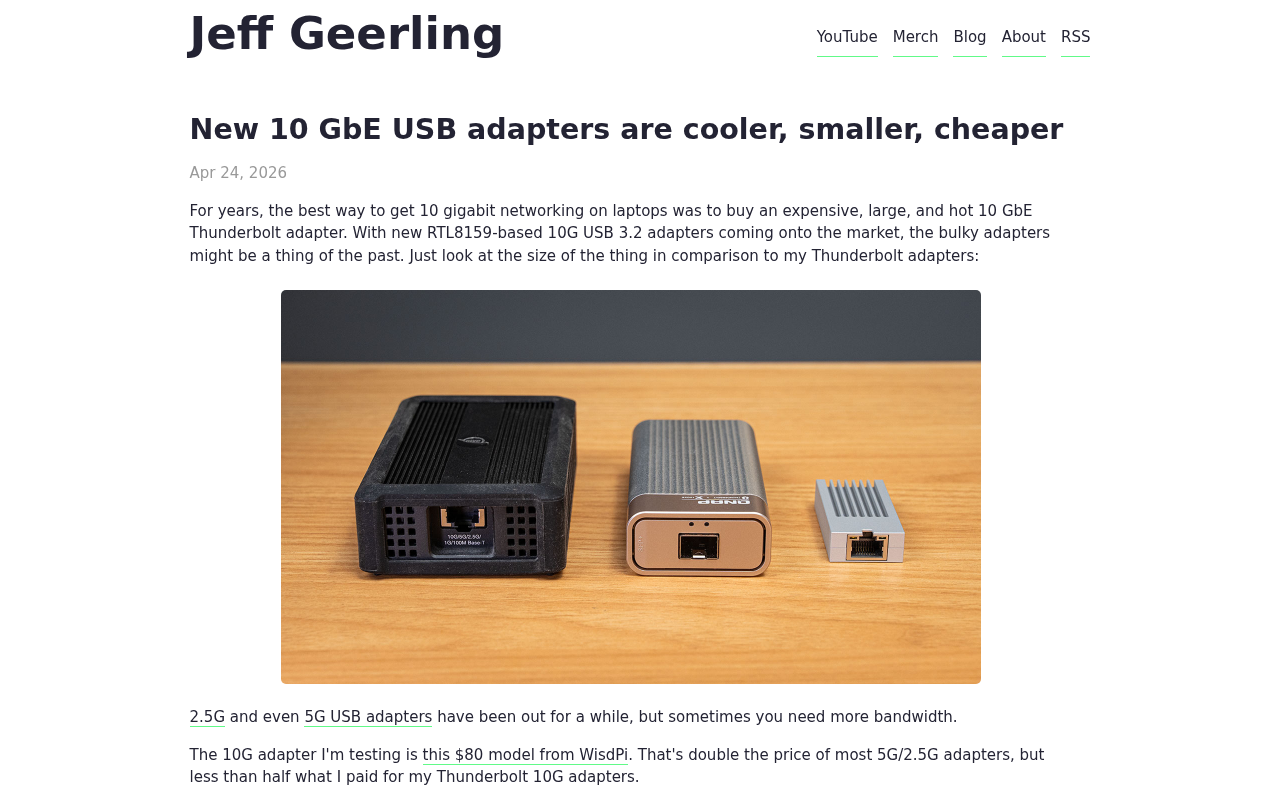
For years, the best way to get 10 gigabit networking on laptops was to buy an expensive, large, and hot 10 GbE Thunderbolt adapter. With new RTL8159-based 10G USB 3.2 adapters coming onto the market, the bulky adapters might be a thing of the past. Just look at the size of the thing in comparison to my Thunderbolt adapters:
2.5G and even 5G USB adapters have been out for a while, but sometimes you need more bandwidth.
🌐 Elegant UniFi network management CLI & TUI - for humans and agents - hyperb1iss/unifly
Agents used to be a thing you talked to synchronously. Now they’re a thing that runs in the background while you work. When you make that change, the …

Previous message (by thread):WireGuard Windows 0.6.1 - Timeline of issues (tunnels lost & import still broken)Messages sorted by:[ date ][ thread ][ subject ][ author ]Hey again,
A practical field-focused walkthrough of building an All Apps Organization in VMware Cloud Foundation 9 using VCF Automation, with emphasis on regions, quotas, networking design, and why manual setup matters over quick start.
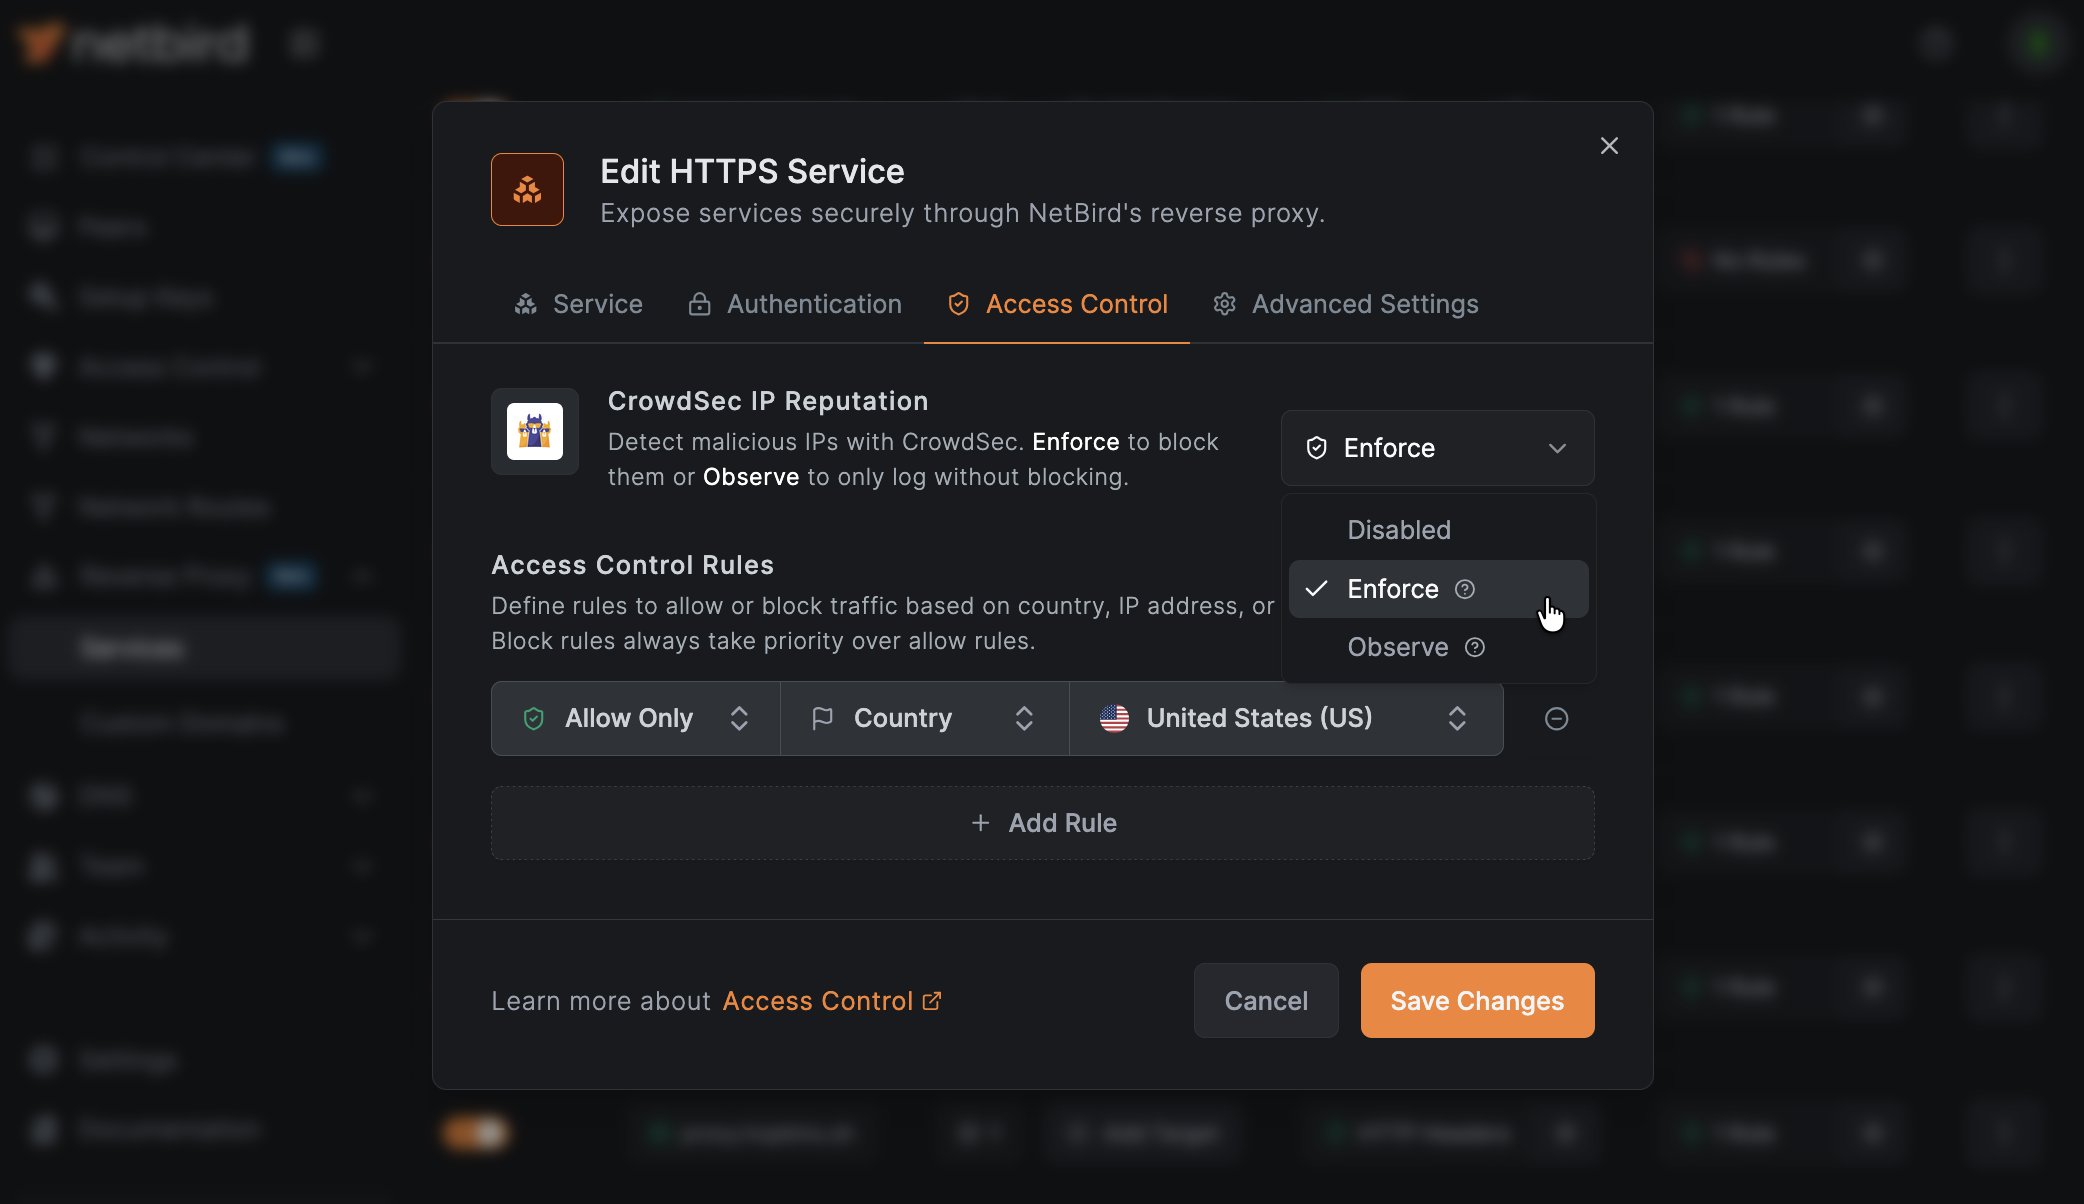
NetBird v0.69 is out. Top of the list for self-hosters:
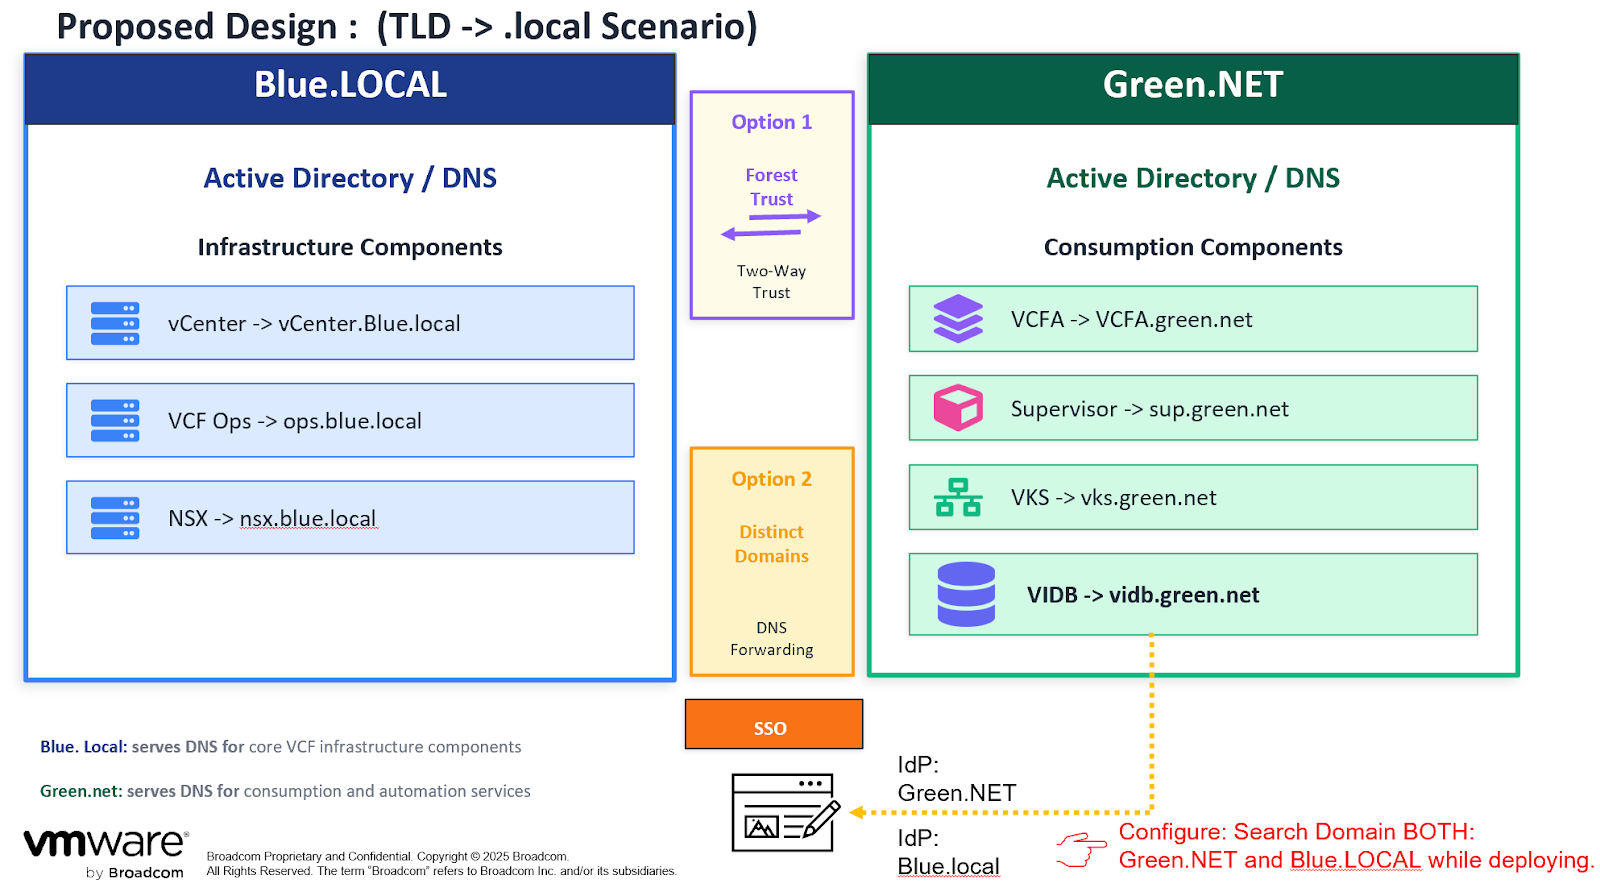
In the ever-evolving landscape of private cloud, technical debt often hides in the most fundamental places, like your DNS naming convention. For many years, .local was the go-to Top-Level Domain (TLD) for internal Active Directory environments. However, as per RFC 6762, .local is now officially reserved for Multicast DNS (mDNS) and is no longer recommended … Continued
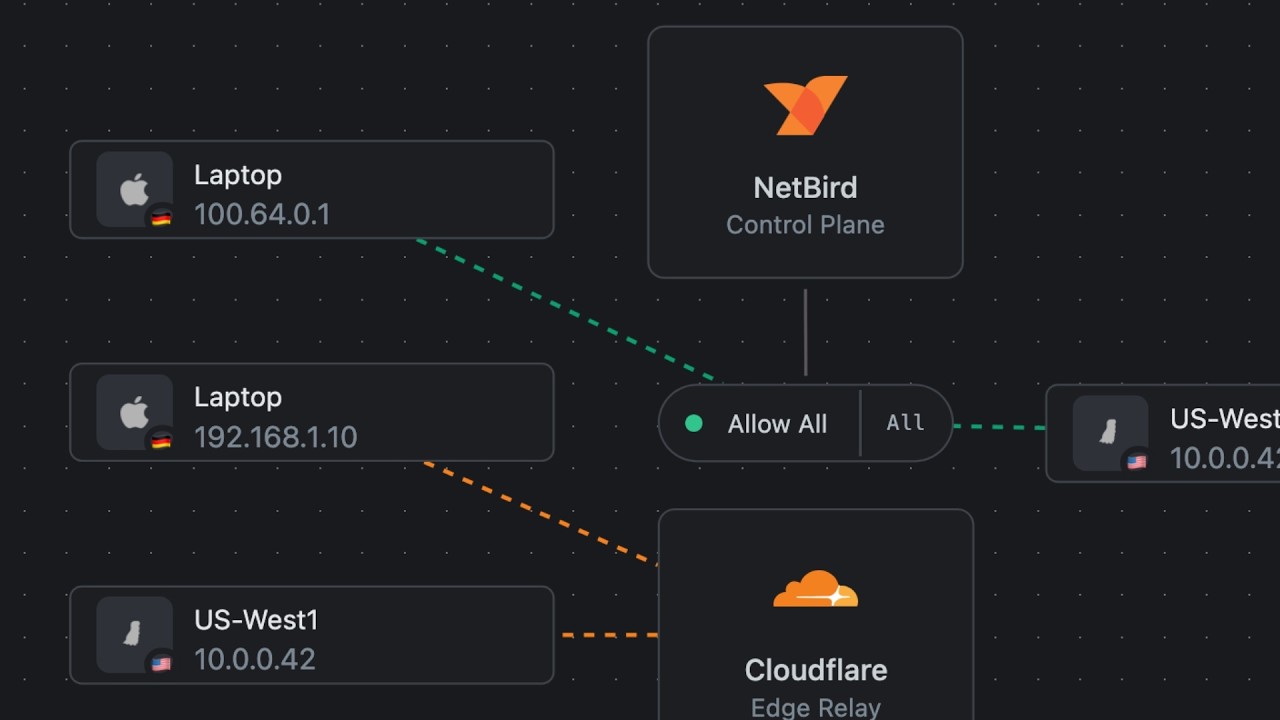
We benchmarked Cloudflare Mesh, NetBird, and Tailscale across AWS, GCP, Hetzner, and residential networks in Europe. Here's what peer-to-peer vs edge routing actually looks like in practice.
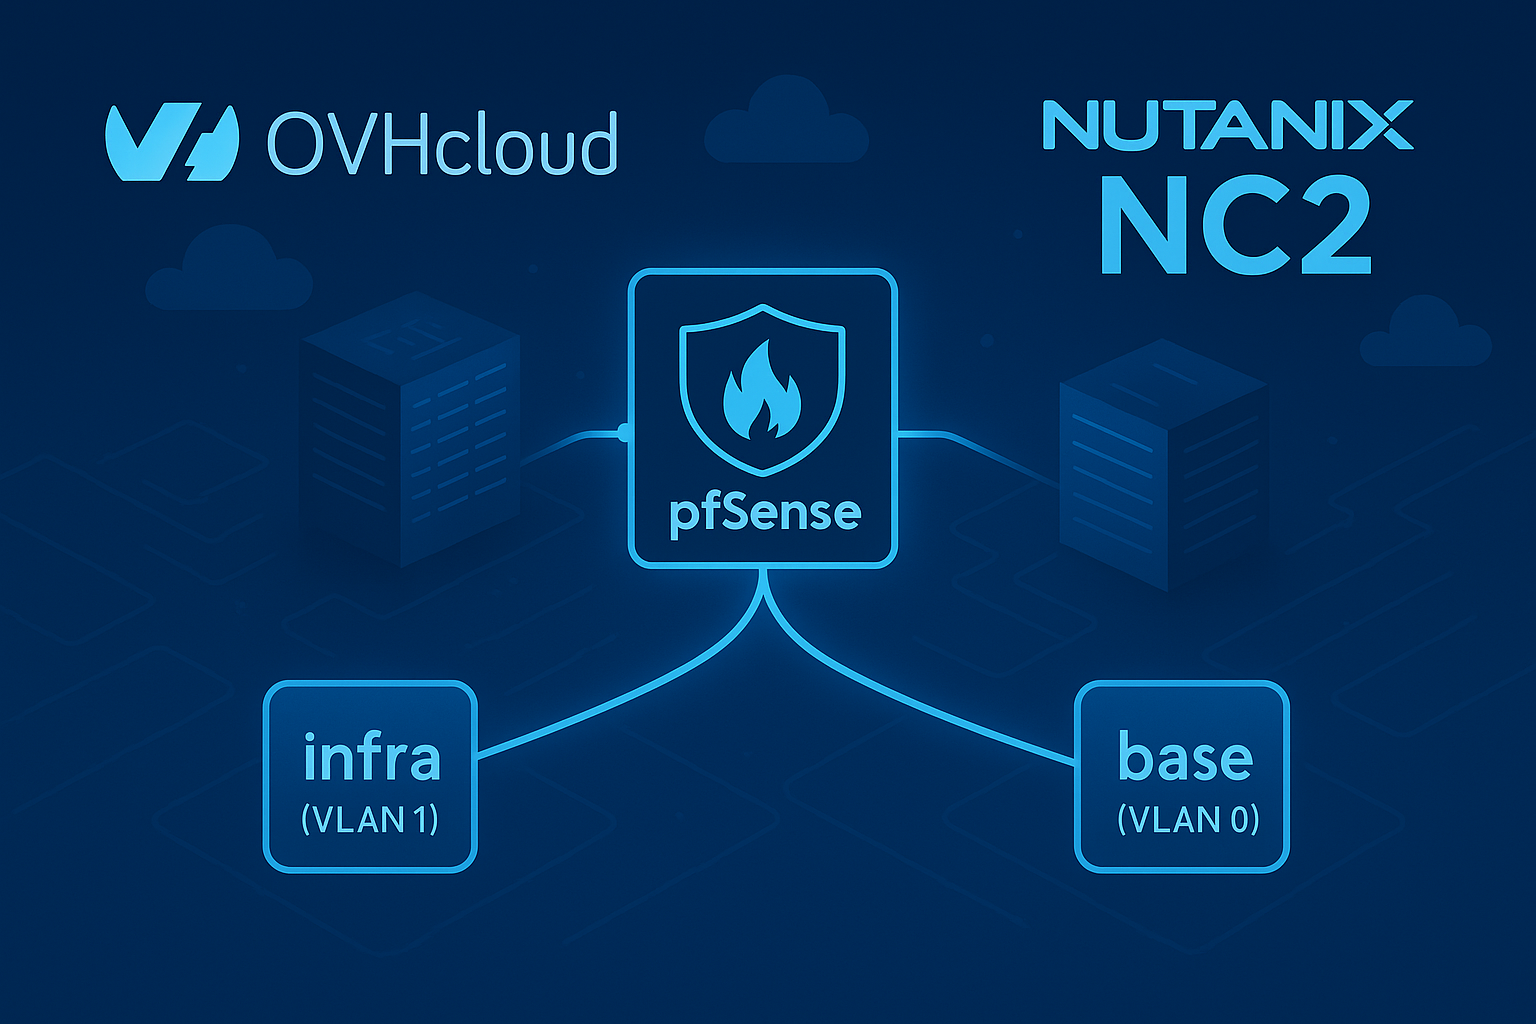
A complete guide to replacing the default OVHcloud gateway with a pfSense firewall on Nutanix NC2.
An interactive CLI tool that replaces whois with a tabbed TUI for WHOIS, DNS, mail, SSL/TLS, HTTP headers, and tech stack detection.
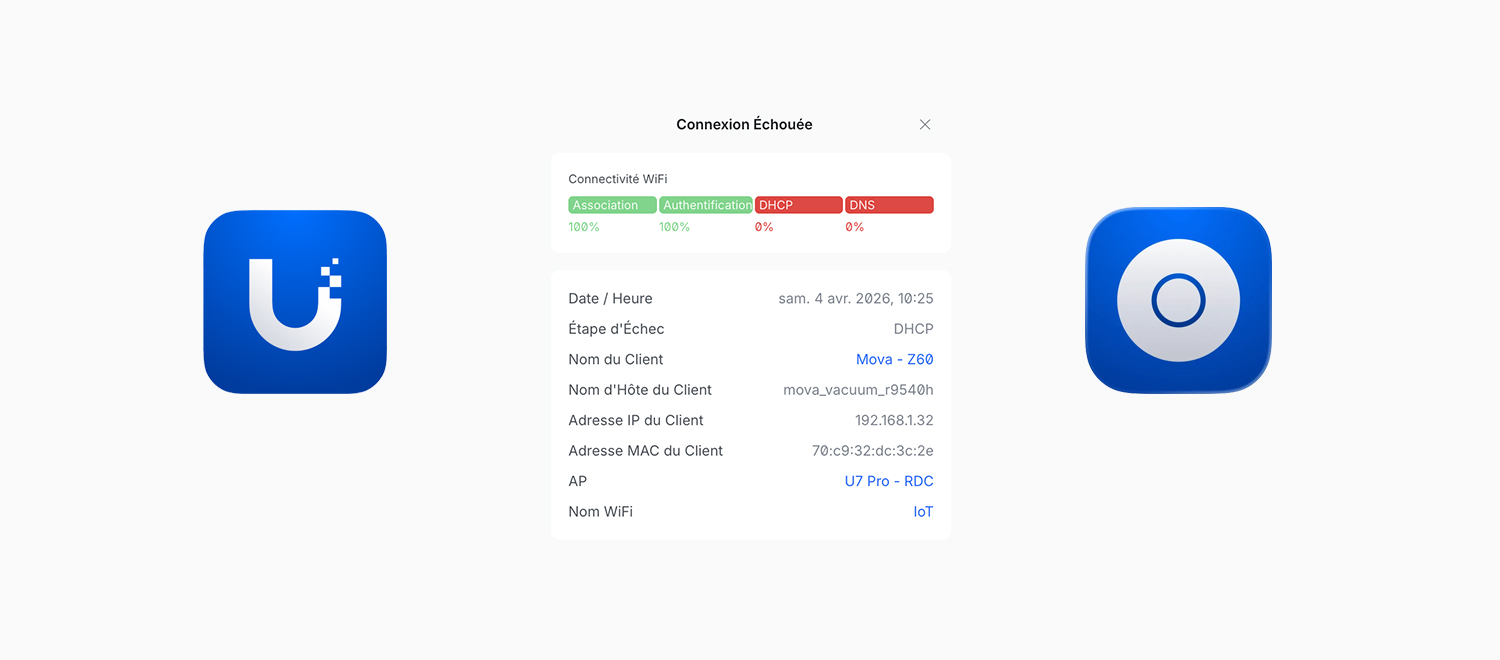
Délai DHCP dépassé sur UniFi : comment j'ai trouvé le coupable (un conteneur LXC Home Assistant) avec l'aide du support et de Claude Cowork.
Learn how to deploy a 2-host VCF Edge 9.0 site with brownfield import. Achieve HA while bringing existing infrastructure under VCF management.
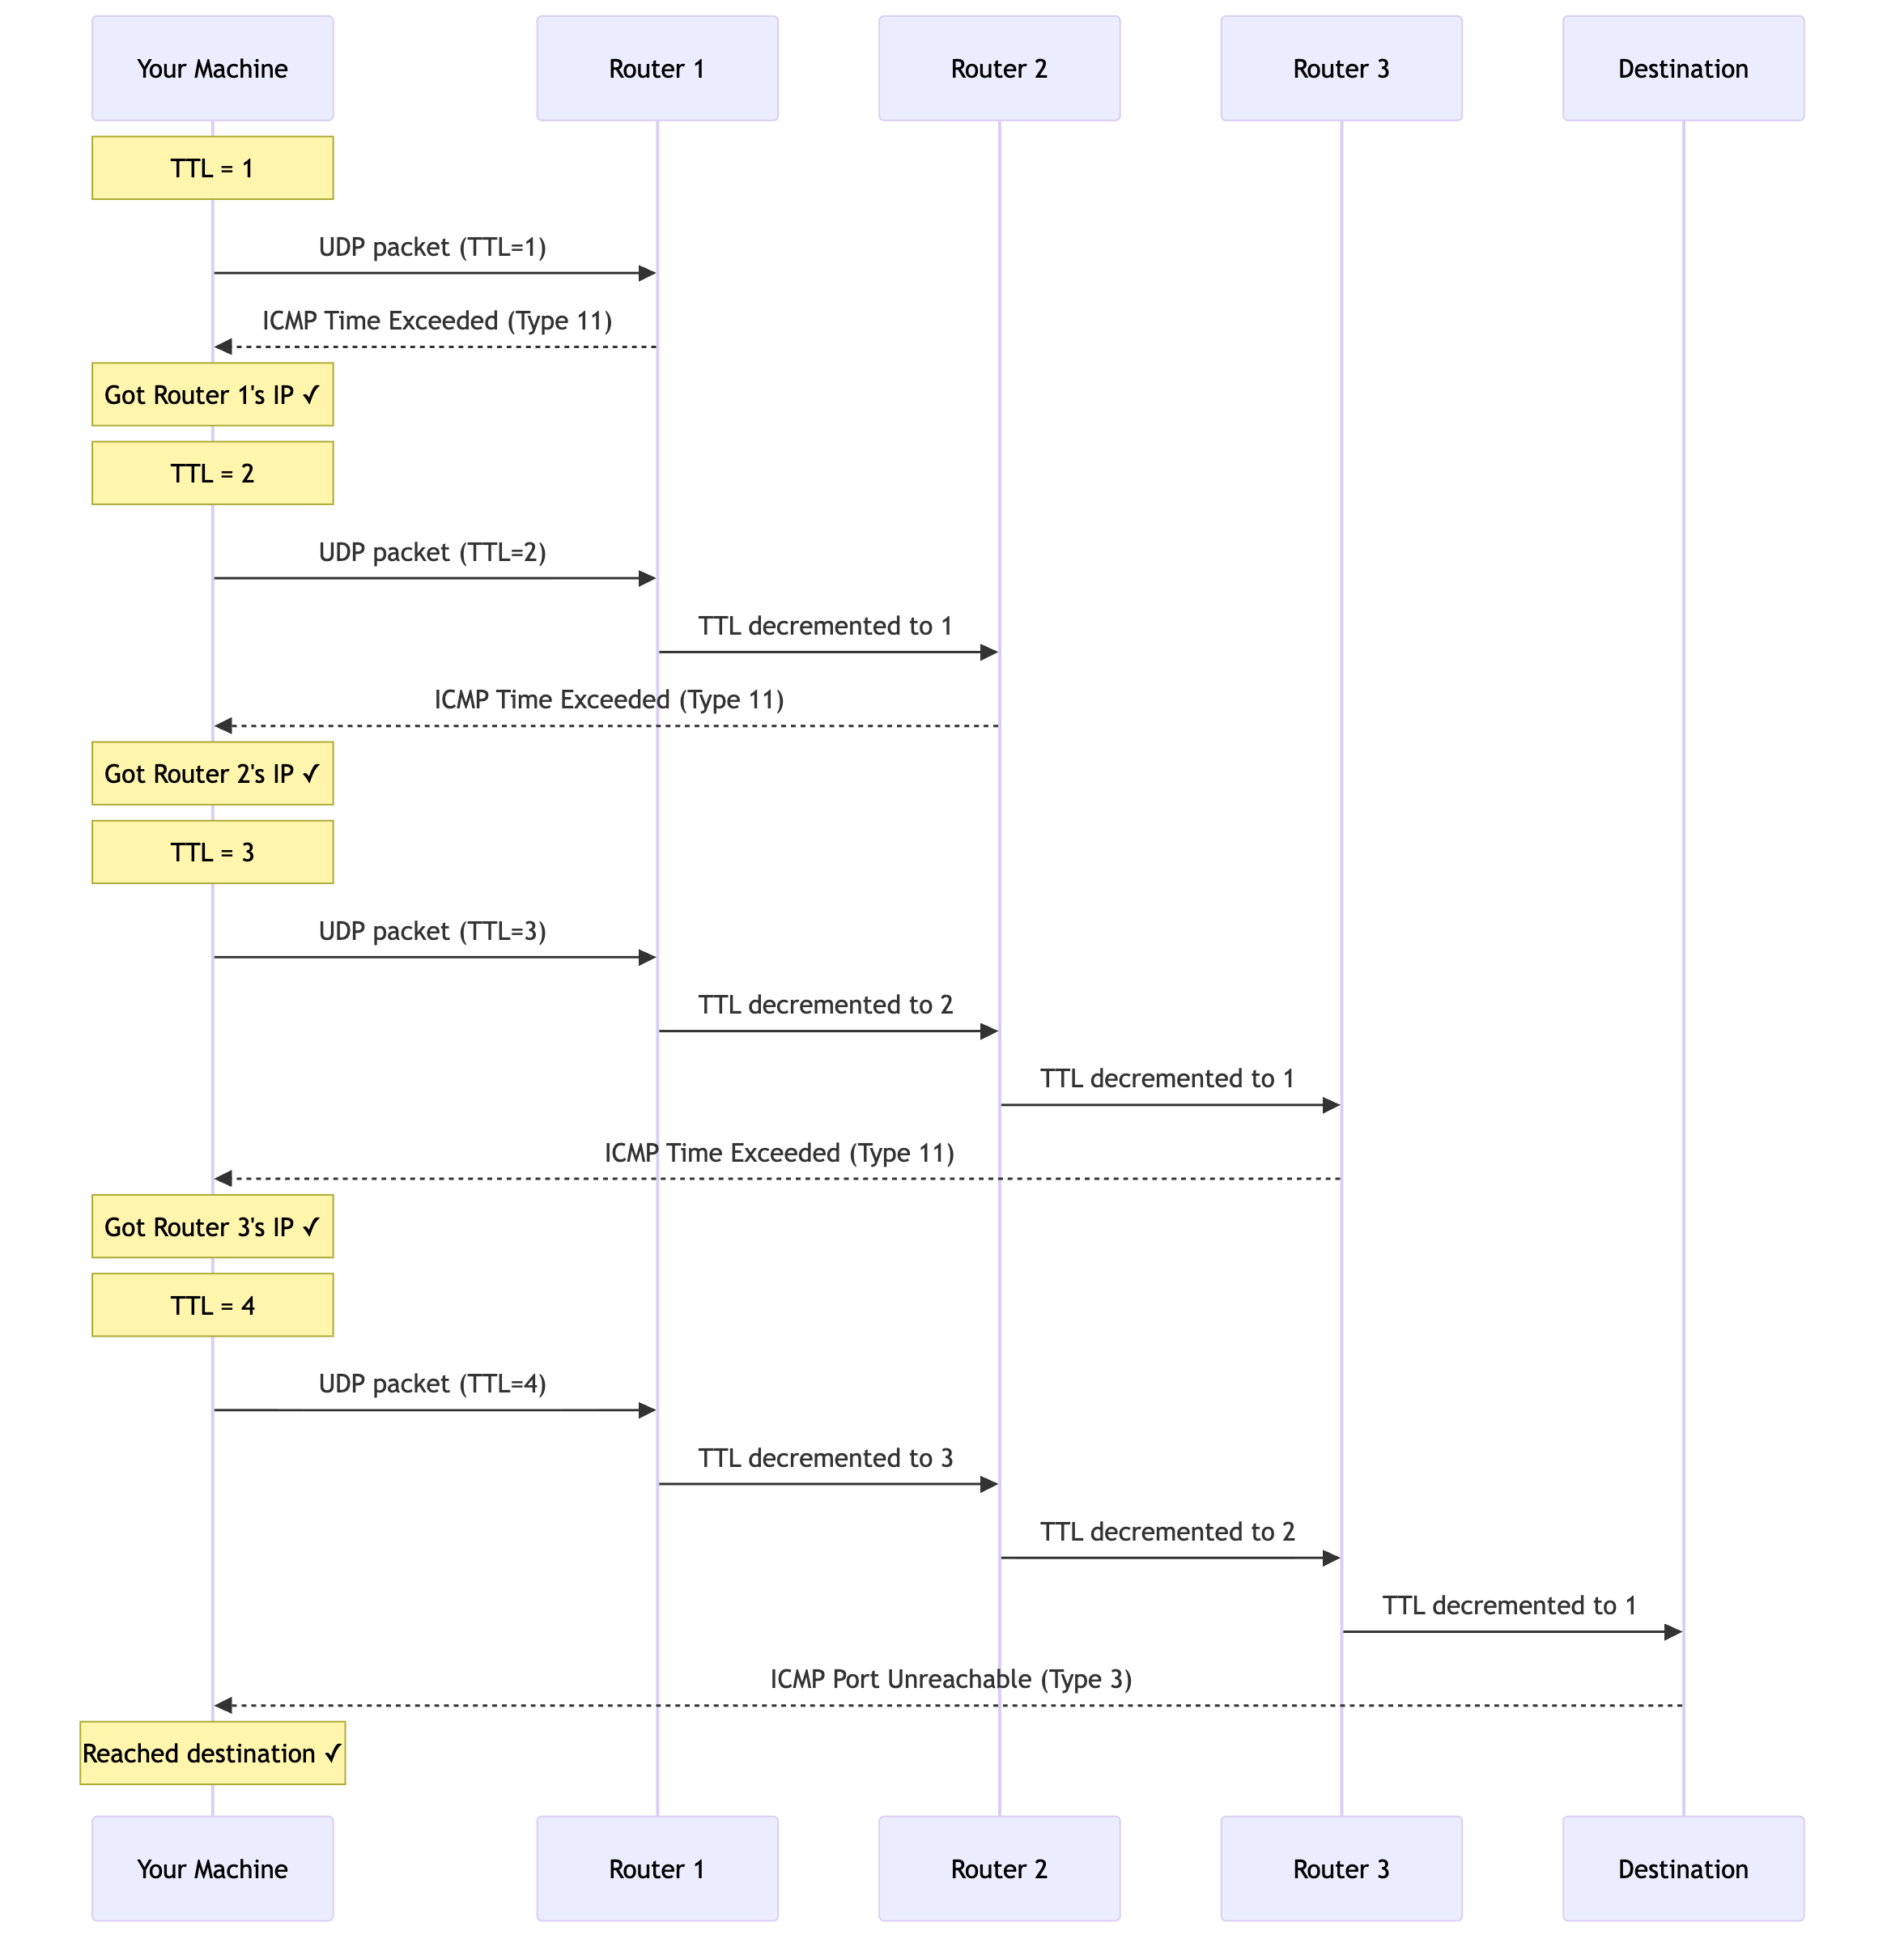
I never understood how traceroute discovers each hop. Turns out it's a clever TTL trick, and about 80 lines of Rust.
Discover powerful applications such as Little Snitch Mini, Little Snitch, LaunchBar and Micro Snitch.
Real-time network diagnostics in your terminal. One command, zero config, instant visibility. - matthart1983/netwatch
A practical field-focused walkthrough of deploying a Supervisor in VMware Cloud Foundation 9, with emphasis on networking design, VPC versus NSX Classic, Tier-0 architecture, routing, VKS operations, and preparing the platform for namespaces and Supervisor Services.
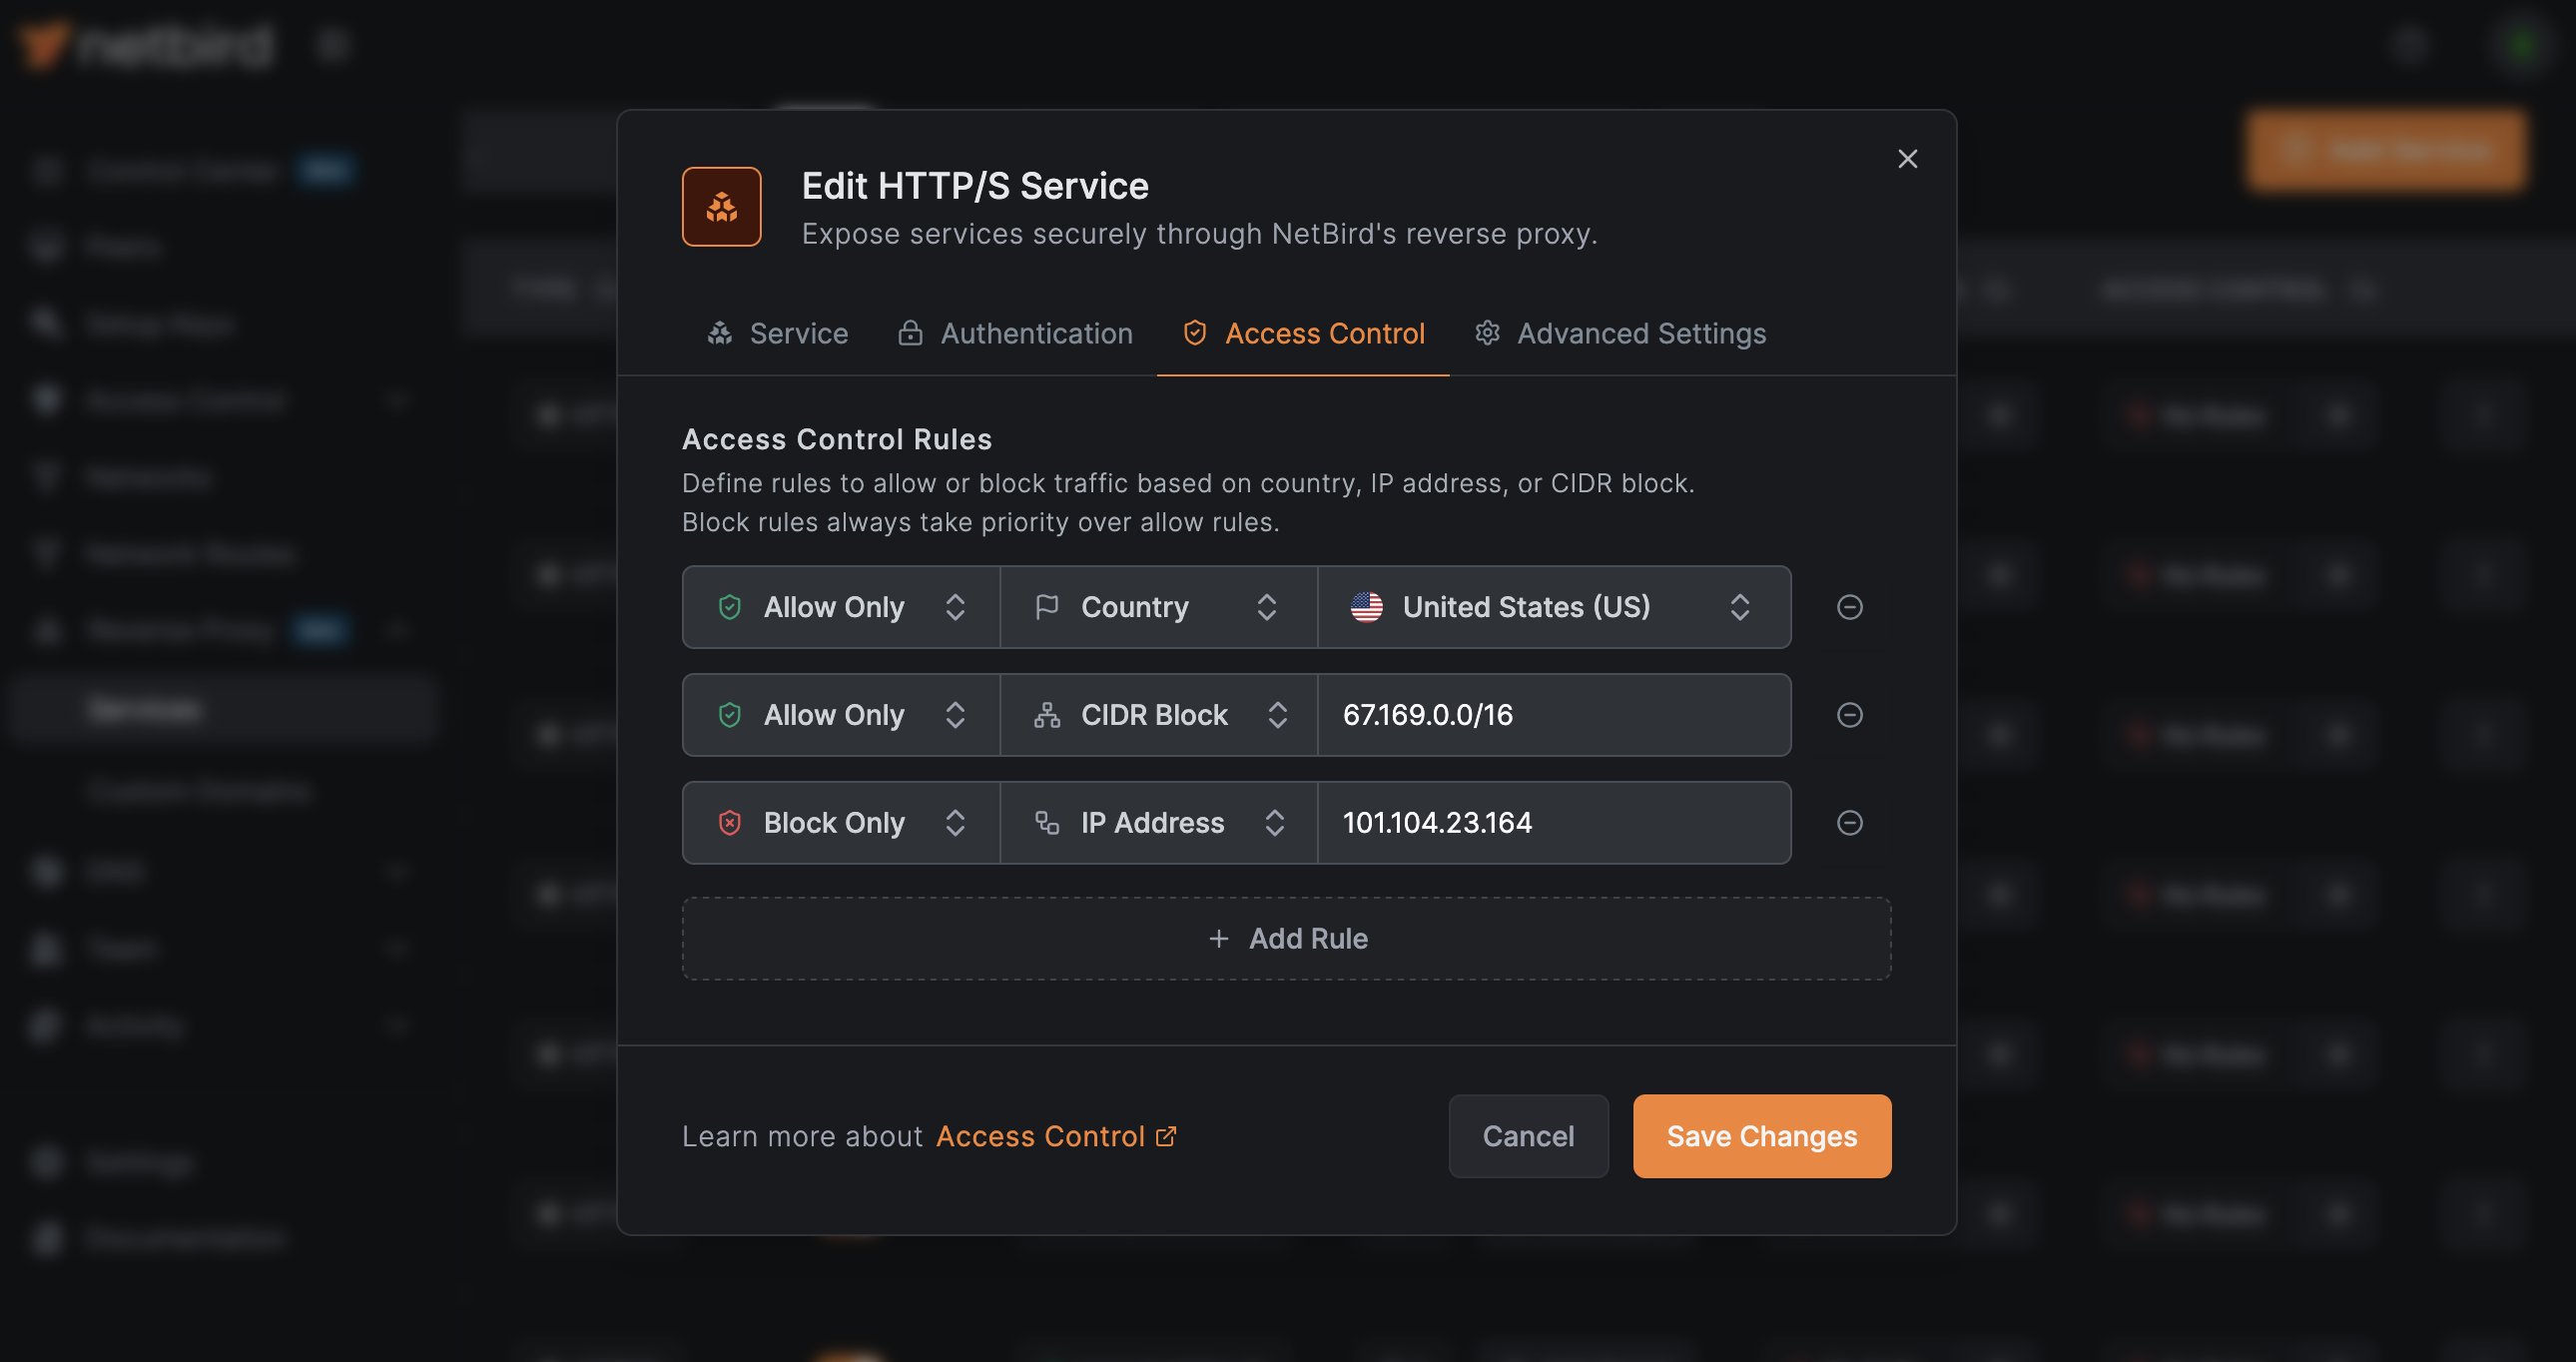
NetBird v0.67 brings Layer 4 proxy support to our reverse proxy! Expose TCP, UDP, and TLS services PLUS header-based auth, geo/IP access rules, client health checks, and more. https://netbird.io/knowledge-hub/l4-proxy
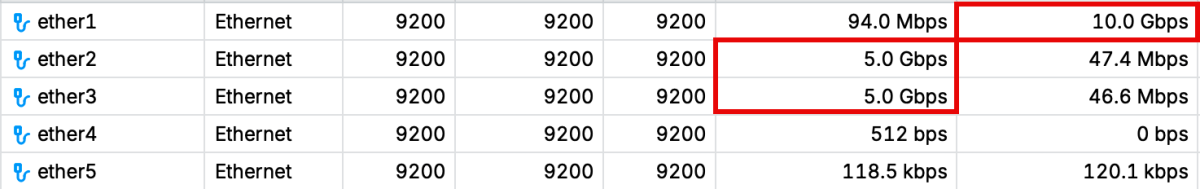
I have been running the full VMware Cloud Foundation (VCF) 9.0 stack using the Minisforum MS-A2 in a three-node configuration for almost a year now. While the MS-A2 is not hardware that you would f…
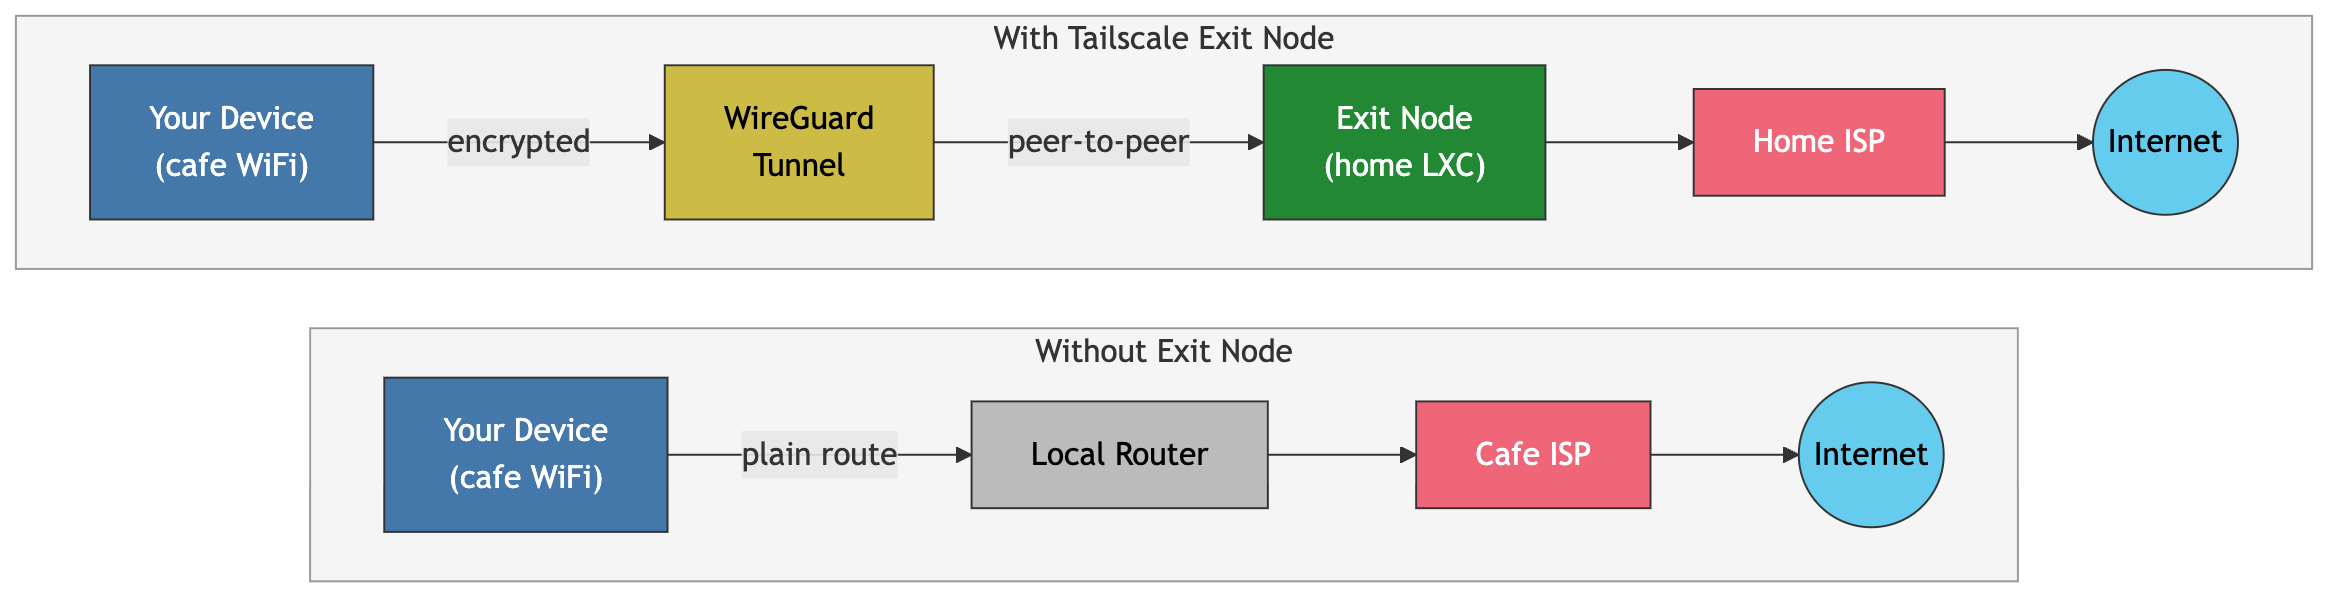
A practical deep dive into Tailscale exit nodes: route changes, traceroute evidence, DERP fallback, trust boundaries, and why this model can be free.
I run Coolify on a Hetzner bare metal server to host multiple web apps I have built and the services I use to maintain them. Of course almost none of my sites have any users, but I enjoy the process, and that is not here or there (but if you
chronyis a versatile implementation of the Network Time Protocol (NTP).
It can synchronise the system clock with NTP servers, reference clocks
(e.g. GPS receiver), and manual input using wristwatch an
Modern web interface for FreeBSD. Unified management of Bhyve VMs, Jails, ZFS storage, networking, and system monitoring.
Browser-based utilities for VCF 9, NSX, vSAN, and networking. No install. Zero data collected.
Applying DevOps to networks.
Content feedback and comments
Let's make a tiny, standalone CA! We'll use a Raspberry Pi 4, YubiKey 5 NFC, and Infinite Noise TRNG.
Complete guide to using NGINX as an API gateway in 2026, covering configuration, load balancing, rate limiting, and the Kubernetes ingress-nginx retirement.
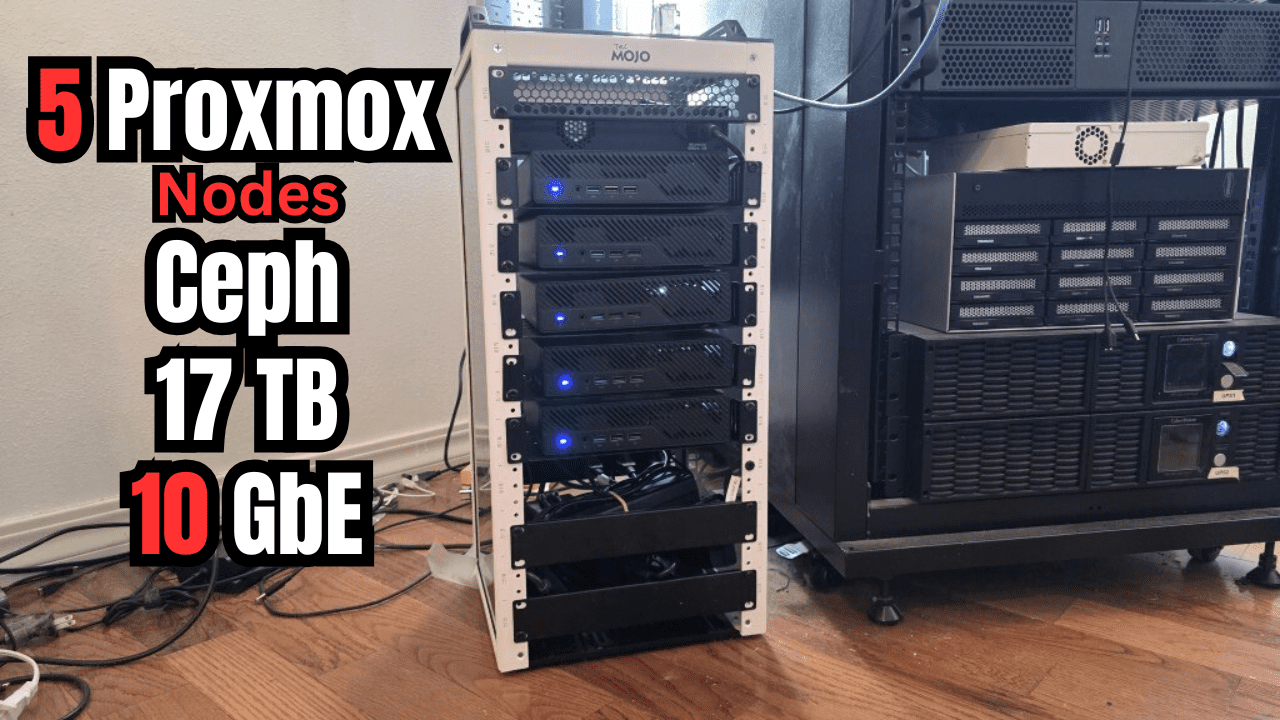
See how I built a Proxmox and Ceph home lab with 5 nodes, 17TB NVMe storage, dual 10Gb LACP, and Talos Kubernetes running on distributed Ceph.
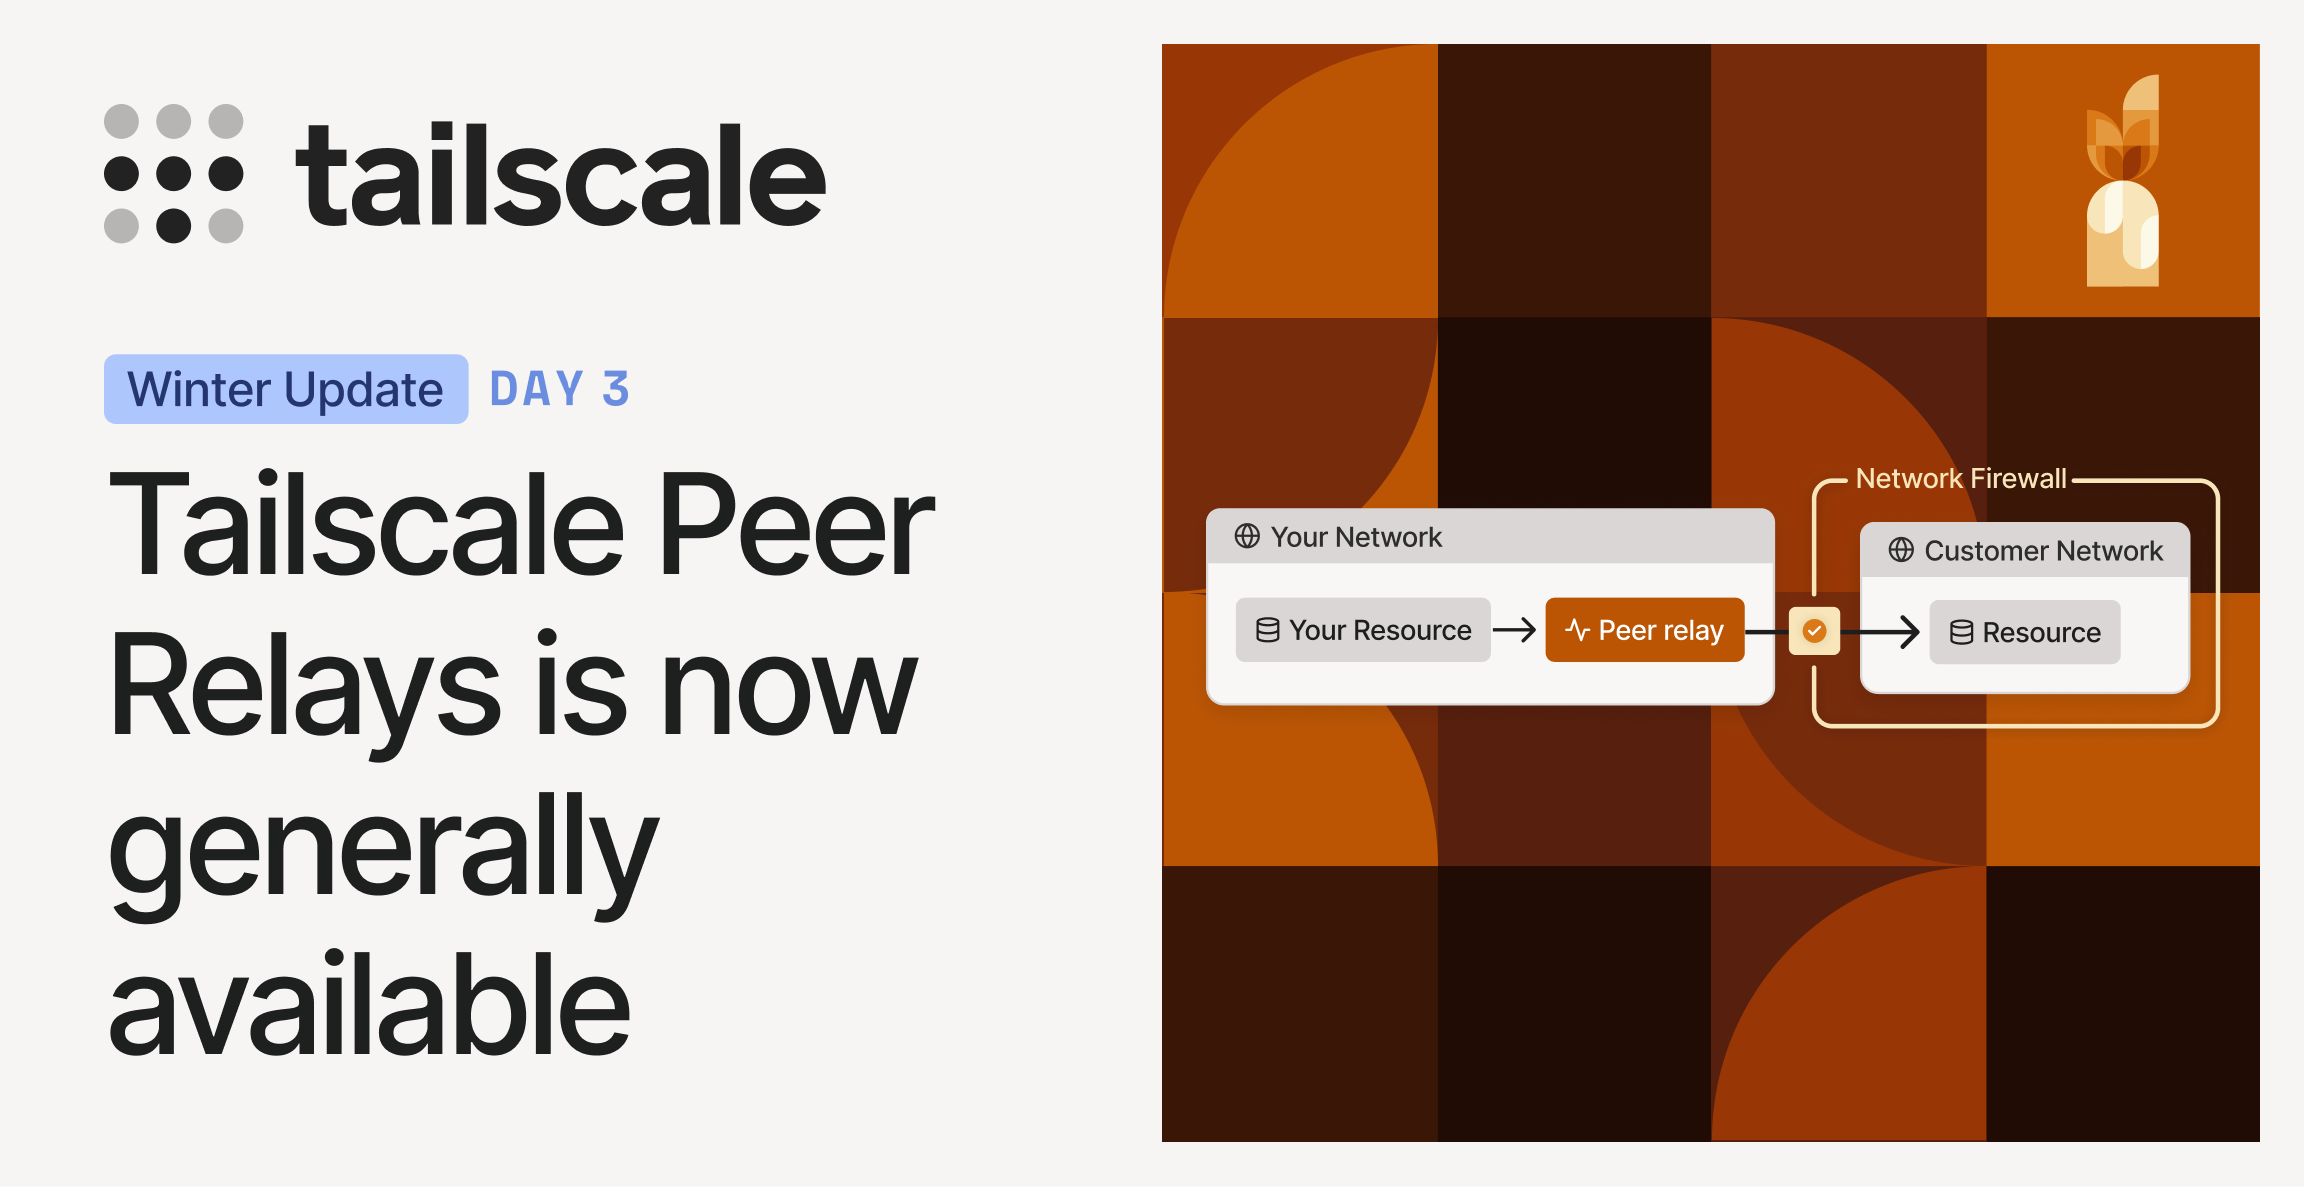
Work around hard NATs and tricky networks with production-grade connectivity nodes you control
When you request a certificate from Let’s Encrypt, our servers validate that you control the hostnames in that certificate using ACME challenges. For subscribers who need wildcard certificates or who prefer not to expose infrastructure to the public Internet, the DNS-01 challenge type has long been the only choice. DNS-01 works well. It is widely supported and battle-tested, but it comes with operational costs: DNS propagation delays, recurring DNS updates at renewal time, and automation that often requires distributing DNS credentials throughout your infrastructure.
Comprenez la différence MTU MSS pour éviter la fragmentation réseau. Tutoriel complet : config, tests ping, Jumbo Frames et exemples Kubernetes.
Give LLM agents shell access without risking your host system. A practical libvirt guide covering VM creation, snapshots for safe experimentation, and remote access options.
This video explains the basic networking within Red Hat OpenShift Platform. From pod network to services, routes and secondary vlan and private networks.
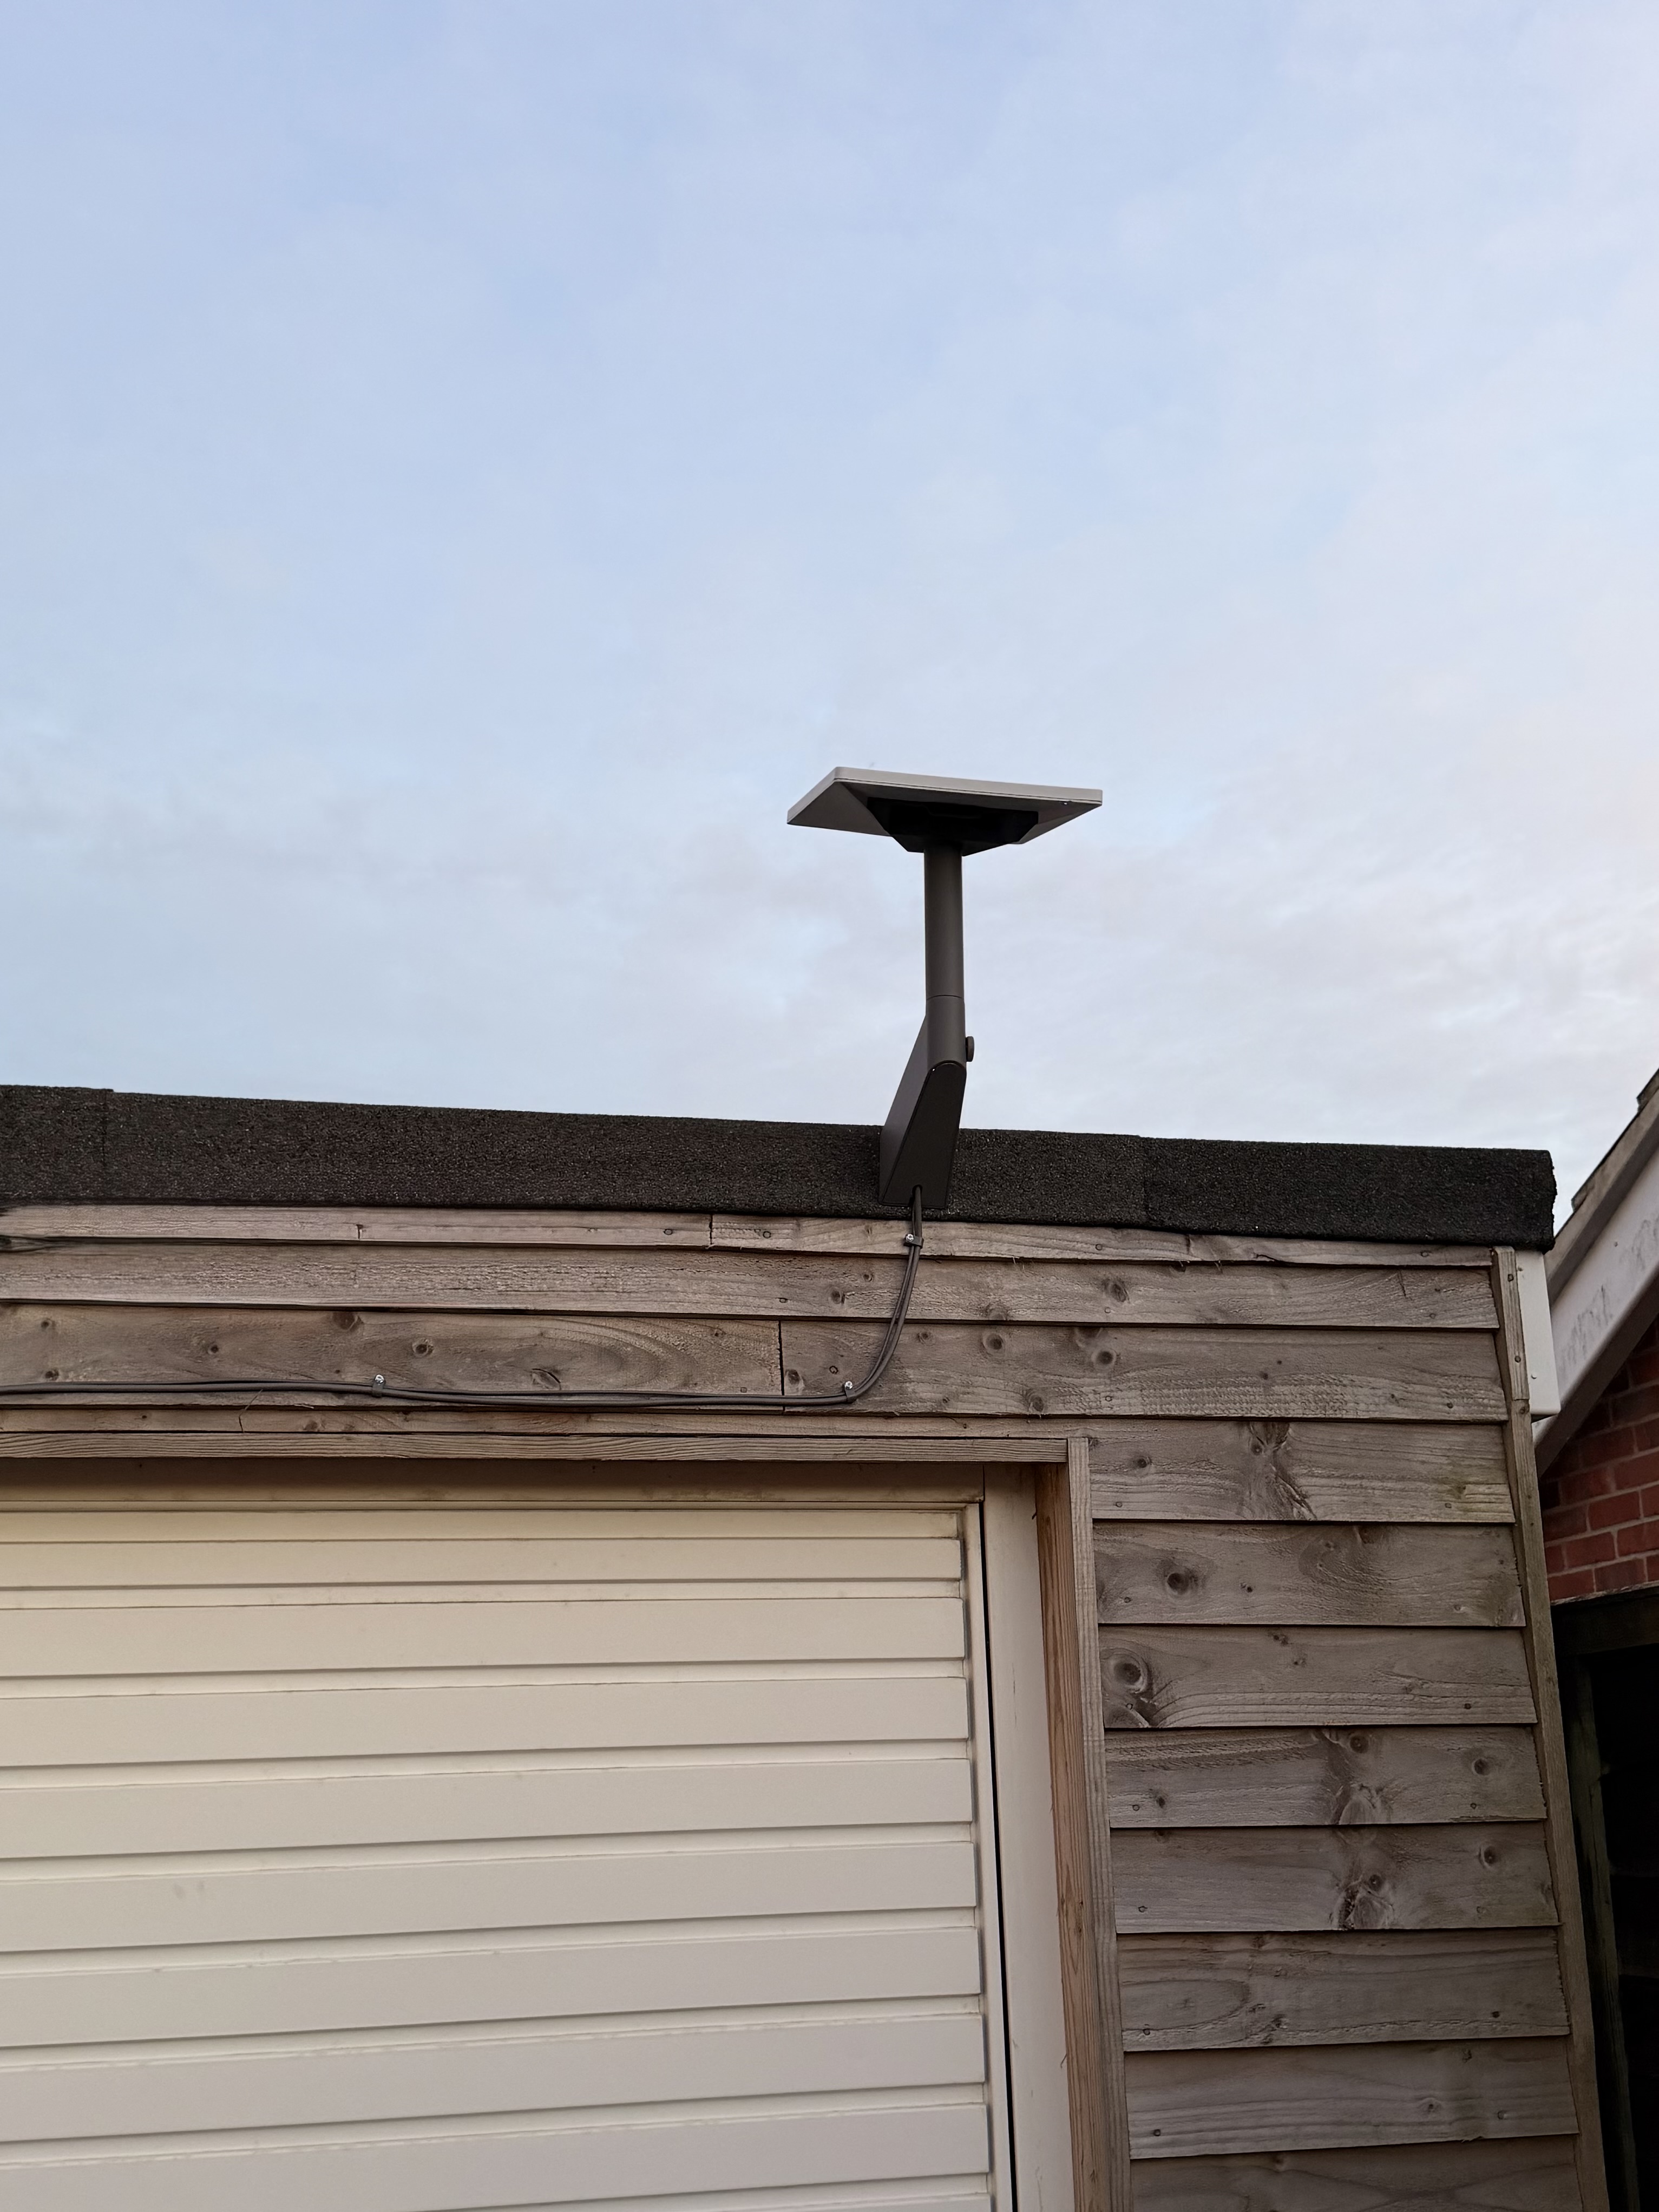
I recently picked up a Starlink Mini to use as a backup connection for my home network. The underlying technology is fascinating - thousands of satellites in low Earth orbit delivering broadband almost anywhere. With the new £4.50 standby plan, it's an excellent way to keep things online.
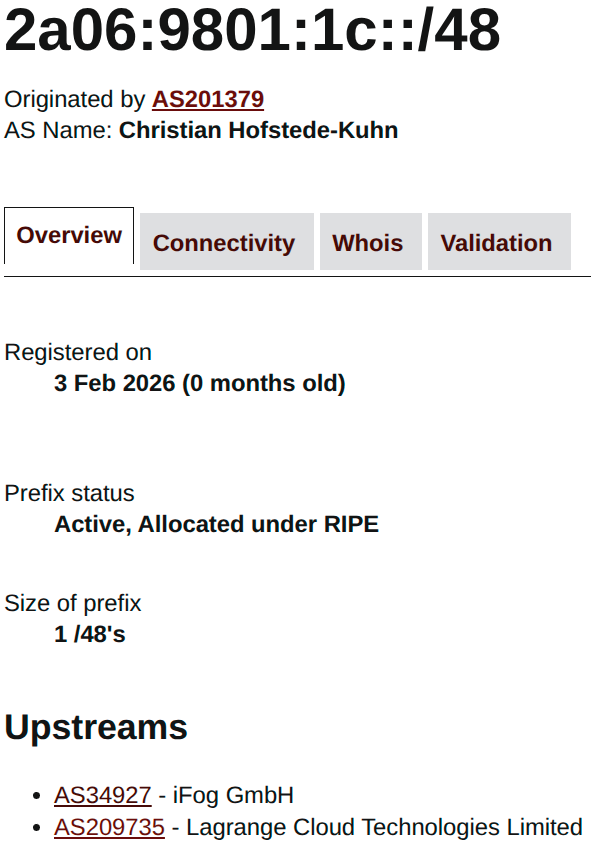
How I obtained my own AS number and IPv6 prefix, set up a FreeBSD BGP router with FRR, and built a tunnel overlay to bring globally routable addresses to servers that already have provider-assigned...
Short blog about my experiences with Nutanix CE and which workarounds I needed.
Comment j'ai obtenu mon propre ASN et utilisé BGP pour annoncer des routes IPv6 depuis chez moi.
The Nutanix Cloud Bible - A detailed narrative of the Nutanix architecture, how the software and features work and how to leverage it for maximum performance.
Author: Nemanja Ilic
Accurate vNIC-to-IP mapping is fundamental for virtual networking visibility, security, and troubleshooting. On the Nutanix AHV hypervisor, this mapping becomes especially important for services like Flow Virtual Networking, microsegmentation,...
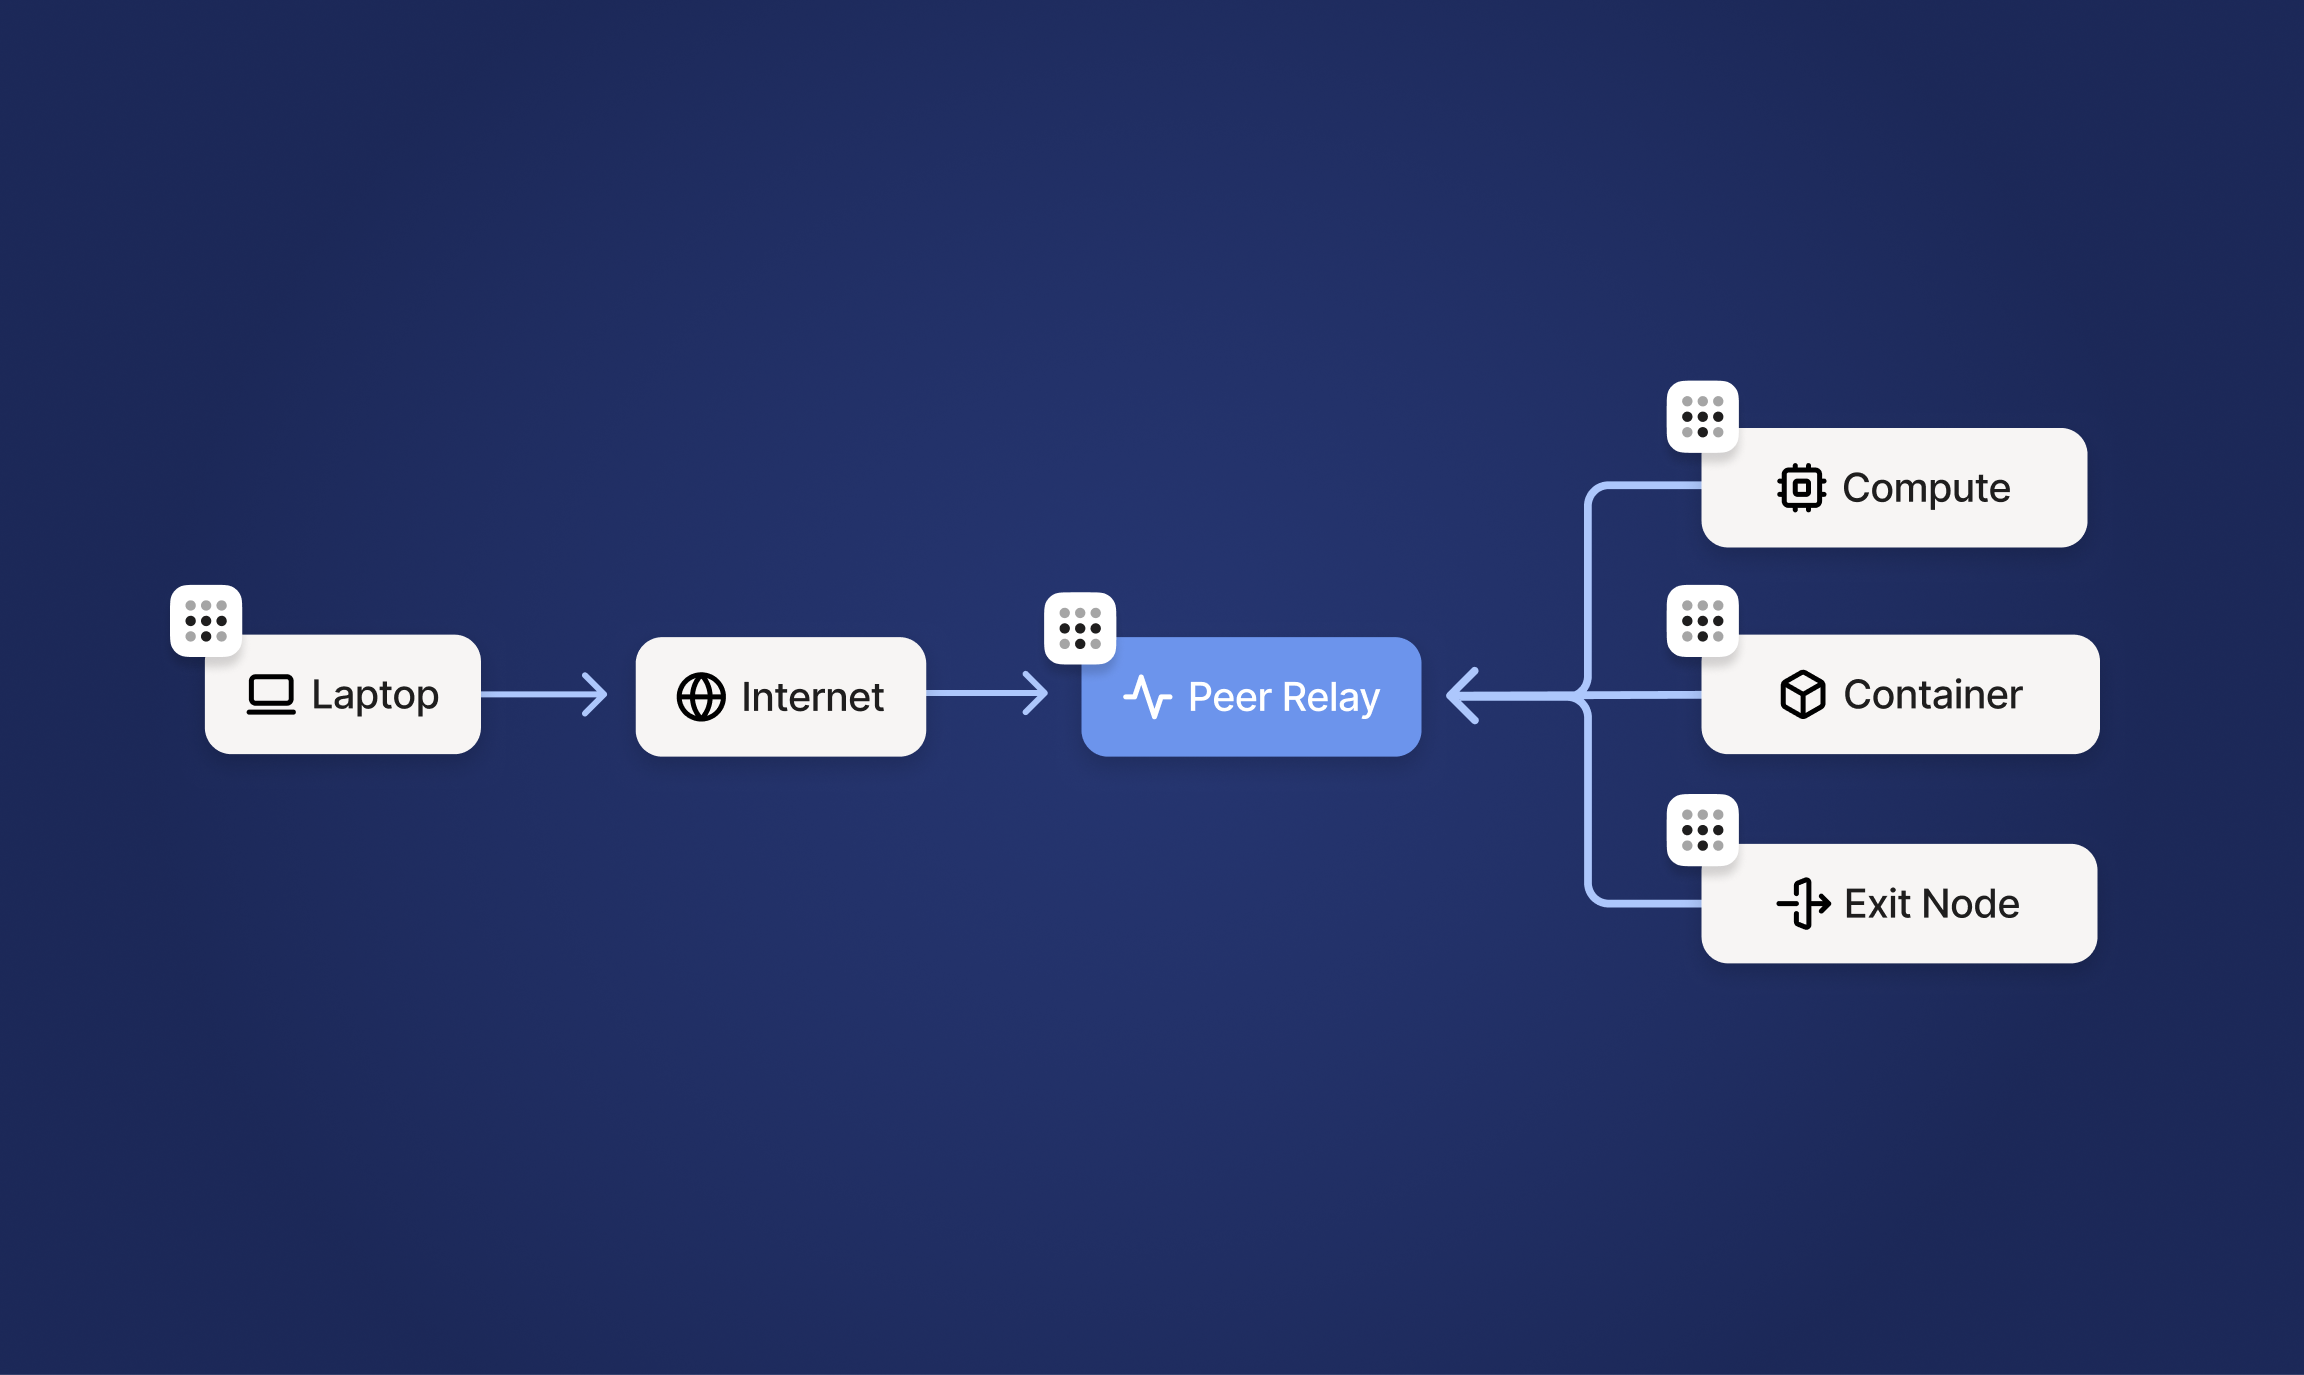
Getting from Delhi back to a Minnesota meant unforgiving networks. Tailscale Peer Relays offered a massive improvement.
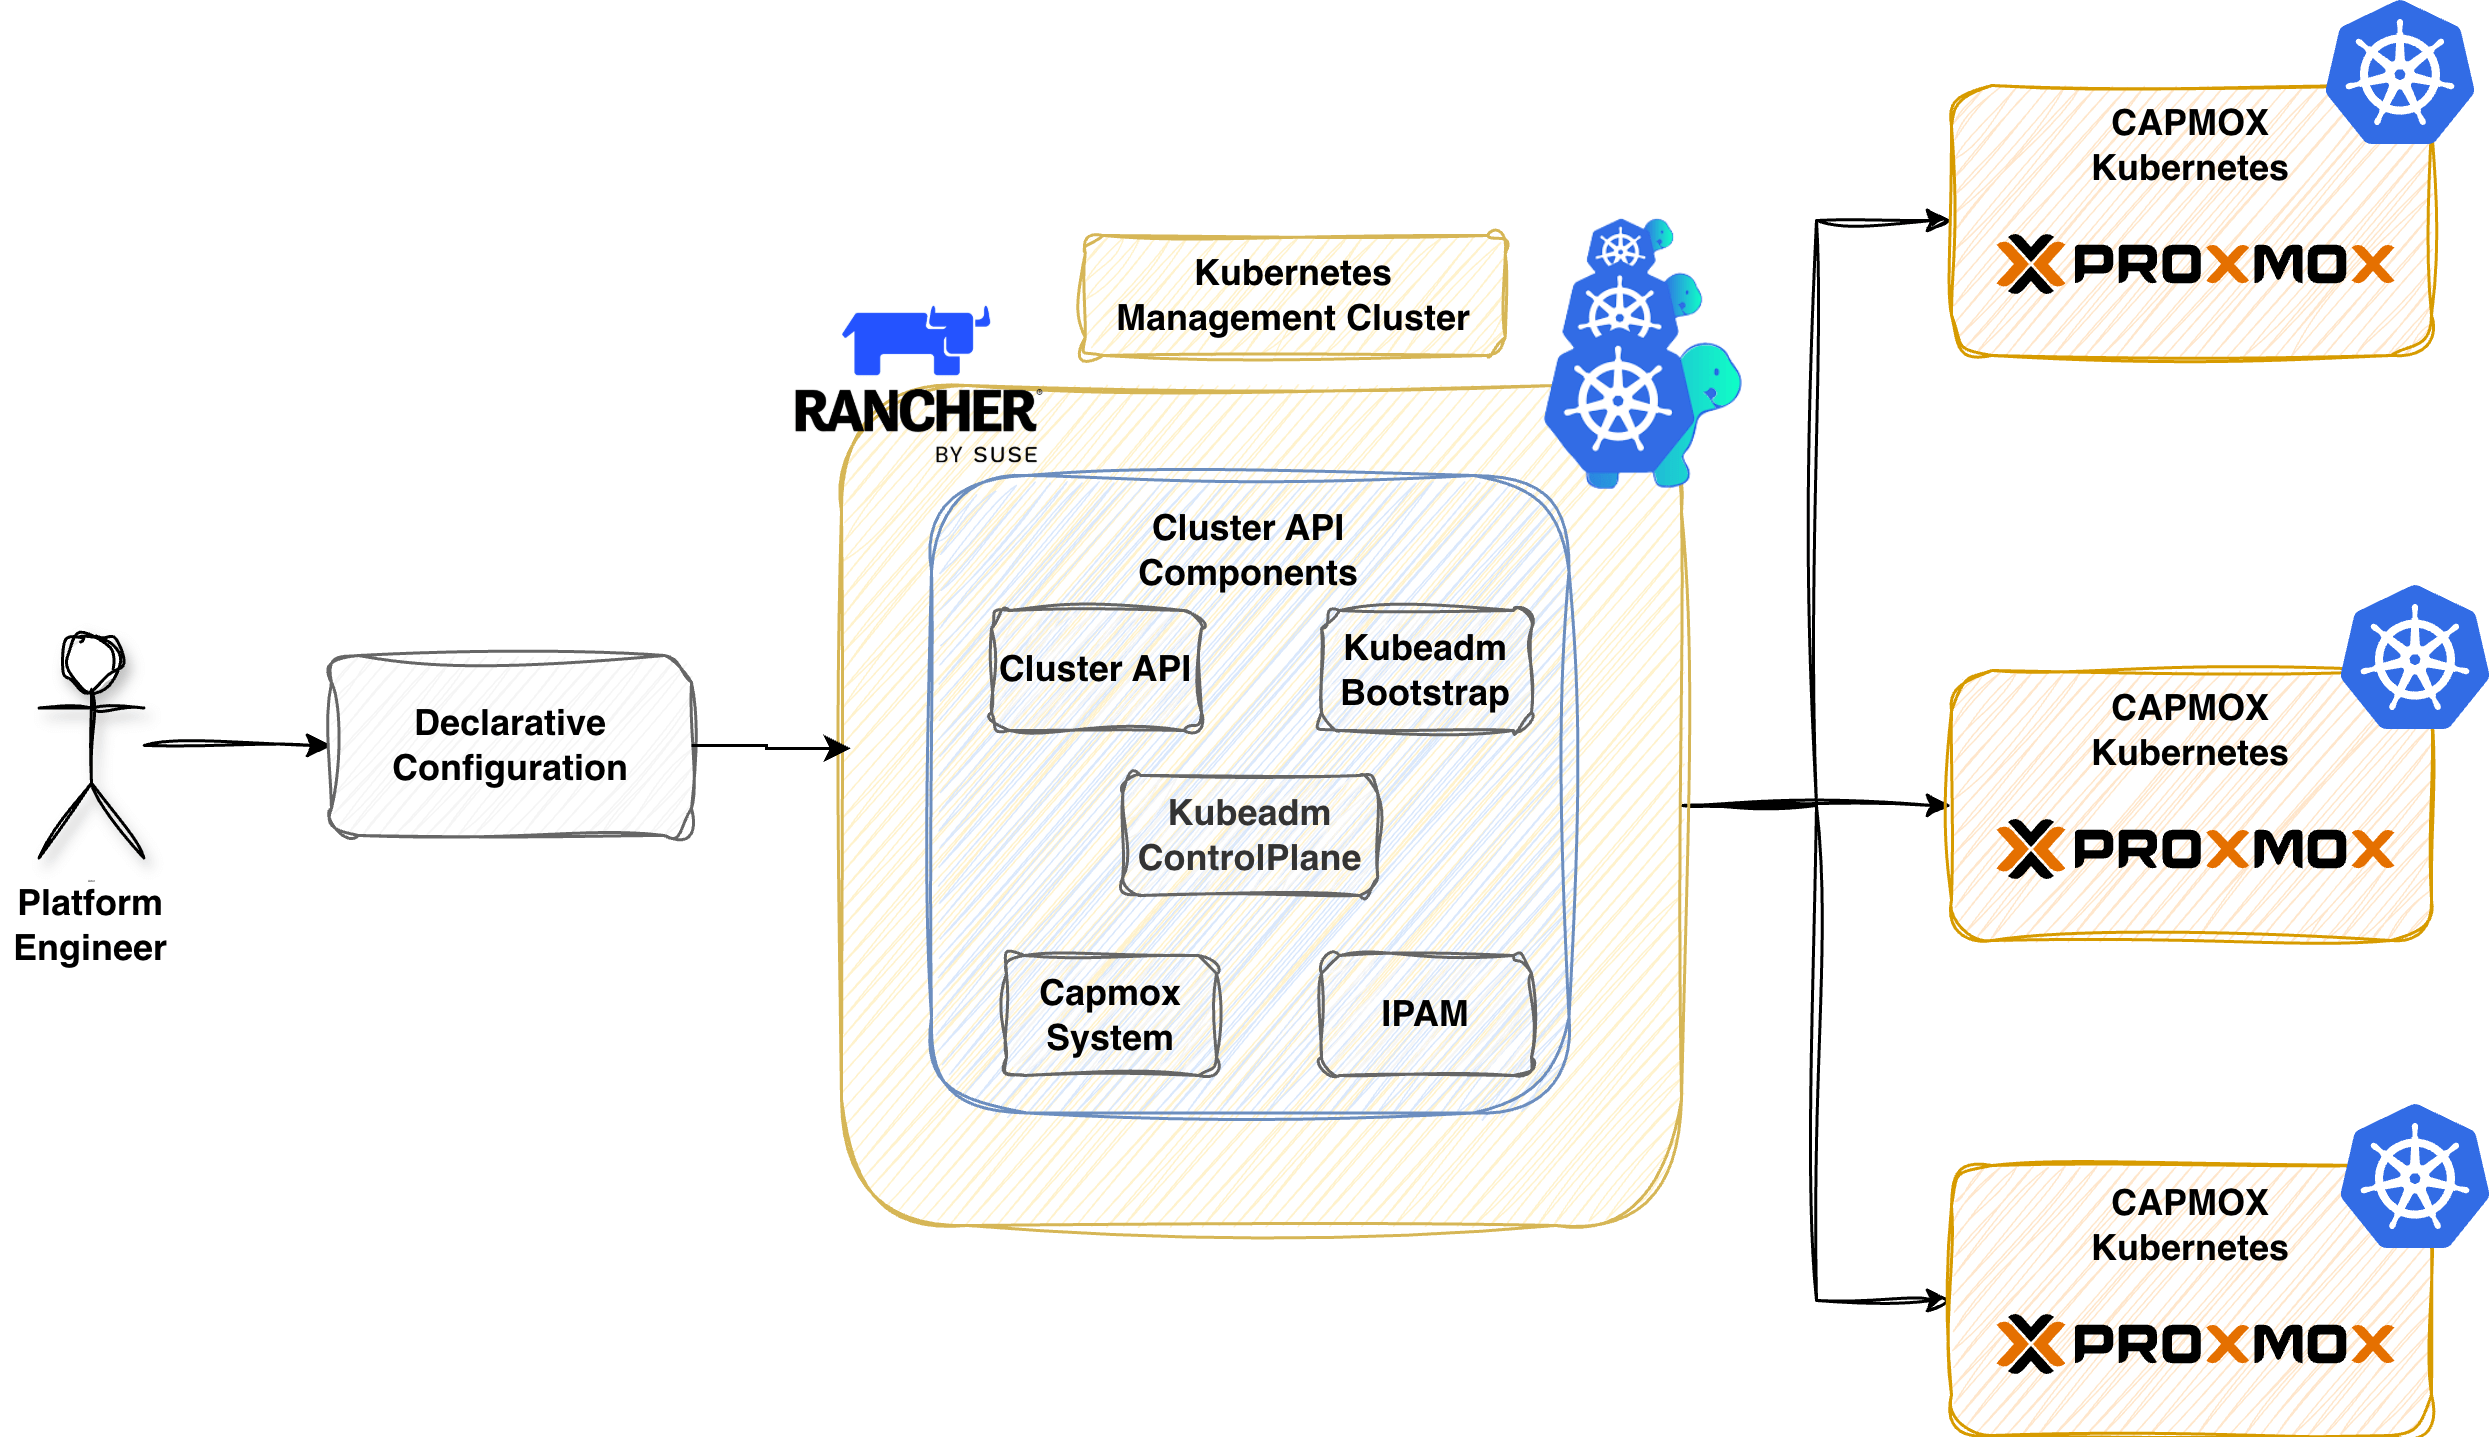
A comprehensive step-by-step guide series to creating Kubernetes managed clusters on Proxmox using Cluster API and Cilium as a CNI.
An inspection of Claude Code's network requests, system prompt, and context handling by intercepting real traffic.
This post explains how I operate my homelab with no public WAN exposure, using WireGuard to stay permanently connected to my home network from all my devices, …
Last month i shared a screenshot of a single switch validation. 12 tests.
When we talk about routing, we often picture routers, firewalls, and network appliances moving traffic across large networks.
Découvrez comment déployer un cluster Kubernetes entièrement en IPv6 avec Talos OS.
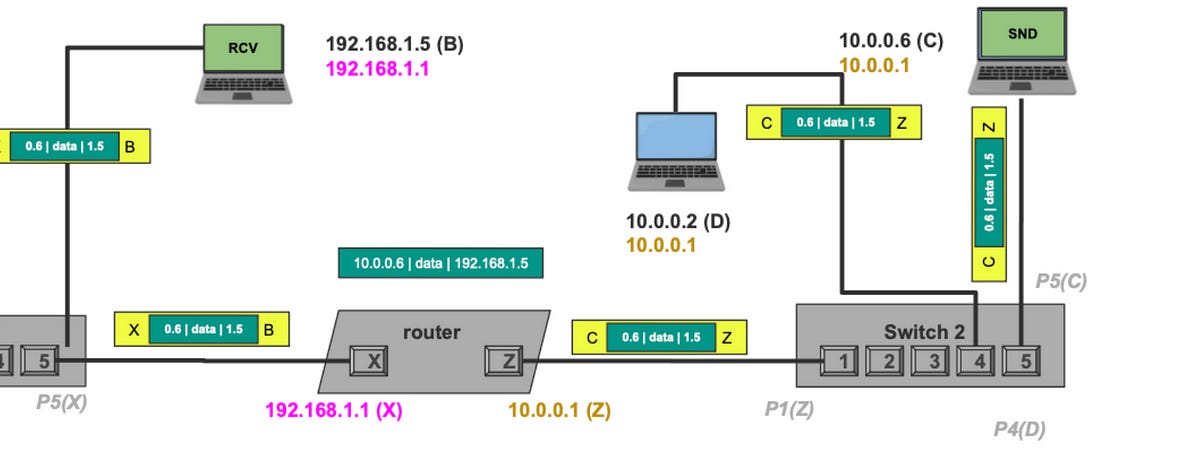
A Primer
Minimal Linux container host. Contribute to vmware/photon development by creating an account on GitHub.
Userspace WireGuard® Implementation in Rust. Contribute to mullvad/gotatun development by creating an account on GitHub.
The Challenge: When Granularity Is Your Only Option We were dealing with a legacy "beast" of a platform: a critical and systemic service running on traditional infrastructure, glued behind a single IP address. This IP hosted hundreds of distinct TCP ports, each representing different customers, prot
VMware Cloud Foundation 9 has brought the Virtual Private Cloud networking model front and center in the vSphere UI. Not only has it become extremely easy to provide a self-service solution for networking, but it also comes with a plethora of networking services and capabilities.
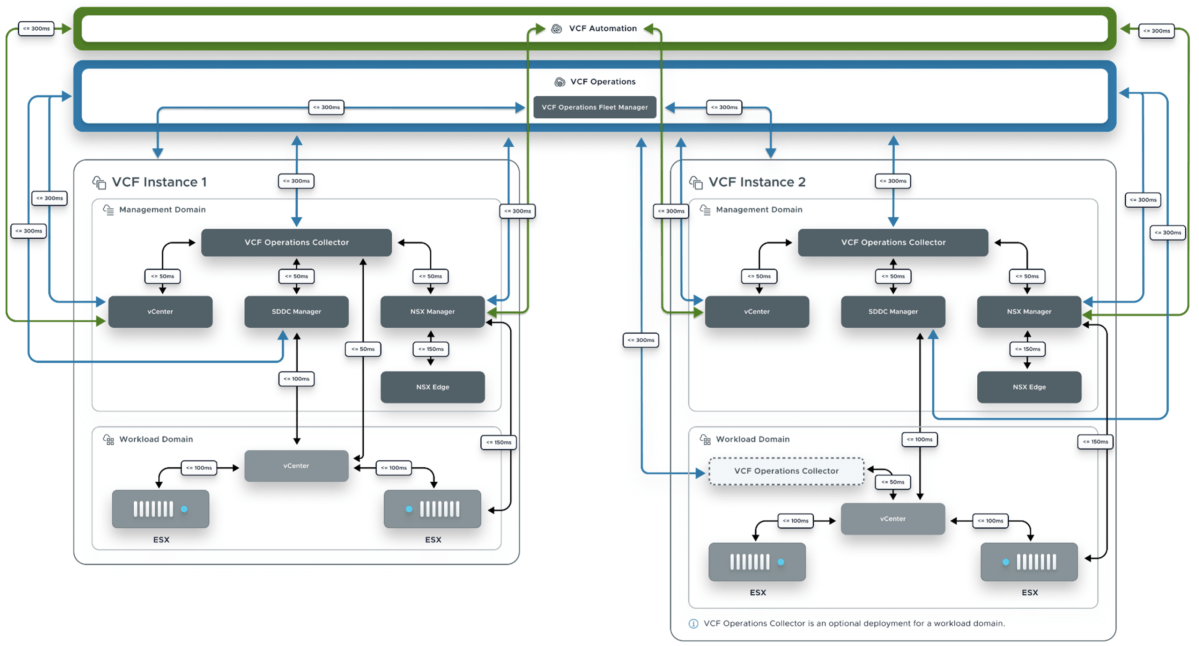
Network latency is an important factor when designing a VMware Cloud Foundation (VCF) Fleet and to assist VCF architects in understanding the various latency maximums, we have just published a new …
The Excavator Doesn't Care About Your Diversity We'd done everything right. Diverse and multiple fiber paths to our remote site.
An exploration of DNS and Name-to-IP translation. This deep dive explores NSS, getaddrinfo, systemd-resolved and more!
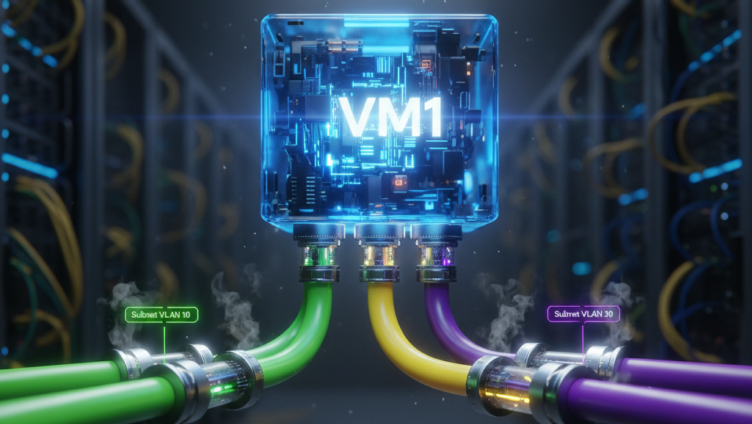
Learn how to attach your VM to multiple Virtual Private Cloud subnets, leveraging Guest VLAN Tagging.
Kasm Workspaces delivers zero-trust remote browser isolation, Desktop as a Service (DaaS), and OSINT workloads to your web browser.
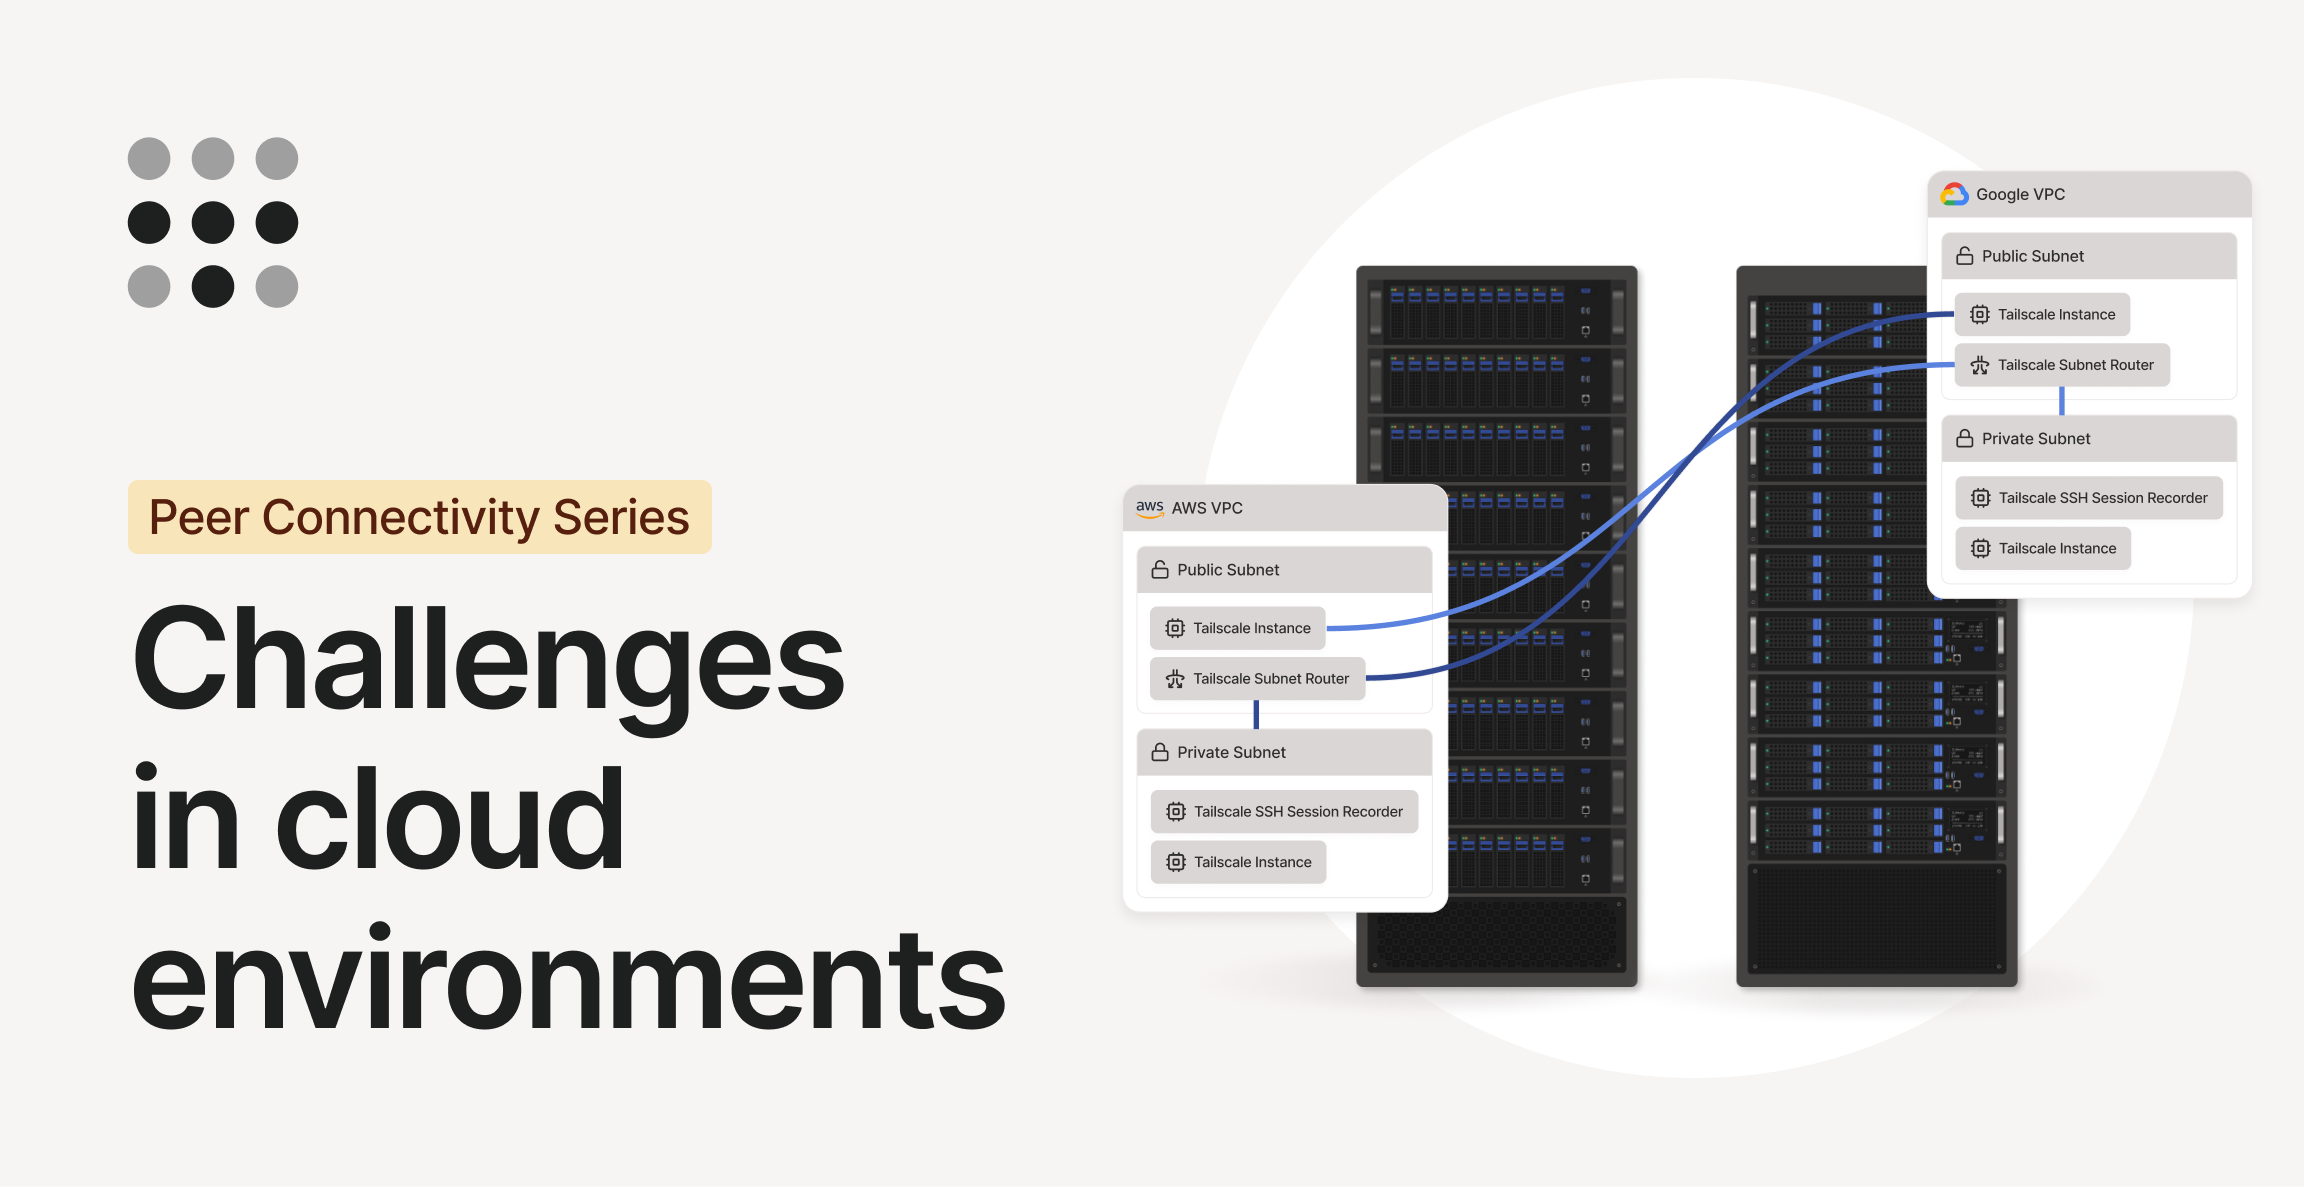
How Tailscale can work with and inside Google Cloud, Microsoft Azure, and Amazon Web Services.
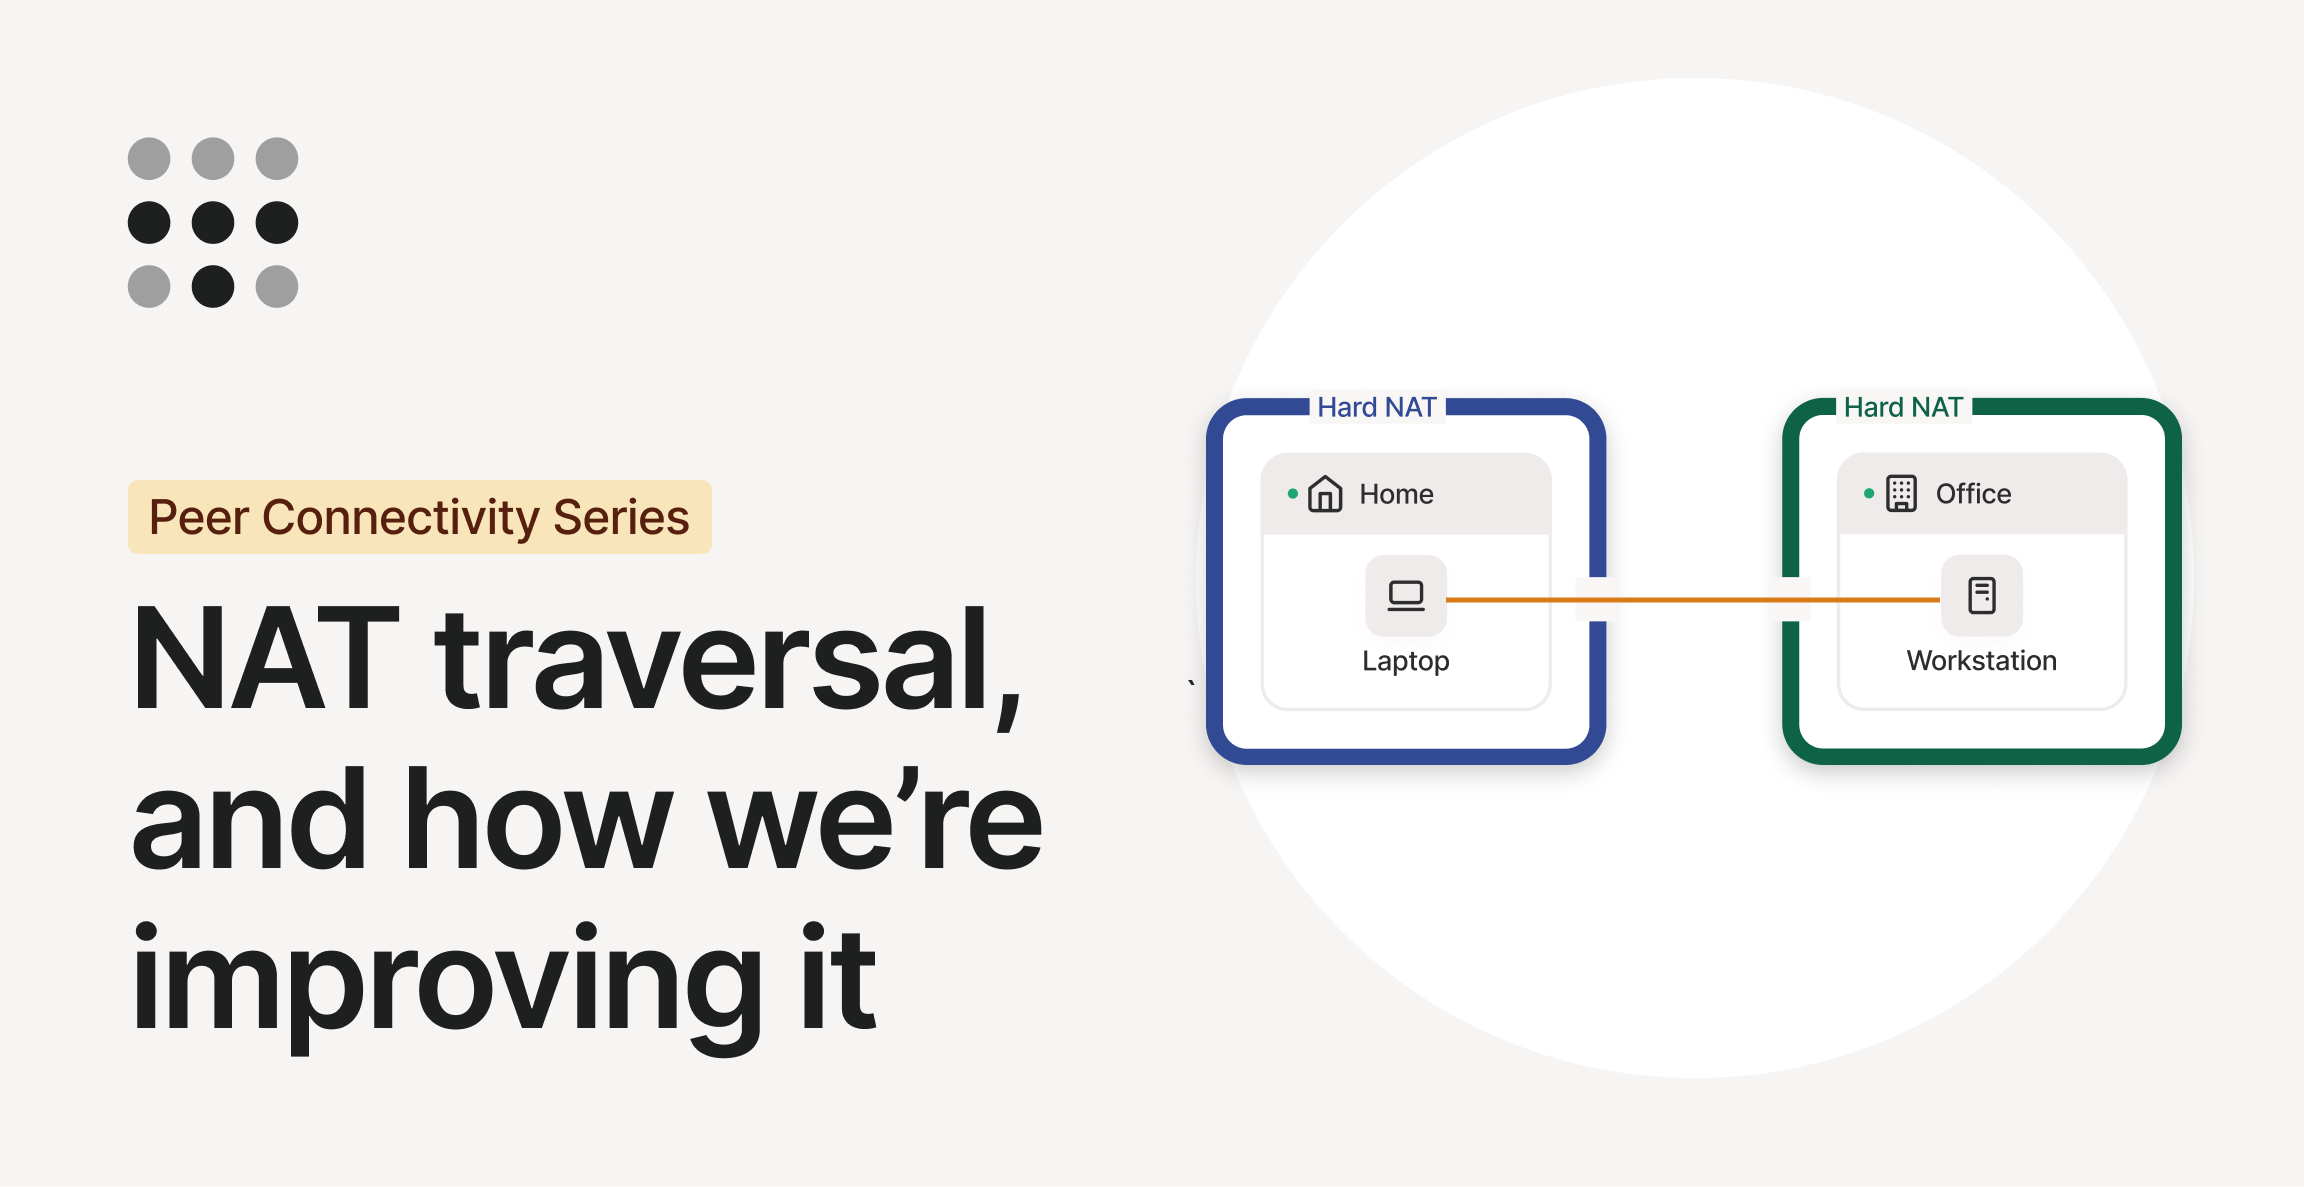
Updates on Tailscale's efforts to improve NAT traversal, for its client and for the web at large.
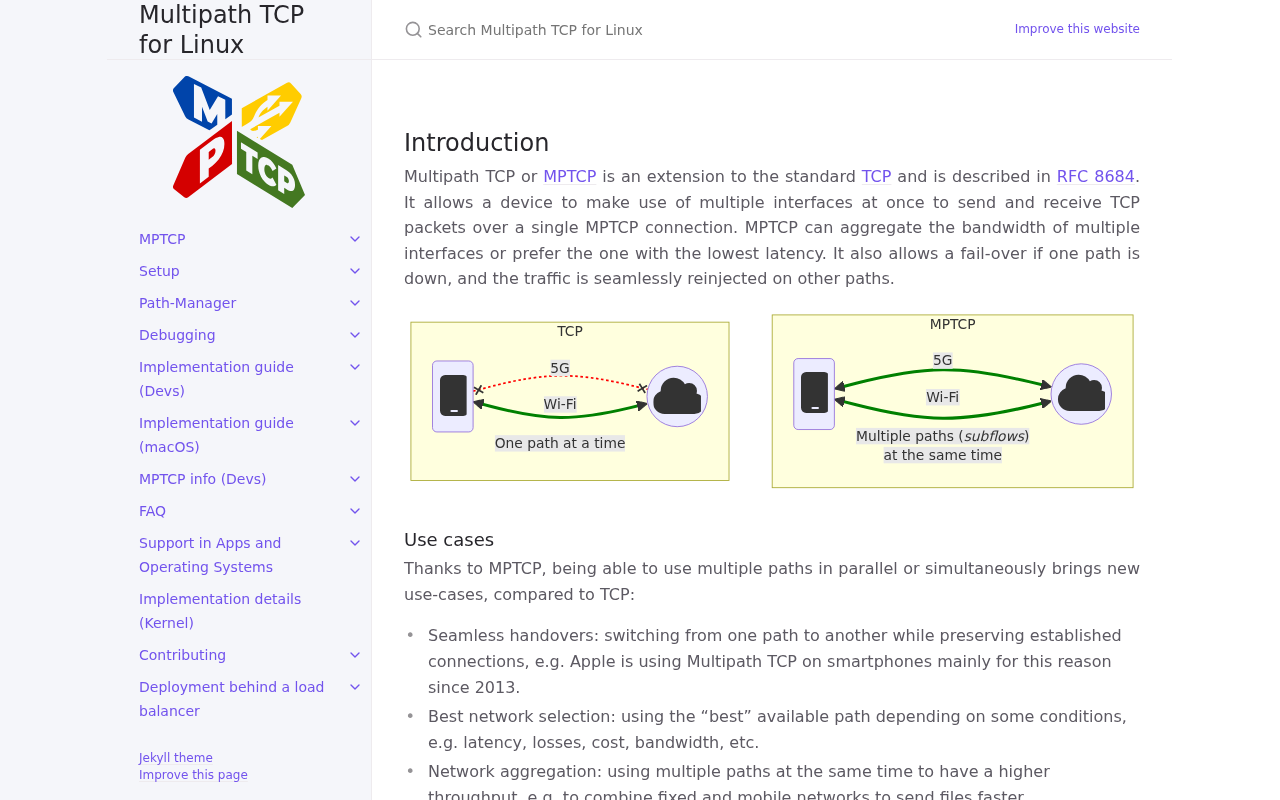
Multipath TCP (MPTCP) for Linux, an extension to TCP that enhances connection redundancy and performance by utilizing multiple underlying TCP sessions simultaneously. This site provides installation guides, debugging tools, FAQs, and a list of apps supporting MPTCP, aimed at facilitating the adoption and implementation of MPTCP for Linux users and developers.
BGP implemented in the Go Programming Language. Contribute to osrg/gobgp development by creating an account on GitHub.
Découvrez comment remplacer votre box Internet SFR, Free, Bouygues ou Orange par du matériel UniFi. Guide complet opérateur par opérateur.
Whilst Microsoft SQL Server is still in technical preview in Data Services Manager 9.0.1, our team continues to release significant enhancements for our customers as we gravitate towards full support.
I recently migrated my self-hosted services from a VPS (virtual private server) at a remote data center to a physical server at home. This change was motivated by wanting to be in control of the hardw
“It’s always DNS” is a famous meme among network people. Name resolution is technically quite simple. It’s “just” translating a hostname like jan.wildeboer.net to an IP address. What could possibly go wrong? I am a radical optimist and detail-obsessed knowledge collector, so I decided to find out. As part of my goal to make my home network a little island of Digital Sovereignty, meaning that everything at home should JustWork™, even with no working internet connection, a DNS server is needed.
Note: this blog is about mapping VLAN tags to NSX segments. The same functionality is described for VPC subnets in this post. Guest VLAN Tagging alone… not great with NSX By default, a virtual machine sends traffic to its vNIC untagged. The virtual switch then receives that traffic into a single VLAN or NSX segment. … Continued
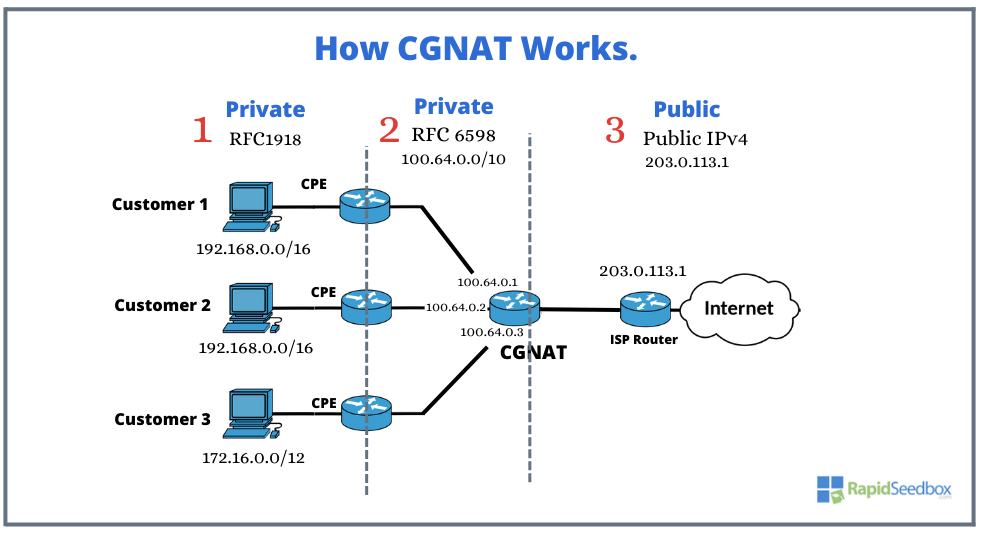
Home internet in the 90s felt simple. You plugged into [Ethernet](https://en.wikipedia.org/wiki/Ethernet), got an [IPv4](https://en.wikipedia.org/wiki/IPv4) address, and you could expose a service dir...
On August 21, 2025, an influx of traffic directed toward clients hosted in AWS us-east-1 caused severe congestion on links between Cloudflare and us-east-1. In this post, we explain what the failure was, why it occurred, and what we’re doing to make sure this doesn’t happen again.
Connect everything, from cloud to IoT, with the next-generation global network solution. Simple, resilient, and secure networking in minutes.
On July 14th, 2025, Cloudflare made a change to our service topologies that caused an outage for 1.1.1.1 on the edge, resulting in downtime for 62 minutes for customers using the 1.1.1.1 public DNS Resolver as well as intermittent degradation of service for Gateway DNS.
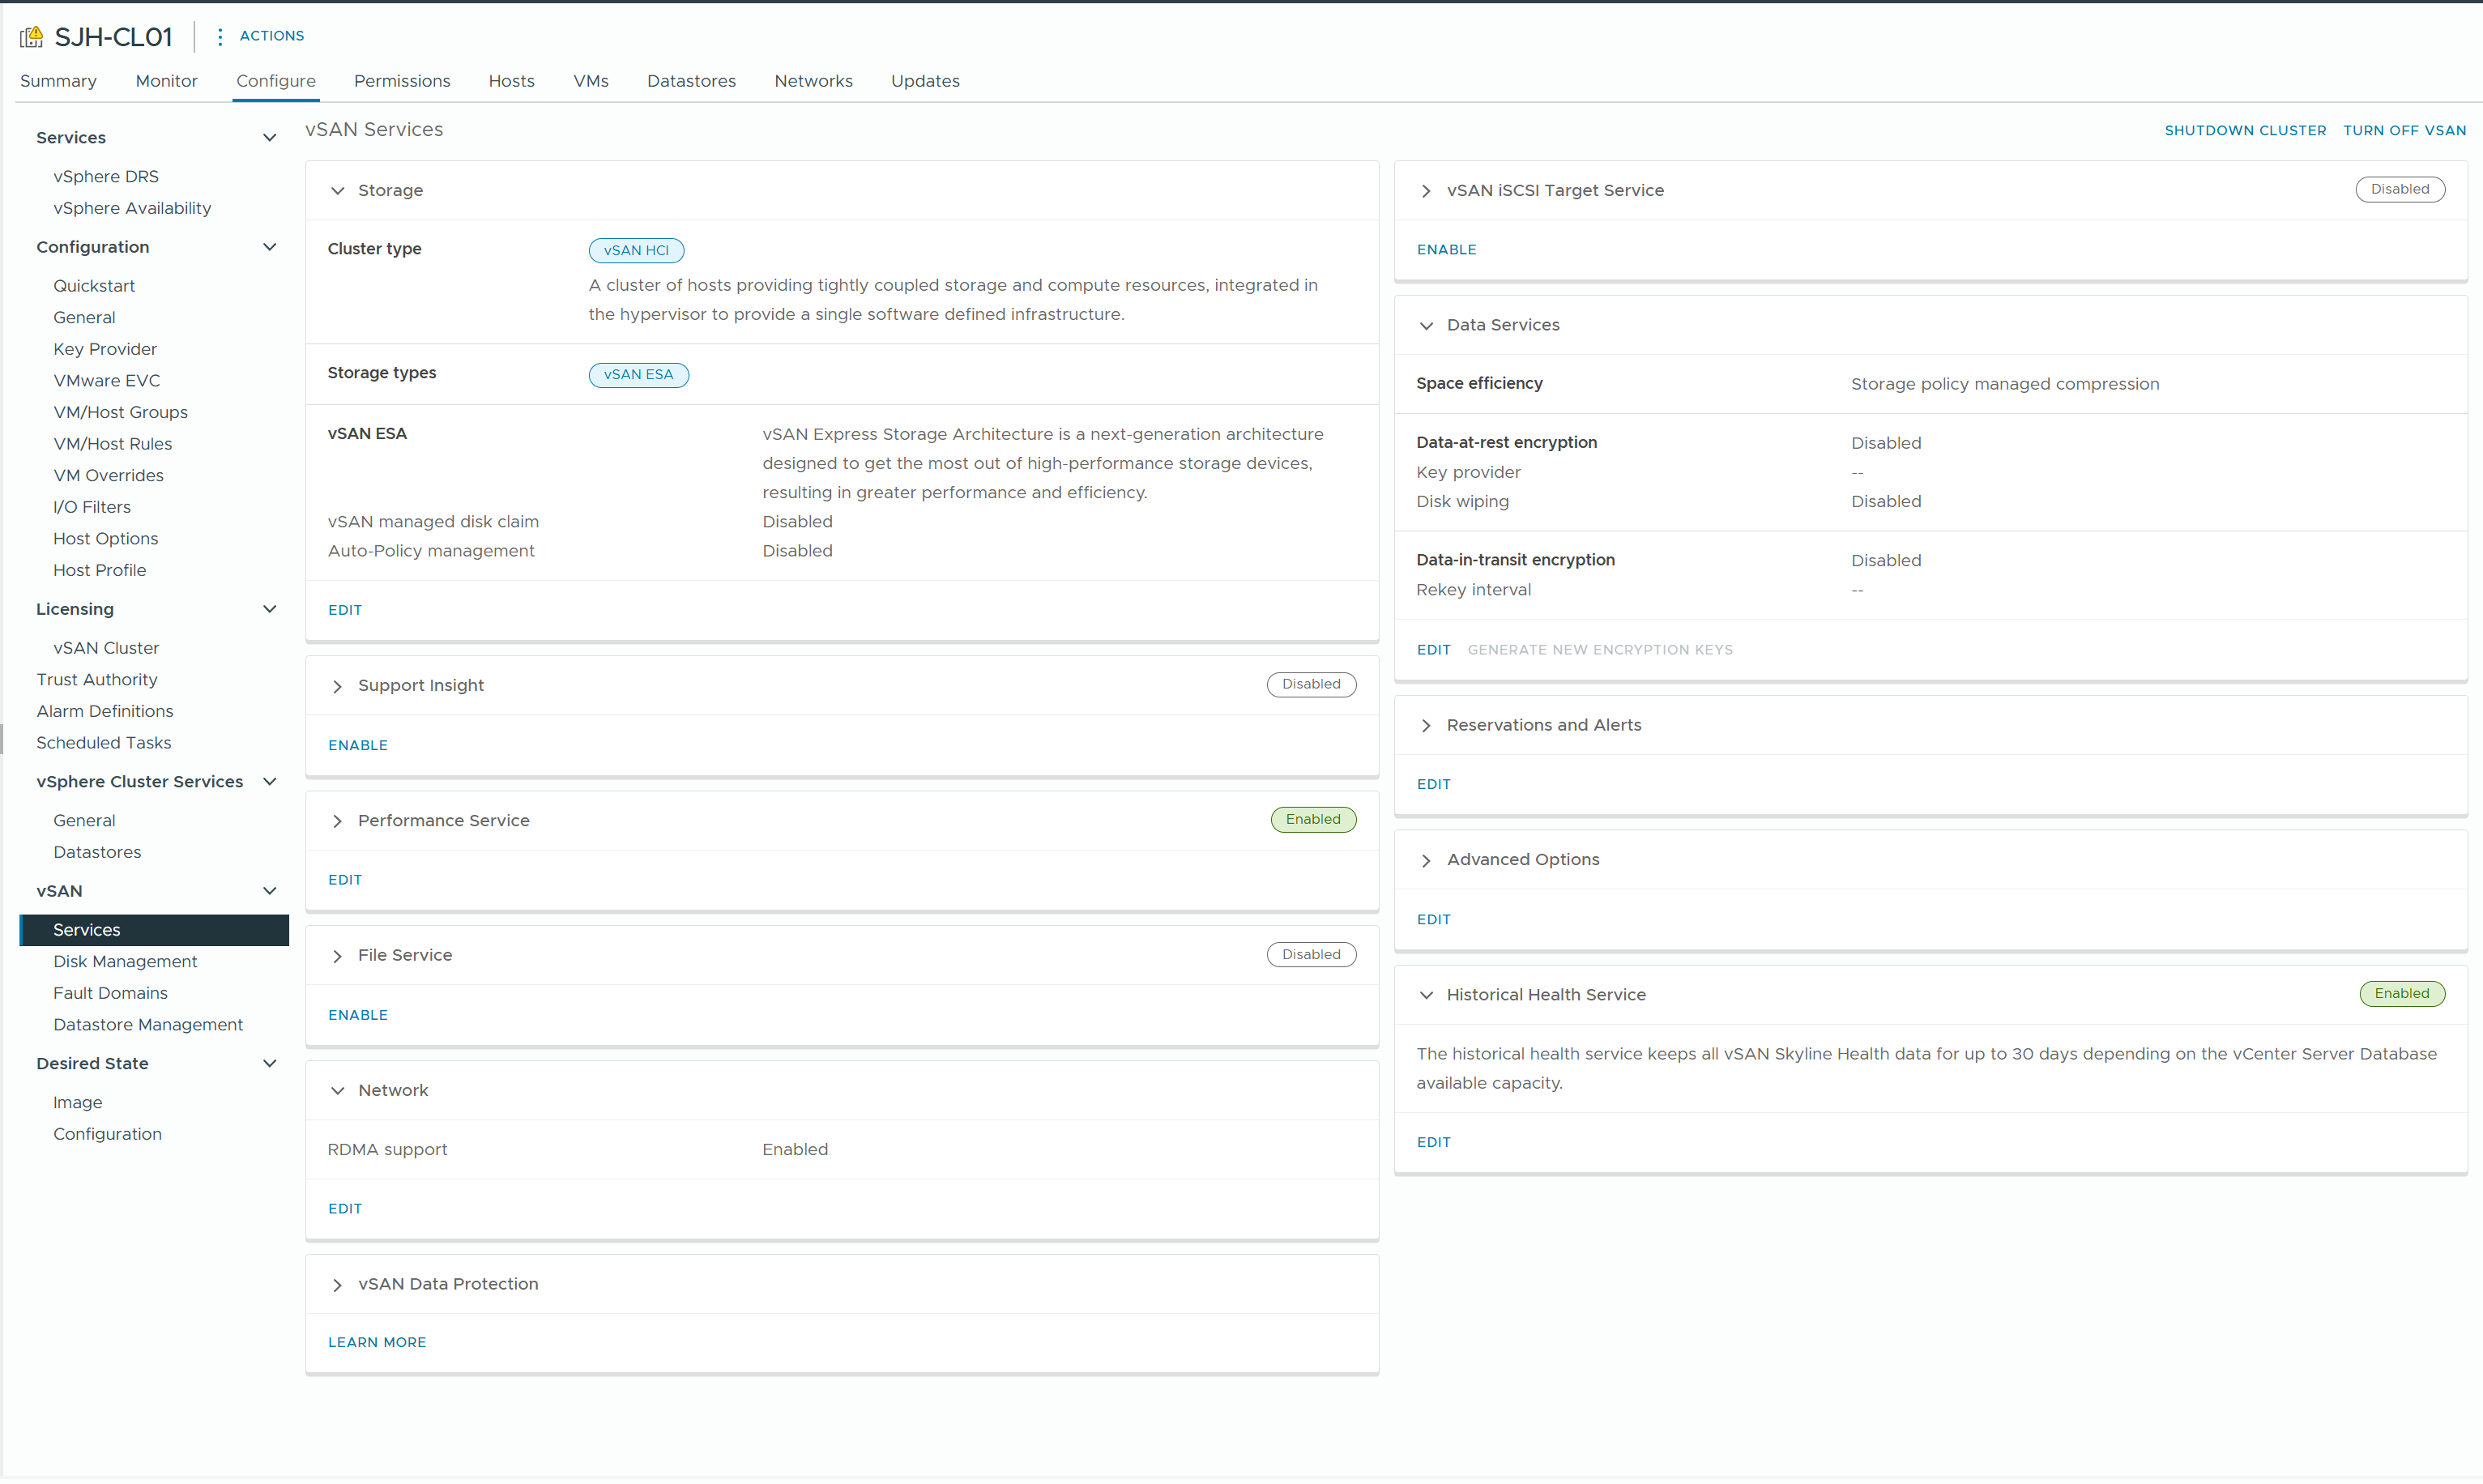
A step-by-step guide to configuring a vSAN ESA over RDMA cluster and a troubleshooting methodology.
The purpose of this website is to provide an overview of various Kubernetes networking components with a specific focus on exactly how they implement the required functionality.
The information here can be used for educational purposes, however, the main goal is to provide a single point of reference for designing, operating and troubleshooting cluster networking solutions.
Warning This is not a generic Kubernetes learning resource. The assumption is that the reader is already familiar with basic concepts and building blocks of a Kubernetes cluster – pods, deployments, services.
Whether you want to gather statistics, or you need to inspect more in depth what's going on in your network, Sniffnet will get you covered.
Should I block ICMP
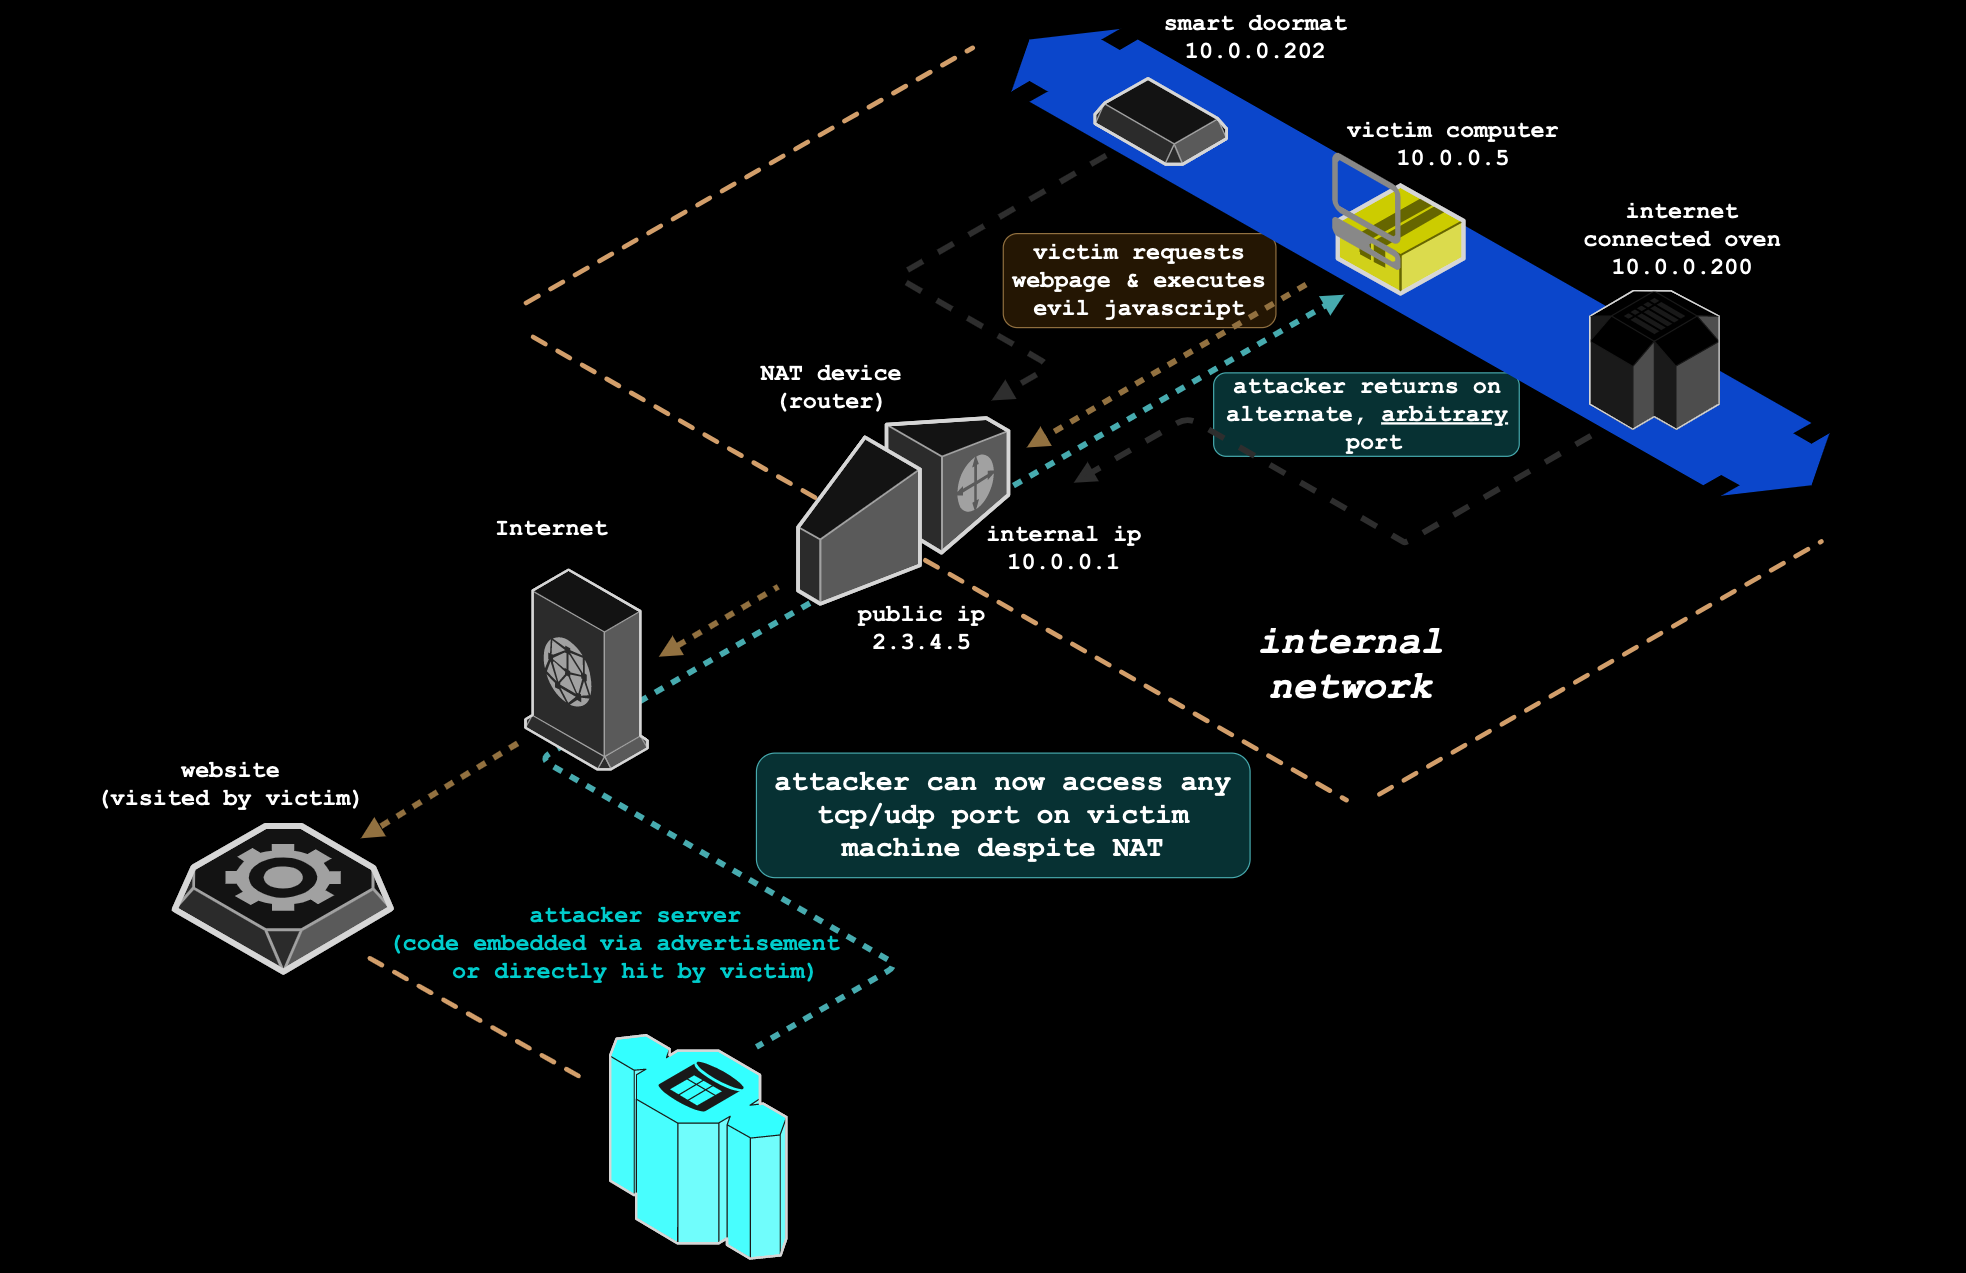
exploit NAT/firewalls to access TCP/UDP services bound to any system behind victim's NAT
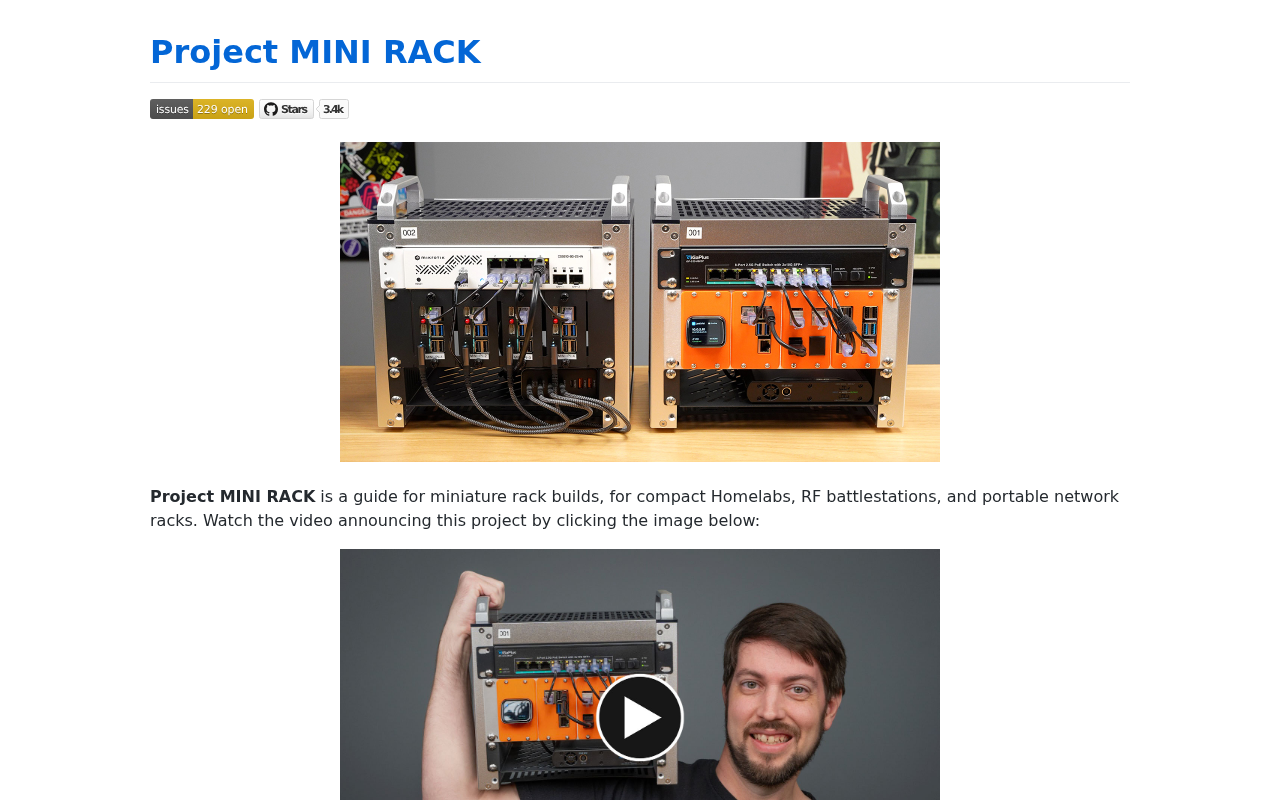
Miniature rack builds, for portable or compact Homelabs.
Network-wide Ad Blocking
We’re thrilled to announce the release of mitmproxy 12, introducingInteractive Contentviews!
It’s now possible to modify the prettified representation of binary protocols,
which is then re-encoded bac
This year I decided to refactor my personal cloud infrastructure. Because of various nuances in m...
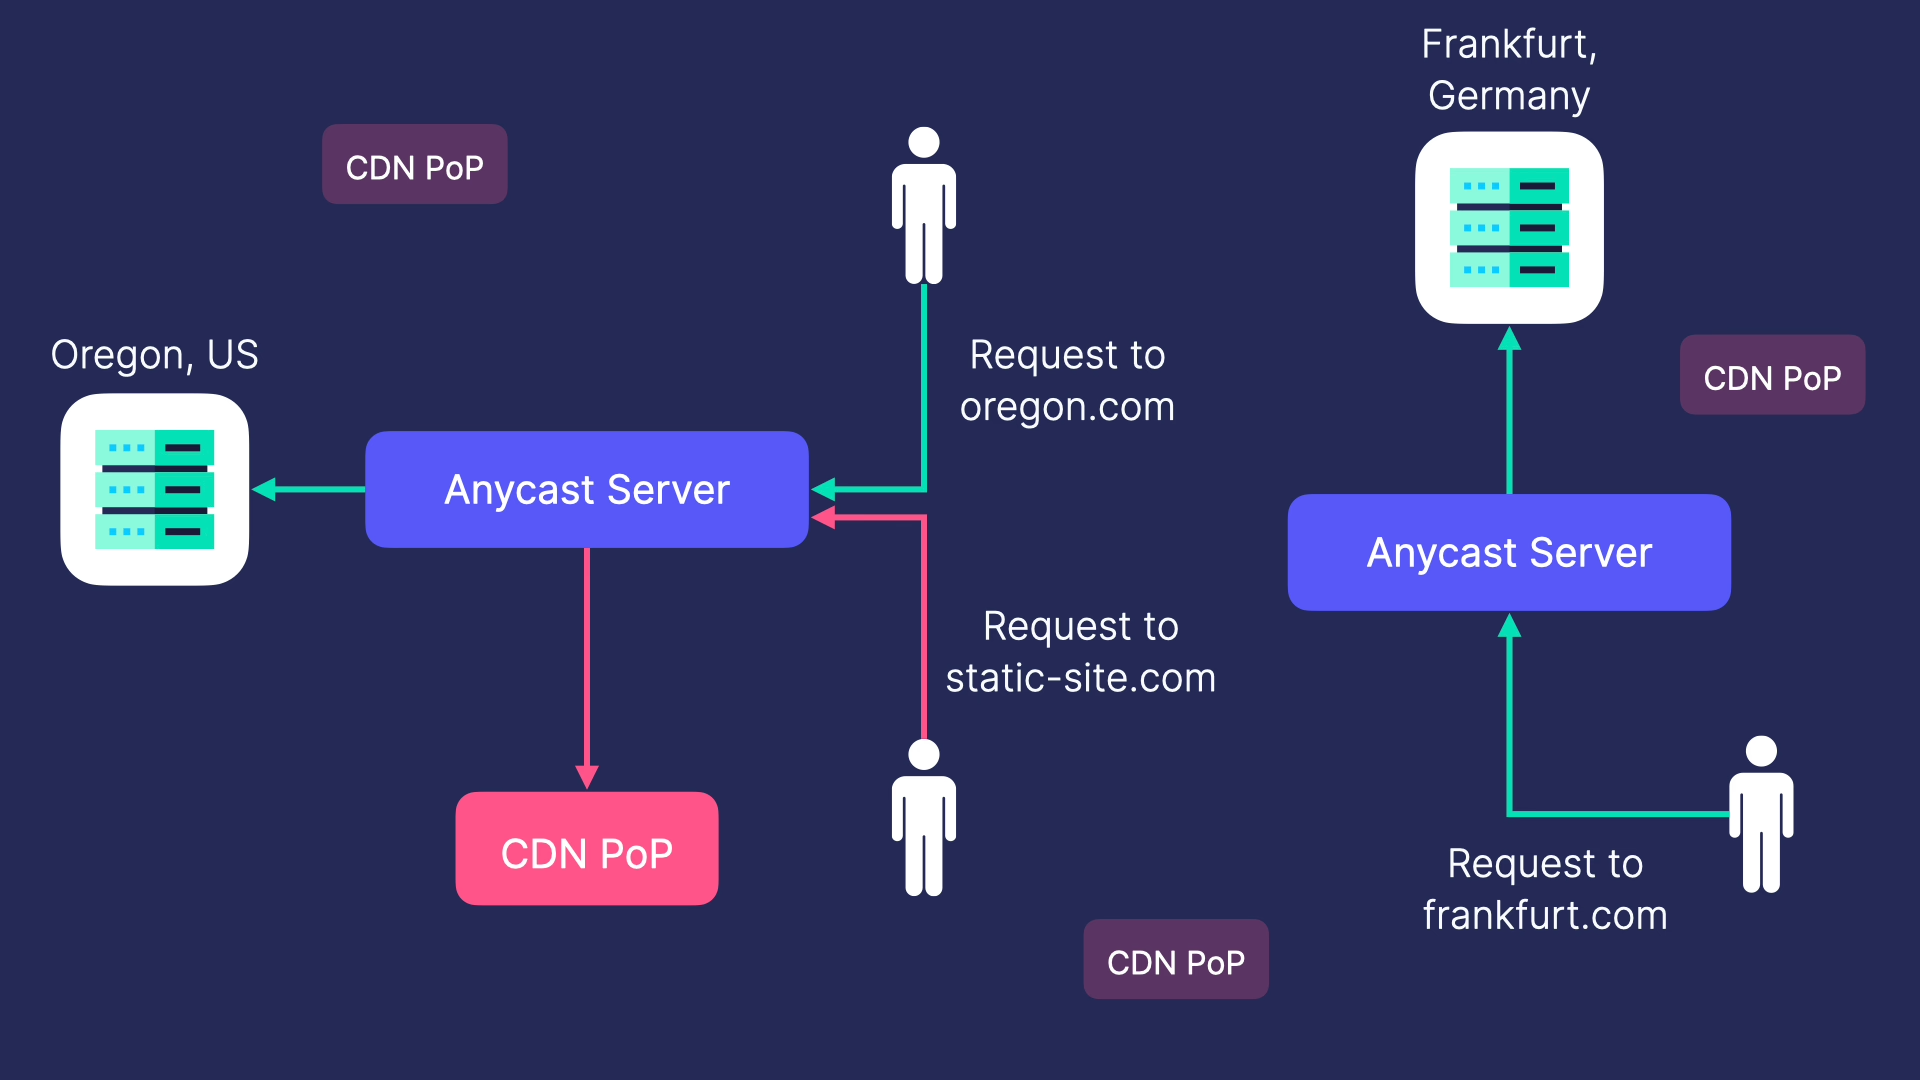
Learn how to build an Anycast network to optimize global traffic routing. Explore how to efficiently direct requests to the best server, regardless of location.
Interactive Streaming Telemetry lab with Nokia SR Linux nodes forming a Clos topology - srl-labs/srl-telemetry-lab
Automate deployment and configuration of nested VMware Software-Defined Data Center environments including solutions like vSphere, vSAN, NSX, vSphere Kubernetes Service, Avi Load Balancer, Aria Ope...
:dog: Command-line DNS Client for Humans. Written in Golang - mr-karan/doggo
Firezone is a fast, flexible VPN replacement built on WireGuard® that eliminates tedious configuration and integrates with your identity provider.
Discover how to design tailored multicloud connectivity scenarios with Megaport and Megaport Cloud Router (MCR). From physical layer configurations to cloud-specific connectivity options, explore resilient and scalable architectures that simplify network complexity. Gain insights into HA designs, dual data center strategies, and step-by-step guidance for building a better network.
you can control access between clients and databases through the use of NSX DFW rules
Introduction K8s is already a crucial part in the VMware ecosystem for many years and the level of integration in other products like NSX and AVI changed a lot in the past. That is also true for the naming like “vSphere with Tanzu”, “vSphere IaaS” and “VKS” and perhaps more changes in the future. For this blog post we will bring some spotlight to the integration for VKS with NSX VPCs, which is from my point of view a great enhancement from tenancy point of view.
A technical blog about Rust, Linux and other topics.
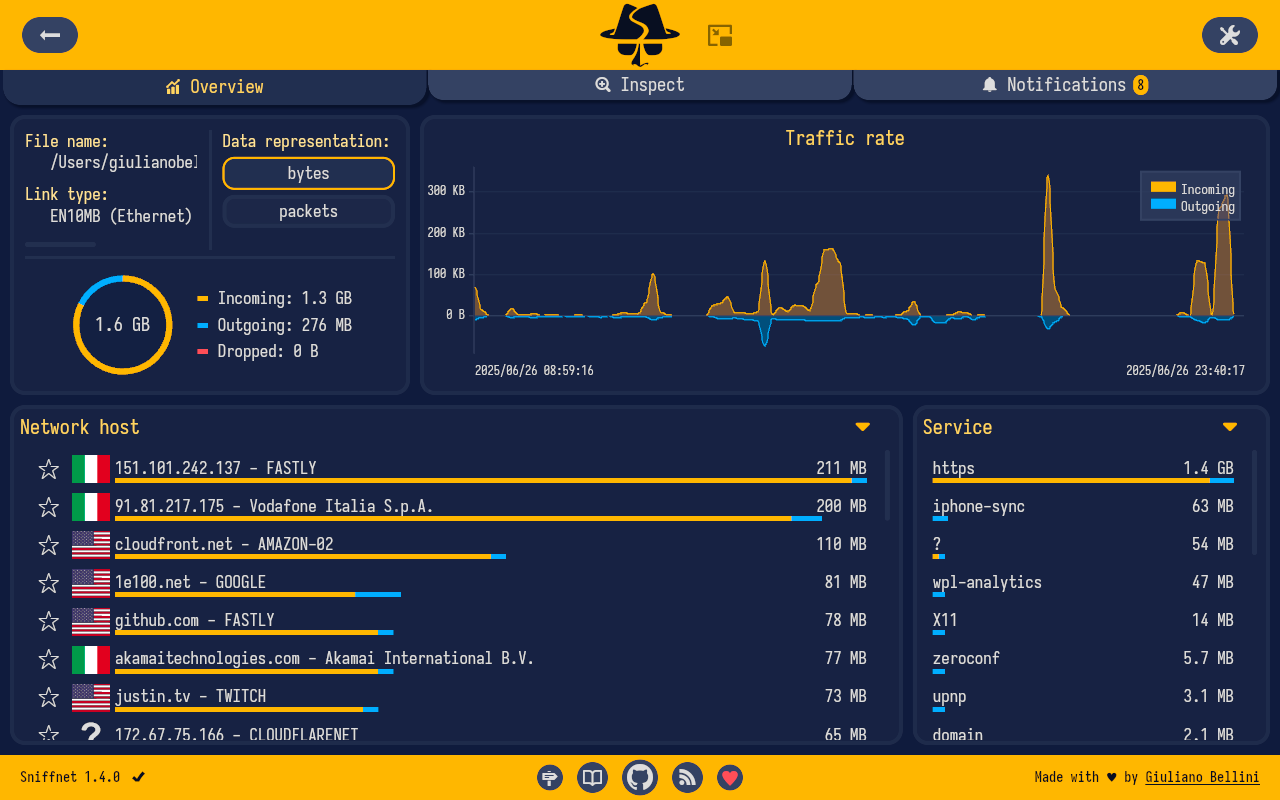
I’m delighted to announce that Sniffnet v1.4 is finally available! This major release brings a bunch of improvements and fixes, making Sniffnet more powerful and reliable than ever before. One of the most exciting new features is the ability to process network data from PCAP files in addition to network...
A short article about VPCs in NSX 9 and VCF 9 Part 2.
Published onJun 25, 2025
Dans cet article, j’expose 3 problèmes que j’ai rencontré dans ma carrière avec le DNS sur Kubernetes. Le 3eme est d’ailleurs un bug non corrigé à ce jour sur kube-proxy en mode iptables, et impacte n
Securely connect to anything on the internet with Tailscale. Built on WireGuard®️, Tailscale enables you to make finely configurable connections, secured end-to-end according to zero trust principles, between any resources on any infrastructure.
A short article about VPCs in NSX 9 and VCF 9.
The Situation I was working in our lab and ran into an issue where the hosts I wanted to use had different NIC configurations. I was building a cluster using two different types of hosts because on…
IPv4 is expensive, and moving network resources around is hard. Previously, when customers wanted to use multiple Cloudflare services, they had to bring a new address range. Now, they can use their resources more efficiently, saving space and reducing operational costs.

Lately I’ve been trying to find (and understand) the limits of time syncing between Linux systems. How accurate can you get? What does it take to get that? And what things can easily add measurable amounts of time error?
After most of a month (!), I’m starting to understand things. This is kind of a follow-on to a previous post, where I walked through my setup and goals, plus another post where I discussed time syncing in general. I’m trying to get the clocks on a bunch of Linux systems on my network synced as closely as possible so I can trust the timestamps on distributed tracing records that occur on different systems. My local network round-trip times are in the 20–30 microsecond (μs) range and I’d like clocks to be less than 1 RTT apart from each other. Ideally, they’d be within 1 μs, but 10 μs is fine.
It’s easy to fire up Chrony against a local GPSTechnically, GNSS, which covers multiple satellite-backed navigation systems, not just the US GPS system, but I’m going to keep saying “GPS” for short.
-backed time source and see it claim to be within X nanoseconds of GPS, but it’s tricky to figure out if Chrony is right or not. Especially once it’s claiming to be more accurate than the network’s round-trip time20 μs or so.
, the amount of time needed for a single CPU cache miss50-ish nanoseconds.
, or even the amount of time that light would take to span the gap between the server and the time source.About 5 ns per meter.
I’ve spent way too much time over the past month digging into time, and specifically the limits of what you can accomplish with Linux, Chrony, and GPS. I’ll walk through all of that here eventually, but let me spoil the conclusion and give some limits:
GPSes don’t return perfect time. I routinely see up to 200 ns differences between the 3 GPSes on my desk when viewing their output on an oscilloscope. The time gap between the 3 sources varies every second, and it’s rare to see all three within 20 ns of each other. Even the best GPS timing modules that I’ve seen list ~5 ns of jitter on their datasheets. I’d be surprised if you could get 3-5 GPS receivers to agree within 50 ns or so without careful management of consistent antenna cable length, etc. Even small amounts of network complexity can easily add 200-300 ns of systemic error to your measurements. Different NICs and their drivers vary widely on how good they are for sub-microsecond timing. From what I’ve seen, Intel E810 NICs are great, Intel X710s are very good, Mellanox ConnectX-5 are okay, Mellanox ConnectX-3 and ConnectX-4 are borderline, and everything from Realtek is questionable. A lot of Linux systems are terrible at low-latency work. There are a lot of causes for this, but one of the biggest is random “stalls” due to the system’s SMBIOS running to handle power management or other activities, and “pausing” the observable computer for hundreds of microseconds or longer. In general, there’s no good way to know if a given system (especially cheap systems) will be good or bad for timing without testing them. I have two cheap mini PC systems that have inexplicably bad time syncing behavior,1300-2000 ns.
and two others with inexplicably good time syncing20-50 ns
. Dedicated server hardware is generally more consistent. All in all, I’m able to sync clocks to within 500 ns or so on the bulk of the systems on my network. That’s good enough for my purposes, but it’s not as good as I’d expected to see.
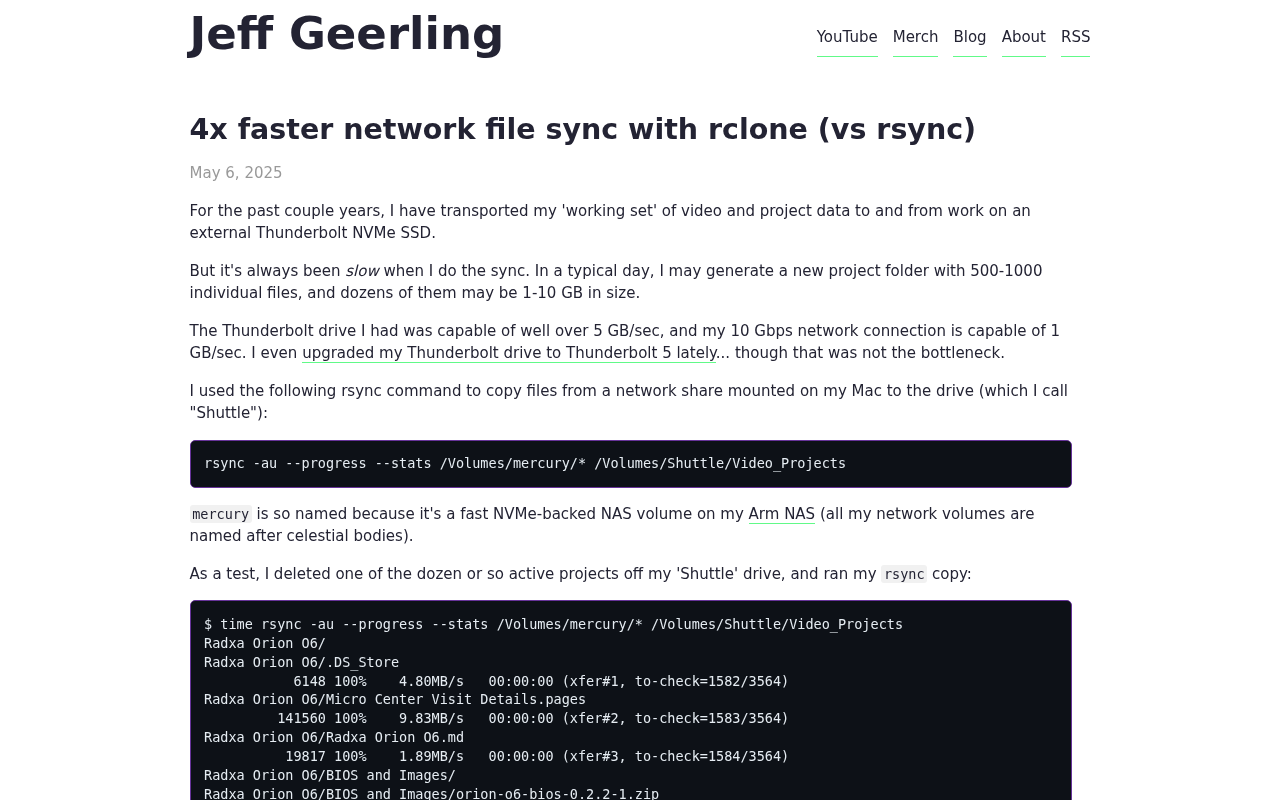
For the past couple years, I have transported my 'working set' of video and project data to and from work on an external Thunderbolt NVMe SSD.
But it's always been slow when I do the sync. In a typical day, I may generate a new project folder with 500-1000 individual files, and dozens of them may be 1-10 GB in size.
The Thunderbolt drive I had was capable of well over 5 GB/sec, and my 10 Gbps network connection is capable of 1 GB/sec. I even upgraded my Thunderbolt drive to Thunderbolt 5 lately... though that was not the bottleneck.
Tired of Annoying Ads and Privacy-Invading Trackers? Here’s How to Take Control...
I'm fortunate enough to live in a place where 10Gbps fiber (FTTH) is not only available but also cheap. Here's how I'm taking advantage of this.
Omni est un outil incroyable qui va vous permettre de gérer des machines Talos n'importe où. Laissez-moi vous présenter Omni, et comment l'interfacer avec Kubevirt pour créer des clusters Kubernetes en un claquement de doigts.
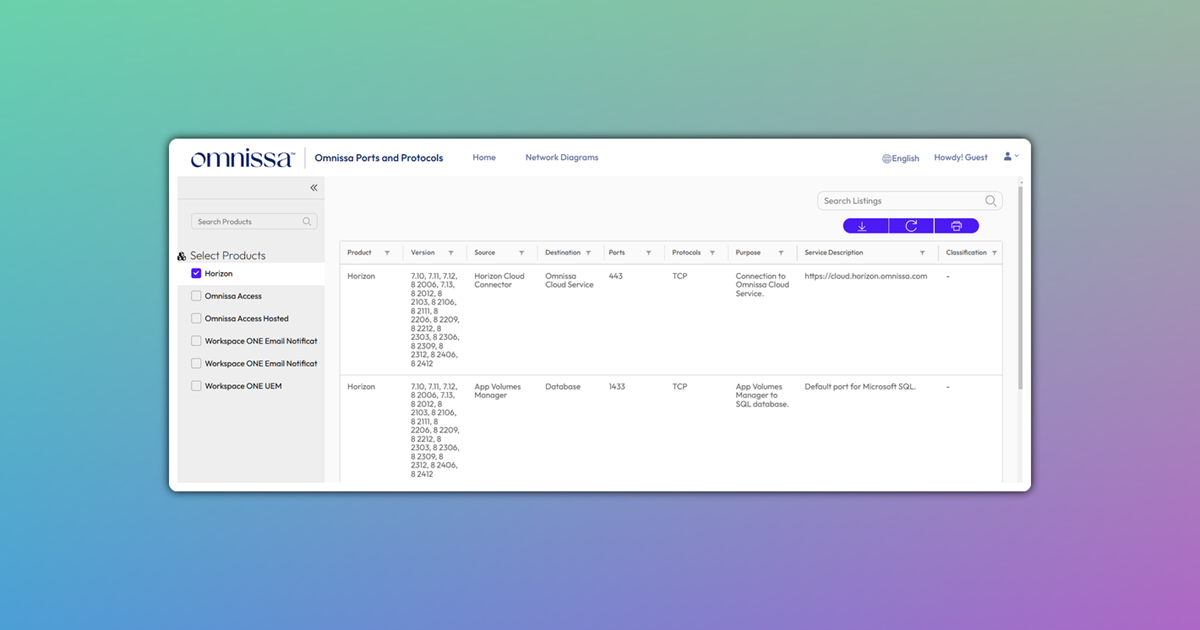
Omnissa recently released their Ports and Protocols tool! There are listings for Horizon1, Omnissa Access and UEM at present. Customized lists can be downloaded in Excel and PDF formats. I wanted to see if I could somehow find this information JSON-formatted. The Horizon listing also includes information for App Volumes, Dynamic Environment Manager and Unified Access Gateway. ↩︎
Explore essential homelab services for 2025 including Plex, Jellyfin, the *arr stack, Immich, Home Assistant, Pi-hole, Grafana, and more.
I want to write a post about Pitchfork, explaining where it comes from, why it is like it is, and how I see its future. But before I can get to that, I think I need to share my mental model on a few things, in this case, HTTP/2.
The article outlines how to automate the deployment and configuration of VMware NSX using Terraform, focusing on components like NSX Manager, Fabric, and Edge Transport Nodes. It details installati…
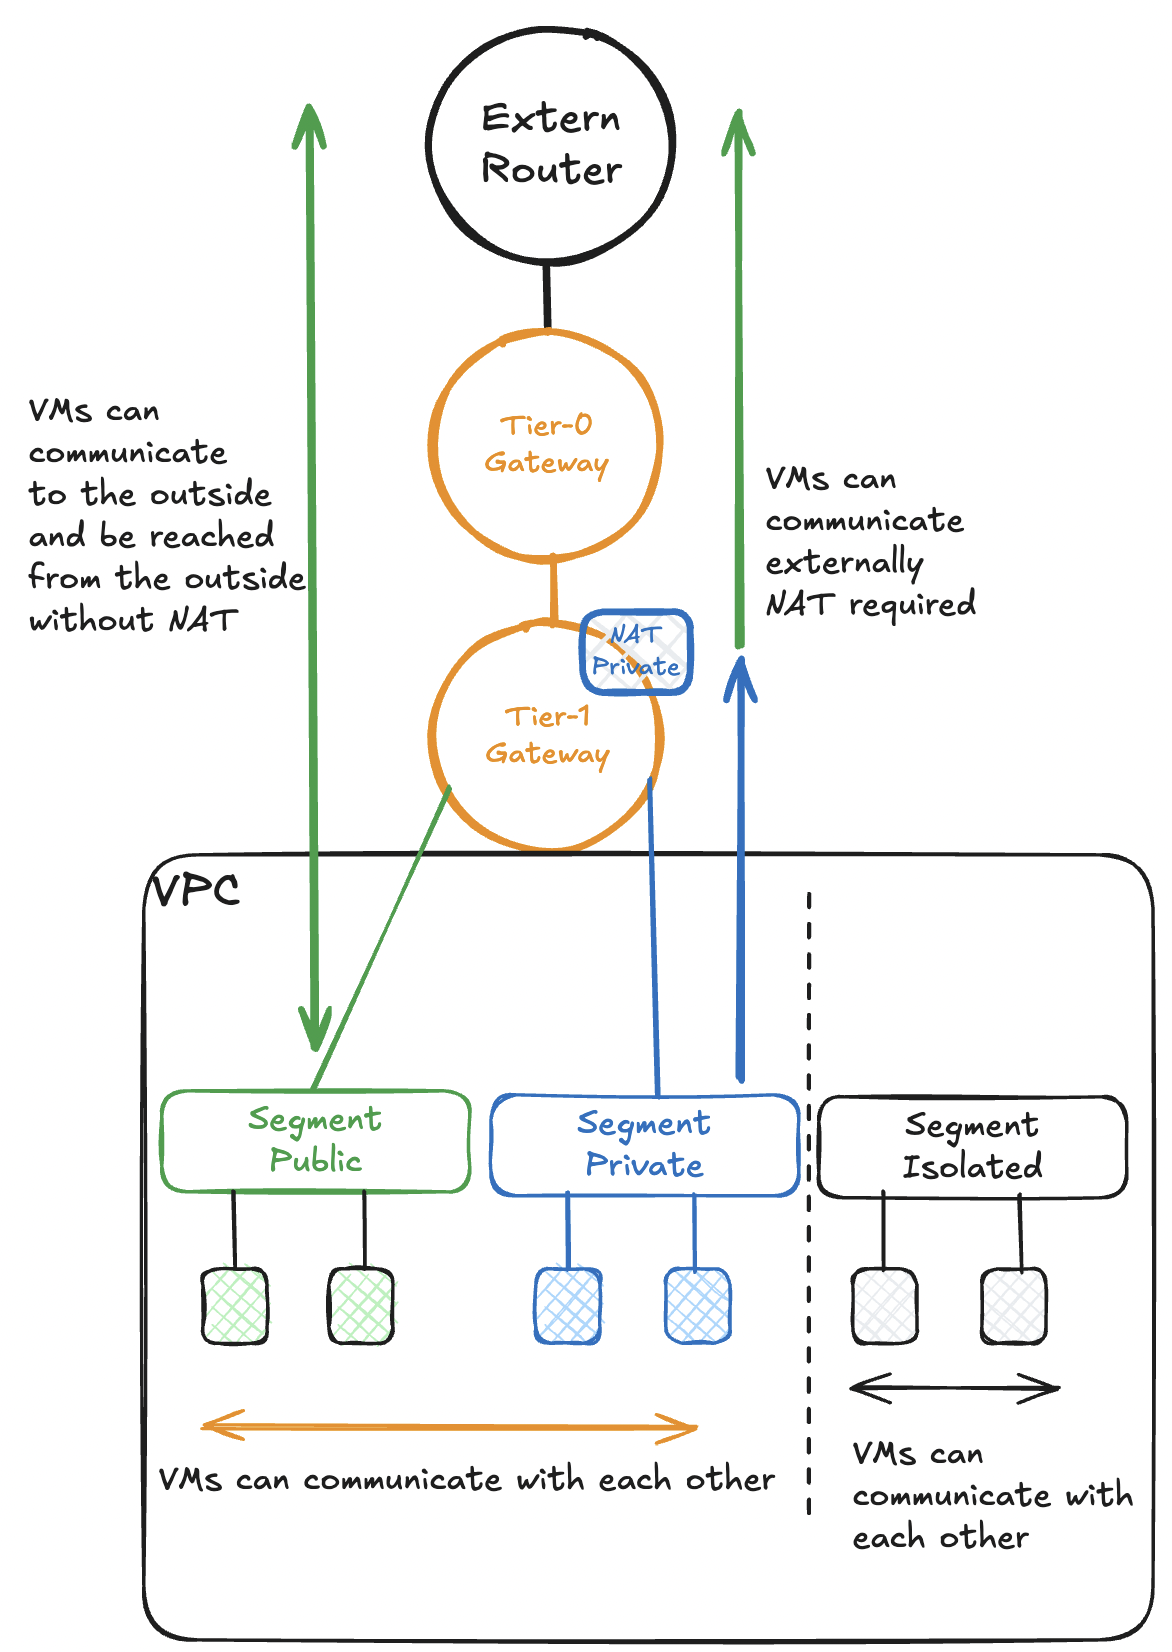
The introduction of VPCs (Virtual Private Cloud) at the network level provides a "self-service" for network, security and other network services in an isolated environment. Those responsible for the VPC can create networks and security rules (within their limits), thus relieving the burden on the network and security teams. It also enables the VPC owners to provide new services more quickly.
Live Migration of Workloads with VMware HCX: A Customer Story
Todays post is about configuring Jumbo frames in NSX for VM to VM communication (East / West) and for upstream connectivity (North / South). NSX supports switching and routing of Jumbo frames. We’re t
When it comes to infrastructure engineering, building a data center is probably closer to building a house than to deploying a Terraform stack.
Introduction Some of you are using NSX for many years already and are aware of the different changes and improvements implemented in the last years. I personally started with NSX in version 2.3 and one of the first important improvements I recognized is “MultiTEP” for edge nodes from type VM. It was released with NSX 2.5 and officially added to the reference design guide.
By the way: The reference design guide is still a great resource to learn the design pricipals for NSX implementaions. This is especially interesting for those who might be new to NSX.
Abstract Now that we have a Vault, with a TLS Issuing CA, and some idea of how to get certs out of it, lets look at how we can use this in a “real” world scenario to put a valid TLS profile onto a Network Appliance (fancy word for a switch I guess).
Why did I say appliance, and not Router or Switch? Weeeeeell, think about it. You manage a lot of network stuff over HTTPS protocols these days, even when its not actually a web interface you are using to do it.
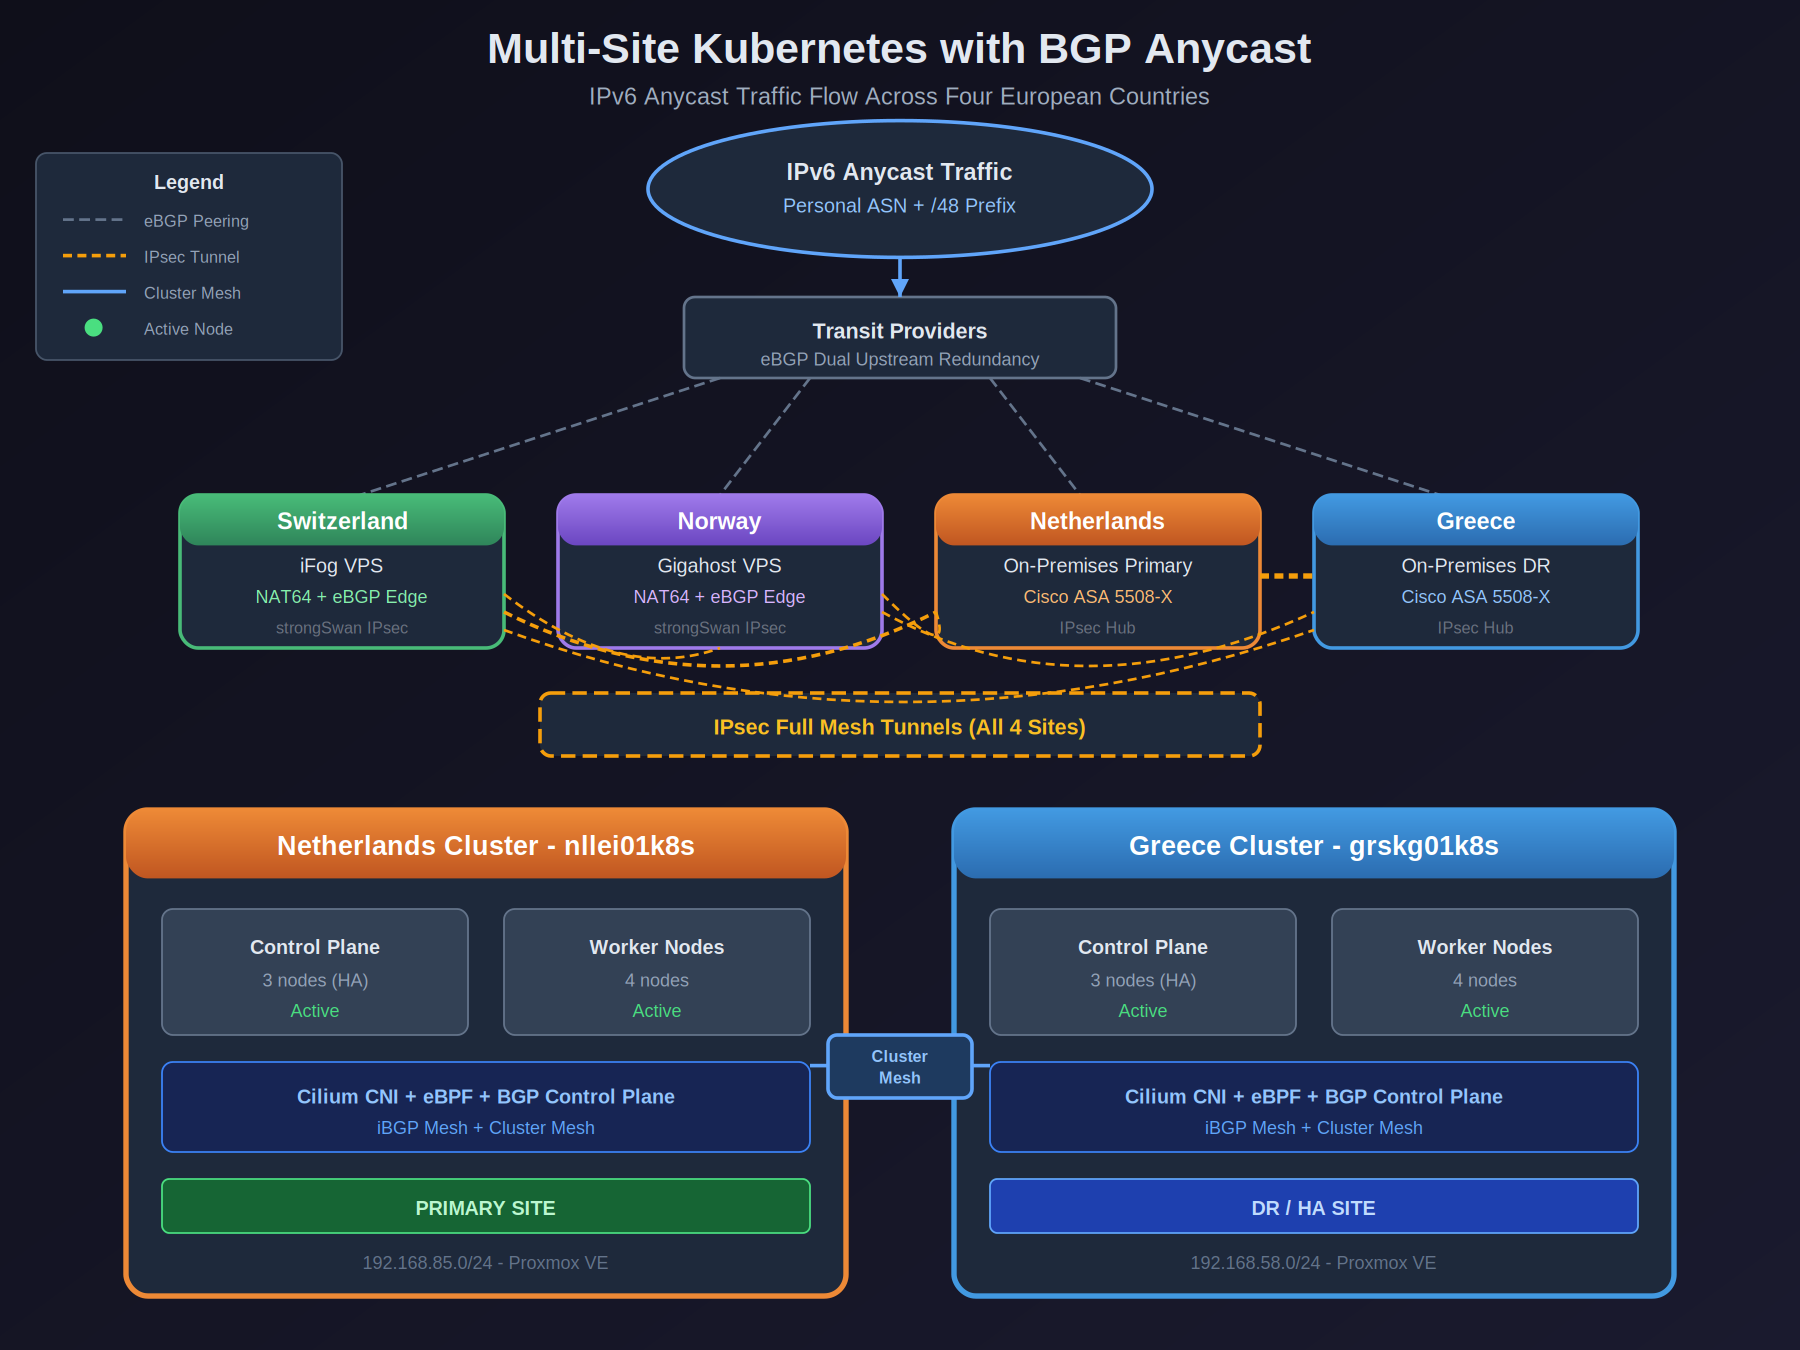
How I connected Kubernetes clusters across 4 countries with my own ASN, BGP peering, and perhaps too many IPsec tunnels
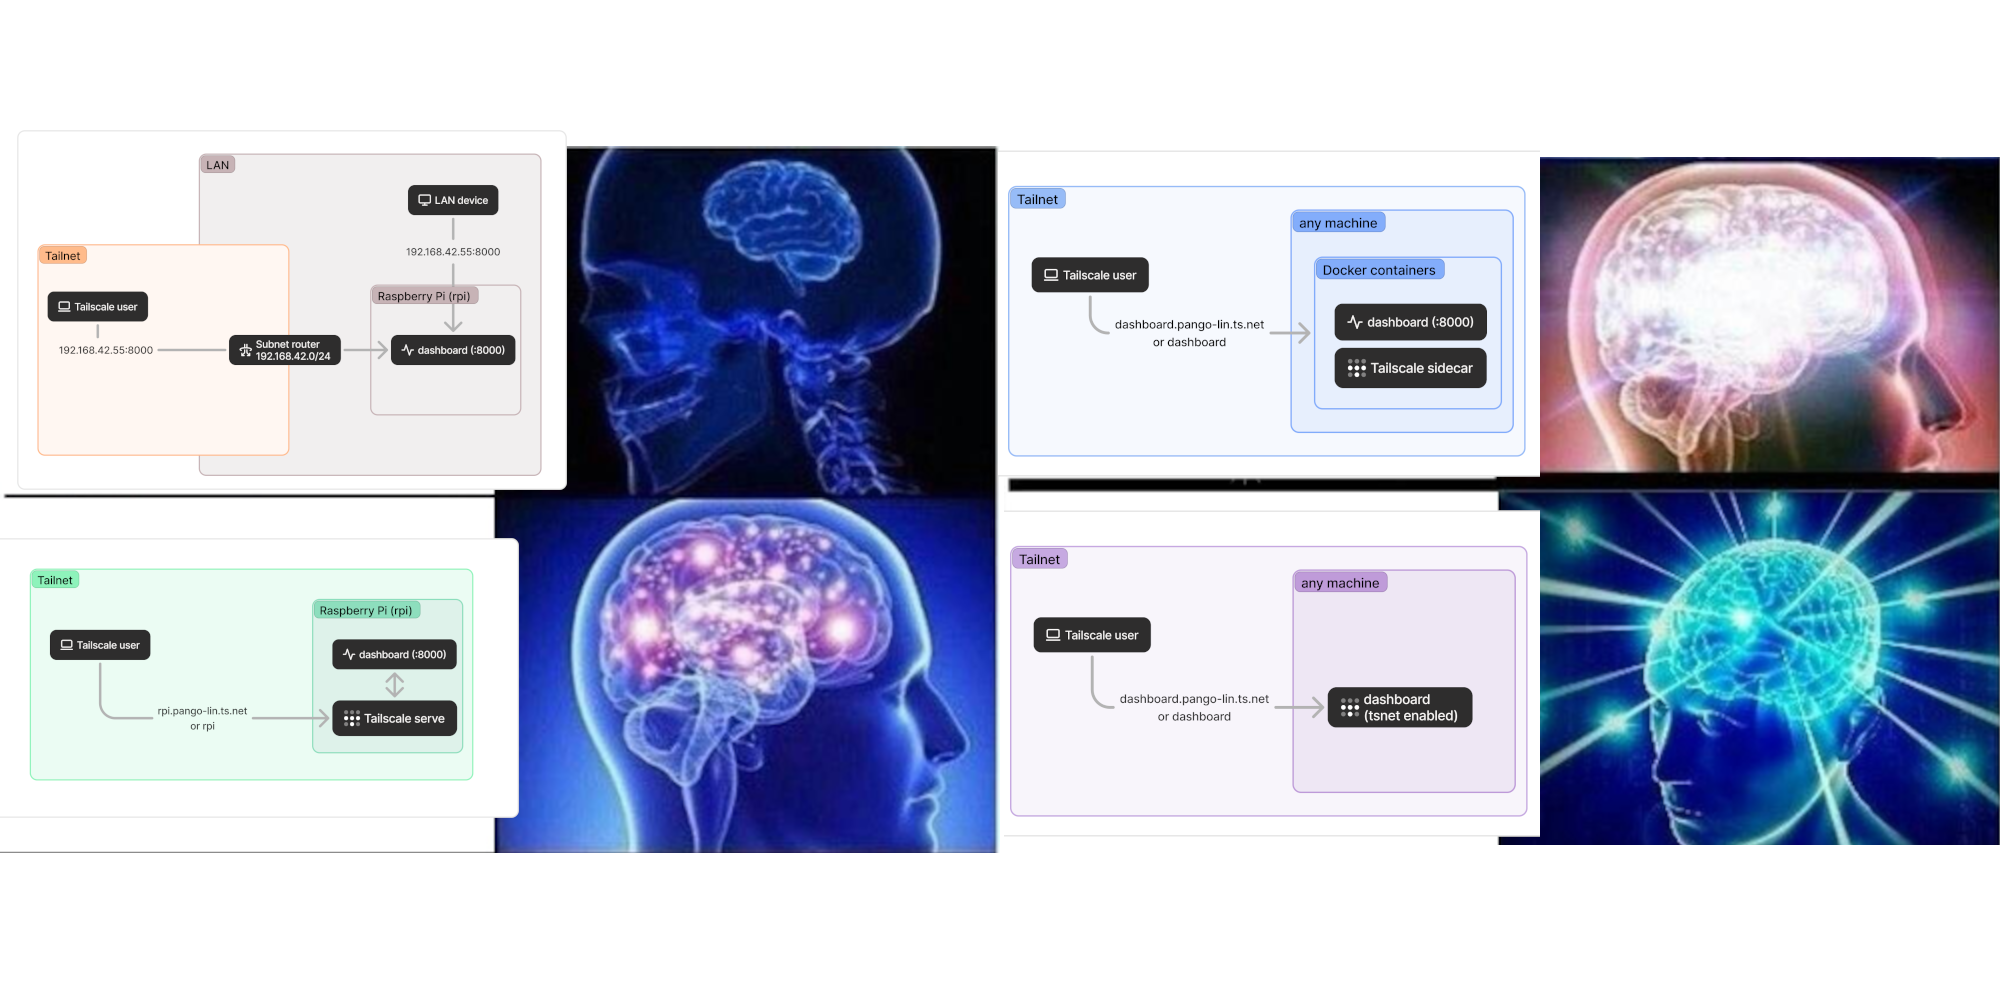
Let’s say you’ve got some kind of service you want to connect to through Tailscale. How do you make it accessible over your tailnet? It's easy for decision paralysis to set in here, so let's consolidate some of the possibilities in one place.
Why you should use MAC Learning
Mac's Tech Blog
Using Linux's fancy networking to keep torrent traffic private
In a previous post, I covered a method to automatically generate DNS zones from an embedded YAML list.
This wasn't the most useful on its own, only ensuring …
Deploying modern web apps – with all the provisions needed to be fast and secure while easily updateable – has become so hard that many developers don’t dare do it without a PaaS (platform-as-a-service). But that’s ridiculous. Nobody should have to pay orders of magnitude more for basic computing just to make deployment friendly and usable. That’s a job for open source, and Rails 8 is ready to solve it. So it’s with great pleasure that we are now ready with the final version of Rails 8.0, after a successful beta release and several release candidates!
You've been lied to. You don't need the cloud – you can just run servers and save 10x your AWS costs. It's not that difficult.
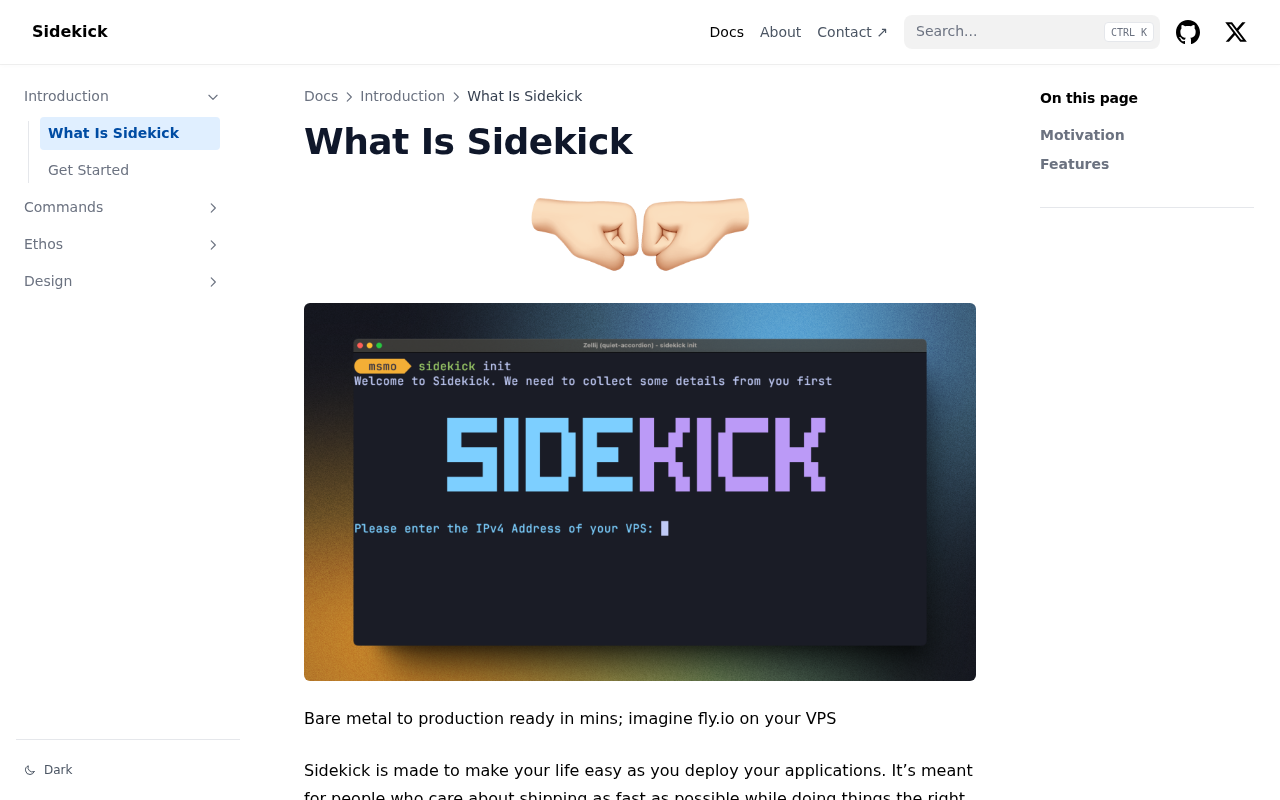
Bare metal to production ready in mins; imagine fly.io on your VPS
Sidekick is made to make your life easy as you deploy your applications. It’s meant for people who care about shipping as fast as possible while doing things the right way. Sidekick is designed to allow you to host multiple applications on a single VPS and take care of making them production ready. If you get enough traction, scale up your VPS and call it a day!
transhumanist and high functioning loser; instantiated simulation, statically stuck in superposition, calculated computationally complex, technomancer at will
Découvrons NATS de A à Y. Ensemble, nous développerons un projet à base de micro-services en Golang pour tester les particularités de NATS et fiabiliser les échanges entre nos applications.
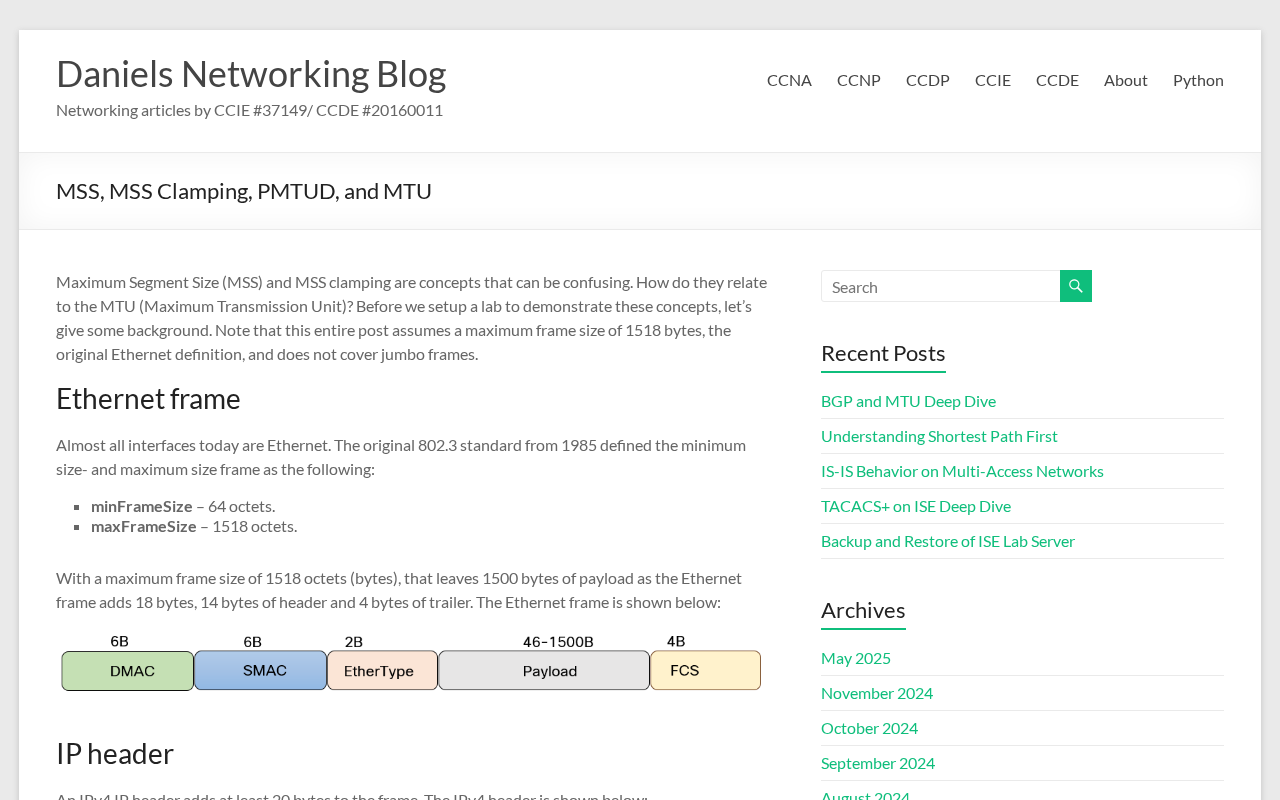
Networking articles by CCIE #37149/ CCDE #20160011
Extension du lab à l ecosystème Xen via XCP-ng et Xen Orchestrator. Installation des solutions et principes de base
After having automated the downloading of bundles for an offline depot in my lab I got the idea of experimenting with hosting it using a containerized nginx instance.
While I was testing the new Release 8.0.3 from Broadcom, I ran into a few problems getting my nested lab...
Last week I wanted to replace my OpenVPN setup with WireGuard. The basics were well-documented, going beyond the basics was a bit trickier. Let me teach you want I learned.
The basics But first, let’s summarize the basics. I have a server with a hosting provider that I want to use as a VPN server. I won’t delve into details here, since there are so many great explanations on the web already (here, here, here or here), let’s just make a quick summary of a simple setup, as a base for discussing the (slightly) more advanced usages I had to configure myself:
Créer une infrastructure VPN hybride avec Headscale pour connecter des serveurs locaux et distants.
Posted:2024-05-25

This video started as the answer to a simple question - how can I self-host a service for my friends and family, behind cgnat, without requiring them to install any apps (like tunnels)? This video turned into a bunch of different ways to proxy IPv4 to IPv6, so you can receive IPv6 traffic natively and bring in legacy traffic from a VPS which does have public IPv4.
While I’m giving you a lot of different examples and methods here, you can mix and match a lot of them to fit your needs.
Inmy previous postI showed how to install automatically a virtual machine with pfSense. The automation I reached was around 90%, as I didn’t know how to automate the installation of the software. Than
As someone familiar with VMware and vCenter, but coming reasonably fresh to Proxmox Virtual Edition (PVE) there are a number of important differences when …
Some time ago I bumped into a blog post from Rutger Blom about implementing EVPN integration between NSX-T and vYOS. As I was involved in my recent past with Arista in DC deployments, I was curious…
Learn why DNS needs security through tacos, crabs, and cryptographic laughs. How DNSSEC Works turns complex internet plumbing into an illustrated adventure.
J'utilise constamment des machines virtuelles pour tester des scripts, pour héberger des services, pour faire des tests de déploiement, etc. J'ai pour habitude d'utiliser Proxmox dans le cadre de mon lab, et Libvirt au travail.
Depuis peu, j'approfondis mes connaissances sur les clouds publiques comme AWS, GCP, Azure, etc. Et s'il y a bien une chose qui me fascine, c'est la vitesse à laquelle on peut créer une machine virtuelle.
Il m'arrive d'utiliser Cloud-Init pour automatiser la création de mes machines virtuelles ou Packer pour créer des templates de VM, mais nous parlons de quelques minutes (et non de secondes).
C'est en faisant mes recherches sur ce sujet que je suis tombé sur Firecracker, un projet open-source d'AWS qui permet de créer des microVMs en quelques millisecondes (oui oui, millisecondes). Alors, je veux pouvoir créer des machines virtuelles en quelques millisecondes, mais aussi pouvoir les détruire et les recréer à la volée. De ce fait, ces machines virtuelles pourront être utilisées pour des tests, pour des déploiements, pour des services, etc.
Sysadmin doing syadmin stuff
I want my services to be sturdy, cheap & easy to maintain. I want very few moving parts, and I treat the hardware as disposable and unreliable. Ansible allows me to achieve a lot at very little cost.

So Linux has adopted Persistent Device Naming, which is a really great thing for most systems. Unlike the old days where we just had eth0 and eth1 and eth2 etc (which at least has no spaces unlike Local Area Connection 6 that another OS uses), whose order depended on driver initialization in the kernel. Most people just had eth0 and were happy, and most people will still just have one Ethernet interface and will still be happy.
Mapping Pihole to Tailscale and enabling subnet routing has made accessing my homelab outside the house an absolute joy.
Consul Associate est une certification officielle de HashiCorp. Celle-ci permet de valider vos connaissances sur Consul via un examen en ligne. Je vous partage mon expérience dans cet article !
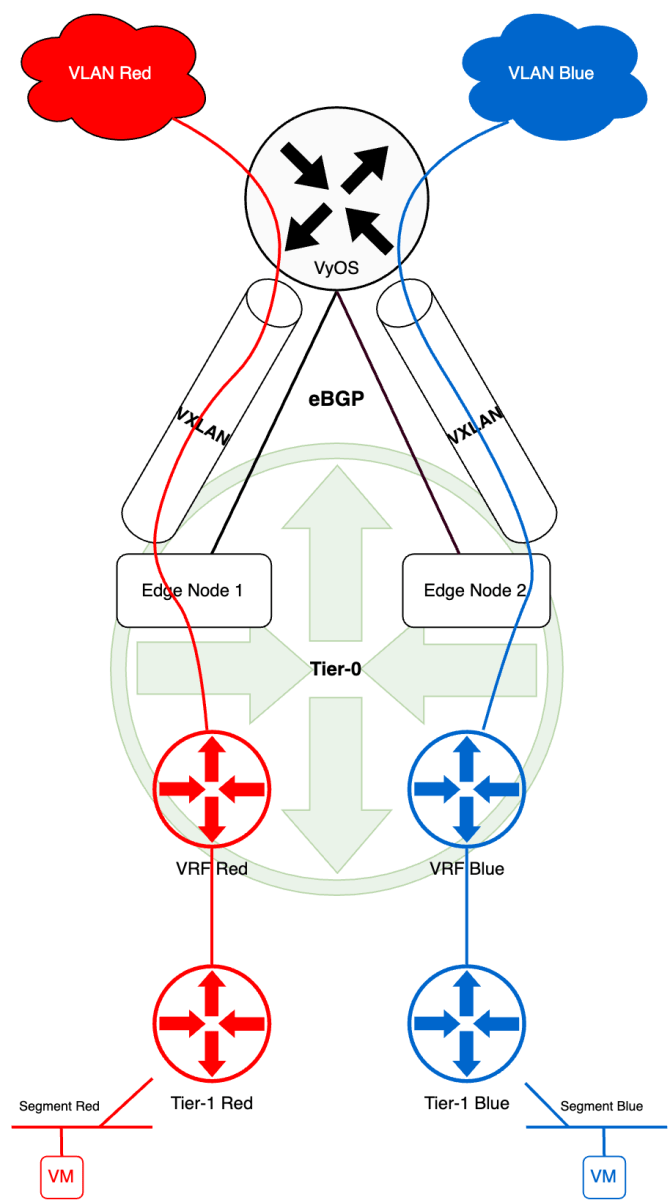
Recently I’ve been looking into setting up BGP EVPN between VMware NSX and VyOS router. I’m using VyOS quite a lot in labs and demos, often as the counterpart to a Tier-0 gateway, and w…
Consul est un outil permettant de gérer des micro-services, de la haute-disponibilité, mais aussi la sécurité et la communication entre les services. Cette page est condensé de ce que j'ai pu apprendre sur le sujet.
New talk: Learning DNS in 10 years
Everyone loves the Cluster API, but there are some cases where it's not the best solution. We chose not to build with it for several reasons.
Ce guide vous explique comment configurer un serveur DNS et DHCP en utilisant DNSMASQ. Il couvre l'installation, la configuration du DHCP et du DNS, ainsi que la gestion des baux statiques.
A next-generation sharing platform built on top of OpenZiti, a programmable zero-trust network overlay.
Lorsqu'on multiplie les infrastructures (locales, distante etc..), avoir un VPN de Mesh permet de vous faciliter la vie. Nous allons donc installer et configurer Tinc
Historically, we have rarely talked about how our servers fetch
the content from the Internet. In this blog we’re going to cover
this gap. We'll discuss how we manage Cloudflare IP addresses
used to retrieve the data from the Internet, how our egress
network design has evolved, how we optimized it for best use
of available IP space and introduce our soft-anycast technology.
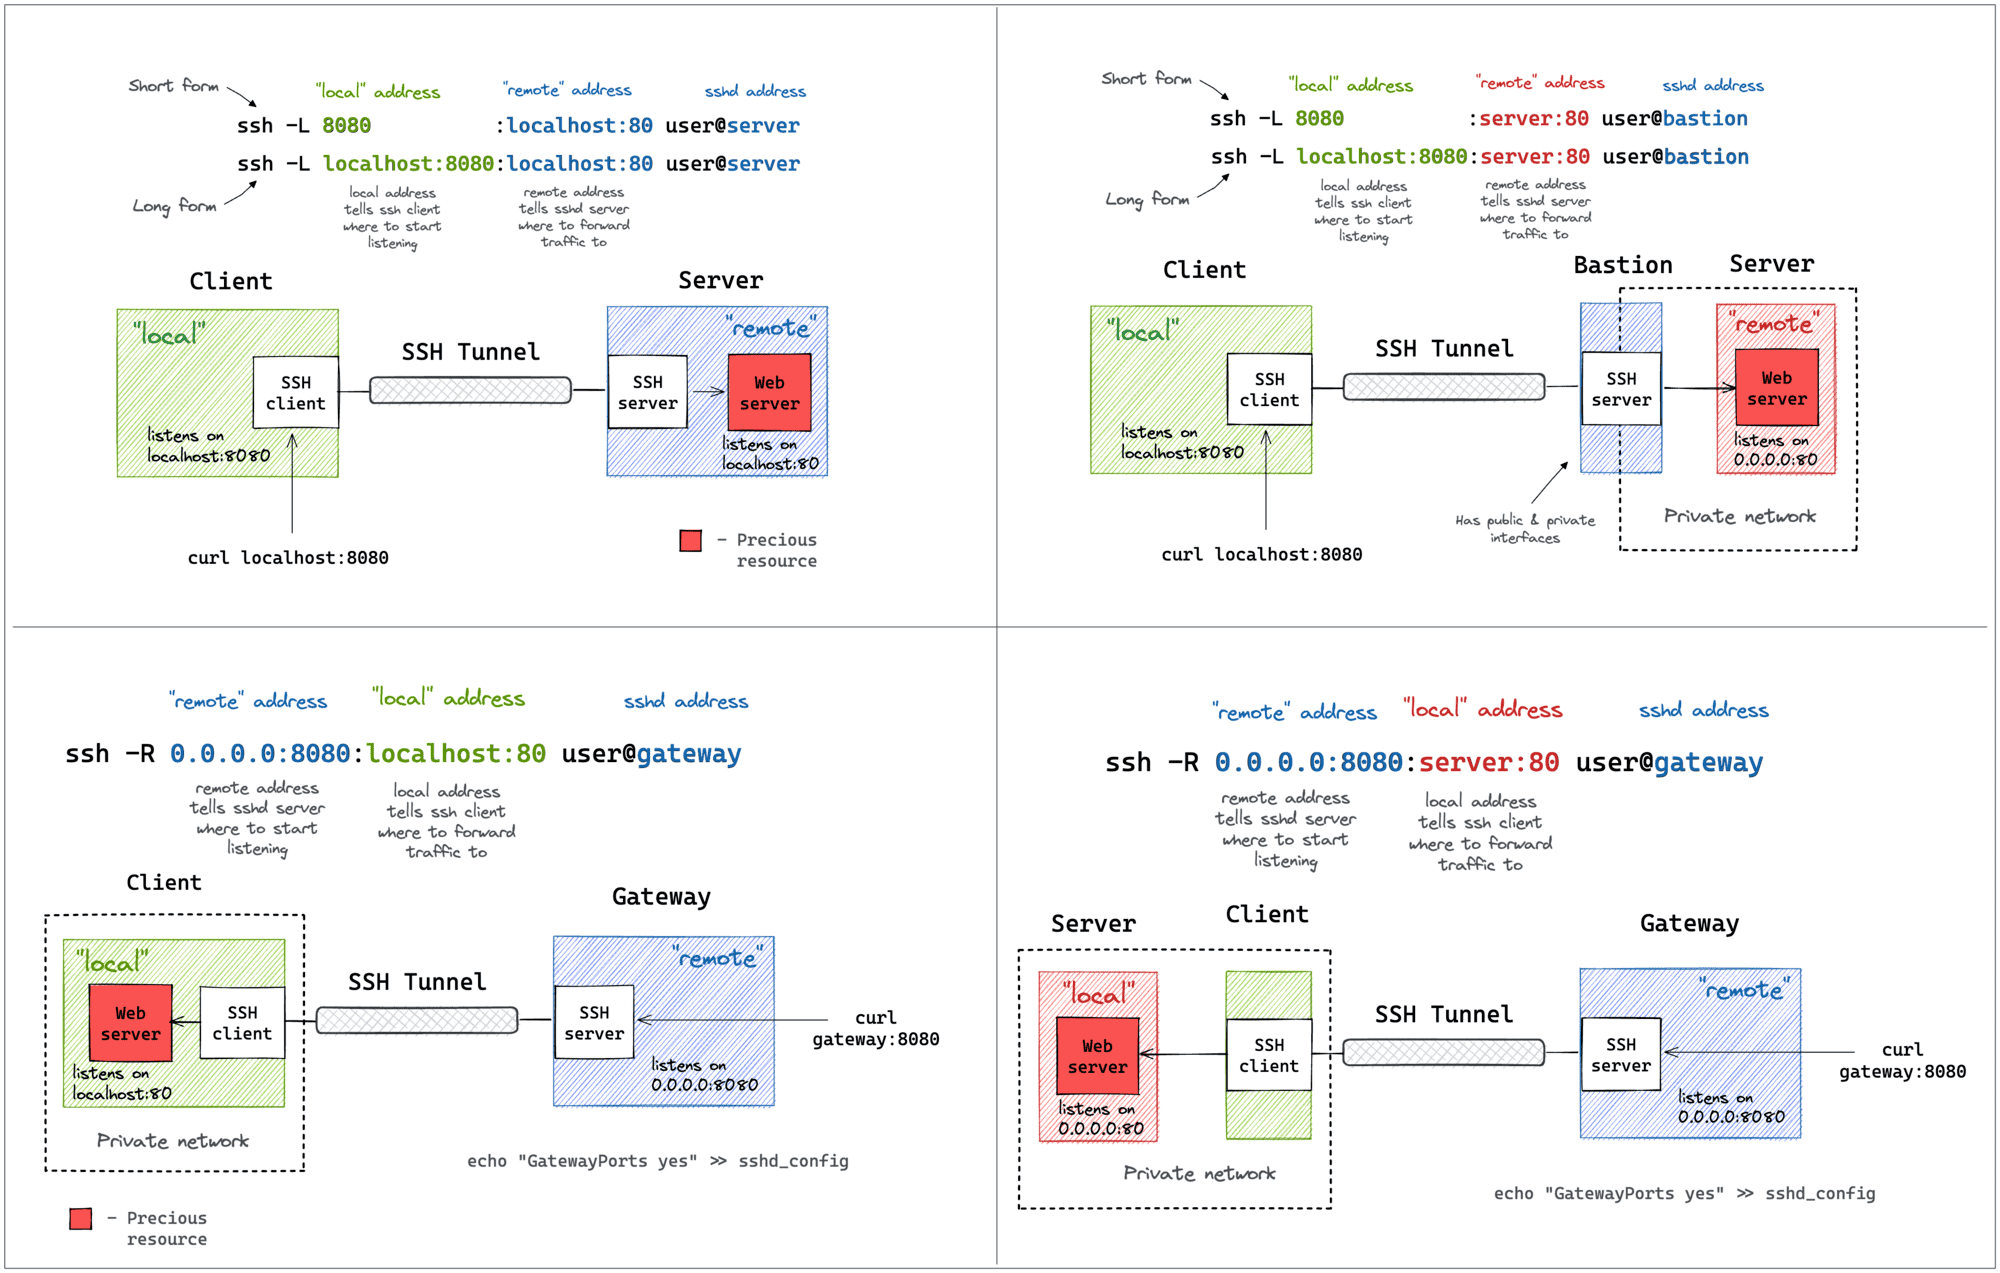
SSH port forwarding explained in a clean and visual way. How to use local and remote port forwarding. What sshd settings may need to be adjusted. How to memorize the right flags.
Learn all about network bonding in XCP-ng and some tricks to configure it.
The need I went into some troubles when I wanted to implement NSXT rules. My aim was to keep the order of the rules as intended by the user when he wrote his data without asking him to enter a rule ID manually. If the order is kept then it’s easy to prioritize the rules according to their placement. With the NSX-T Terraform provider the rules are in the form below :
Thus far, this series of posts have all been about Layer 2 over Layer 3 models; the customer ethernet frames encapsulated in UDP, traversing L3 networks. The routing has been confined underlay, the customer traffic has stayed within the same network.
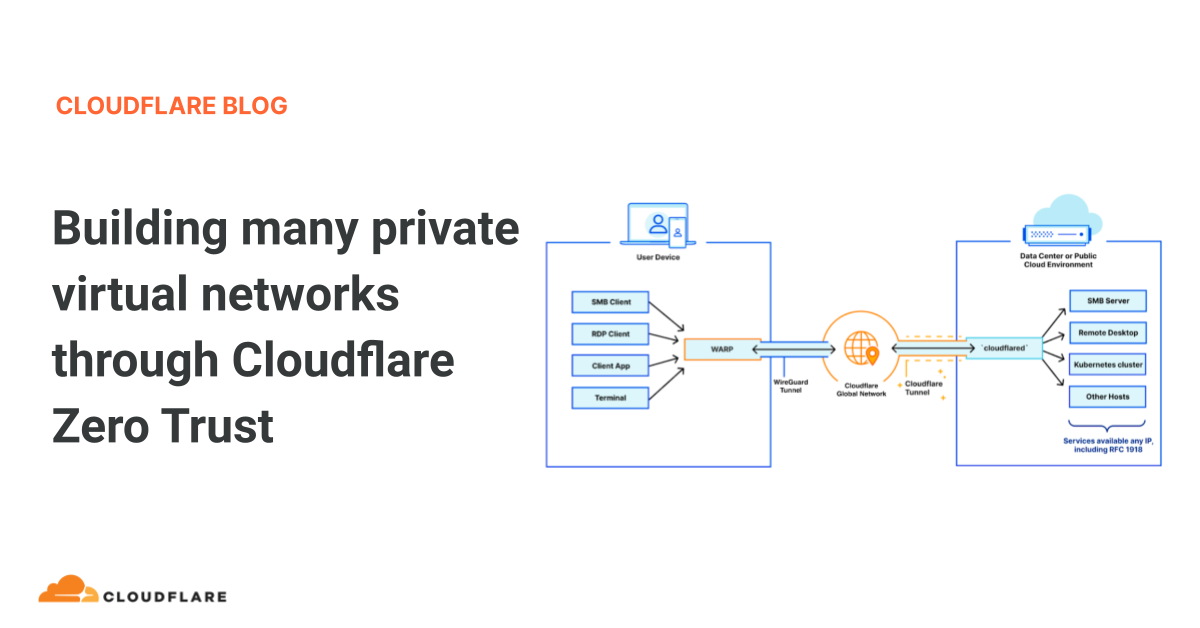
Starting today, we are thrilled to announce that you can start building many segregated virtual private networks over Cloudflare Zero Trust, beginning with virtualized connectivity for the connectors Cloudflare WARP and Cloudflare Tunnel
Whiletroubleshooting of a failed SDDC Manager deploy taskin Cloud Foundation 4.4 together with VMware support, the engineer showed a way to update the SDDC bring-up parameters. This can be very helpfu
A technical dive into traditional TCP proxying over HTTP
Traefik est un reverse-proxy qui se démarque des autres par son systeme de provider et de middleware. Il ne réinvente pas la roue, mais il est particulièrement efficace lorsque l'on a un grand nombre de redirections à paramétrer ou que nous avons des règles qui changent régulièrement.
Learn how packets flow inside and outside a Kubernetes cluster. Starting from the initial web request and down to the container hosting the application
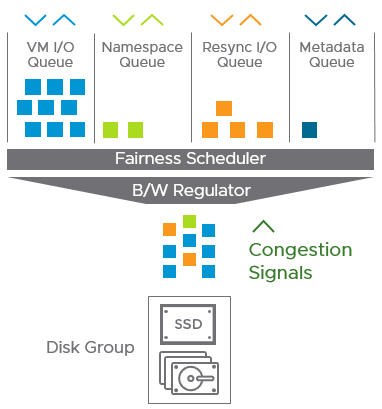
Delivering consistent performance while maintaining data resiliency is a key tenet behind enterprise storage solutions. VMware vSAN is the industry leading distributed storage system built right into VMware vSphere, and is designed to offer the highest level of resiliency and performance, with the maximum amount of agility should hardware faults occur, or demands of the … Continued
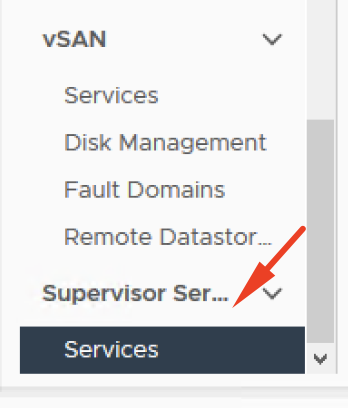
In this blog post, I will help you with the set of steps needed to enable MinIO service on a “vSphere with Tanzu” Supervisor cluster. I will not explain about MinIO, feel free to read about MinIO o…
Today at 1651 UTC, we opened an internal incident entitled "Facebook DNS lookup returning SERVFAIL" because we were worried that something was wrong with our DNS resolver 1.1.1.1. But as we were about to post on our public status page we realized something else more serious was going on.
Lorsqu'il s'agit d'initialiser une machine virtuelle dans une infrastructure VMWare vSphere, les systèmes Linux sont le parent pauvre....
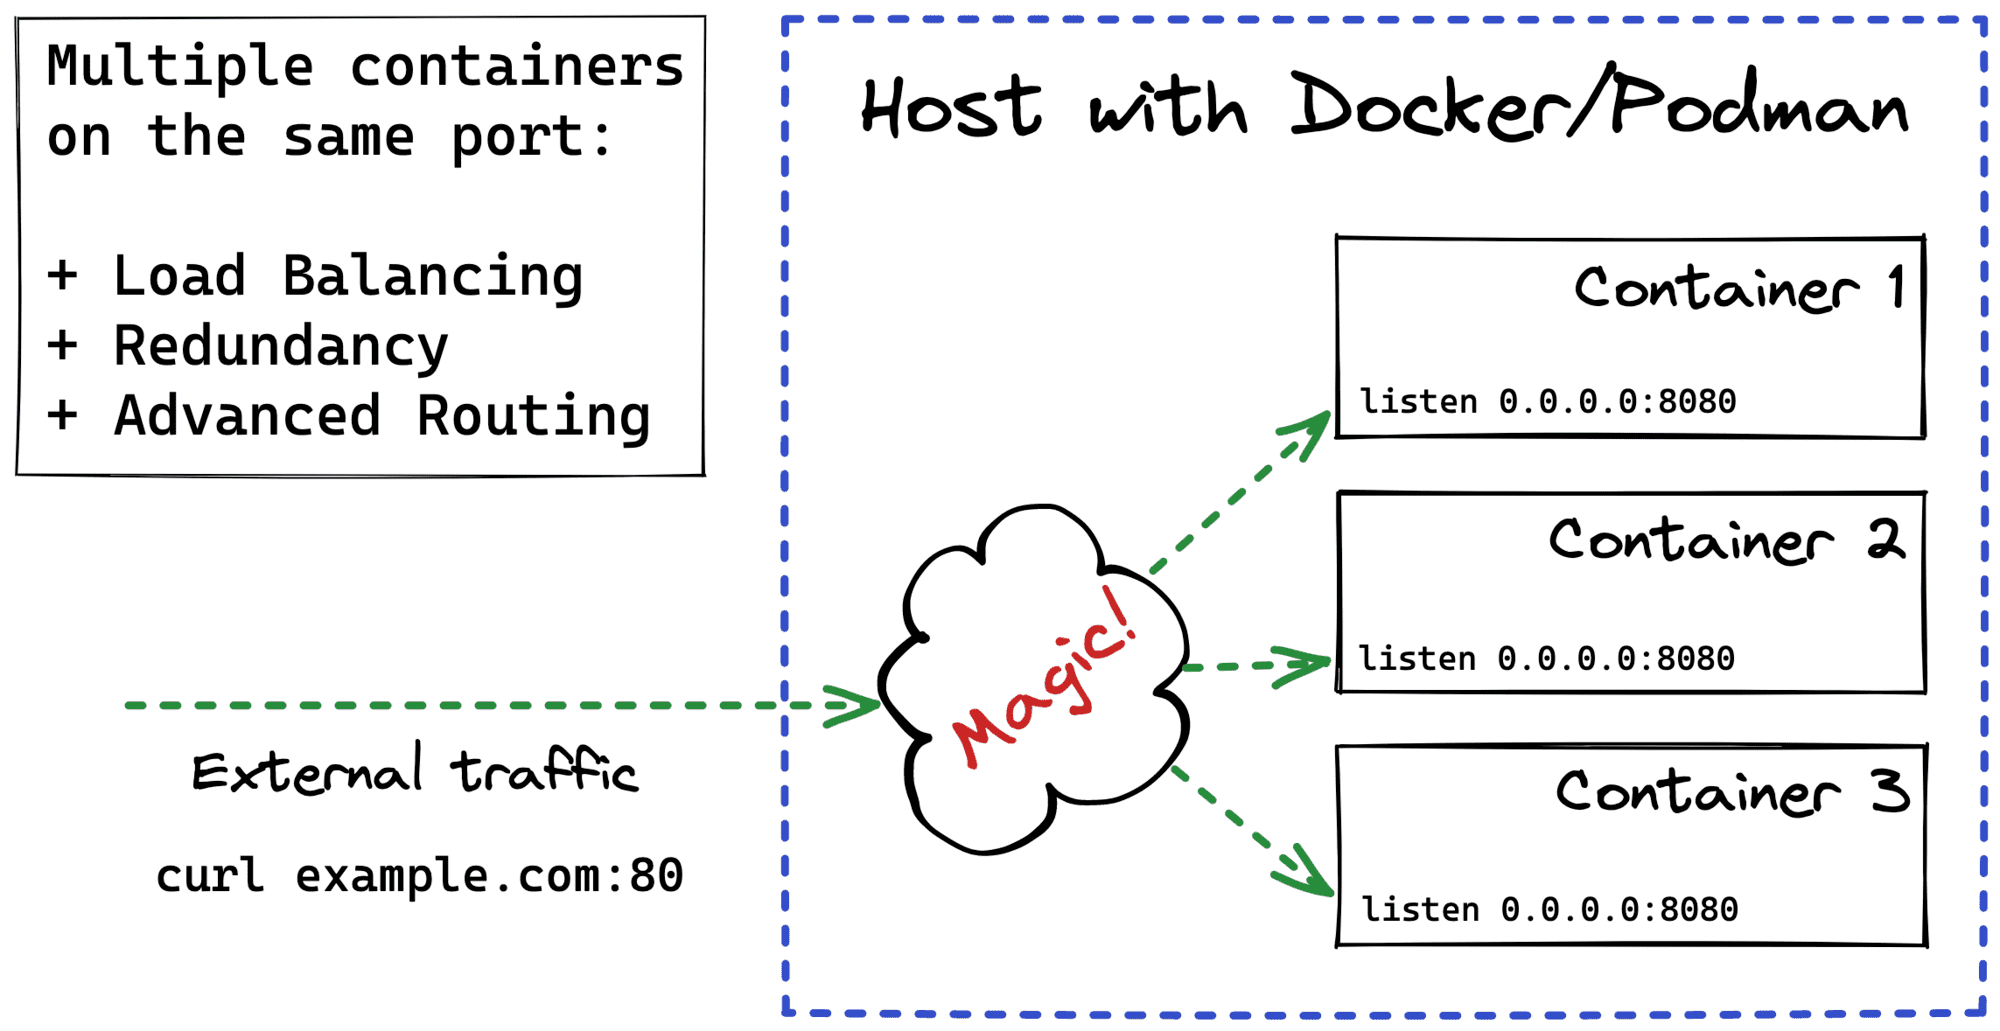
How Docker publishes container ports on the host? How to use SO_REUSEPORT to make multiple containers listening on the same port? How to use iptables to make multiple containers exposed on the same port?
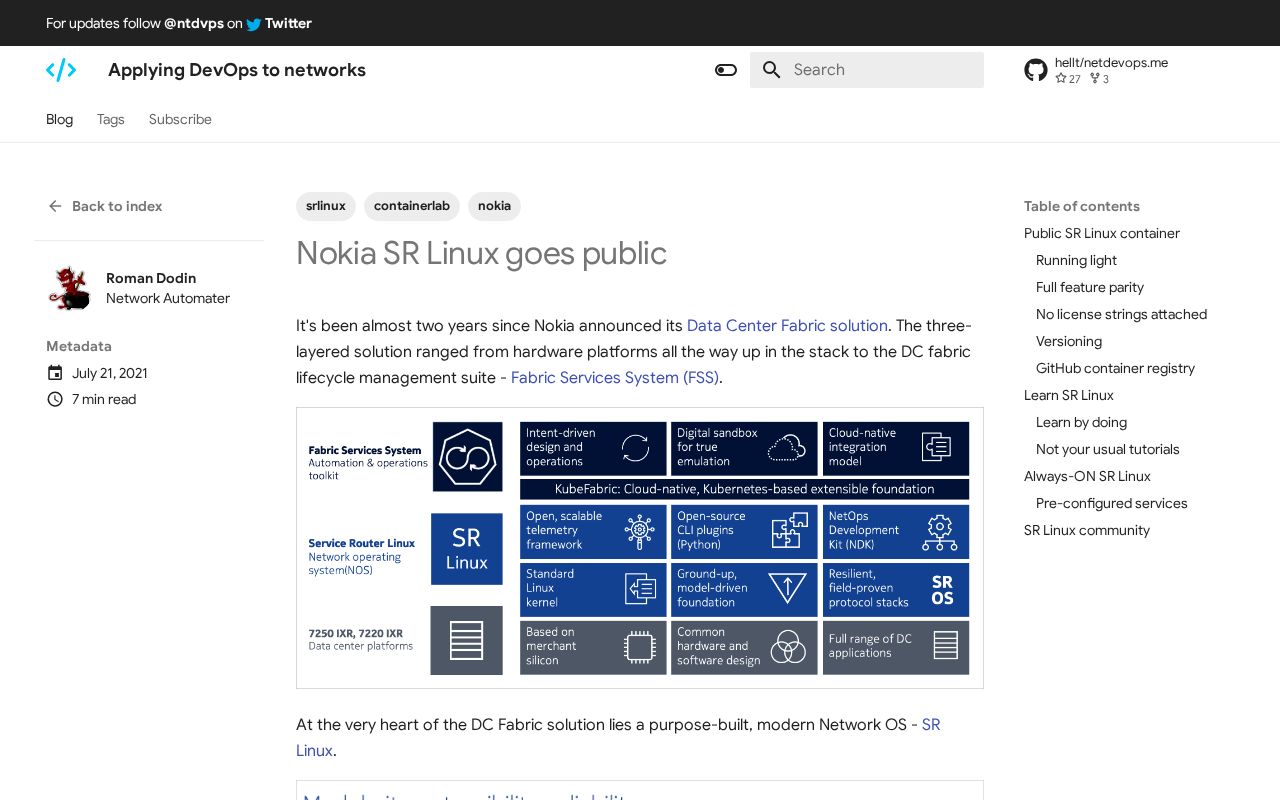
Applying DevOps to networks.
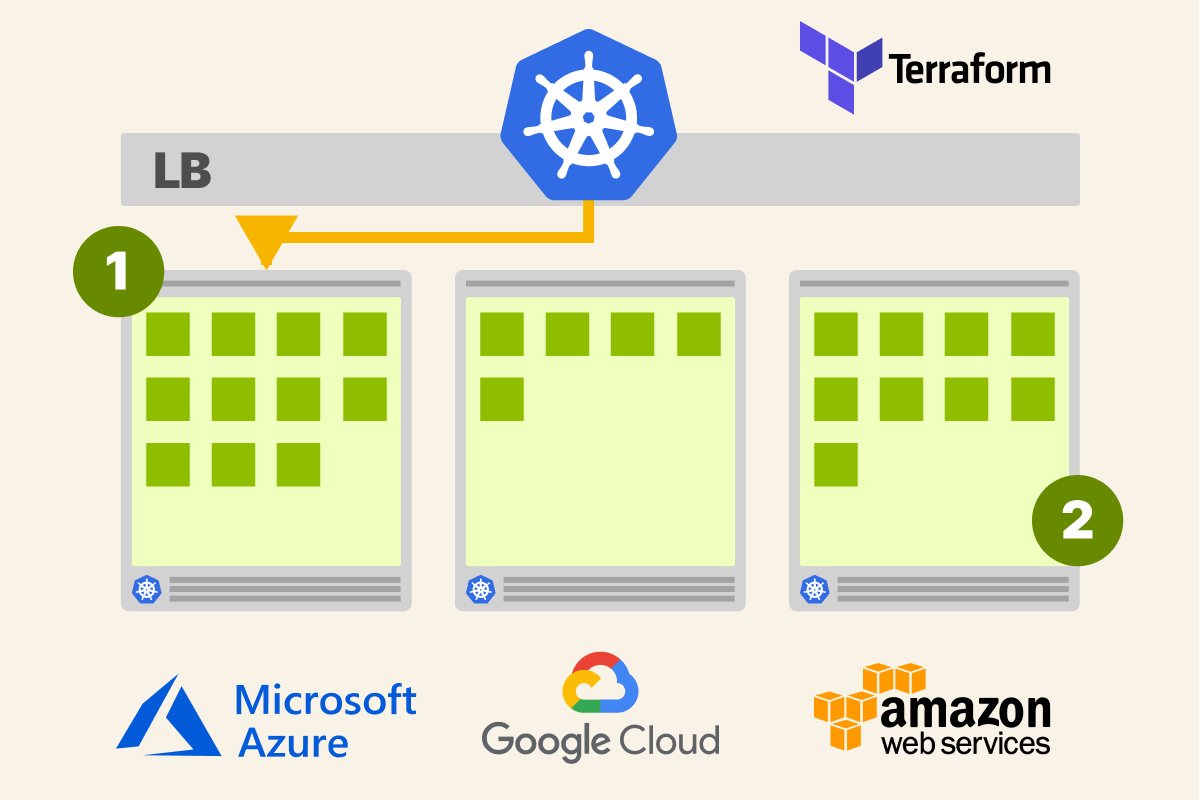
Learn how to create a Kubernetes cluster on Azure, Amazon Web Services (AWS) and Google Cloud
Software-Defined Datacenters | NSX-T | NSX-ALB | VMware Cloud Foundation (VCF)
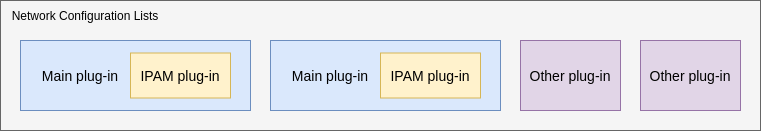
CNI is the container network interface that provides a pluggable application programming interface to configure network interfaces in Linux containers.
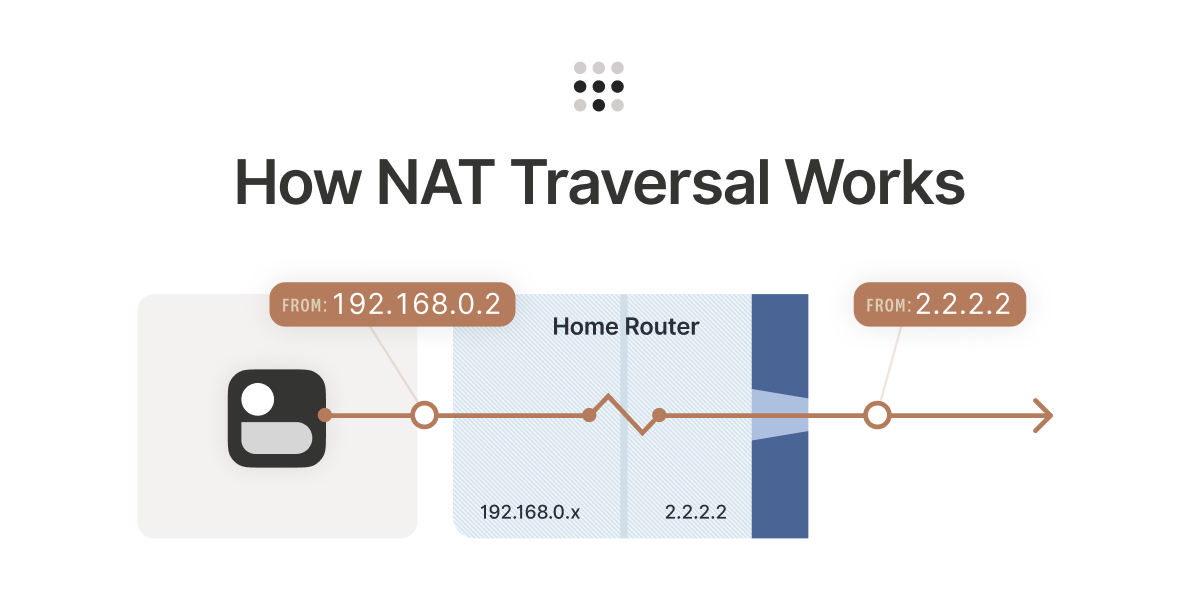
Learn how NAT traversal works, how Tailscale can get through and securely connect your devices directly to each other.
Todays topic is VMware Cloud Director inter-tenant routing with a NSX-T backed provider VDCs (pVDC). The reason for writing this post is that some use-cases require routed connectivity between Org VDC
Cheatsheet to a more maintainable configuration.
Applying DevOps to networks.
This article contains several examples I could have used after reading up on the basics in Python. After I read the first chapters of Automate the Boring Stuff with Python and Learning Python, 5th Edition, I struggled to put the concepts I read about into practice. I understood the basic...
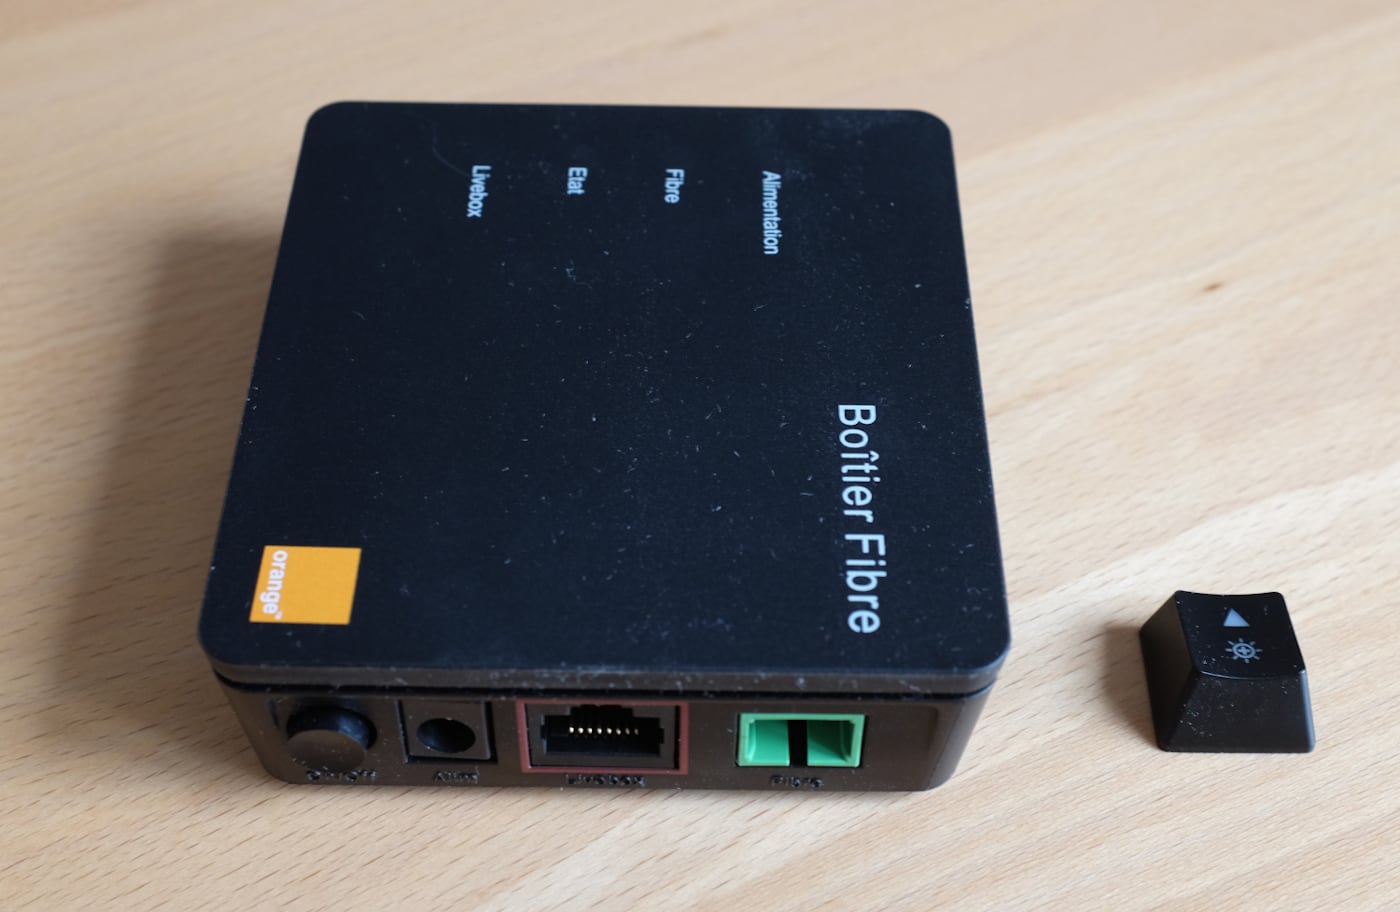
Replacing Orange Livebox with another router is widely documented but too kludgy for my taste. I expose a cleaner setup.
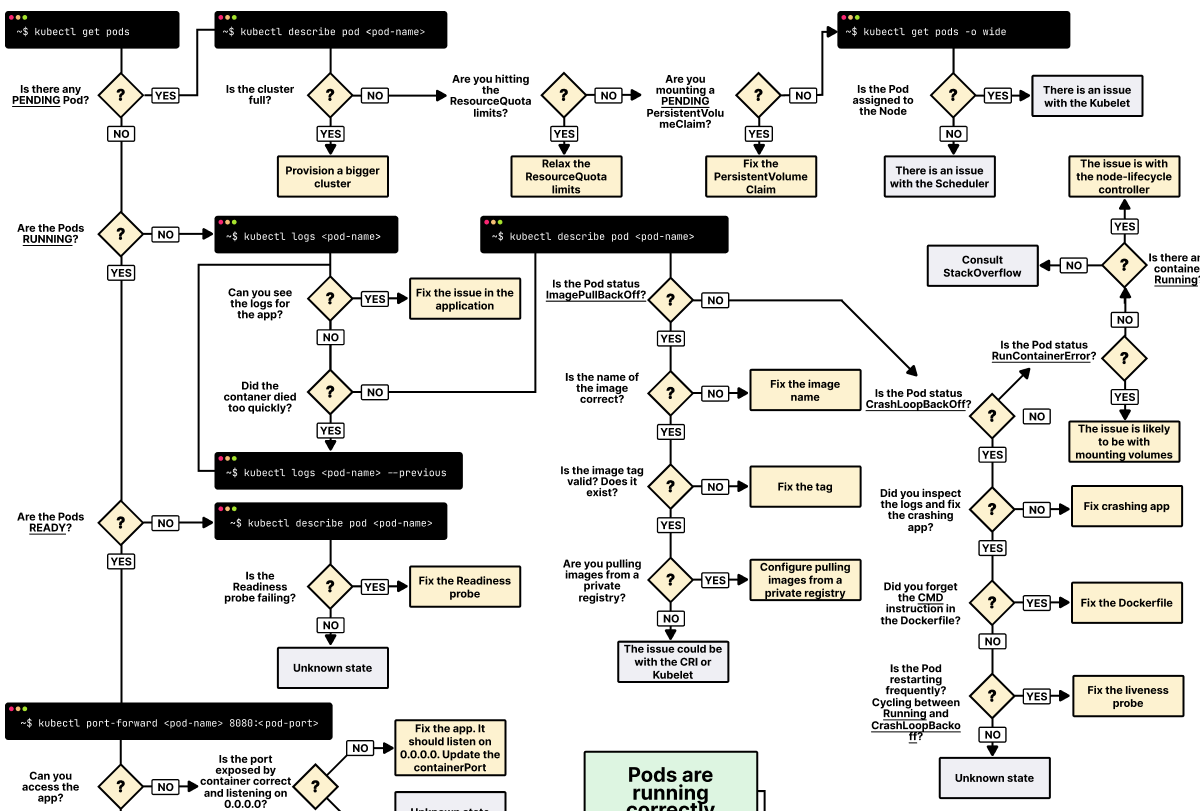
Troubleshooting in Kubernetes can be a daunting task. In this article you will learn how to diagnose issues in Pods, Services and Ingress.
If you work with computer networks sooner or later you will have to learn how to efficiently work with IP addresses and networks. As you probably guessed from the title of this post, we'll be learning how to create, modify and perform operations on IP objects using Python. Having to
Guest Post: Why does half the Internet use a TTL of 1 minute or less?
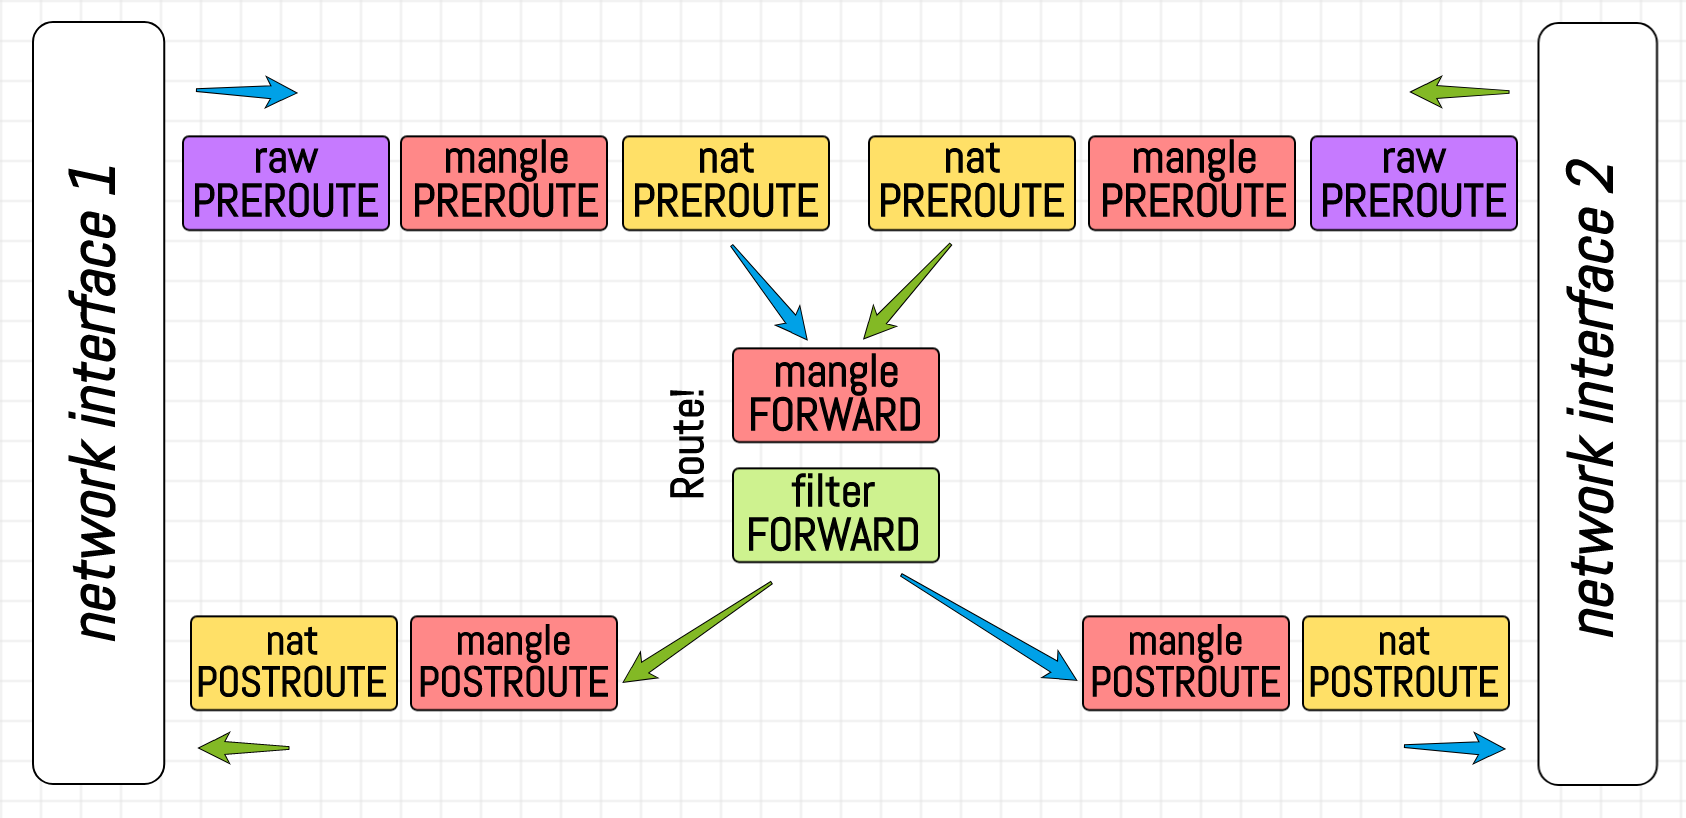
What are iptables chains, rules, policies, and tables? Describe iptables in layman's terms.
Step by step guide for using cloud-init on vSphere
Intro
I have been experimenting a lot over the past 18 months with containers and in particular, Kubernetes, and one of the core things I always seemed to get hung up on was part-zero - creating the VMs to actually run K8s. I wanted a CLI only way to build a VM template for the OS and then deploy that to the cluster.
It turns out that with Ubuntu 18.04 LTS (in particular the cloud image OVA) there are a few things need changed from the base install (namely cloud-init) in order to make them play nice with OS Guest Customisation in vCenter.
Blog
Introduction Traditionally, Data Centers used lots of Layer 2 links that spanned entire racks, rows, cages, floors, for as far as the eye could see. These...
Implementation of redundant site-to-site VPNs on Linux with WireGuard (instead of IPsec) and BGP.
For ease of configuration, virtual guests are usually connected to a layer 2 network. However, hypervisors can be turned into layer 3 routers...
Linux IPsec implementation is usually policy-based. However, route-based VPNs with a pseudo-interface are also available.
Linux uses an LPC-trie for looking up routes. It provides good performance with low memory use even with millions of routes.
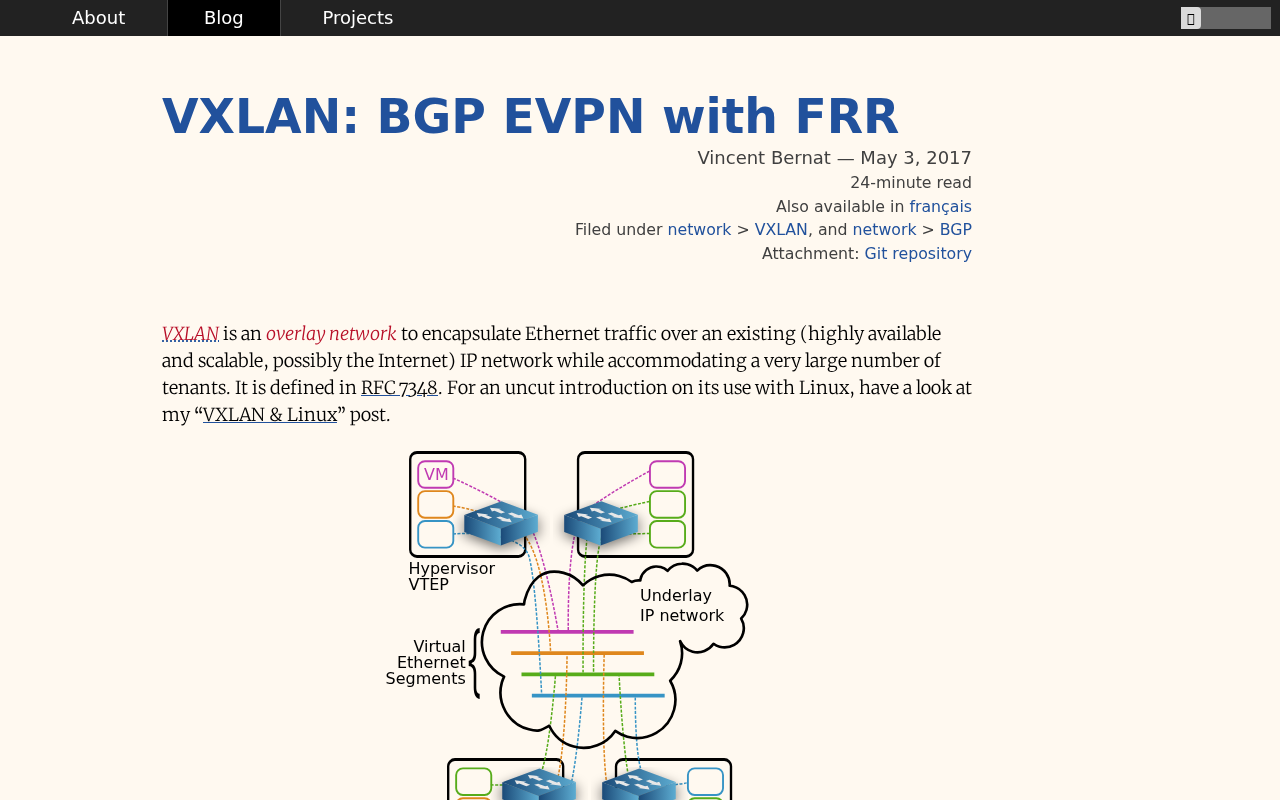
VXLAN is an overlay network for L2 traffic over an existing IP network. One deployment option is BGP EVPN.
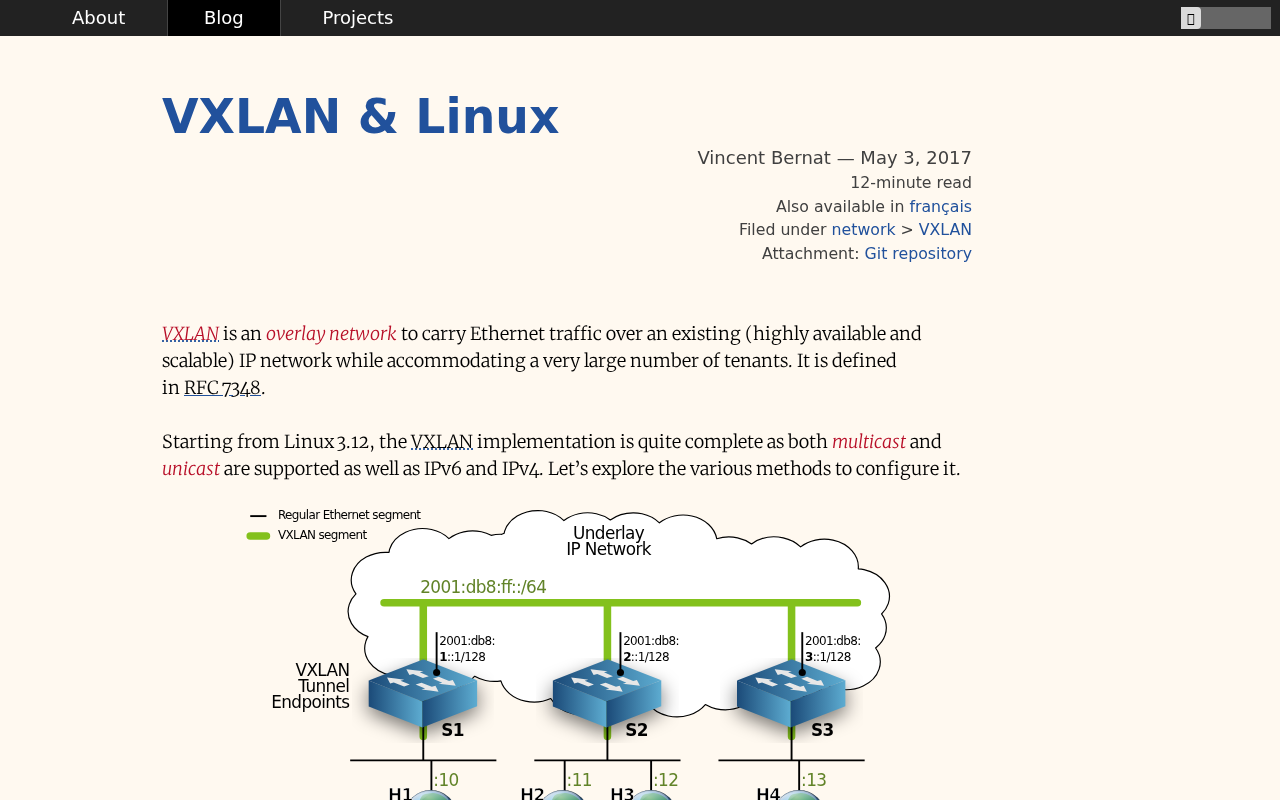
VXLAN is an overlay network for L2 traffic over an existing IP network. Let's explore how to configure it on Linux.
On Linux, a network bridge without any IP address configured will still process IP packets. How to disable such a feature?
Virtual eXtensible Local Area Network (VXLAN) is a protocol to overlay a virtualized L2 network over an existing IP network with little setup. It...
In a recently published article, Paul Vixie, past author and architect of BIND, one of the most popular internet domain servers, explains why DNS...
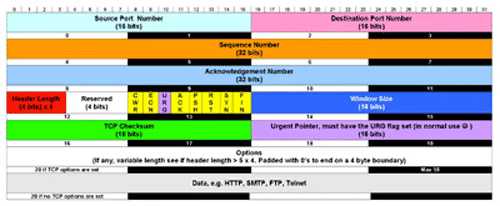
tcpdump is the world's premier network analysis tool—combining both power and simplicity into a single command-line interface. This guide will show